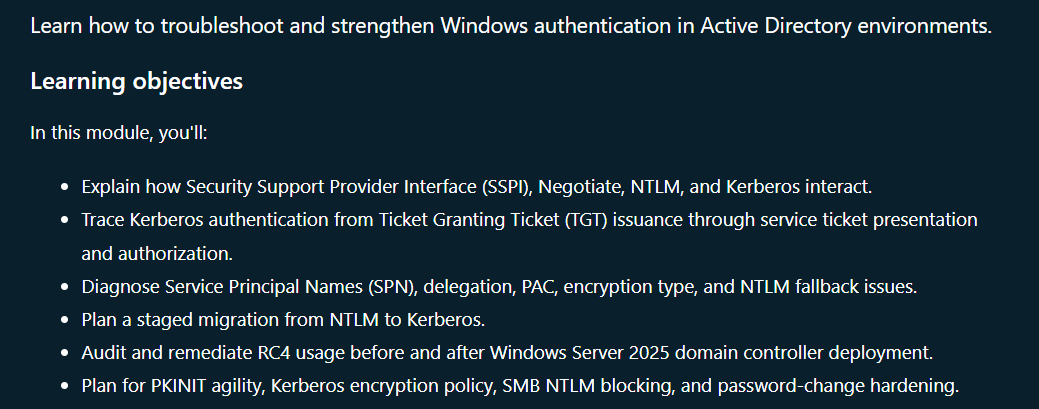
Microsoft reúne una excelente serie sobre #ActiveDirectory Hardening, con temas fundamentales para reducir la superficie de ataque:
✅ Deshabilitar NTLMv1
✅ Eliminar SMBv1
✅ Forzar LDAP Signing
✅ Implementar AES para Kerberos
✅ Configurar LDAP Channel Binding
✅ Forzar SMB Signing
✅ Aplicar Least Privilege
✅ Reducir y eliminar el uso de NTLM
⚠️ Hardening no significa aplicar una GPO y esperar lo mejor. Requiere inventario, auditoría, pruebas y validación de dependencias.
Una lectura imprescindible para cualquier administrador de Active Directory. 👇
https://t.co/1vpiTDL5Bu
For all the the IT admins asking, how do I make Active Directory MORE defensible. This is how…
Jerry Devore’s awesome series on Active Directory hardening.
Part 1 - Disabling NTLMv1
Part 2 - Removing SMBv1
Part 3 - Enforcing LDAP Signing
Part 4 - Enforcing AES for Kerberos
Part 5 - Enforcing LDAP Channel Binding
Part 6 - Enforcing SMB Signing
Part 7 - Implementing Least Privilege
Links for each one👇
https://t.co/JNDMfVqoDP
This is a really good question.
What do you do after Entra ID is compromised?
The good news is this scenario happened to none other than Microsoft themselves and to their corporate tenant.
Even better is they've been providing quarterly updates through their SFI program on what they've been doing across all of their services.
In my last two years at Microsoft, I was part of the team that took all the internal learnings and made them available to all our cuatomers.
We published the guidance at https://t.co/v9pHn2OfEN
There's a lot in there and you don't need to wait till you get compromised to roll them out.
Note: This is after you address the basics of recovering the tenant.
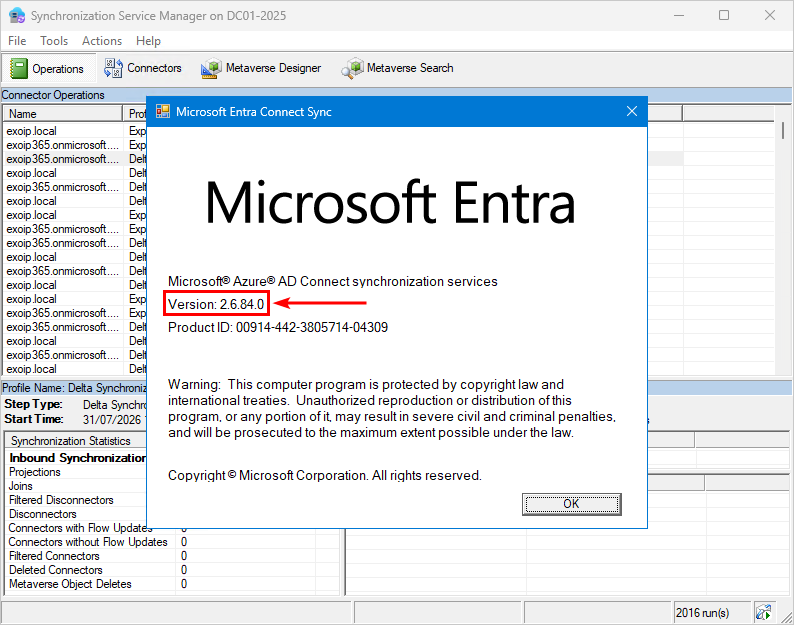
Microsoft Entra Connect Sync upgrade required before September 30, 2026!
All synchronization services in Microsoft Entra Connect Sync will STOP working on September 30, 2026 if you're not on at least version 2.5.79.0.
In May 2025, Microsoft released this version with a back-end service change that hardens its services. Upgrade before this deadline to avoid any service disruption.
Microsoft strongly recommends upgrading to the latest available version 2.6.84.0, rather than only meeting the minimum version requirement.
Version 2.6.84.0 includes security fixes and is the current recommended release.
If you're unable to upgrade before the deadline, all synchronization services will FAIL until you upgrade.
The Microsoft Entra Connect Sync .msi installation file is exclusively available on Microsoft Entra Admin Center.
Make sure you meet the minimum requirements, including .NET Framework 4.7.2 and TLS 1.2.
Learn more:
- https://t.co/Uwzw2y49F7
- https://t.co/3VTk4fO9ko
#Microsoft365 #EntraID #EntraConnect #Cybersecurity
There are numerous ways to extract cloud credentials (like tokens) once an attacker gains access to a workstation. Protect your cloud admin credentials as Tier 0.
https://t.co/yjD8tKv2eA
Claude-AD
Active Directory pentest methodology for Claude Code.
Skills, agents and commands that give Claude the playbook for an internal Active Directory assessment: the phase order, the environment constraints that break your tooling, the telemetry each technique leaves behind, and how a finding maps to a compliance control
Resource/Credit: https://t.co/m2CSH1EUhw
Ensure you have at least 2 emergency (break glass) accounts for Entra ID. These should have long passwords and FIDO2 keys. Monitor and alert when logon to either of these accounts occurs.
https://t.co/kDJqtq4AOd
A simple guided setup for emergency access accounts 😎
Recommend dev/test for now - includes setup of emergency access accounts, automated exclusion from CA policies, optional RMAU and alerting
azd init -t nathanmcnulty/azd-emergency-access && azd up
https://t.co/Ik485fs4J5
I’ll be honest. Purview has always felt like someone else’s part of the Microsoft security stack.
I’m an Entra person. Ray Reyes isn’t, and that’s why I wanted him on https://t.co/YTVmebsh6k
The lines between our products and teams are disappearing.
Insider Risk can influence Conditional Access. Purview and Global Secure Access can help stop sensitive data moving into unsanctioned AI apps. A policy that looks simple in one portal can involve identity, network, data security, cybersecurity, HR, managers and data owners.
Ray had some really good tips for Entra admins. We don’t need to become Purview experts but we do need to understand enough of the neighbouring products to ask better questions.
→ What triggered this policy?
→ Who should own the alert?
→ Should the response be a block, an investigation or simply some education?
→ And what will the user actually experience?
Ray made a great point: the technical configuration may take 15 minutes, but getting all the right teams aligned is the real work.
The conversation also went to some areas that are close to my heart. Ray shared the story of the charity he and his wife started in Nepal, and we spoke openly about burnout, layoffs, gratitude and building a career safety net outside any one employer.
If you work in Entra, this episode is an invitation to look over the fence and understand the security products and people you increasingly depend on.
Ray is a Principal Security Consultant at Engage Squared and the author of Mastering Microsoft Purview Deployment in the Era of AI.
Watch or listen: https://t.co/iyOYRulzeQ
If you want to learn Kerberos and all the delegation techniques, this is imho the best resource I have read so far: https://t.co/Z731m9QP9R
Shoutout to @abdo_mhanni for the detailed explanations and great illustrations. The wiki covers pretty much all of Kerberos.
ACTIVE DIRECTORY SECURITY SIMPLICITY
PAW - Privileged Access Workstation
Jump Server - Only for administration
DUO/2FA - Mandatory
Group Policy
- Windows Firewalls on DCs locked down
- RDP inbound only from Jump Server(s)/PAW(s)
- Software Restriction Policies
-- Yeah, we kill Chrome and all other %LocalAppData% abuses
-- Lockdown app access
- User Account Control
-- Mandatory for ALL domain users
-- On the Secure Desktop
-- Credentials Required for ALL
-- RD Session Hosts: Elevation BLOCKED
Now, here's our ADDS KISS (Keep It Simple S_______) Architecture:
In today's modern threatscape the above gets implemented in a dedicated role based ADDS Forest/Domain!
- Production: UserVille
- Infrastructure: Servers not required on UserVille
- Dev: Yeah, they don't belong anywhere near UserVille
- DMZ: IIS security is better under ADDS
- IT: Yup, support gets their own Forest/Domain
-- RemoteApps in UserVille suffice
-- One can restrict copy/paste to PAW/Jump Server
Now, one can create a trust but it should be one way and one should always keep in mind that _UserVille is a Hostile Tenant_ no matter what!
Remember, most compromises start with an errant click in UserVille. So, we can mitigate out of the box with a solid, secure, and segmented architecture.
Password sprays like this reveal more than meets the eye information. You can make inferences about specific conditional access policies. When a username and password is correct, you can enumerate what MFA methods are available for follow-on attacks. Believe it or not, that informatiin has a value. For example, if your CAPs were thrown together without careful thought using device filters, that can work against you and leave you vulnerable in ways you thought you are covered.
PS Note. Az Cli can also be used in such a way it looks like its coming feom the browser.
Another day, another bad set of CIS recommendations
Here are the items you do not want to do in this list:
5.1.5.6 - Ensure maximum certificate lifetime for applications does not exceed 180 days
⚠️ This will silently break cert renewal for all of your SAML based SSO apps...
I just wrote a new blog on bypassing CA policies in Entra ID that have a resource exclusion, and why you probably want to enable baseline enforcement if you have such policies. Enjoy!
https://t.co/a1rGl3wss8
Look.. it's a Conditional Access policy simulator built by an infra architect guy who got tired of squinting at What If results 🫠 Shiny graphs yay! 🔗https://t.co/hqKKVDnBFV No sign-in needed, click Sample Data and play around. Or connect to your own data - all's in browser.