‼️ UPDATE: Security firm Calif says it took over Jira, Confluence, Jenkins and Keycloak servers with Java4Shell, without even logging in.
The flaw sits in the code Java uses to decode Base64, a common way to send data as text. A short malformed string makes it write past the end of its memory.
Calif's researcher says OpenAI's Codex helped him find the bug in an hour and build a working exploit in two more, for under $200 in AI costs.
Oracle shipped a patch tonight. Calif is holding back its exploits until people have patched.
🔴 CRITICAL 9.5 · React: remote code execution in server components (CVE-2026-126187)
An unauthenticated attacker can run arbitrary code on the server by sending a crafted request, without logging in.
👉 Fix: 19.0.9, 19.1.10 and more
https://t.co/0Oh2rKFY2Y
I CANNOT believe the report: it proves that eMudhra is a clown show, and was never fit to be a CA:
The point of a HSM (hardware security module) is that the private key NEVER leaves it. Guess what eMudhra did: it turned off FIPS mode (WTF?!) and copied out the private key 😱
‼️ eMudhra revokes 8 more certificate authorities it previously said were unaffected.
A Python script retrieved RSA private key material from HSMs into process memory, leaving the company unable to verify proper key handling.
16 CAs revoked in total.
Details: https://t.co/xLAy9dJixe
‼️ UPDATE: An attacker using AI models with their safeguards stripped out broke out of Railway's build sandbox and went hunting for customers' AI API keys.
The cloud hosting platform's full postmortem says secrets for up to ~100,000 workspaces may have been decrypted. The stolen keys ran up an estimated $740,000 in charges.
The way in was an unknown bug in Railway's build isolation, then a misconfigured cloud login that led to the database of encrypted secrets.
Railway believes the keys were sold on to feed AI model distillation. It calls the fight "a contest of agent speed".
talking to a coding agent is more like email than irc - because the interactions are few and far between, I often finding myself quoting their most recent text, answering multiple questions. addressing different topics. it's like replying to an email.
It makes me wonder if you could have a coding agent UI that was more like an email client or mailing list kind rather than chat
New phishing kit just dropped: MadApe
It steals Microsoft 365 access without fake login pages.
Victims receive a “document” PDF → a device code appears → they sign in on the real Microsoft site → the attacker gets the token (MFA is often satisfied).
Over 300 domains tracked (phishing components on 97 of them), plus dozens of PDF hashes and URLs. Multiple languages. SharePoint/OneDrive/Teams lures.
IOCs by OTX.
IaC isn't dying, it's becoming more essential. Non-deterministic layers add new volatility to the stack, but they don't break the core principles. For example, it's becoming more obvious that we want some layers to be truly reproducible.
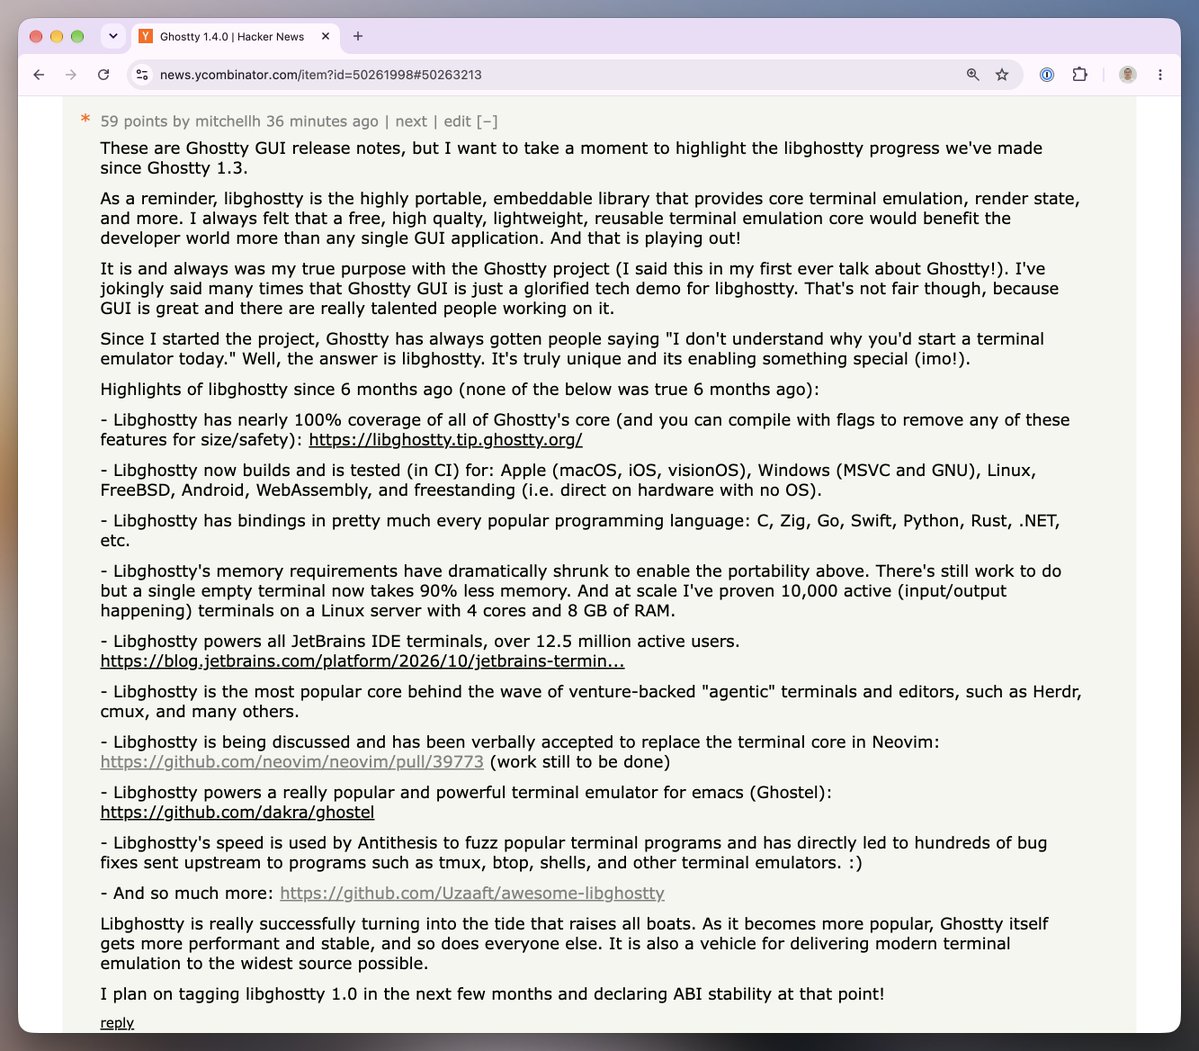
Libghostty progress in the past 6 months. It's amazing that NOTHING IN THIS LIST was true 6 months ago, and now its ALL VERY REAL. I remember bringing up the idea of libghostty 4 years ago and most people saying "but why." I did it anyways. And here we are!
Text reproduced in case its easier to read this way:
As a reminder, libghostty is the highly portable, embeddable library that provides core terminal emulation, render state, and more. I always felt that a free, high qualty, lightweight, reusable terminal emulation core would benefit the developer world more than any single GUI application. And that is playing out!
It is and always was my true purpose with the Ghostty project (I said this in my first ever talk about Ghostty!). I've jokingly said many times that Ghostty GUI is just a glorified tech demo for libghostty. That's not fair though, because GUI is great and there are really talented people working on it.
Since I started the project, Ghostty has always gotten people saying "I don't understand why you'd start a terminal emulator today." Well, the answer is libghostty. It's truly unique and its enabling something special (imo!).
Highlights of libghostty since 6 months ago (none of the below was true 6 months ago):
- Libghostty has nearly 100% coverage of all of Ghostty's core (and you can compile with flags to remove any of these features for size/safety): https://t.co/y8MY1k3gG7
- Libghostty now builds and is tested (in CI) for: Apple (macOS, iOS, visionOS), Windows (MSVC and GNU), Linux, FreeBSD, Android, WebAssembly, and freestanding (i.e. direct on hardware with no OS).
- Libghostty has bindings in pretty much every popular programming language: C, Zig, Go, Swift, Python, Rust, .NET, etc.
- Libghostty's memory requirements have dramatically shrunk to enable the portability above. There's still work to do but a single empty terminal now takes 90% less memory. And at scale I've proven 10,000 active (input/output happening) terminals on a Linux server with 4 cores and 8 GB of RAM.
- Libghostty powers all JetBrains IDE terminals, over 12.5 million active users. https://t.co/GD8Wgyk3L2...
- Libghostty is the most popular core behind the wave of venture-backed "agentic" terminals and editors, such as Herdr, cmux, and many others.
- Libghostty is being discussed and has been verbally accepted to replace the terminal core in Neovim: https://t.co/8aCBceaY1v (work still to be done)
- Libghostty powers a really popular and powerful terminal emulator for emacs (Ghostel): https://t.co/Ce7mrr1EC9
- Libghostty's speed is used by Antithesis to fuzz popular terminal programs and has directly led to hundreds of bug fixes sent upstream to programs such as tmux, btop, shells, and other terminal emulators. :)
- And so much more: https://t.co/lAJXhCX8GC
Libghostty is really successfully turning into the tide that raises all boats. As it becomes more popular, Ghostty itself gets more performant and stable, and so does everyone else. It is also a vehicle for delivering modern terminal emulation to the widest source possible.
I plan on tagging libghostty 1.0 in the next few months and declaring ABI stability at that point!
‼️ WARNING - Cisco confirms active, in-the-wild exploitation of a new critical flaw (CVE-2026-76519 // CVSS 9.8) in Cisco Secure Email Gateway.
Unauthenticated attackers can achieve full root command execution simply by sending an email with a crafted attachment.
Details >> https://t.co/Yb1QWiWxQu
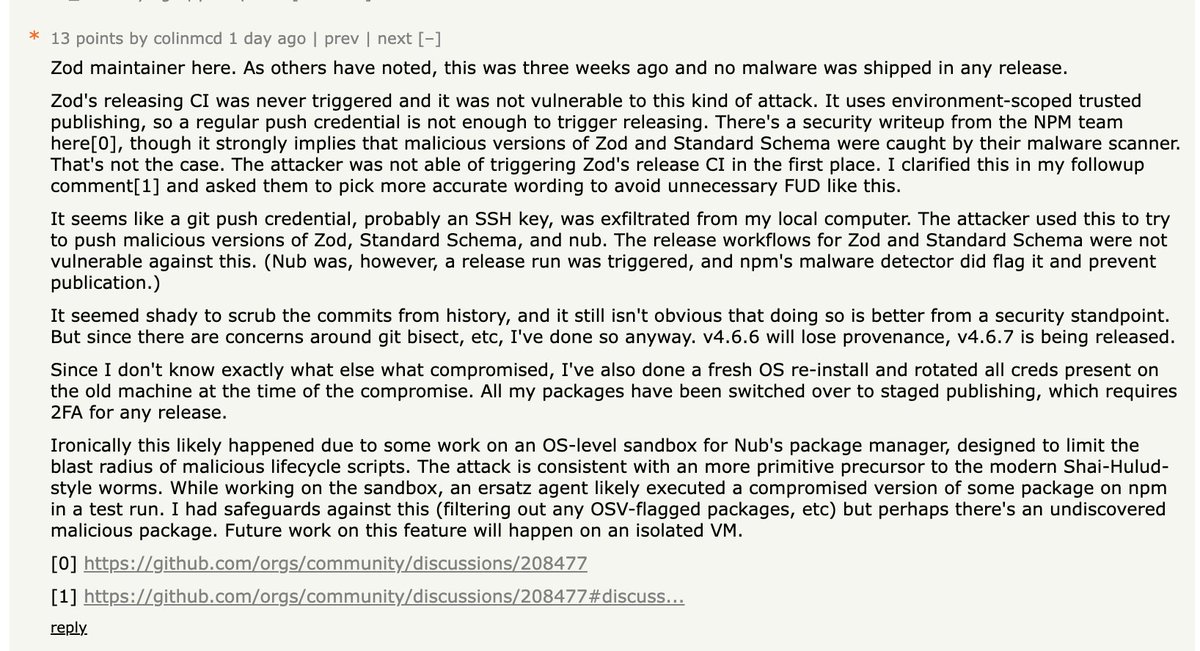
@kara_mage as you said, a push credential was compromised and commits got through to main (now scrubbed from git history). but Zod's releasing CI uses environment-scoped trusted publishing so no npm publish was possible. more info in my HN comment below.
T3 Code Mobile version 1.1.0 is now out on both Google Play Store and App Store!
• Voice input: Dictate prompts with on-device transcription on supported iPhones running iOS 26 or later.
• Files and media: Attach documents and videos, share files into T3 Code from other apps, and preview images, PDFs, and videos without leaving your thread.
• Better drafts: Keep multiple task drafts per project and queue messages while attachments upload.
• Themes: Personalize the app with built-in color themes.
• Usage limits: Check your remaining Codex and Claude subscription allowances across connected computers.
• Thread organization: Reorder active threads and see linked pull requests in your thread list.
• Agent controls: Access skills from the slash menu, compact supported conversations, and work with Google Antigravity.
• Terminal paste: Paste your phone's clipboard directly into the terminal.
Plus smoother chat scrolling, clearer work logs and connection status, faster file previews, and fixes for draft recovery, keyboard behavior, and app updates.
For anyone with endless ideas, this agent age is nirvana as those ideas are met with endless execution, endless exploration. I've never had has much fun working with computers as I do right now. What a time to be alive.
No one can stop me from adding new features! Here's a new experimental cellSpanningFeature I've now whipped up today.
I used to think this would have been a very intrusive feature, but it seems to have been simpler than I thought. Also opt-in, of course.
it's so absurdly cool to get a PR back from your agent with screenshots
had a problem w/ the Executor app name in the MacOS system menu being wrong, the agent used my testing framework with a mac vm to open up a PR with the fix
Do you have a legitimate report or are you just rage baiting on social? We take any leak reports seriously but of course need a reproduction or footprint report or some other method to track it down.
We run all our tests under Valgrind including various graphics e2e tests and there are no known leaks. That doesn’t mean there aren’t any, just showing we take it seriously and will cover scenarios with tests if we can.
Let me know, happy to look into this.
If you’re just trying to get internet points though for no reason, okay.
@KhalidWarsa Eh I don't think this is shady at all. One year of updates then you can use the last version forever is not the same as a subscription. Sketch and TablePlus both do this, and I really appreciate it.
It's 2026 and your CEO just sent you a 2,400 line pull request.
You get a cup of coffee and sit down to review it.
It's a disaster. A dozen unrelated refactors. Unused methods with names like `convertFromBase10` and `normalizeBeforeSerialization`.
You catch a few hardcoded API keys, but that's ok. It's part of the dance. They didn't consider that someone might look at this diff. Here's a comment buddy.
They respond in an hour (after Copilot, qodo, CodeRabbit and Greptile finish their reviews) saying we shouldn't worry about "implementation details" anymore, those are relics of the past. Hey let's jump into a room and figure it out. We can't just agree to disagree, this is probably my last job in tech and I can't watch this fucker burn the place to the ground.
The PR merges and goes to prod. You feel a shared sense of apathy and dread with Hannah the intern (she has to review his AI generated social media posts ever since Grok got too imaginative).
That night you go to sleep and have nightmares of that code. You can still see the shapes of it on the backs of your eyelids.
You go to work the next day ready to quit. You no longer understand the system. There is no foundation. Time to use those savings and an SBA loan to buy a liquor store and never login to GitHub again.