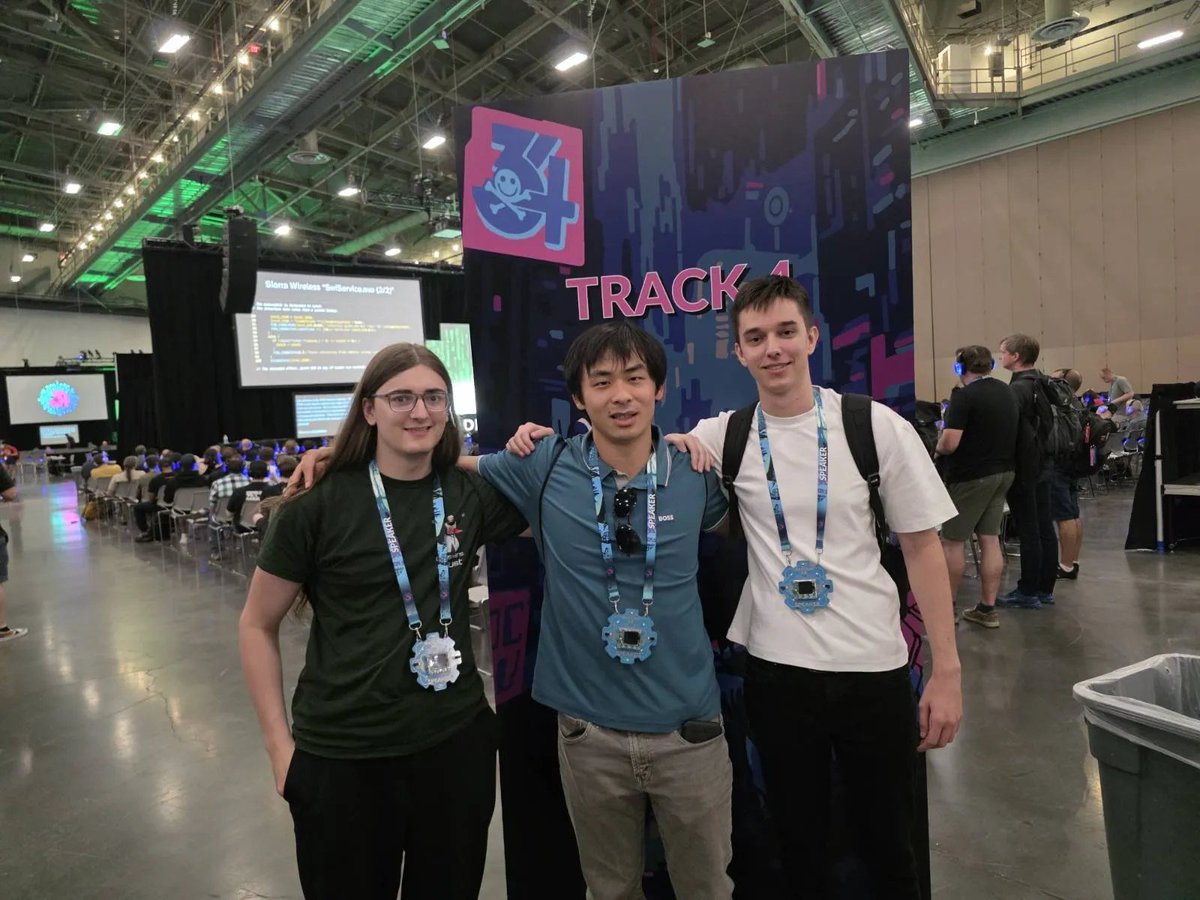
Come watch our talk at DEFCON Mainstage from this summer by @clubby789@ryaagard and https://t.co/0NktUKF46V! Back in the days of artisanal hand-crafted Chrome exploits😇
https://t.co/s3JrC37CQE
i jailbroke the nintendo switch 2
so i modded cinnamoroll, peter griffin, hatsune miku, and more into Mario Kart World, a switch 2 exclusive
now watch my friends and i get cooked by bots
learn more and get the exploit https://t.co/ykjgyfrFRp
Busy weekend for CoR members at @defcon!
Congrats to all our teammates who got 3rd at DEFCON CTF Finals under @SuperDiceCode and to @clubby789, @ryaagard, and https://t.co/PzcyCKjeK4 for their main stage talk on a Samsung Galaxy UXSS exploit (slides + video coming soon)🫡
We had a blast this weekend at @offensive_con 🔥- thank you to @Binary_Gecko for the awesome conference!
Congrats to our teammates @caueobici for his pwn2own success and @ryaagard for his talk on a 1-click Minecraft 0day😎
We achieved a guest-to-host escape by exploiting a QEMU 0-day where the bytes written out of bounds were uncontrolled.
Full breakdown of the technique, glibc allocator behavior, and our heap spray/RIP-control primitive ↓
Watch XOR’s talk CUDA de Grâce: Owning AI Cloud Infrastructure with GPU exploits
Kernel + driver bugs aren’t just a LPE problem, they’re a cloud problem. With the explosion of AI in the cloud, NVIDIA’s GPU drivers have become a valuable attack surface
https://t.co/cIYKcYMb6L
My HEXACON talk video is out! It covers a small race condition in the Linux kernel’s io_uring. I recommend watching it at 1.25× speed since I’m still not great at speaking 😅
https://t.co/lMuweA7PyU
Here is the slide!
https://t.co/9jPoKMzxwL
If you missed HEXACON 2025 or want to rewatch some of the talks, they’re now available on our YouTube channel 📽️
Enjoy the content, and see you in 2026!
https://t.co/KHHVAGY48M
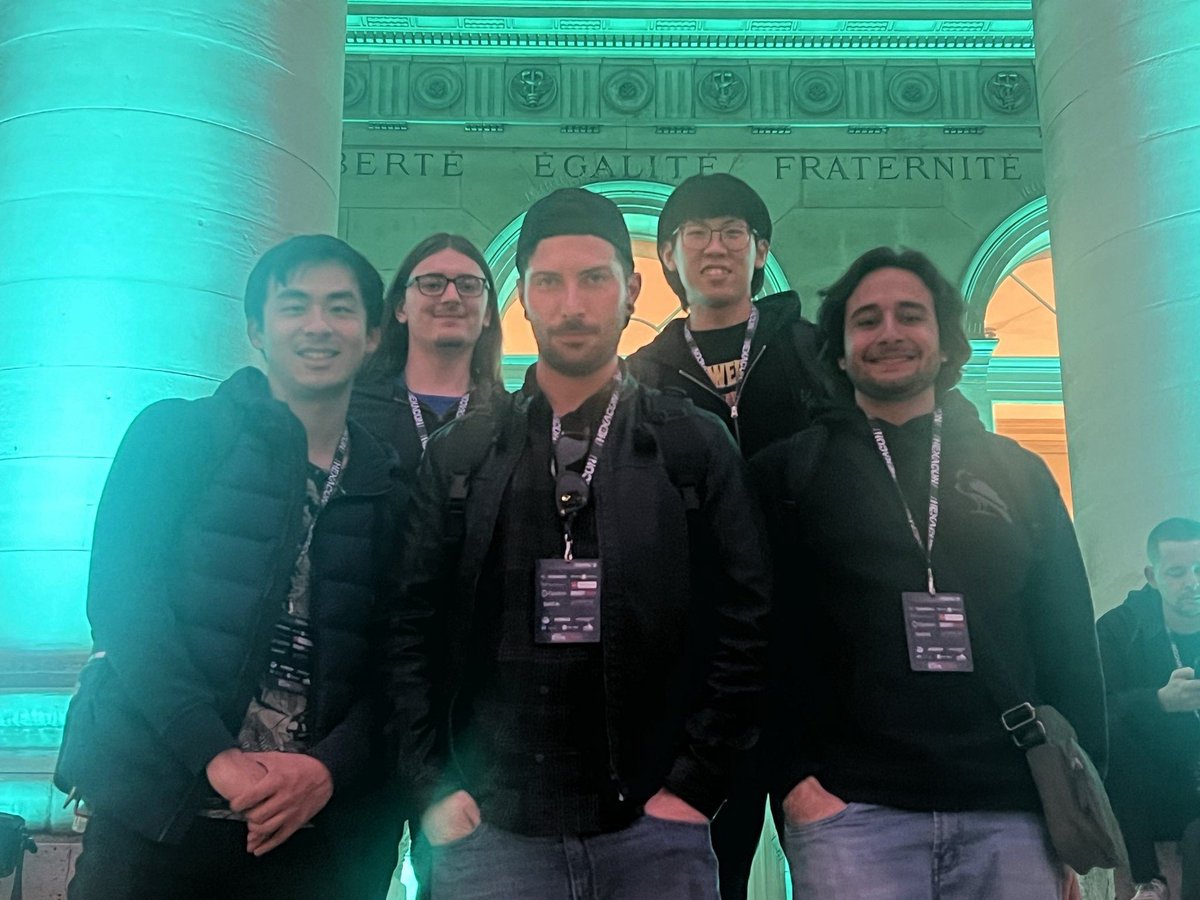
We at CoR (+ @u1f383) had a great experience at @hexacon_fr this weekend
Met many skilled VR people, the venue was amazing, and the speaker gifts were simply🔥
Best offensive security conference we have seen so far - thanks again to the organizers for the opportunity!