I've been crawling business websites. About 116 million live sites so far.
Then I rechecked the ones that looked dead, a week later from two locations. Half came back. Single checks overstate decay about 2 to 1 seemingly due to bot checks & cloudflare type filters.
1 in 4 sites hasn't touched its footer in 3+ years.
Most of these sites have nobody watching them. I'll be posting what I find.
@FrontlineTalks Already on it. Re-checked the same sites this morning: patched went from 6.4% to 19.5% in a day. 8.4 sites jumped to 62%, 8.2 only 19%. The 8.1-and-older crowd barely moved, 92 of 3,606. Next re-scans are tomorrow and Oct 28.
PHP shipped emergency patches today for PHP2Shell, and CISA says sites on 8.1 or older should go offline until fixed. I checked 175,110 small business websites I track.
95% hide their PHP version. Of the 8,775 that show it, 93.6% are on a vulnerable version, and 41% are on one with no official fix.
@Ultra_Domains Mostly never told. Of the working business sites I track, 61% have no DMARC record at all. About 24% published one but stopped at p=none, and only 15% actually enforce. So most never started, and of the ones that did, more than half stalled at monitoring.
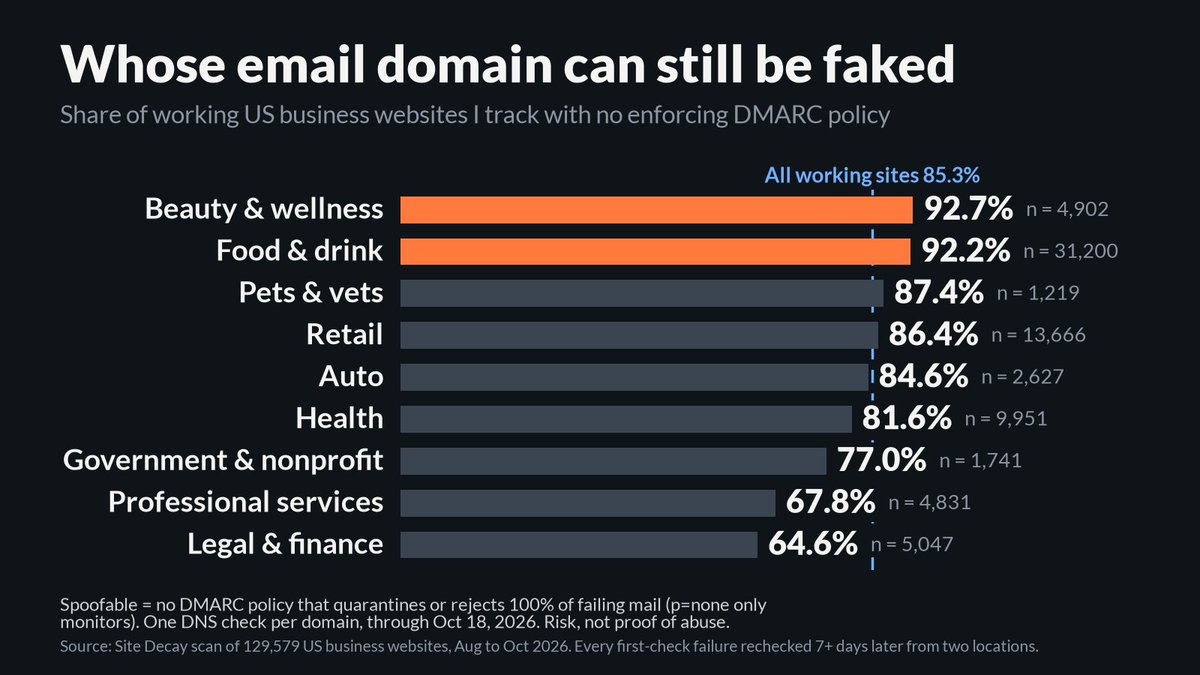
Email spoofing risk is not evenly spread.
Share of working business websites I track where the domain can still be faked in email:
Beauty & wellness 92.7%
Food & drink 92.2%
Legal & finance 64.6%
Salons and restaurants are close to wide open. Law firms and finance shops do better, and most of them still aren't fully locked down.
If your business lives on Google reviews and phone calls, your domain name is doing unpaid work for whoever wants to fake an invoice from you.
The real certificate problem isn't scary roots. 7,664 small business sites I track (4%) serve a cert that fails in browsers: self-signed, missing intermediate, or expired.
Visitors see a warning page. Owners usually have no idea.
Chrome drops the emSign ECC G3 root on Oct 27. I checked 192,129 small business sites I track that serve a certificate.
Chained to that root: 0.
83% use free certs from Let's Encrypt (62%) or Google (21%). The free stuff won.
Also new: I'm now tracking sites going from fine to down or hacked every night. First 10 hours: 6 confirmed outages, 0 confirmed defacements. Too early to blame PHP2Shell, but now I'll see it when it happens.
PHP2Shell, day 2. I re-checked the same 8,775 small business sites I track that show their PHP version.
Yesterday 6.4% were on their branch's fixed release. Today it's 19.5%.
Real movement. Still 4 out of 5 not there.
The hard part hasn't moved. 3,301 sites still show PHP 8.1 or older, which has no official fix. Only 92 of them jumped to a fixed release overnight.
If that's you, patching isn't an option. Upgrading or rebuilding is.
@MikeTheTrader Wikipedia going dark to patch is the good outcome. The scary ones are the small business sites that never blinked yesterday because nobody's around to patch them. 41% of the ones I track that show a PHP version show 8.1 or older, which gets no fix.
@vladozahradnik A lot. Of the small business sites I track that show their PHP version, about a quarter show PHP 7 or older, and 648 still show PHP 5. Most of them aren't kept alive on purpose. Nobody's left who remembers they exist.
@calvinnwq Worth adding to #1: Amazon says it saw PHP2Shell attempts on Oct 17, four days before the patch. So "we patched Wednesday" isn't the end of it. Check logs and new admin accounts back to the 17th.
@Dhanush_Nehru And most of the sites at risk have nothing visible in front of them. Of the small business sites I track showing PHP 8.1 or older, about 88% show no Cloudflare or similar. For a lot of them the only fix is an owner who has to call someone.
@Amospikins Same trap one layer down: the host patched the box, the container still ships last year's PHP. Of the small business sites I track that show a PHP version, only 6.4% were on a fixed build on day 1. Rechecking today to see who moved.
@VaibhavSisinty The eMudhra one has a deadline most site owners will miss: Chrome drops the emSign ECC Root CA G3 on Oct 27. If your site's certificate chains to it, it starts throwing errors that day. Worth a 30 second look at who issued yours.
@RoundtableSpace The part that worries me: no fix exists for PHP 8.1 and older. Of the small business sites I track that show their PHP version, 41% show 8.1 or older. Those owners aren't patching this week. Most don't know what PHP is.