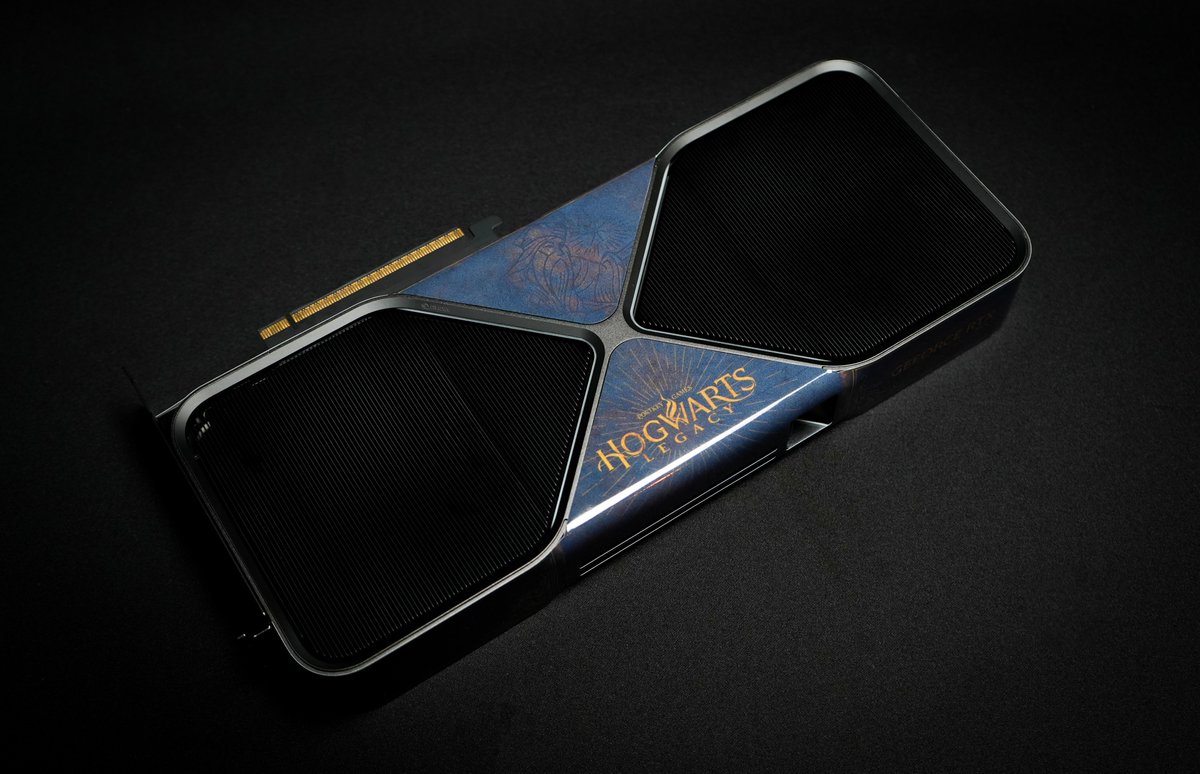
Wir verlosen eine NVIDIA GeForce RTX 5090 im individuellen Hogwarts Legacy-Design, um den offiziellen Release mit DLSS 5 zu feiern 🪄
So machst du mit:
🟢 Teile diesen Beitrag
🟢 Kommentiere mit #RTXON
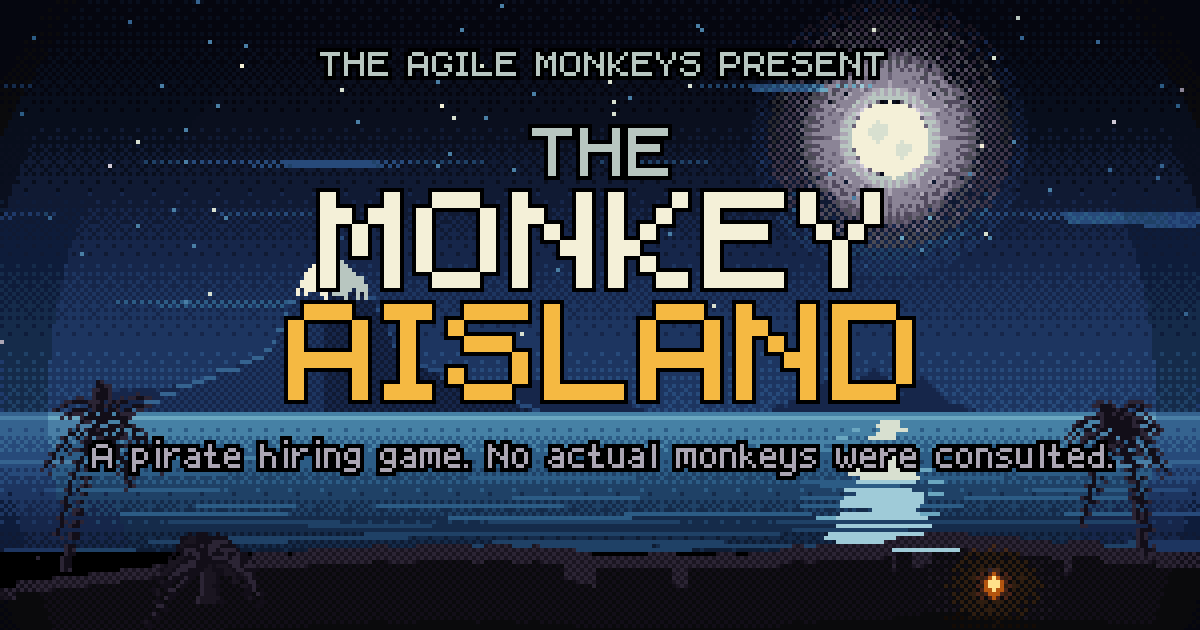
¿Alguna vez te han contratado a través de una aventura gráfica de piratas? 🏴☠️
Habla con el vigía, cruza el muelle y sobrevive a El Patilla para convertirte en el mejor ingeniero de la historia.
Si llegas al final, hablamos.
¿Te atreves? (Spoiler: está en inglés)
So basically, today PHP got two critical bugs that let anyone run code on your server without even logging in, which is bad, and then the details leaked before the patch was even out, which is worse, and it works on WordPress and MediaWiki and Magento and Joomla and Laravel, and Censys says like 1.5 million servers are running a version with no fix, so the NSA was like "take your system offline," and the FBI was like "take your system offline," and CISA and the UK and CERT-EU were all like "take your system offline," and then the Prime Minister of Japan, the actual Prime Minister, posted at 5:55 in the morning telling 48.8 million people to take their system offline, so everyone took their system offline, like the Dutch cybersecurity agency took its own website offline, and the Dutch parliament went offline, and the Port of Rotterdam went offline, and Finland and France and Denmark started pulling government sites, and Wikipedia went down, and https://t.co/QlOXb3COq3 went down, and Asana and GOG and Something Awful went down, and the University of Vienna's webmail went down for some reason, and that's just PHP. Because GitLab also dropped a CVSS 10.0, which is the highest score they give out, for a bug that's been there since 2014, so that's every self-hosted GitLab for twelve years, and then LiteLLM 1.107.0 got hijacked and shipped a credential stealer and a remote access trojan in every single wheel and the Docker images, including latest, and you didn't even have to import it, just installing it was enough, and it's the second time this year, and then Railway paused every deployment on the entire platform because someone got into the environment variables, so now everyone has to rotate every secret they've ever stored there, and TiDB Cloud said someone was walking around inside with stolen credentials for basically a month and an extortion group says they took 10.6 terabytes, and Zeabur got breached for the second time in two months and is just shutting down, like the whole company, and Node.js patched remote code execution and a TLS bypass, and CISA says Plex is being actively exploited, and someone took over 300 Tor exit relays to steal SSH passwords, and SafePay ransomware has hit over 600 critical infrastructure orgs, and India's biggest bank filed a data loss incident, and Japan has been in an official state of emergency in cyberspace since October 9, which honestly explains the 5:55 AM post. Oh, and eMudhra, a certificate authority that's issued over 60 million certificates, whose entire job is proving websites are who they say they are, was supposed to be using private keys that are random numbers over a hundred digits long, and one of them was 4. Just 4. And the others were like 66 and 237. Anyway, it's Wednesday.
We have posted more information about today's security releases, including the sequence of events that led to the discovery, how the PHP security team is improving their processes, and what we need from you to continue this critical work. #php#security https://t.co/gbGTmk7yh1
PHP 8.6.0RC4 is out for testing - 50 changelog entries across 19 components. Run your apps and extensions against it and report regressions before GA.
https://t.co/CzGec0TXbn
@gabrielrufian Cómo era aquello de “cabeza de ratón que cola de león”… Me vienen a la cabeza imágenes y sonidos de mi infancia, de programas de la tele pública (la única que había) destinado a menores. Uno de ellos decía recurrentemente: “solo no puedes, con amigos sí”