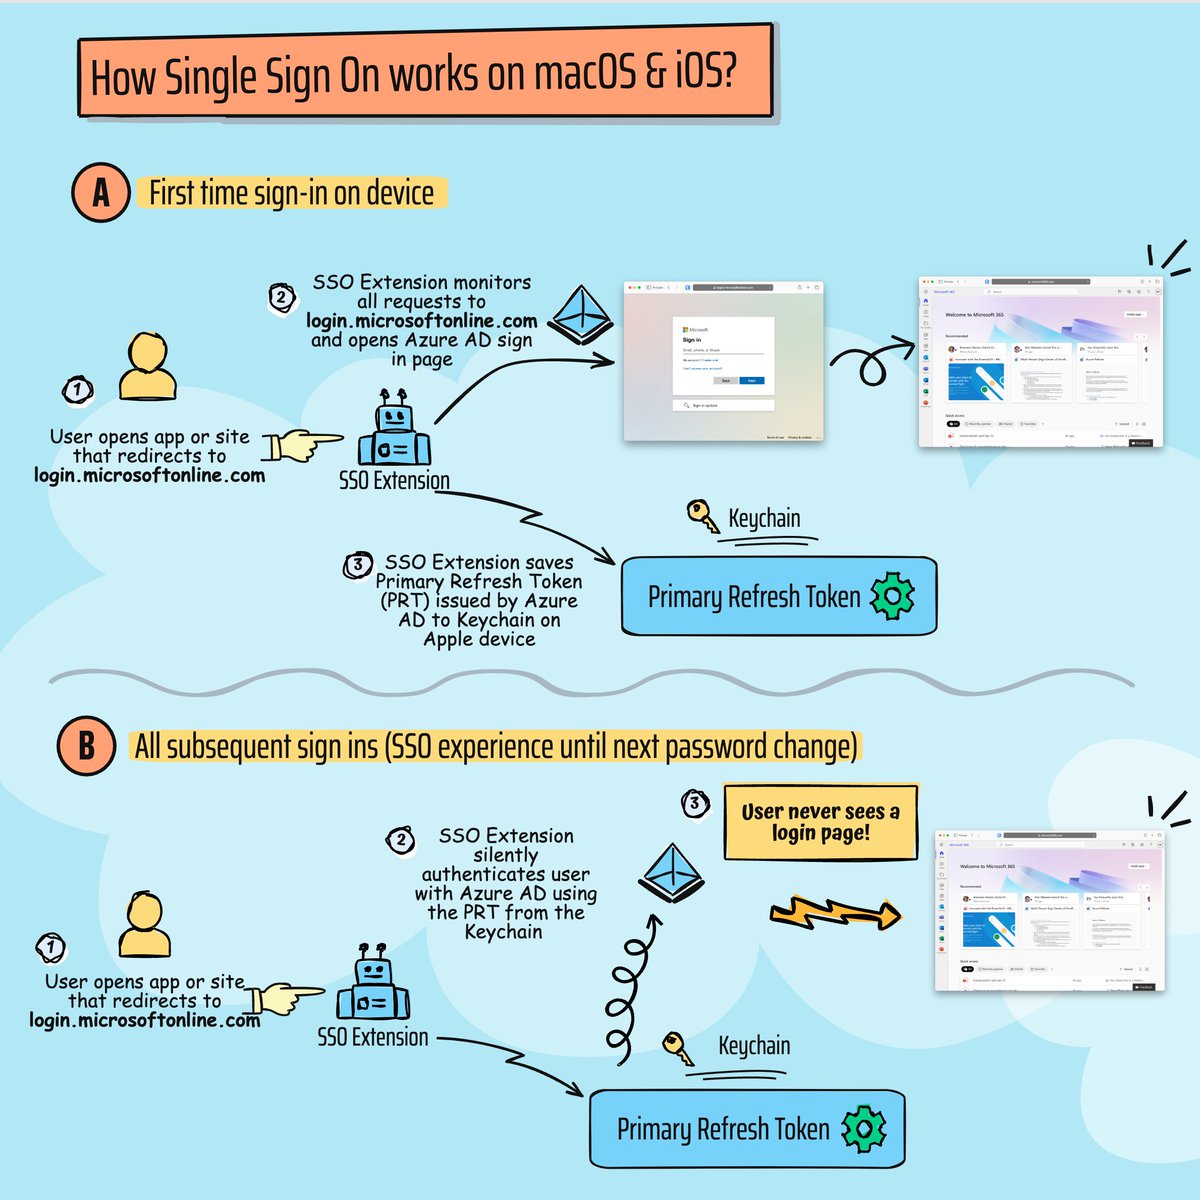
As promised, here is my deep dive into the Microsoft Enterprise Single Sign On (SSO) plug-in for Apple devices
This works on all Apple devices including iOS, iPadOS & macOS!
Windows users have long enjoyed SSO, now you can bring that experience to your Apple users 😍
Read on⬇️
Call for action!
There are two important deadlines for Microsoft Authenticator App features approaching:
- May 8: Authenticator App Number match will be enforced for all tenants. As services deploy, some may see number match while others don't. To ensure consistent behavior for all users, we highly recommend you enable number match for Microsoft Authenticator push notifications in advance.https://t.co/n2b6kjeIzL
- May 26: Authenticator App Lite (companion app) will be enabled for all users. The 'Microsoft managed' setting for this feature will be set to enabled on May 26th, 2023. This will enable the feature for all users in tenants where the feature is set to Microsoft managed. If you wish to change the state of this feature, please do so before May 26th, 2023. https://t.co/78WSz827Oe
Continuing the #BingBang thread, many have asked how we found the vulnerable Bing Trivia endpoint.
Let me share our unique Azure Active Directory cloud reconnaissance technique to find misconfigured authentication prompts🧵
Good basics.
[Article] Monitoring Service Comparison – AWS vs Azure vs GCP (Part 1)
https://t.co/iwxpMULbu5
[Article] Monitoring Service Comparison — AWS vs Azure vs GCP (Part 2)
https://t.co/Yal1Y9PLeO
#Monitoring#PublicCloud#CloudComputing
Uber won't fix the vulnerability that lets anyone email as "Uber"—this isn't a spoofed email but sent from Uber via an exposed endpoint.
Researcher @0x21SAFE states threat actors could abuse this to phish 57 million victims of the 2016 Uber data breach.
https://t.co/5BLRLroWv3
🚨If you are collecting Windows Firewall events or EID 5156 into #MicrosoftSentinel, I've developed beaconing detection for both of them. Grab it here 👇
https://t.co/fTL3sb9VlL
#ThreatHunting#DFIR#Beacon
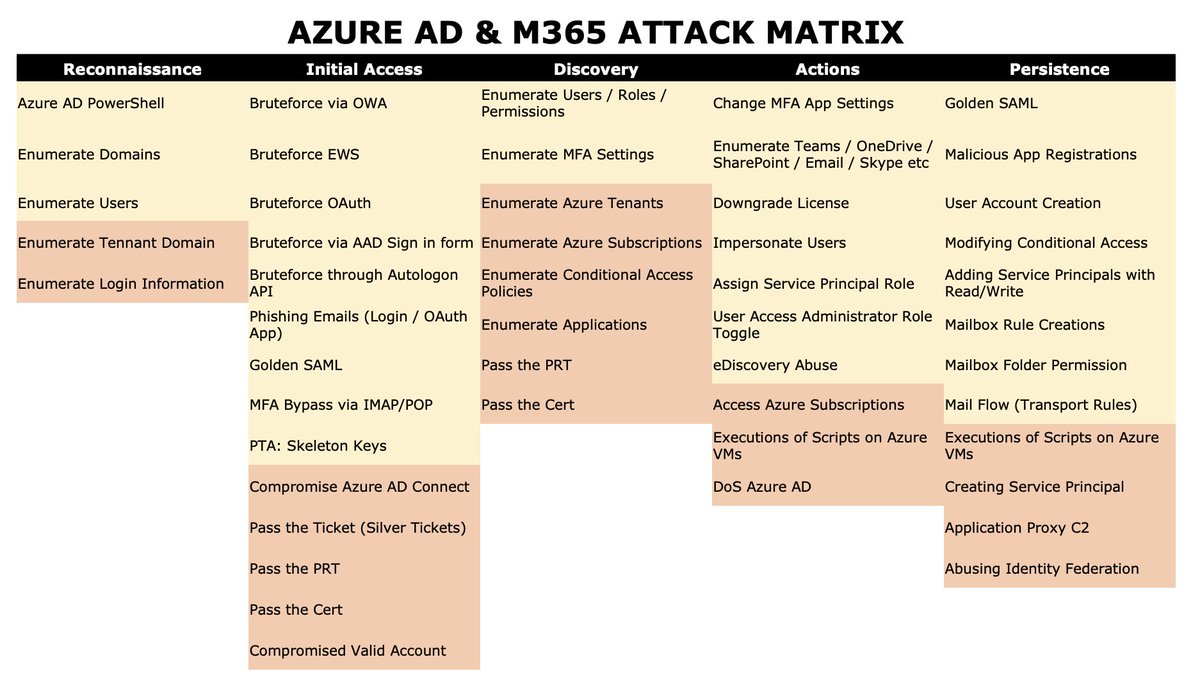
1\ I updated the attacks on #AzureAD and #M365 matrix! Now includes hybrid/non hybrid techniques used for impersonation, persistence and access including:
> Silver Tickets
> Pass the PRT / Cert
> Service principal abuse
> Identity federation abuse
https://t.co/lX9T4pSAaJ
Ppl often release attack tools & write a paragraph on defensive possibilities.
We’re changing that.
Here’s a post on the thought-process involved in building a MySQL-dump canarytoken (touching on its SQL injection application)
https://t.co/PY8IGM0LAa
(It’s worth the read)
MS Office ActiveX CVE-2021-40444 summary:
🎯No macros needed - normal detections & mitigations fail.
🎯No word from MS on patch ETA
🎯Can in some cases be executed in Explorer Preview mode. (RTF older O365 client?) - h/t -https://t.co/naT9iwfJ67
1/x
#RemotePotato0 new release!
Now you can also grab and steal the NTLMv2 hashes of every user logged on a machine from an unprivileged user!
✅ works fully local - no network interaction (except win 2019)
✅ ntlm related
✅ won't fix
Windows in 2k21
cc @decoder_it