🔥At @offensive_con, we showcased three different attack scenarios on ARM UEFI and beyond:
1️⃣CWE-125: OOB (memory leak) with GetVariable/SetVariable pattern.
2️⃣BRLY-2022-033: GetVariable Stack overflow (UsbConfigDxe).
3️⃣LPE to SMM from DXE by design.
https://t.co/9F0P3uPhN3
⛓️The widespread use of UEFI on ARM devices notably expands the attack surfaces within TrustZone and beyond, raising security concerns
💥REsearch: "A Dark Side of UEFI: Cross-Silicon Exploitation" presented the new ARM attacks at @offensive_con
🔬Slides: https://t.co/c7MR1YmSSa
🎙️Join us tomorrow for the #BHASIA talk: "The Various Shades of Supply Chain: SBOM, N-Days, and Zero Trust." /cc @hughsient @immune_gmbh
⛓️We have some fascinating data insights regarding firmware supply chain security.
https://t.co/TRRAR8xFNh
Heading to the Qualcomm Product Security Summit and @Offensive_con this week
🔥A Dark Side of UEFI: Cross-Silicon Exploitation
@Binarly_io REsearch going to present new ways of exploiting Qualcomm Snapdragon 8 devices with UEFI-specific flavor. Stay tuned!
@flothrone@yeggorv
⛓️Design issues are the worst!
🔥Given the current revocation architecture, we are facing the serious challenges of accommodating over 2300+ bootmgr binaries within DBX Revocation List (limited space left in EFI Variable storage).
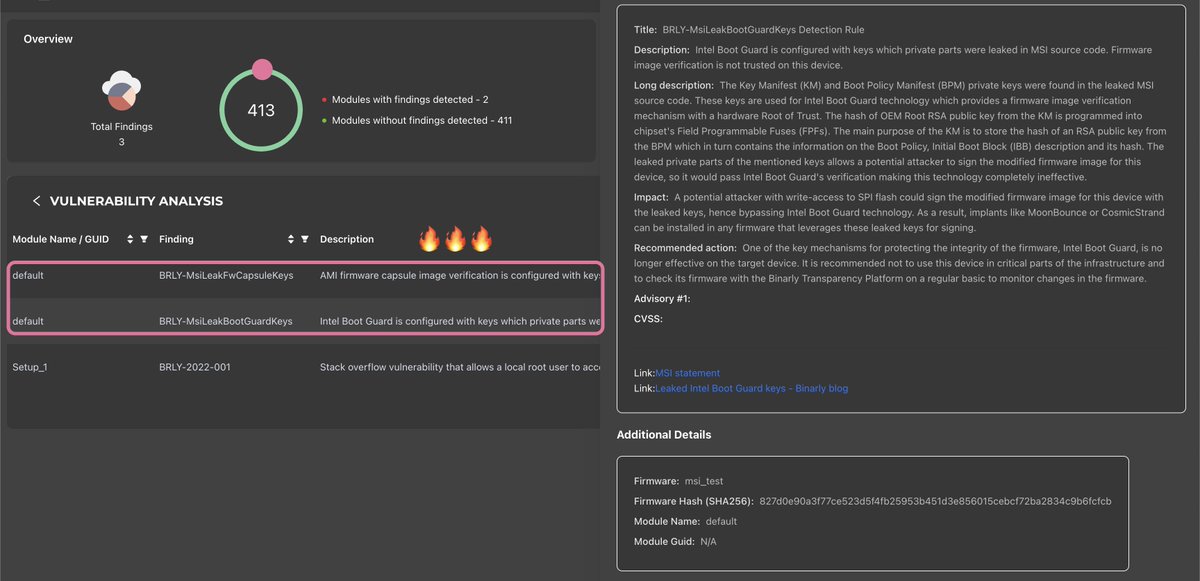
🔥New finding! We have confirmed that previously leaked Intel BootGuard private keys from Lenovo/LCFC in September 2022 are still relevant for numerous devices in the field (Lenovo, Supermicro, Intel ...).
⛓️https://t.co/WfyIYgLBmD
🔬FwHunt: https://t.co/PHvxAdXzOL
🔥The bxt_dbg_priv_key.pem, which is the Intel OEM Platform Key (Orange Unlock) obtained from an MSI leak, has been detected on devices from HP, Lenovo, AOPEN, CompuLab, and Star Labs.
🔬Stay tuned for more updates as the investigation continues.
https://t.co/WBedhuzPNJ
⛓️Diving deeper into MSI leak, it has been discovered that one of the leaked keys (bxt_dbg_priv_key.pem) is associated with Intel Orange or OEM Unlocked.
🔥Based on Intel documentation, it appears to be more powerful in comparison to Boot Guard keys.
https://t.co/mtABZNgalM
Security researchers on claiming on Twitter that an Intel Boot Guard OEM Private Key was leaked as part of the MSI data breach https://t.co/KRQAYukEgp @matrosov@intel@binarly_io
⛓️Confirmed, Intel OEM private key leaked, causing an impact on the entire ecosystem. It appears that Intel BootGuard may not be effective on certain devices based on the 11th Tiger Lake, 12th Adler Lake, and 13th Raptor Lake. Our investigation is ongoing, stay tuned for updates.
⛓️Digging deeper into the aftermath of the @msiUSA data breach and its impact on the industry.
🔥Leaked Intel BootGuard keys from MSI are affecting many different device vendors, including @Intel , @Lenovo, @Supermicro_SMCI, and many others industry-wide.
🔬#FwHunt is on!
⛓️Recently, @msiUSA announced a significant data breach. The data has now been made public, revealing a vast number of private keys that could affect numerous devices.
🔥FW Image Signing Keys: 57 products
🔥Intel BootGuard BPM/KM Keys: 166 products
🔬https://t.co/uwqWIU9xhR
Come join us at our #cybersecurity seminar next Thursday!
As the Founder and CEO of @binarly_io, @matrosov will discuss #research areas of interest to help the industry recover from repeatable failures in firmware #security.
Tune in on zoom: https://t.co/MWf9VkSq7p