The FLARE team now freely distributes its quality reverse engineering and malware analysis educational content at https://t.co/bGCIjBfD3C. Launched with:
- Malware Analysis Crash Course
- Go Reversing Reference
- Intro to TTD
I built an open-source library of 700+ cybersecurity skills for AI coding agents -- covers DFIR, threat hunting, cloud security, and more https://t.co/vM5SgmXCrO
Step-by-Step Malware Analysis Lab Setup
A malware🦠 analysis lab lets you safely study malicious software in an isolated, controlled environment. Here��s how to set one up.
🔥🔥Check This Out🔥🔥
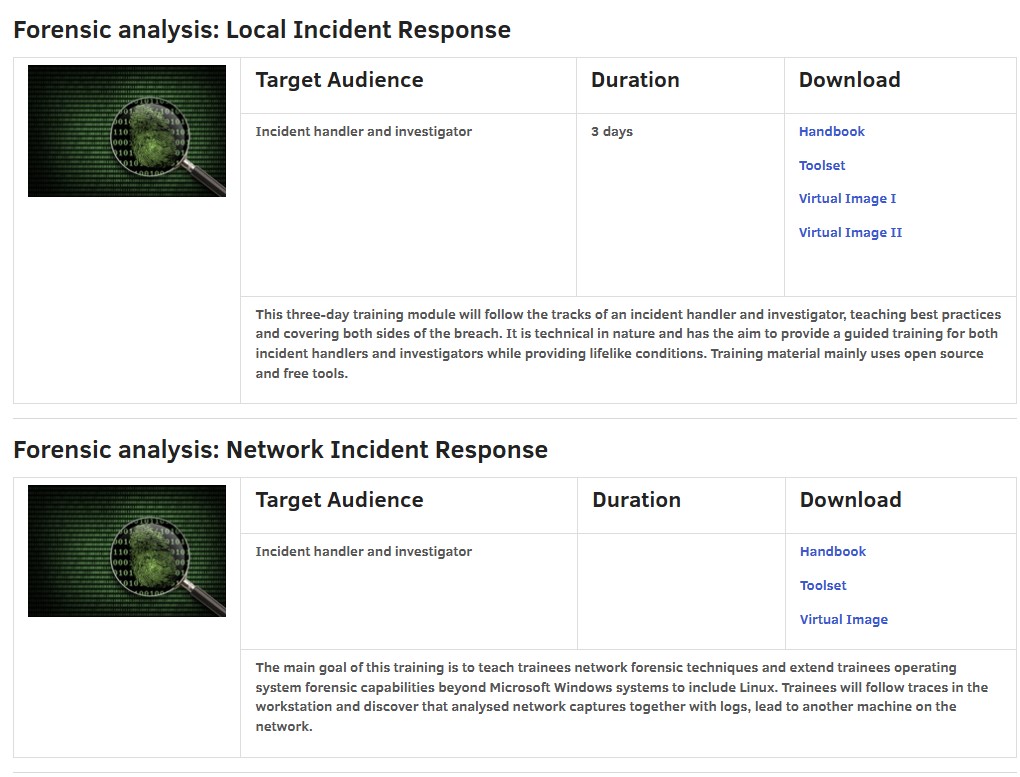
Today's Training Tuesday Highlight is ENISA!
They offer FREE hands-on training material related to:
- Digital Forensics
- Incident Response
- Mobile Threats Incident Handling
- Network Forensics
- Malware Analysis
and more!
Link: https://t.co/OyGkoR2fuT
#DFIR #IncidentResponse #DFIRDivaTTH
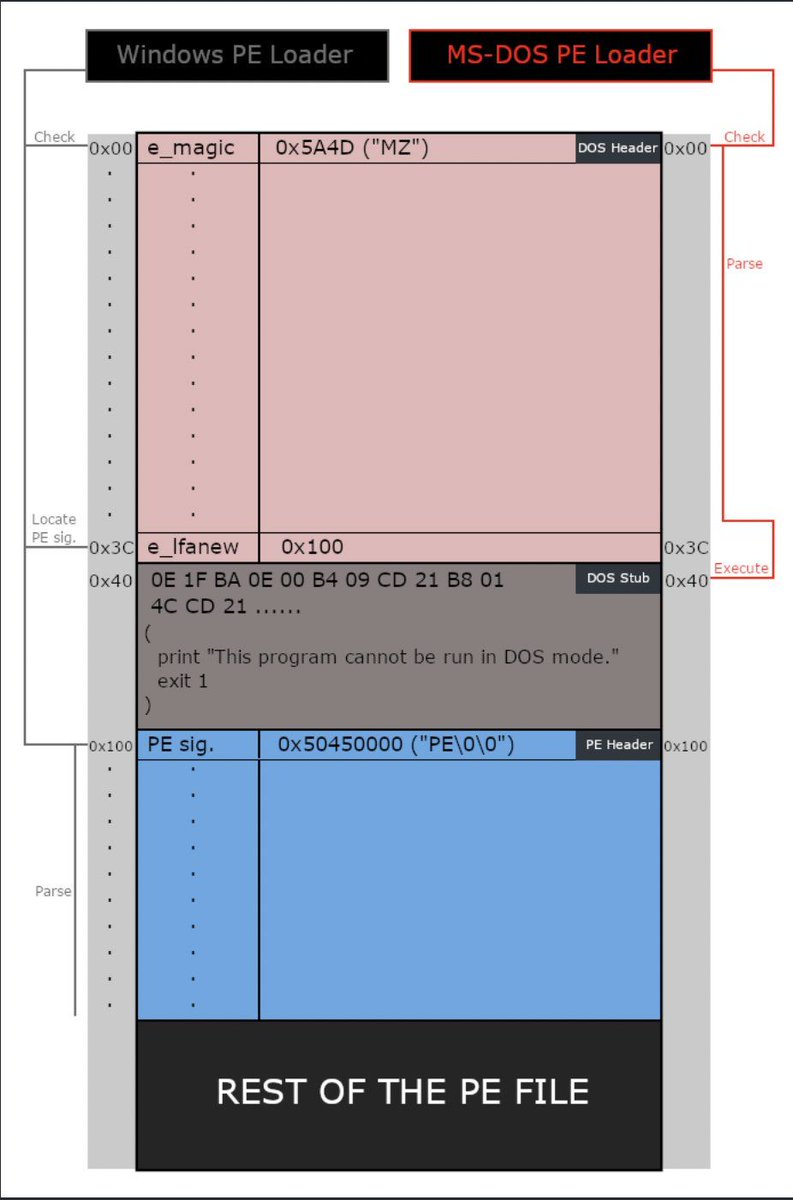
Great series by @Ahm3d_H3sham on PE file format
https://t.co/LxEJeLLmcX
https://t.co/mZNoapgO2i
https://t.co/fFjMAVo7bO
https://t.co/SjgSqlBrFW
https://t.co/EtcJ7TqX7S
https://t.co/xey0z0O7PI
https://t.co/qnyEWtxju1
#infosec#cybersecurity
The Linux Forensics section of the Free & Affordable Training Site has been updated: https://t.co/8iu7QcY0n8
Scroll down on the homepage to view other categories:
https://t.co/Mr0kzVApxo
#DFIR
Reverse backdoor written in PowerShell and obfuscated with Python. It generates payloads for popular hacking devices like Flipper Zero and Hak5 USB Rubber Ducky, and changes its signature after every build for evasion. https://t.co/0hknD7NW8r
The first article in Exploiting Reversing (ER) series is available (109 pages):
https://t.co/2Hv0XLMuqU
Thank you @ilfak and @HexRaysSA for supporting me in every project.
#reversing#windows#idapro
I've updated my #Antivirus Event Analysis Cheat Sheet to v1.11
- more #hacktool identifiers
- more #ransomware identifiers
- had to break the layout to fit everything on a page but I think it's still clear enough
https://t.co/bkH9yYmdYb
Hello Hackers,
Hope you are doing great
Got a lot of DMs about beginner-friendly #tryhackme learning path
I am sharing a #tryhackme path which includes mostly all types of basic boxes, you can follow this if you are interested in cybersecurity
[Thread]🧵👇
Uploaded all my Offensive Security & Reverse Engineering (OSRE) course labs (docx) to my repo found below. Most of them have very detailed instructions and should be great to get you started in Software Exploitation. 1/n
#Offsec#SoftwareExploitation#RE
https://t.co/D5oBtDNOnS