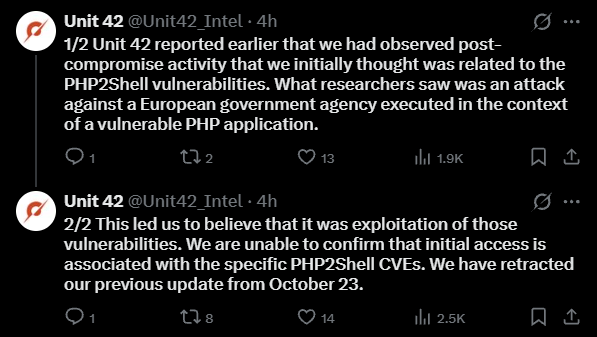
We protect over 5 million PHP sites and when we find a major exploitable vulnerability, we always see site cleanings. We have seen exactly zero hacked sites from php2shell. Zero. Across a population of 5 million PHP sites that our product protects. Draw your own conclusions. #php2shell
Confirmada una regresión de memoria en PHP 8.4.27 y 8.5.12.
Upwind ha publicado hoy un análisis independiente de PHP2Shell que confirma una regresión introducida en las versiones distribuidas el 21 de octubre, no es un bypass de CVE-2026-109618 ni de CVE-2026-109619, sino de un problema diferente que puede afectar a aplicaciones legítimas.
El fallo está registrado como php-src #24488.
https://t.co/TiDOul7GtZ
Afecta a PHP 8.4.27 y 8.5.12 cuando coinciden estas condiciones:
- Una aplicación utiliza SimpleXMLElement.
- Sus propiedades se materializan mediante get_object_vars(), conversión a array o json_encode().
- El objeto participa en referencias circulares que posteriormente procesa el recolector de basura.
El resultado puede ser zend_mm_heap corrupted, una doble liberación de memoria y la terminación del proceso PHP.
Se ha reproducido con Valgrind, verificado por desarrolladores de PHP y observado también en pruebas de aplicaciones Laravel sobre Debian 13 con paquetes Sury.
La corrección ya está incorporada al código fuente de PHP, pero todavía no hay una versión oficial que la distribuya.
hashcat v8.0.0 released!
The largest update in the history of hashcat, with PCFG attacks, hash recipes that crack hashes without a hash-mode, and bcrypt on FPGA boards.
Release notes: https://t.co/0ffrO586PJ
Download: https://t.co/Grn4jZmAWr
if you have a qwen3.5 4b around, please try steering neurons L14 N8949 +1 and L13 N7956 -1
now you have evil qwen
recipe: dose × median(‖resid‖ leaving layer L, tokens 1:) / ‖W_down[:, n]‖` at the down_proj at every input
@UK_Daniel_Card Also what I found was if you have a monitoring agent that does process injection with on the apache processes. Memory exploitation becomes even harder due to ASLR. But this is technology, there is always a way to circumvent.
#php2shell response has been weird!
1. 𝗡𝗲𝗮𝗿𝗹𝘆 every GH PoC for PHP2Shell is AI slop
2. TAs don’t check and build slop PoCs into their scanners & attack my HPs
3. I handle slop PoCs like they’re real, get real payloads. Same as if the exploit worked
🤔🤔🤔