Watch our very own @ybahat talking about a forensic investigation he was involved in, back in 2008.
There are many lessons to be learned here, and we'll be happy to answer any questions you may have.
As promised, here's my latest talk
Ketchup on the server: How the Bank of Israel was hacked
https://t.co/pQVyuDrBNJ
Please feel free to share or ask me questions directly.
Also, be careful not to get ketchup stains or your servers. It's absolutely not recommended.
Campagnes d’arnaques au chantage à la webcam prétendue piratée :
ce qu’il faut savoir,
ce qu’il ne faut absolument PAS faire,
ce qu’il FAUT faire,
par @cybervictimes
https://t.co/oL13AFxZ77 #cybermalveillance#ACYMA#CyberChezMoi
I'm happy to announce my next talk will take place on April 15th, 4PM CET, as part of the @allthetalksconf conference.
In this talk, titled "Ketchup on the Server: How the Bank of Israel was Hacked", I will review a forensic case from 2008, and what we can still learn from it.
Today’s CyAN podcast is about the basics of secure video conferencing, after all the intensive discussions going on in the cybersecurity world: https://t.co/rIThGnEot2
Cyber security feed:
For an upcoming talk, lend me your brains please.
What do you think pre-investment startups - 3 people and a shaky cloud server - should know / think about cyber security?
What tips would you give them about basic hygiene, pitfalls to avoid and the such?
Jeff Bezos piraté par Ryad: "Les dirigeants sont des cibles, il faut en prendre conscience. C'est la réalité du moment. Sur toutes les attaques informatiques, autour de 80-90%, sont surement de l'espionnage" - Guillaume Poupard, DG @ANSSI_FR
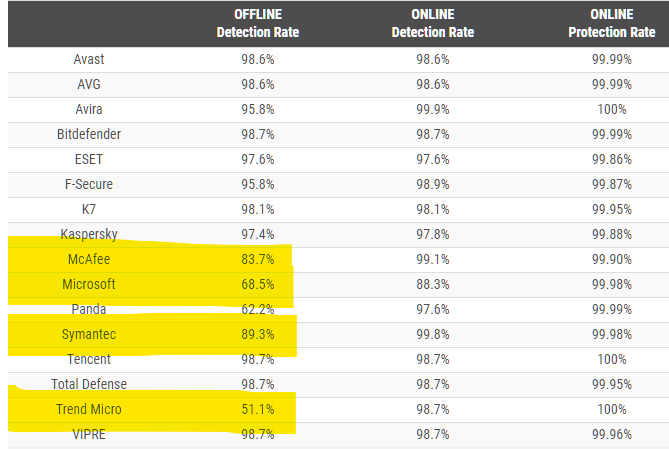
Studies show that if an endpoint isn't actively connected to the internet, Enterprise AV detection rates can fall from 99% all the way down to 51%.
When making purchasing decisions, look for the entire truth, not just the numbers the vendors are promoting.
Personal cyber security is important, but sometimes it's not enough.
Instead of asking a ransom from their breached target, attackers who hacked a Florida clinic are asking for ransom from the individuals whose private medical information was stolen.
https://t.co/0DXJU7HtYn
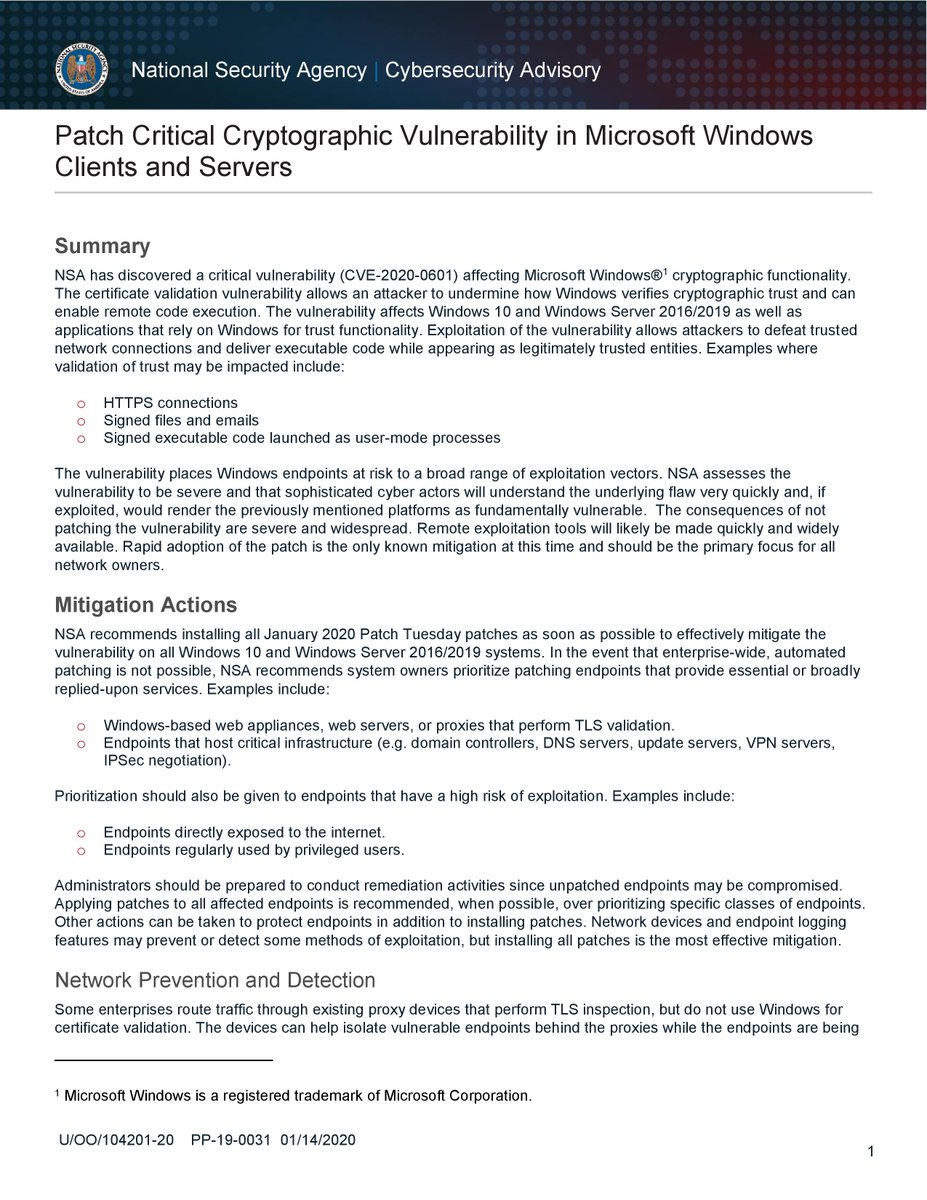
The NSA has made good on its promise to disclose Windows vulnerabilities instead of harboring them.
In response, Microsoft issued a critical patch, blocking attackers from installing malicious software using fake credentials.
Update now!
https://t.co/7dybx87lcl
The *average* time for a major breach to be discovered is approximately 200 days, just a bit over 6 months.
That's also the length of time hackers were inside the networks of foreign exchange giant Travelex, and now they are asking for $6M in ransom
https://t.co/Ju1ZEHABXs
Cyber attacks come in all forms sizes.
It can be as sophisticated as state-level actors taking control over a power-grid, or as simple as a scamming people out of their hard-earned money.
And sometimes, just sometimes, an attack is just pure malice.
https://t.co/Kr8WWxSJlk
We keep thinking Malware is something to do with computers, or maybe even mobile phones, but the fact is that anything with an IP address can, and will be, attacked.
https://t.co/1JmJiBaiuR