The next precedence is to exploit vulnerabilities then report the breach to triage is this the new norm @intrigiti @Hacker0x01 program rules state dont exploit triagers demand you exploit
jumpserver v5.0.0 — JumpServer is an open-source Privileged Access Management (PAM) platform that provides DevOps and IT teams with on-demand and... https://t.co/mIRhzNDdgR
Do you want to learn how to fuzz like a real expert, but don't know how to start ?
If so, this is the course for you!
10 real targets, 10 exercises. Created by github staff member.
Github:- https://t.co/wtW5l1QehQ
If your AI security tool is flooding you with false positives, try this. I started using it a lot after @pashov told me to try it a while back.
https://t.co/2oZKqgKOC0
I run it right after I get a ready AI report. So far it has never removed something that was actually valid 🫣
Feedback: https://t.co/Me8TAuaY4f
It is not perfect and it is not my whole system.
It is one small piece I wanted to make easy for hunters to run locally before sending another report into a triage queue.
Open to feedback, especially on false positives and false negatives.
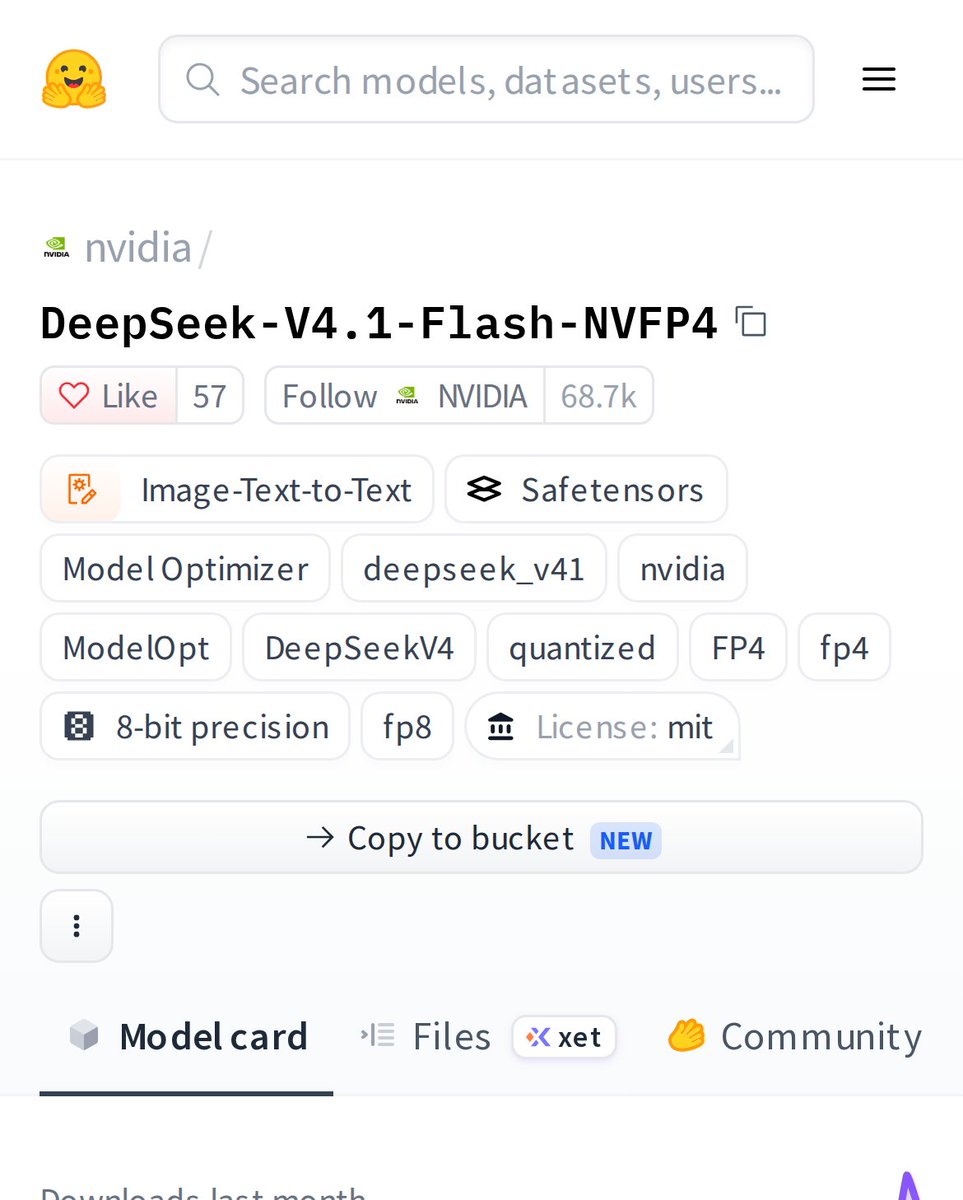
NVIDIA just dropped DeepSeek-V4.1-Flash-NVFP4, a quantized version of DeepSeek V4.1 that fits in 4-bit precision. This means faster inference, lower memory, and it handles both images and text. A big win for running powerful AI on modest hardware.
Did you know that some exposed Google Maps API keys also have access to Gemini Models? 👀
geminiHunter by @devploit is a new tool that finds and validates exposed Google Gemini API keys across web assets, source maps, Wayback snapshots, and even Android APKs. It deduplicates findings, checks if keys are actually valid, and even attempts bypass variations on restricted ones! 🤠
Check it out! 👇
https://t.co/r38vApfDei
Just released ntlmscout, a single-file, zero-dependency recon tool for internet-exposed NTLM endpoints. Combines the best parts of several tools all in one.
Decodes the Type-2 challenge across HTTP/SMB/MSSQL/mail/LDAP/RDP, recovers the internal IP (OXID, IIS host-header, cert SANs), flags DCs, and sprays lockout-safe.
Hack the Planet!
https://t.co/8V8tJM9bzi