@lfreiredev Sure checkout @LoganOpSec‘s YouTube.
I know he is still new in the space but, his content is for hacking along.
It’s motivational to listened to him and his thought process while you are also trying to solve your own bugs too.
Just search live Bug Bounty hunt on YouTube
People like Nahamsec are nolonger worth following in my opinion.
We put much trust in them because they pioneered bug bounty but truthfully speaking he is one of the most confusing content creators in the space.
Focus on people who live hunt 💯 on their videos or watch POCs.
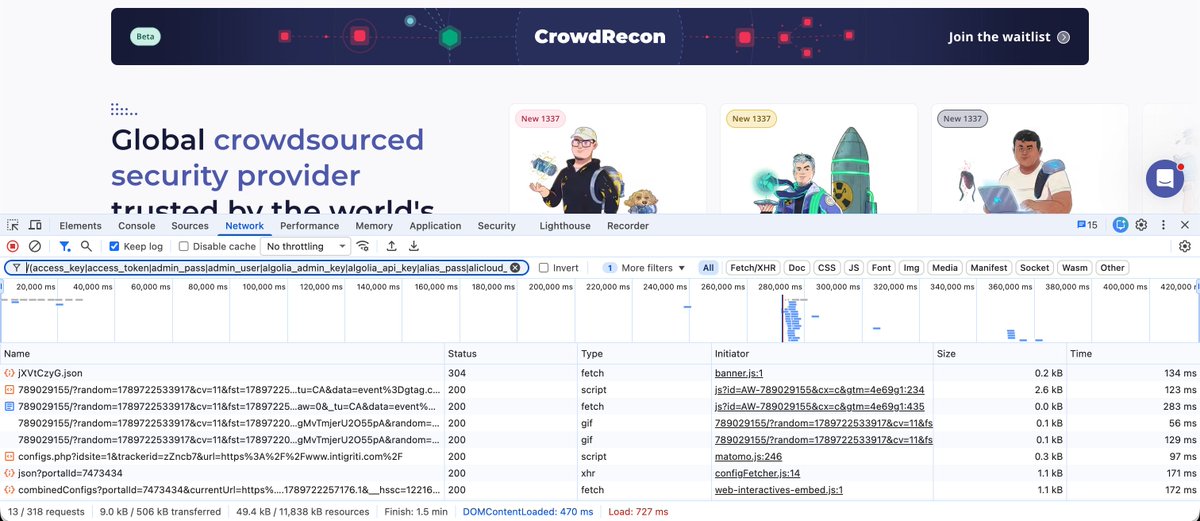
Manually searching through HTTP traffic for leaked credentials can be tedious... 😓
Leaked-Credentials by @h4x0r_dz gives you a ready-to-use regex that catches API keys, secrets, tokens, and database passwords across 100+ common patterns. It works directly in Chrome DevTools, Firefox and Burp Suite! 🤠
Check it out! 👇
https://t.co/9oiSV0TcBE
Before running dozens of recon tools, I always check a few common files that can reveal valuable information about a web application.
Some of the files I look for:
📄 robots.txt
🗺️ sitemap.xml
🛡️ security.txt
📦 .git/
⚙️ .env
📘 Swagger/API Docs
💾 Backup files
#bugbountytips
People like Nahamsec are nolonger worth following in my opinion.
We put much trust in them because they pioneered bug bounty but truthfully speaking he is one of the most confusing content creators in the space.
Focus on people who live hunt 💯 on their videos or watch POCs.
In my last 3 months of returning to bug bounty, I have been very impressed by @Hacker0x01 triage across programs and live hacking events. Considering the massive amount of both valid and slop reports they are getting, they have been precise, patient, and empathetic in the reports.