i gave prePO 50 dollars in 2022 and got 51 back in 2026
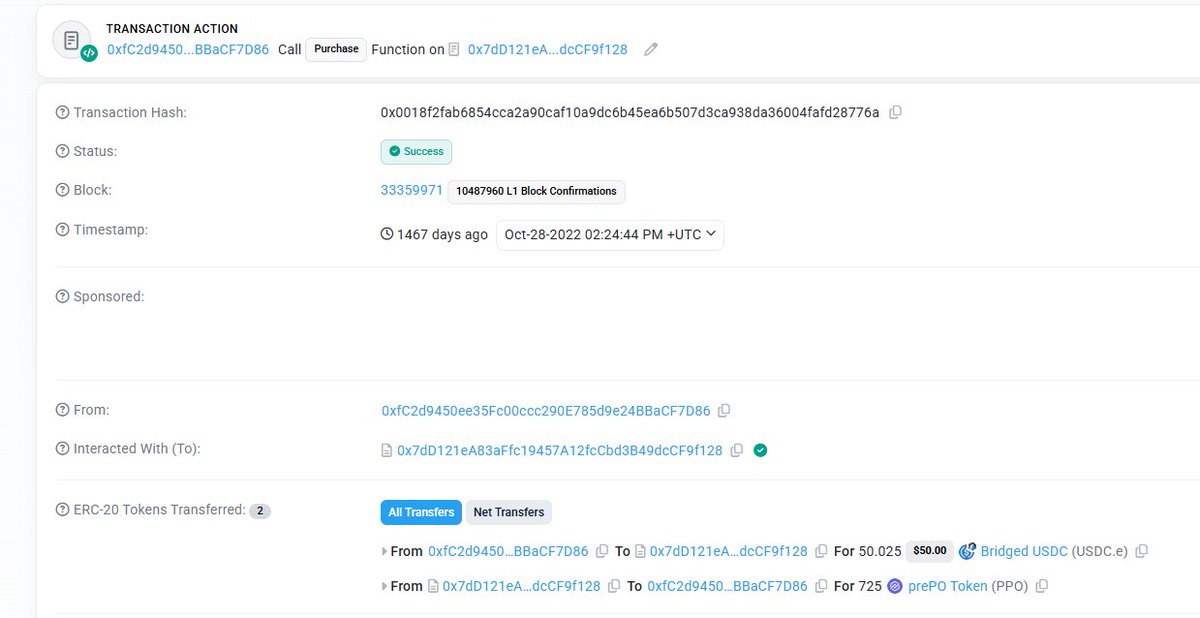
found my original purchase transaction. october 28, 2022, i sent 50 USDC to the prePO contract on arbitrum and received 725 PPO. four years later, one transaction shows up in my wallet: 725 PPO out, 51 USDC in. that's my refund. one dollar of profit for four years of holding.
the project didn't fail. @prepo_io took the money, built the product, rebranded to @PreStocks, moved to solana, brought in new investors, and kept going. the early holders who funded the start weren't invited. we sat on a dead arbitrum token while the team started over on a new chain with a new name. then they sent back our original buy-in and called it a refund.
think about what that means. they had my money for four years. used it to build. launched a new version of the project with new people. and returned exactly what i put in, to the dollar, with zero upside. no token in the new project, no equity, no interest. just the 50 bucks i gave them in 2022 minus the time value of those 50 bucks over four years of inflation.
i funded a startup in 2022. the startup succeeded. and my return was zero. if you held PPO and got your money back, reply with what you paid and what you received. i want to know if everyone got their original amount or if the math is more creative than that.
THEY TOOK $650K FOR A TOKEN YOU COULD NEVER SELL. NOW THEY’RE PRESTOCKS
prePO raised that money on arbitrum in 2022 and 2023, and to me what happened next is a slow rug. the team rebranded into @PreStocks and now sells tokenized OpenAI.
the old prePO app, where you could check your PPO balance, is a 404 and so is their github org. @prepo_io is locked, and the medium post with the public sale results has been deleted. so tonight i went through everything that’s still online, before more of it disappears.
the presale was september 20, 2022. 193 wallets put in $390,244 at $0.06 and it sold out in 17 minutes 50 seconds. the public sale ran after that at $0.069 to $0.20 and took another $250k. seed investors had paid $0.013, so retail paid between 4.6x and 15x the seed price, and both public rounds together bought about 1% of the supply while the team kept 25%.
from day one PPO was non-transferable. the FAQ, which is somehow still up, sold this as a feature: holders would vote to unlock transfers, estimate H2 2023, even though the same page admitted voting wasn’t possible yet. one of their own conditions for unlocking was “the return of a crypto bull market”. btc went past $100k and PPO is still sitting in the same wallets it was bought into.
while the token was frozen they kept selling it. in january 2023 they opened PPO bonds on bond protocol at $0.05 and called it 50% off a $0.10 “market” price, for a token that had no market at all. by january 23, 70 wallets had bonded $8,458, and one of them posted their dashboard that night: 2,002 PPO, market value $0.
march 2023 brought early deposits for their $ARB pre-token market. your ETH went in as wstETH with 2% taken on the way in and 3% on the way out, and the “rebates” were paid in PPO. people who deposited in march paid that 2% out of their ETH before the fees were scrapped in june.
in may 2023 they ran a “transferability survey” and paid for the answers in more PPO. in october they sunset v1 and promised a v2, and the medium blog ends there.
august 2025, prePO comes back as PreStocks on solana. their launch post lists “freely transferable” as a selling point and doesn’t mention PPO once. i looked for any migration or statement about PPO holders and found nothing.
today 1,225 wallets still hold PPO on arbiscan at $0, and no exchange lists it. PreStocks advertises 100K+ holders and $1.75B in volume. it’s the same company with the same founder, it just changed chains and left the first holders behind.
@RWAFoundation_ lists @PreStocks among its 18 member teams, next to securitize and maple. before you put your name next to a team, you might want to ask what happened to the last people who trusted it.
@XavierEkkel, you raised that $650k. what’s the plan for PPO holders? if there isn’t one, say so. and put the deleted post back up so people can see what they were sold.
about $6 billion left Binance wallets in roughly 20 minutes. then i read the contract you accepted to keep money there.
Binance says it will cover client losses. i could not find that obligation anywhere in the Terms of Use (27 Oct edition) or the privacy notice (July). what i did find:
1. a hack is on the list of losses Binance excludes. clause 35.2 rules out liability for a "security breach", and the contract defines that to include a cyberattack on Binance itself. the promise to cover you exists in press statements.
2. they can freeze your withdrawals for an "incident" (16.4). they did, for days after 29 Oct. they can freeze your whole account for any reason and keep the reason secret (25).
3. Binance can send you a bill and set the amount itself. if it suspects you of fraud or market abuse and says that cost it money (a credible allegation from a third party is enough), the sum is due immediately (34). everything in your account is pledged against it (11), they can sell it without telling you, and if it falls short you owe the rest. the custodian may also refuse to hand your assets back at its sole discretion (11.1.7), though ADGM client asset rules override that.
4. if Binance goes bankrupt, you help pay for the bankruptcy. your coins sit in shared wallets with Binance's own, and Binance is a beneficiary of that pool (8.4.1). process costs come out of its share first, then out of client assets pro rata (8.4.2).
5. stay away for 90 days and your coins can turn into an IOU. an email goes out, and 30 days of silence later they may convert your assets, move the account to a third party, charge a monthly fee and turn your ownership into a "contractual claim" (24.3). the email counts as delivered even if it bounced (40.2).
6. good luck suing. 80 days of complaints, 90 days of negotiation, then arbitration in Abu Dhabi with three arbitrators, no fast track, no class action, everything confidential, UAE courts waived (36-39). law firms who analysed it say small claims may not be worth filing.
7. the privacy notice lists a face scan matched to your passport, your voice and video, phone book contacts, salary and, where the law asks for it, criminal record data. call recordings are kept up to six years. "US monitors" appointed under Binance's plea agreements get account and transaction data.
save this if you keep money on an exchange.
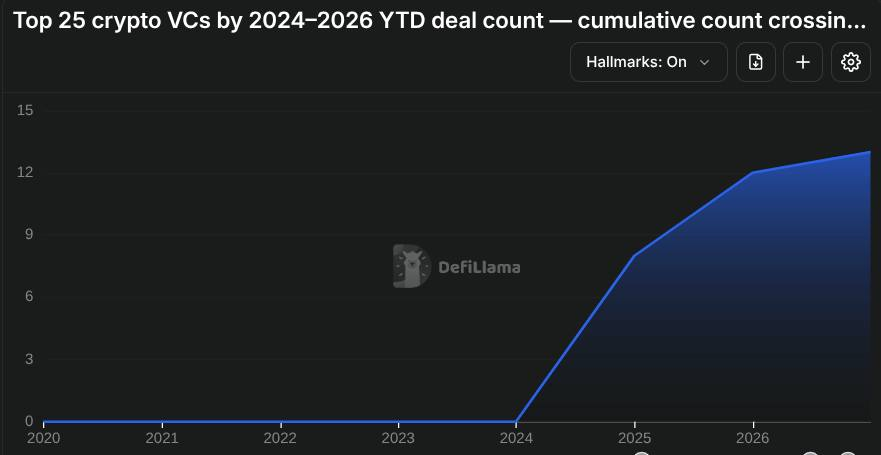
half of the top crypto VCs are already investing outside of crypto.
for two years now, crypto venture funds have been quietly putting money into projects that have nothing to do with crypto. AI startups, biotech, plain fintech. the graph shows it clearly - the share of crypto funds diversifying out of the industry has been growing steadily, and nobody was paying attention.
only about 50% of leading crypto VCs remain purely in crypto. the rest are already halfway out the door.
and here’s what makes it worse. these same funds keep raising new crypto-focused vehicles, keep taking LP money under a crypto thesis, keep showing up at conferences talking about the onchain future. but when it comes to actually deploying capital, more and more of it lands nowhere near a blockchain. investors are paying for crypto exposure and getting a portfolio where half the positions are regular startups with regular equity.
when the most informed people in the industry start quietly repositioning - that tells you more about crypto’s real prospects than any onchain metric ever could.
hackers stole $6.4 billion from Binance. but the craziest part isn’t the amount - it’s that they rehearsed the robbery in plain sight. test transactions for a couple of dollars, right on Ethereum, on a public blockchain. nobody even blinked.
Bloomberg broke down the timeline minute by minute. when the test code ran without a hitch, the hackers pulled the trigger and launched the attack across multiple blockchains simultaneously.
but then comes the part that still doesn’t sit right in my head. while the hackers were draining wallets, Binance kept sending fresh money into them. hackers empty a wallet, the exchange automatically refills it, hackers empty it again. for a period of time Binance was literally topping up its own robbery. spoon-feeding the robbers.
Binance co-founder Yi He was at home in Abu Dhabi at the time. according to Bloomberg, she found out about the breach scrolling her X feed before bed. imagine: you open twitter for the night and see billions of dollars flowing out of your own exchange in real time.
within minutes Binance assembled a 100-person crisis team. the FBI, the U.S. Secret Service, blockchain analysts around the world all joined in. meanwhile some employees were reportedly worried not about the exchange - but about their annual bonuses.
but the most chilling detail surfaced later. the hackers used valid permissions. to the blockchain every transfer looked fully legitimate. not a single transaction was flagged as suspicious. just authorized operations calmly moving billions out of wallets the system still trusted.
the $6.4 billion heist didn’t start when the billions began moving. it started days earlier, with transactions worth a couple of dollars - too small for anyone to notice.
by the time it got scary, the blockchain was still saying: authorized.
fifty signatures from Binance 14
on October 29 at 20:24 UTC, almost 168,000 ETH and 63 more tokens, including 1.6 billion USDT, left the Binance 14 hot wallet in a single transaction. about two and a half billion dollars in total. the fee for this withdrawal was under a dollar, I made a point of checking.
a lot of people are about to write that EIP-7702 is to blame for all of it. I spent some time in the explorer, and going by the chain, the hole is in Binance's signing. 7702 is just the most convenient tool here.
timeline
- Oct 28: gas for the operator address comes in from Tornado Cash
- Oct 29, daytime: the operator deploys a sweeper contract with their own address hardcoded into the bytecode. any other caller gets rejected
- 20:20 UTC: a type 4 transaction attaches this code to Binance 14
- 20:24 UTC: sweep() is called, three and a half minutes later
inside the delegation
the most interesting part sits inside the delegation transaction: fifty Binance 14 signatures for fifty consecutive nonces.
the exchange wallet sends several transactions a minute and the nonce keeps moving, so the attacker brought a whole batch to guarantee one would match at the moment it landed in a block.
one signature can be phished. a batch of fifty, signed by my rough estimate 10-20 minutes before the attack, means on-demand signing access: to the key itself or to the service that signs on the exchange's behalf.
a second argument points the same way. less than half a minute after the sweep, another exchange hot wallet, Binance 16, sent 28,000 more ETH to the same address. a plain transfer with no 7702 at all, and judging by the gas, it looks like a routine withdrawal from the exchange.
why 7702 then
if the signatures can be obtained anyway, why bother? a hot wallet lives in a constant stream of withdrawals. start sending 64 separate transfers from it and you end up fighting the exchange's bot for every nonce.
with delegation one matching signature is enough. after that the wallet is run from your own address, and the exchange's queue doesn't get in the way at all.
the delegate code also has a function that calls execute() on a smart wallet on behalf of Binance 14. a quarter of an hour later, another 780 million USDC went to the same address from Hot Wallet 34, the wallet Binance 14 controls.
the 1 ETH detail
the detail from the bytecode I like least: the sweeper leaves exactly 1 ETH in the wallet. I suspect that's so the exchange bot doesn't fall over on an empty balance and make noise too early.
the bot didn't fall over. at 20:33 Binance 14 calmly sent someone a 29 USDT withdrawal, while deposits kept flowing into an address that still had someone else's code hanging on it.
where things stand
- on Ethereum it adds up to almost three and a half billion dollars, more than two Bybits
- the receiving address also holds assets on Arbitrum, Optimism, Base and Avalanche
- the ETH has already moved on, almost 200,000 in one transaction to a fresh address
- about a billion USDT was still in place when I looked, so a lot depends on how fast Tether moves
- Binance hasn't confirmed anything yet
I'm not seriously considering the planned wallet migration theory. an exchange doesn't top up its own service addresses with gas through Tornado.
receipts are in the first reply, check them yourself. if you find something on-chain that I missed, drop it in the replies and I'll add to this.
onchain options start with sellers
the onchain options piece has the same retail trader everywhere: buys cheap lottery tickets and waits for a 10x. in crypto people already get that from memecoins and 50x perps, so that seat is taken. that’s why i think the first big wave of onchain options comes from the other side of the trade, with people selling them.
that’s how i got in. since april i’ve run 28 ETH positions on @ryskfinance, mostly weeklies, and collected around $3.6k in premium. you pick a price and a date, market makers send a quote. the premium lands upfront, no greeks required.
the article says the market needs non-toxic taker flow and quietly assumes the taker is a buyer. on an RFQ venue the taker is whoever comes in for a quote. when i sell a call, i’m the taker. for a market maker that’s a comfortable client: i want my price and my date, and i’m not hunting for holes in their pricing.
options will grow once people stop calling them options. to a normal person a sold put is a limit buy that pays you while you wait. from late august i sat on a limit like that at 2350 for three weeks, it never filled, and i got about $640 in premium. a covered call is a take-profit that pays you upfront. packaged like that, the product makes sense to anyone who has ever placed an order, and all the math stays with the market maker.
the most underrated lever here, i think, is the calendar. the article shows that every new expiry day on the S&P brought new demand, and it took Cboe 17 years to get to an expiry on every trading day. crypto never closes, so you can list expiries every hour and on sundays. whoever first makes short-dated expiries on majors easy to trade gets their own version of the 0DTE boom.
options are also the only crypto product that doesn’t empty out in a bear market. in an uptrend people buy calls, in a downtrend they sell puts to buy lower. perps and memecoins go quiet in those months. you can see it in the article’s Robinhood numbers: options revenue stays steady while crypto revenue jumps around from quarter to quarter. for a protocol that’s income that doesn’t depend on the market phase, and DeFi has almost no sources like that.
i think the first big flow will come from treasury companies. they need a reason to trade above the value of their coins, and options on the stack bring in income without selling a single coin. Hyperion DeFi, a public company with a HYPE treasury, announced an options vault on Rysk for its own balance sheet back in february. once dozens of treasuries do the same, retail will walk into liquidity that’s already there.
that's literally the point of the post tho - the bot detects VMs and kills the malicious behavior inside them. u test it in a sandbox, looks clean, feels safe. move it to ur real machine and that’s where it flips.
but yeah you're 100% right, free bots shouldn't touch ur main machine ever. problem is most ppl don't know that. they download, run it, get rekt
claude code just decompiled a sniper bot someone shared in a telegram chat. the bot works. buys fast. does everything it promises. and every 30 minutes sends your clipboard contents to a server in singapore.
someone dropped an "alpha bot" in a private chat. free. source code on github, 200 stars, english readme, even a demo video. they said it's open source. they said they checked it.
i didn't run it. i opened claude code and typed: "decompile this binary. show me every network call it makes. show me what files and system resources it accesses. show me everything that doesn't relate to its stated functionality."
70 seconds later - a report.
the bot does exactly what it claims. connects to a node, monitors the mempool, sends transactions. clean. well-built. works.
plus three things not in the description.
first: on launch the bot scans standard wallet paths - metamask, phantom, rabby, keystore files. doesn't open them. just checks if they exist. and sends the list of found paths to an external endpoint. POST request. once on launch. silent.
second: every 30 minutes the bot reads the clipboard and sends the contents to the same server. the clipboard. where you copy your seed phrase, private key, wallet address, password. every 30 minutes.
third: the bot checks whether it's running in a virtual machine or sandbox. if yes - those three functions don't activate. it behaves perfectly clean. meaning anyone who "tested" it in a VM before using it saw a clean binary. on a real machine - different bot.
i checked the server. cheap VPS, registered 3 weeks ago. domain behind cloudflare. whois closed. same IP running a bot for another "alpha chat" with a different name and a different readme.
no blockchain scanner will show this. it's not on-chain. it sits on your machine and waits for you to copy something valuable.
what to do before running any bot, script or tool from a chat:
1. open claude code → drop the file → paste the prompt below
2. if the bot accesses wallet files or reads the clipboard - delete immediately
3. if there's a VM detection check - that's not bug protection, that's anti-detection
4. "open source" ≠ safe if the build doesn't match the source code in the repo
i checked 4 bots from telegram chats in the last month. 1 clean. 1 with telemetry that could pass as analytics. 2 - with direct clipboard exfiltration and filesystem scanning.
both had "source code" on github. both had stars and forks. the builds didn't match the source.
save this prompt. next time someone drops an "alpha bot" - run it before launching. 70 seconds. cheaper than a new wallet.
prompt:
decompile this binary. show the full list of network calls — where, how often, what data it sends. show all filesystem access — what paths it reads or checks, especially standard crypto wallet directories (metamask, phantom, rabby, keystore). check if it reads the clipboard, and if so — what it does with it. check if there's virtual machine or sandbox detection, and whether behavior changes depending on the environment. compare the build to the source code in the repository if one is listed — does it match. show everything that goes beyond the stated functionality.
THE LEGAL RUGPULL, STEP BY STEP
1. boost tvl
the move: points and airdrop promises pay people to park capital on the chain. @blast passed two billion in deposits this way.
what you see: a leaderboard with a multiplier that changes every week, and a tvl number that only goes up.
2. pump the token
the move: the tvl screenshot becomes the pitch. @berachain had about three billion locked within weeks of its token going live.
what you see: the same chart in every feed, and a price for a token that doesn’t exist yet.
3. vc exit
the move: investors hold tokens bought at a fraction of the listing price, and the listing is the first moment that gap is worth anything.
what you see: nothing. their wallets don’t announce. you find out from the unlock schedule, if the docs publish one.
4. dump on retail
the move: unlocks arrive while attention is still high, and people who bought at the listing take the other side.
what you see: a green launch day, then a red line that slides every month while the chat says “buy the dip”.
5. recycle capital
the move: the proceeds go into the next project, and the next points program opens.
what you see: a new chain with new multipliers and the same pitch.
the charts, for anyone who wants to check. @blast is about 99% under its token high. @berachain went from about three billion in tvl to under two hundred million. @LineaBuild’s token is about 95% off its high.
the case i keep looking at is @AbstractChain. 400k users and over 300 million transactions, and it shuts down on december 15 because costs are higher than revenue. it has no token, so steps 2 to 5 never got a chance to run. the team behind it, @iglooinc and @LucaNetz, is closing it.
nobody in steps 1 to 5 promised a drop, so every one of them can end differently. i look at the charts above before i look at the multiplier.
THEY TOOK $650K FOR A TOKEN YOU COULD NEVER SELL. NOW THEY’RE PRESTOCKS
prePO raised that money on arbitrum in 2022 and 2023, and to me what happened next is a slow rug. the team rebranded into @PreStocks and now sells tokenized OpenAI.
the old prePO app, where you could check your PPO balance, is a 404 and so is their github org. @prepo_io is locked, and the medium post with the public sale results has been deleted. so tonight i went through everything that’s still online, before more of it disappears.
the presale was september 20, 2022. 193 wallets put in $390,244 at $0.06 and it sold out in 17 minutes 50 seconds. the public sale ran after that at $0.069 to $0.20 and took another $250k. seed investors had paid $0.013, so retail paid between 4.6x and 15x the seed price, and both public rounds together bought about 1% of the supply while the team kept 25%.
from day one PPO was non-transferable. the FAQ, which is somehow still up, sold this as a feature: holders would vote to unlock transfers, estimate H2 2023, even though the same page admitted voting wasn’t possible yet. one of their own conditions for unlocking was “the return of a crypto bull market”. btc went past $100k and PPO is still sitting in the same wallets it was bought into.
while the token was frozen they kept selling it. in january 2023 they opened PPO bonds on bond protocol at $0.05 and called it 50% off a $0.10 “market” price, for a token that had no market at all. by january 23, 70 wallets had bonded $8,458, and one of them posted their dashboard that night: 2,002 PPO, market value $0.
march 2023 brought early deposits for their $ARB pre-token market. your ETH went in as wstETH with 2% taken on the way in and 3% on the way out, and the “rebates” were paid in PPO. people who deposited in march paid that 2% out of their ETH before the fees were scrapped in june.
in may 2023 they ran a “transferability survey” and paid for the answers in more PPO. in october they sunset v1 and promised a v2, and the medium blog ends there.
august 2025, prePO comes back as PreStocks on solana. their launch post lists “freely transferable” as a selling point and doesn’t mention PPO once. i looked for any migration or statement about PPO holders and found nothing.
today 1,225 wallets still hold PPO on arbiscan at $0, and no exchange lists it. PreStocks advertises 100K+ holders and $1.75B in volume. it’s the same company with the same founder, it just changed chains and left the first holders behind.
@RWAFoundation_ lists @PreStocks among its 18 member teams, next to securitize and maple. before you put your name next to a team, you might want to ask what happened to the last people who trusted it.
@XavierEkkel, you raised that $650k. what’s the plan for PPO holders? if there isn’t one, say so. and put the deleted post back up so people can see what they were sold.
HODLING DROPS: HOW I GOT PLAYED BY MY OWN NUMBERS
all the numbers in the last post are real, and so are the screenshots. the conclusion drawn from them is false, and it's built exactly the way most provocative posts about holding get built.
out of twenty drops, one grew. $HYPE from @HyperliquidX: 438.8 tokens, claimed on november 29, 2024, worth $878 at claim, $18k now. the other nineteen were worth about $9.8k at claim, and now all of them together come to about $1.3k, down 87%.
so the $19.3k "if you just hold" is 93% one token. take hype out and holding turns into $1.3k against the $9.8k i took by selling at claim. the same profit-taking i was mocking wins by about seven times over.
the rest is bent with wording. the $44.7k "at the peaks" adds up tops the tokens hit in different months, that sum never sat in a wallet for a single day. the $34k "left on the table" only comes out if you sell each of the twenty exactly at the highs. the line "didn't need to guess" hides exactly what did need guessing: which one of the twenty would take off. and i never gave a single example of those advisers with untouched bags.
i won't draw a conclusion from one wallet, that's the same trick in the other direction. @KeyrockHQ analyzed 62 drops from 2024, after 90 days only 8 were in the green. i have 1 out of 20. these stats don't sit well with me, so i'll keep selling at claim from here on.
I SHOULD HAVE DONE NOTHING
twenty drops since 2023, and i handled every one of them the same way: claimed and sold straight into stables. the chats call this locking in profit, and i spent three years locking it in.
today i finally did the math. at claim, all those drops brought me $10.7k. the exact same tokens would be worth $19.3k today, and at the peaks it was $44.7k.
so the "lock it in" advice i got in every chat cost me $34k. and it's most often handed out by people whose own bags sit untouched.
even if you forget about the peaks, just by not touching anything i'd be $8.6k richer. that didn't take any guessing or sitting on charts, not hitting sell would have been enough.
I SHOULD HAVE DONE NOTHING
twenty drops since 2023, and i handled every one of them the same way: claimed and sold straight into stables. the chats call this locking in profit, and i spent three years locking it in.
today i finally did the math. at claim, all those drops brought me $10.7k. the exact same tokens would be worth $19.3k today, and at the peaks it was $44.7k.
so the "lock it in" advice i got in every chat cost me $34k. and it's most often handed out by people whose own bags sit untouched.
even if you forget about the peaks, just by not touching anything i'd be $8.6k richer. that didn't take any guessing or sitting on charts, not hitting sell would have been enough.
CLOSING THE @AAVE TOPIC. THIS IS THE FOURTH POST AND THE LAST ONE.
almost a month ago i dropped $30k into them. the money went to their contract, and the dashboard is still empty. i wrote to support, and ever since it feels like i'm begging them for my own money. not a single answer of substance, nobody ever explained what happened. then the whole thing fizzled out.
i'm not posting the tx, otherwise my dms fill up with "crypto recovery specialists", and that's the last thing i need.
for a protocol with billions in tvl my $30k is probably pocket change. one real person would have been enough, someone to open an explorer and answer like a human being. in a month they couldn't find one. a fucking month.
to me aave is now in the same category as scams, just with nicer design and louder partners.
if you've got serious money sitting there, keep in mind: something breaks, and you're dealing with it on your own. i've been dealing with it for a month.
go fuck yourselves, @aave.
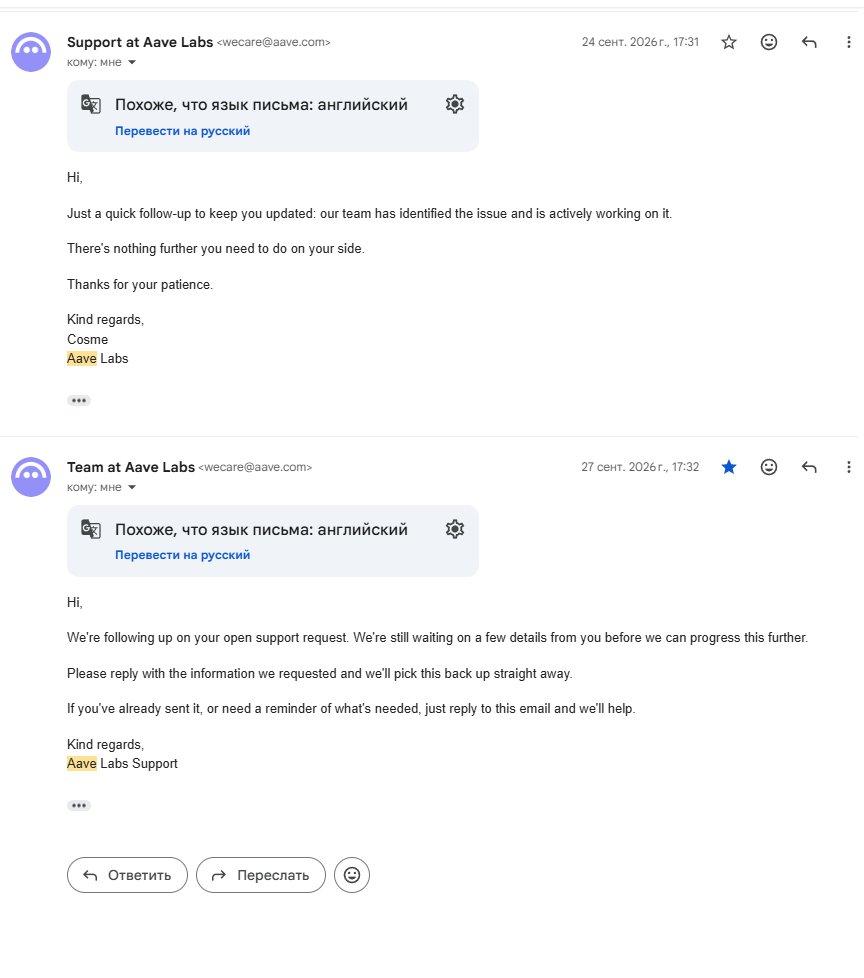
ALMOST A WEEK AGO @aave TOLD ME THEY'D IDENTIFIED THE ISSUE, WERE WORKING ON IT, AND DIDN'T NEED ANYTHING ELSE FROM ME. NOW THEY'RE SAYING THE EXACT OPPOSITE.
First support said the case had been escalated. Then they sent another update saying the issue was identified and the team was actively working on it. I was explicitly told there was nothing else I needed to do. After that, almost a week of silence.
Now I get another email saying they're "still waiting on some information from me before they can move forward." What information? Where was that request? And why does it directly contradict the previous messages in the same ticket?
This case involved roughly $30 000, and at this point the biggest problem isn't response time. It's that the support thread looks like nobody actually owns the case. One message says they have everything and are working on it, then a week later another message acts like the delay is on me.
If a case involving around $30k can sit like this for a week and support can't even keep its own story straight, that's completely fucked.