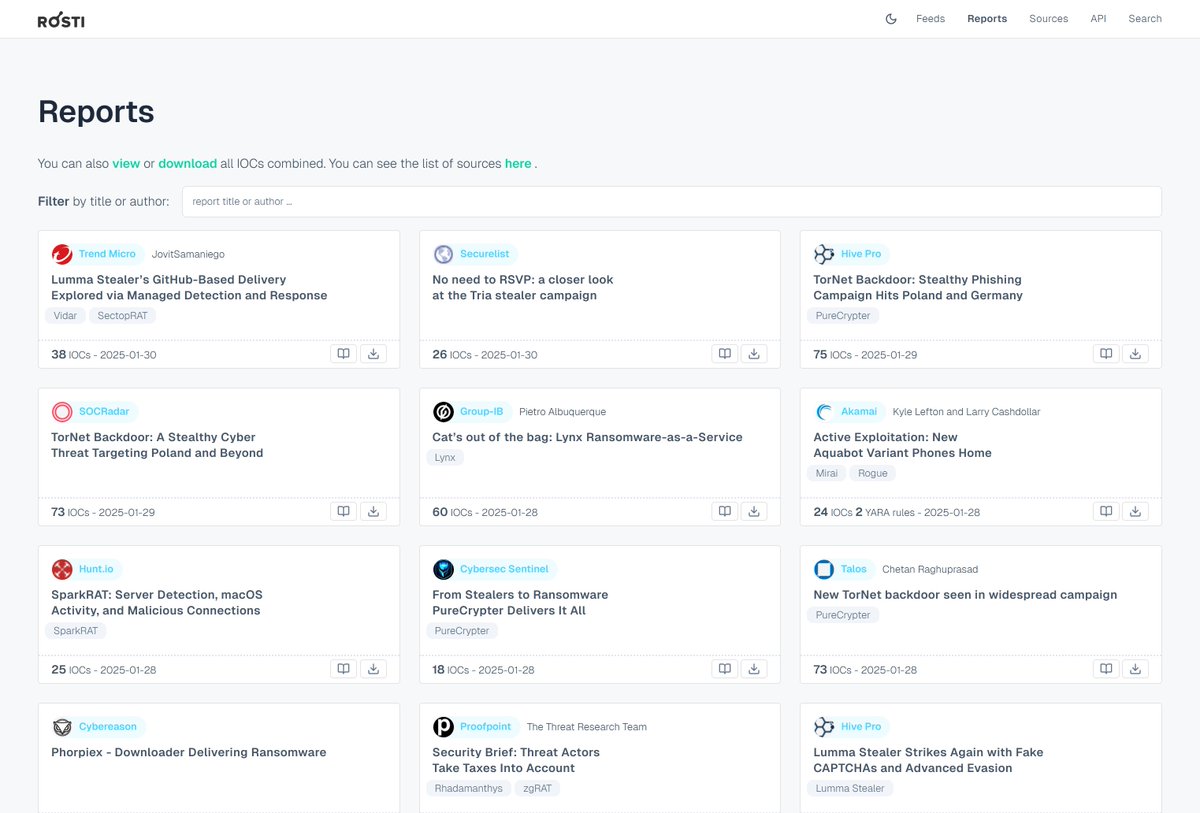
Today, I'm releasing the first version of a small web 🚀: https://t.co/WZMsLWpGEK
It provides IOCs and YARA rules collected semi-automatically from public blog posts and reports of almost 200 cybersecurity sites.
I hope it proves useful to some of you ... 🙏✨ #ThreatIntel
I recently found some samples of maybe #APT37
Some may already been found
9b4476ffe7e72188015aa161f4400944
9fe0552634db234c6f5e396d51c7fd6f
103d4dd7479f7b1a2f3cab2657432535
dbb3ff5a5738c0443b48d9aa055d6950
c6e567d2d7763682a98ac9267bb9dd73
471b83a6714d8b69bc9e5c84408013ca
1/n
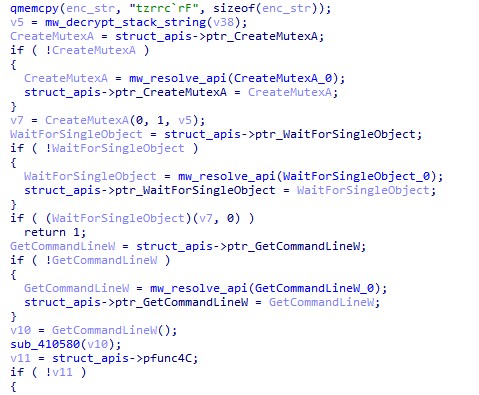
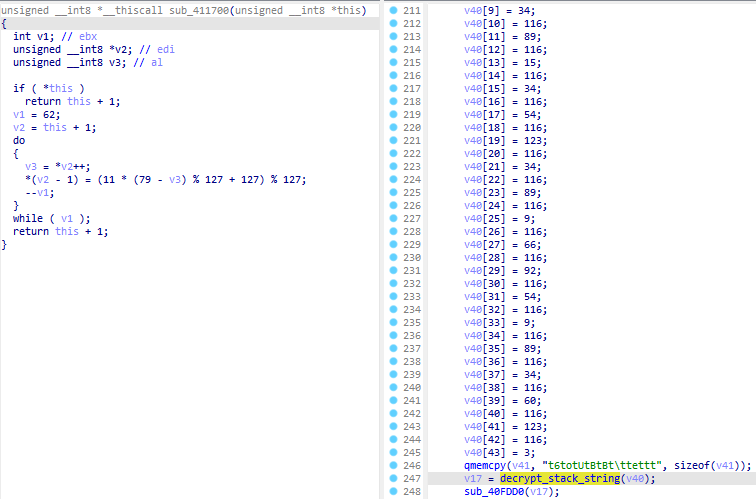
Here, IDAPython script to count how many times a function has been called. High call count usually points to decryption functions in obfuscated malware.
https://t.co/5hlcdYxgjI
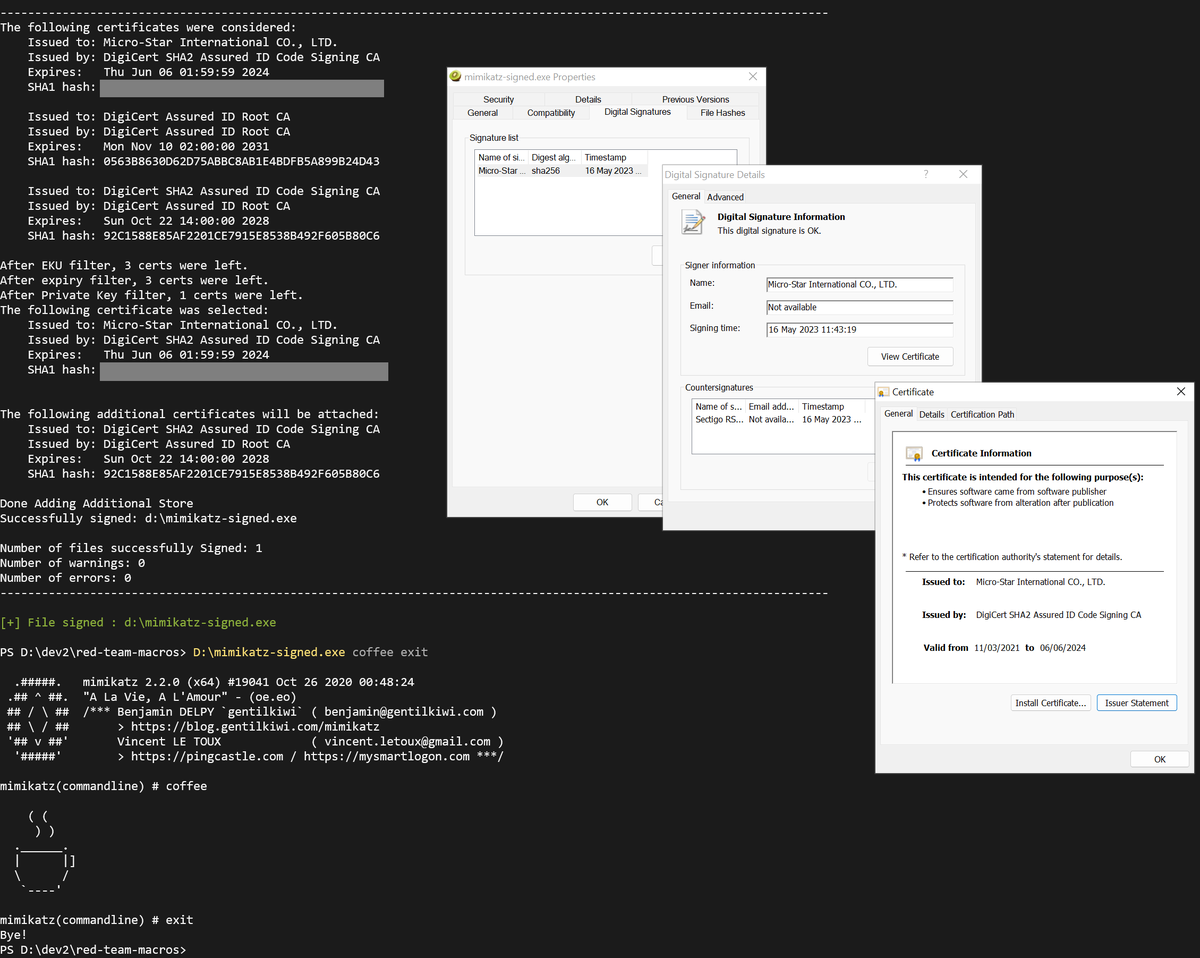
☢️MSI leaked code signing certificate already abused by Threat Actors (expires in 2024).
I've collected 9 recently leaked certificates to cover up in upcoming Modern Initial Access training sessions🔥
https://t.co/vhHKWITJaC
👾 Already weaponised in Red Macros Factory 1.8!
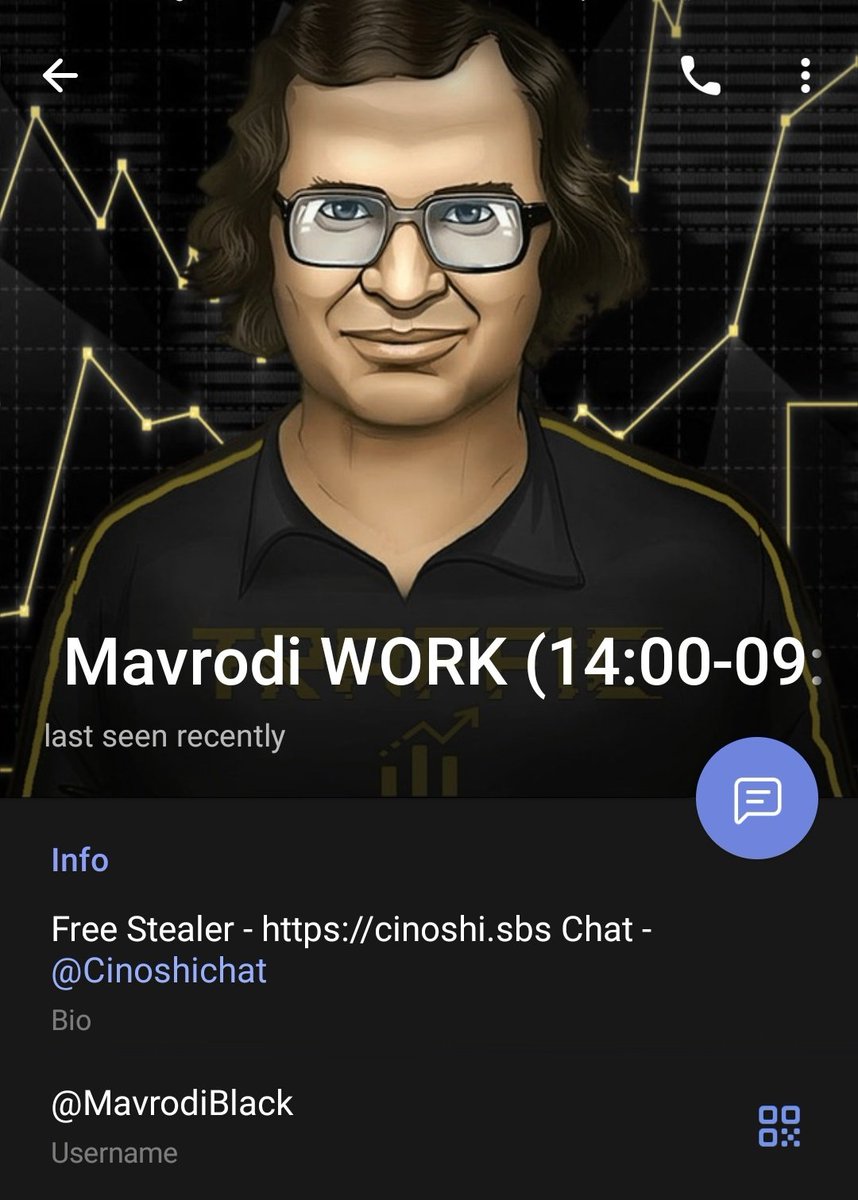
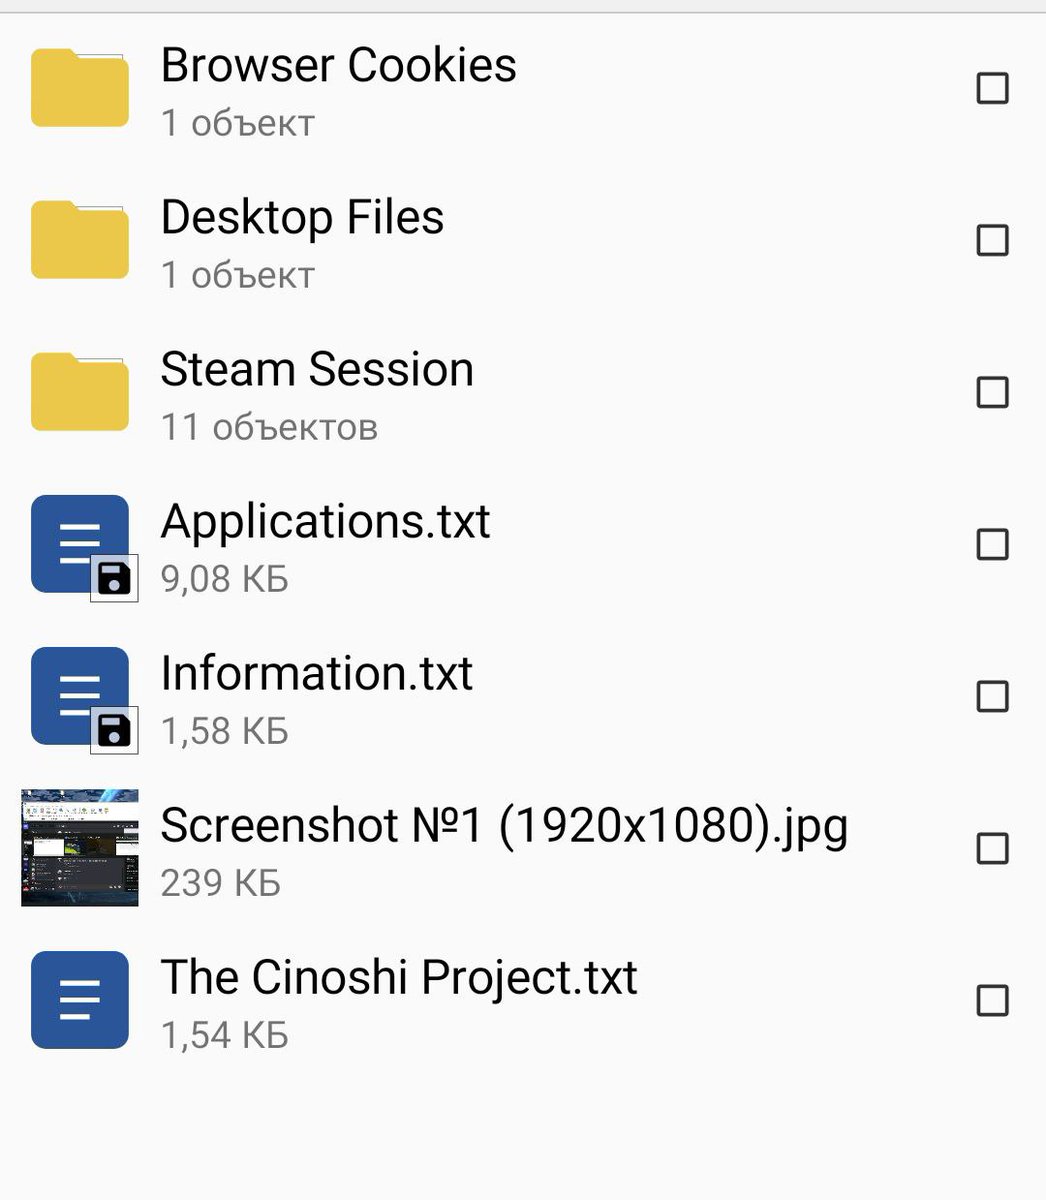
@Gi7w0rm The first Loader Stealer could be Cinoshi Stealer, a new stealer/botnet/clipper/miner project apparently born now in May.
mavrodiblack seems to be one of his administrators and user of Cinoshi services
I will leave some Intel pics from his tg chat.
Panel at cinoshi[.]sbs
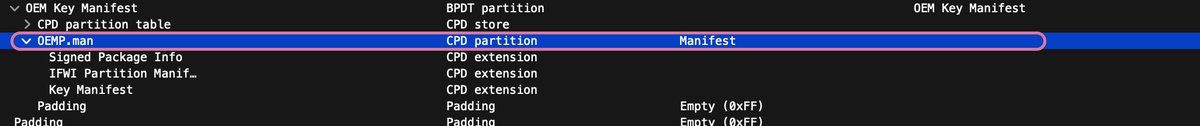
⛓️Confirmed, Intel OEM private key leaked, causing an impact on the entire ecosystem. It appears that Intel BootGuard may not be effective on certain devices based on the 11th Tiger Lake, 12th Adler Lake, and 13th Raptor Lake. Our investigation is ongoing, stay tuned for updates.
Windows 10 offline admin creation? 😈
Why not?!
Everything happens through built-in offlinelsa and offlinesam DLLs. Official, but not very documented.
Enjoy the source code and the compiled exe, as usual: https://t.co/BNp9kaLnkr
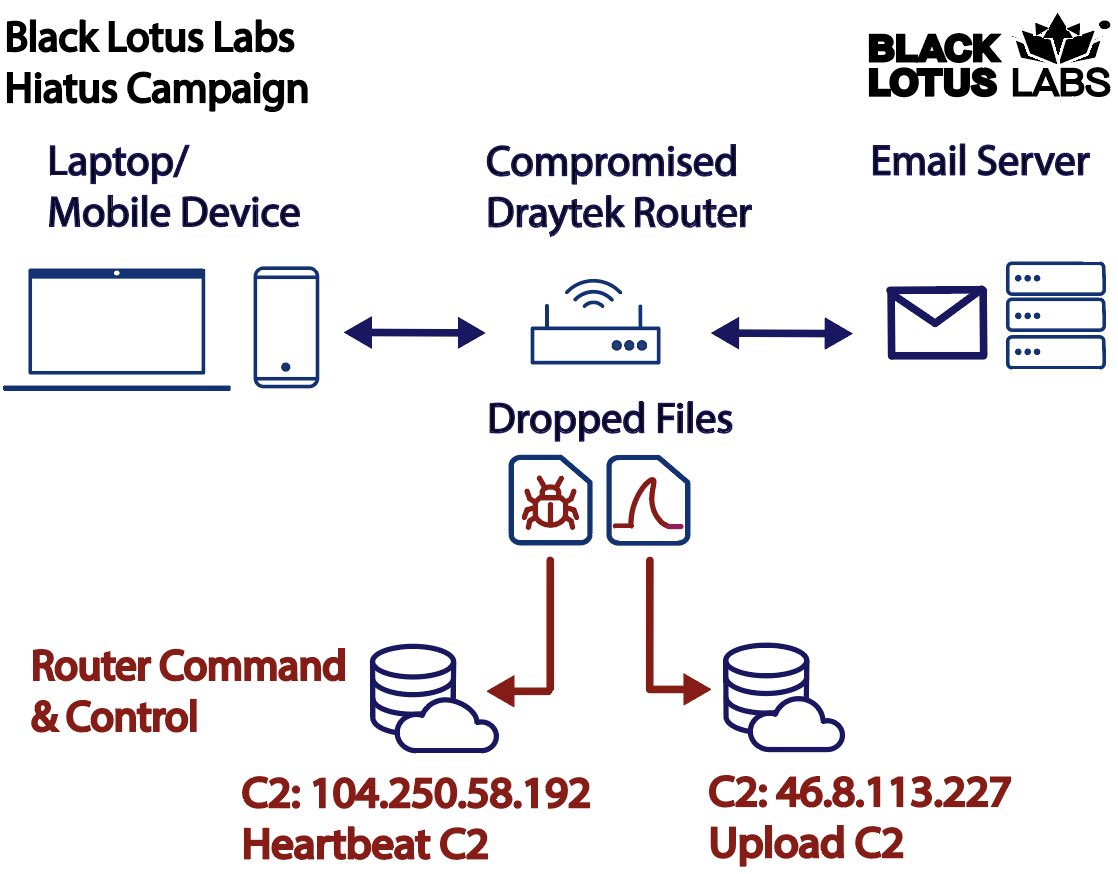
Today we’re releasing research on brand new activity cluster we’re calling Hiatus. This actor has an affinity for target routers, to gather pcap and use as covert infrastructure.
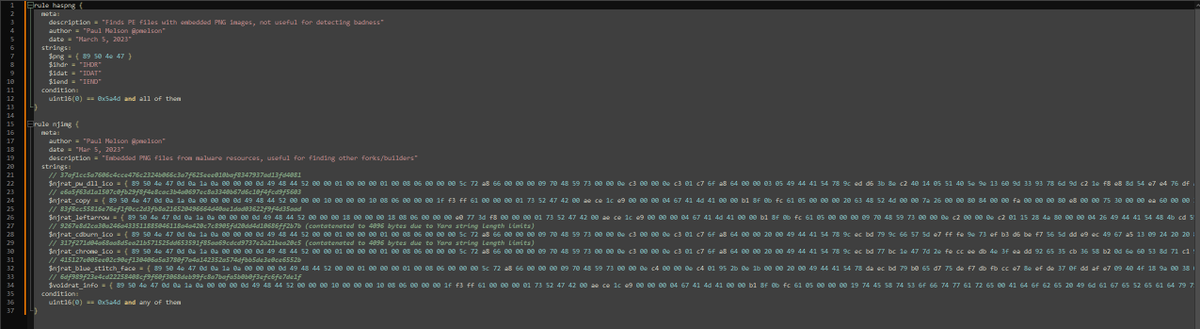
Looking at a new sample today led me down a rabbit hole of PNG images embedded in malware. I wrote a little Python to extract PNG files from malware @ScumBots has scraped, stacked the images, and made the common ones into a Yara rule for hunting. #100daysofyara
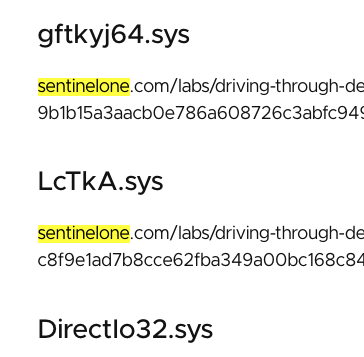
With lots of help from @_josehelps and @mattnotmax, I present a sneak peak of the LOLDrivers Project -
Ability to search, access resources, hashes, CSV and json downloads as well.
Coming soon. We're that much closer to a one stop driver shop.
I have published a highly technical debunking whitepaper called:
A brief note on "Exonerating Morocco disproving the spyware"
(I'm sorry for the lack of pet photos, but that just wouldn't be professional)
https://t.co/XgpDsLi8c4
ICYMI: Mandiant CTO spoke about threat hunting inside Naftogaz, the largest national oil company of Ukraine 🇺🇦, because “wiper malware” kept reappearing
I spent ages looking for this today… 1/2