The audit log query that most SOCs have never run:
AuditLogs
| where TimeGenerated > ago(30d)
| where OperationName in (
"Consent to application",
"User registered security info",
"Admin registered security info",
"Register device")
| summarize Count = count()
by OperationName, bin(TimeGenerated, 1d)
| render timechart
This shows the daily volume of the three most common persistence operations in your Entra ID tenant. MFA registrations, OAuth consent grants, and device registrations — exactly what an attacker does in the first 30 minutes after compromising an identity.
Run it now. Save the baseline.
When the next identity compromise alert fires, you’ll instantly see whether today’s activity is normal… or 4× the daily average.
Without this baseline, every investigation starts with “Is this normal?”
With it, you start with “This is anomalous — let’s move.”
If you came to SOCON, you may have seen the fireside chat on Ouroboros (if you weren't too busy counting my "urm"s 😝). The blog post is now live, detailing how we can use Dev-Tunnels for lateral movement, and allow pivoting from GitHub/Entra ID access. https://t.co/yb1jl1xkgV
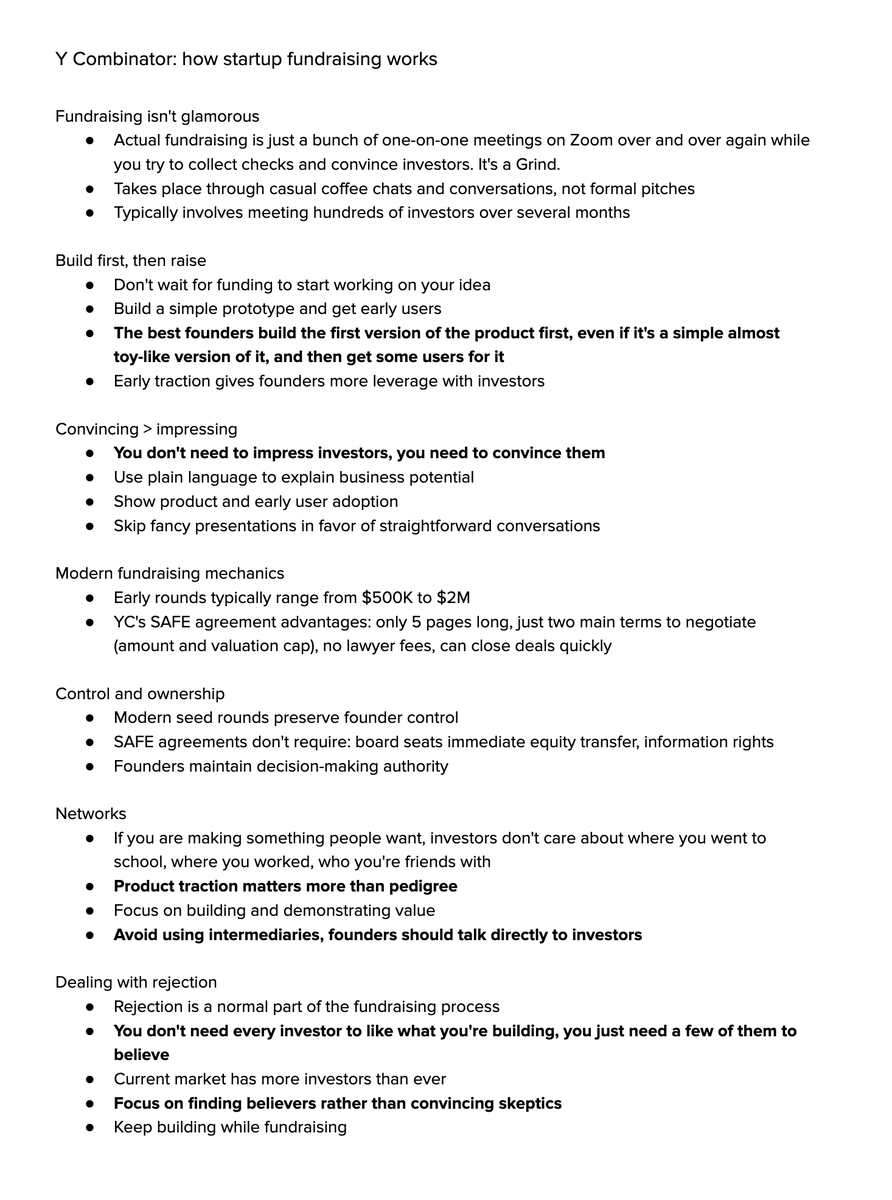
Founders thinking of doing YC are mistaken to worry about the dilution, because their advantage in fundraising afterward more than makes up for it. A year ago I calculated that the median YC startup is net ahead after the first round they raise.
@JackRhysider My own lol. Nice work BTW. Due diligence adds intrinsic value to your content. It reminds me of that story from "that guy" who used your platform and other respected media outlets for clout and new opportunities years back. The dude played the long game for sure!
An interesting observation and POV.
It’s important to distinguish and communicate the value prop and expected outcomes of threat emulation campaigns and security awareness training up front.
Helps keep everyone happy 🕺🏻
I’ve seen infosec teams make internal phishing campaigns way too realistic, indistinguishable from the real service they’re impersonating.
That’s not the point? You’re supposed to leave some identifiable flags for them to feel good about spotting, or learn from. Otherwise it’s just a frustrating experience.
Which is partly why phishing campaigns have debatable benefit. Ultimately an attacker will be successful by asking people to click links on the link clicking machine.
My favorite phishing-simulation-simulator is Google’s phishing quiz (linked in comment).
Runs through examples and a few scenarios and explains how to identify the bad.
Supplement (or replace) phishing campaigns with it.
@IceSolst Is it possible that you’re mixing expected outcomes between CTI-based phishing campaign emulations and email security awareness training?
Both satisfy unique requirements and have different functions, objectives, and outcomes that add value to the org.
Windows and MacOS support it.
Pwsh command telemetry isn't detected or correlated 100% of the time, regardless of the current year.
To help teams increase pwsh detection coverage until it reaches end-of-life support.
An obvious use case is running pwsh from apps that live in the CLR.
Windows and MacOS support it.
Pwsh command telemetry isn't detected or correlated 100% of the time, regardless of the current year.
To help teams increase pwsh detection coverage until it reaches end-of-life support.
An obvious use case is running pwsh from apps that live in the CLR.
ATT&CK is a KB—just like any other KB. It’s designed to help people adopt a common language when discussing PE, writing IRRs and ARRs, tracking work, improving detection accuracy, building threat-hunting workflows, etc. There are so many use cases for ATT&CK on both sides of the spectrum.
The accountability problem you pointed out—how people use KBs, frameworks, standards, and guides as checklists—is the real issue here.
Teams that use ATT&CK as a checklist (like the OWASP top 10) don’t have an embedded engineer focused on offensiveOps, don't understand how to deploy offensiveOps workflows into their eco system (they use QA-style methods to prioritize risk), or need a nudge and help to know how to use ATT&CK from the perspective of a TA, an Analyst, a Detection Engineer, etc.
True story: We’ve had customers we couldn’t convince to shift away from the checklist method. So, what do we do?
We deployed a simple pipeline that enriches output from their internal PT/OST
- check if TTP exists
If not
— tag with extended TTP that is not publicly documented by ATT&CK
Now it’s “known” by the customer and ends up in their checklist backlog. Yeah, their backlog of knowns increased twofold.
They were cool with it because we didn’t disrupt their day-to-day operations or tell them how to do their job. Win win 😀.
OST -——|
VECTR — |—enrichment pipeline —ES
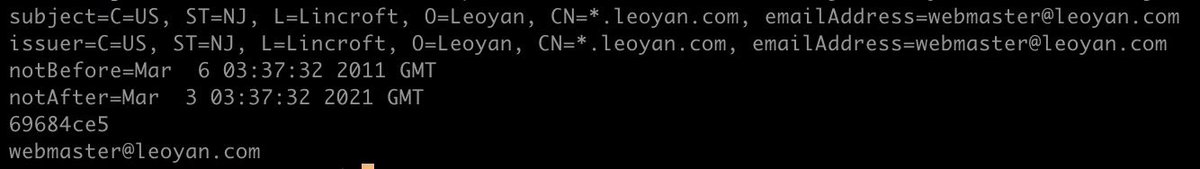
@ylecun Hey! One of your LE certs expired 20 days ago and the other well, is from 2011. Can you fix it? We want to learn more about your research but the NYU Ubuntu server isn’t not trusted. 🤷🏻♂️
@fr0gger_ @MITREengenuity ‘s Blueprint templates - makes it easy to standardize, customize, distribute, and manage STIX formatted TR docs. We use their layout + stix and CLI Tool to manage and share TRs on GH. Gonna open source the cli tool soon. It’s handy. https://t.co/0Ewa62mSid
@luomostesso@ImposeCost You good man? I remember having a similar POV at NTC towards folks that tried to avoid deployment. From getting pregnant to intentionally pissing hot. That POV lasted 4w. These same folks still did their part. + we all jumped together, trained together, and trusted each other 💯
@Malcoreio@ImposeCost Curious. Where does this frame of thought come from?
Never heard this from U.S. ex-mil 11Bs. Or any 11. The respect was mutual irrespective of mos.
At the end of the day, we all jumped together, trained together, rolled together, and trusted each other to do the job.
A red teamer is also a full stack developer, just 10x more cracked.
Backend, front-end, thick clients (on host malware, multiple OS), network, AAA, humint, infra, reporting.
Give yourself a pat on the back or something.