Final giveaway of the year🎁:
4️⃣Hand-On Web Exploitation (Course Only https://t.co/Vk3Q9lzV6l)
3️⃣Shodan Codes
2️⃣Caido licenses
1️⃣Hands-On Web Exploitation (Certificate+Course Bundle)
To enter drop a 🫶🏼and RT
🚀 Big Announcement! 🚀
After 8+ years of working on PayloadsAllTheThings, I’m excited to release it as an ebook on Leanpub! 📖✨
To celebrate, I’m gifting 5 free copies to random retweeters! 🔥
👉 Retweet for a chance to win
Thank you all for your incredible support! 🙌
This cheatsheet has been a labor of love and countless hours of dedication.
👉 Grab your copy now: https://t.co/SNs7mSgXAJ
The results will be announced on 25th December. Entries will close Tuesday 24th, December at 12:00 PM (GMT) 🕐
#CyberSecurity #Infosec #PayloadsAllTheThings #EbookRelease
Our talk at #BHEU is done! Hope you all enjoyed it. 😉 A detailed blog is on the way, but in the meantime, check out the pre-alpha website https://t.co/lGRfqhmcVK for early access and the slides!
Huge thanks to @BlackHatEvents and my awesome co-presenter @_splitline_! 🐈
SimpleHTTPserver is a go enhanced version of the well known python simplehttpserver with an additional, fully customizable TCP server supporting TLS!
Install today! 👇 #hackwithautomation
https://t.co/3baPbwKbts
Thanks to everyone who's created and submitted a BCheck so far - we're going through the GitHub repo to decide who will win some swag... Hit the link below to submit your own BCheck and vote for your favourite submissions!
https://t.co/k1sSnGRTfE
If you want to know why collab is important and how we made 120k in 2022 check out our first video, we share lots of #bugbountytips.
Many thanks for @gregxsunday, @haqpl and @OlivettiOriana - it wouldn't be possible without you, it was a great year!
https://t.co/7YxLbucGi5
Hello Hackers 🥳
We are giving away 40 (20+20) PentesterLab vouchers to celebrate this twitter milestone. Thanks to @PentesterLab for doubling the vouchers.
Details in the 🧵
Share with anyone you think may be interested.
#hackwithautomation#giveaway#security#opensource
CVE-2022-32225 A reflected DOM-Based XSS vulnerability has been discovered in the Help directory of Veeam Management Pack for Microsoft System Center 8.0. This vulnerability could be exploited by an attacker by convincing a legitimate user to visi... https://t.co/FMJdR68h7r
☢️ Agenda of my Modern Red Team Malware Development training that I'm running at @x33fcon next week - almost ready. Just a few final touches!
I already feel like there won't be enough time to cover everything I'd like over 3 days. A month would do tho!
What do you think?💀
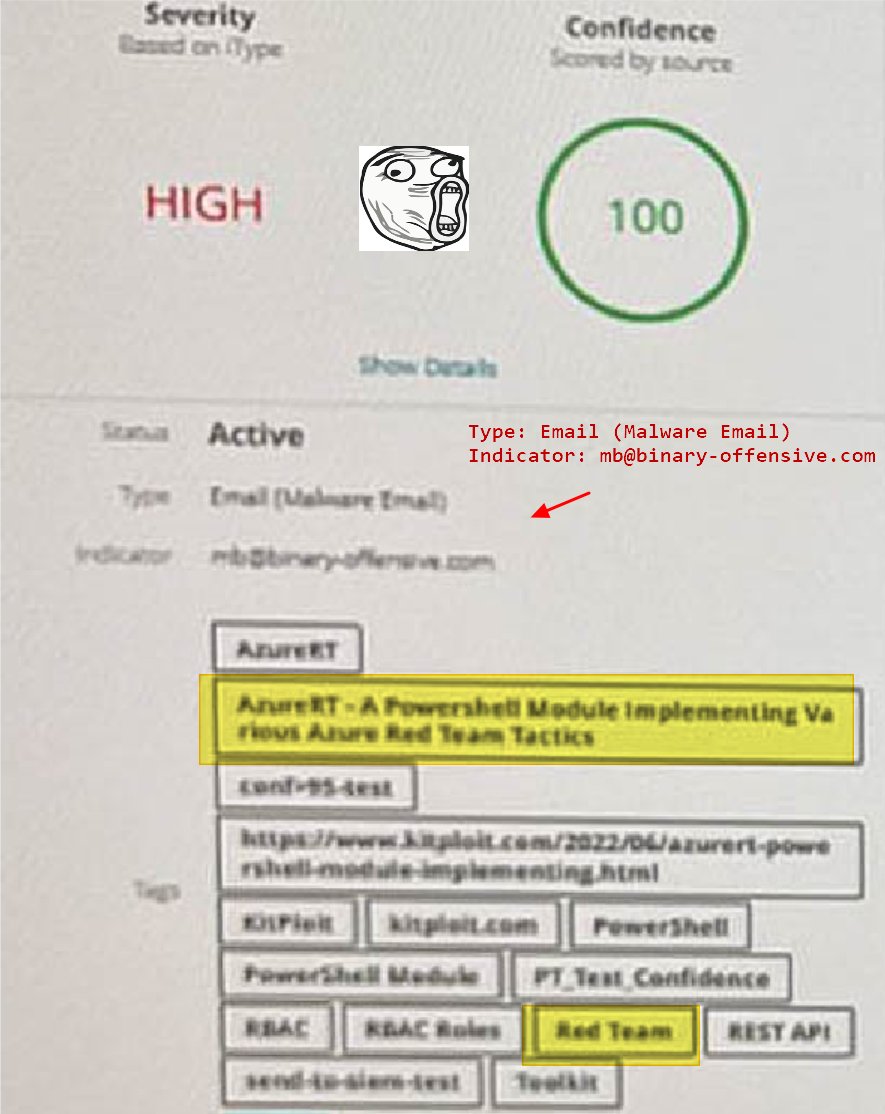
💀 Smelling cyber-criminals based on their "Malware E-Mail" isn't going to make us any safer from real threats.
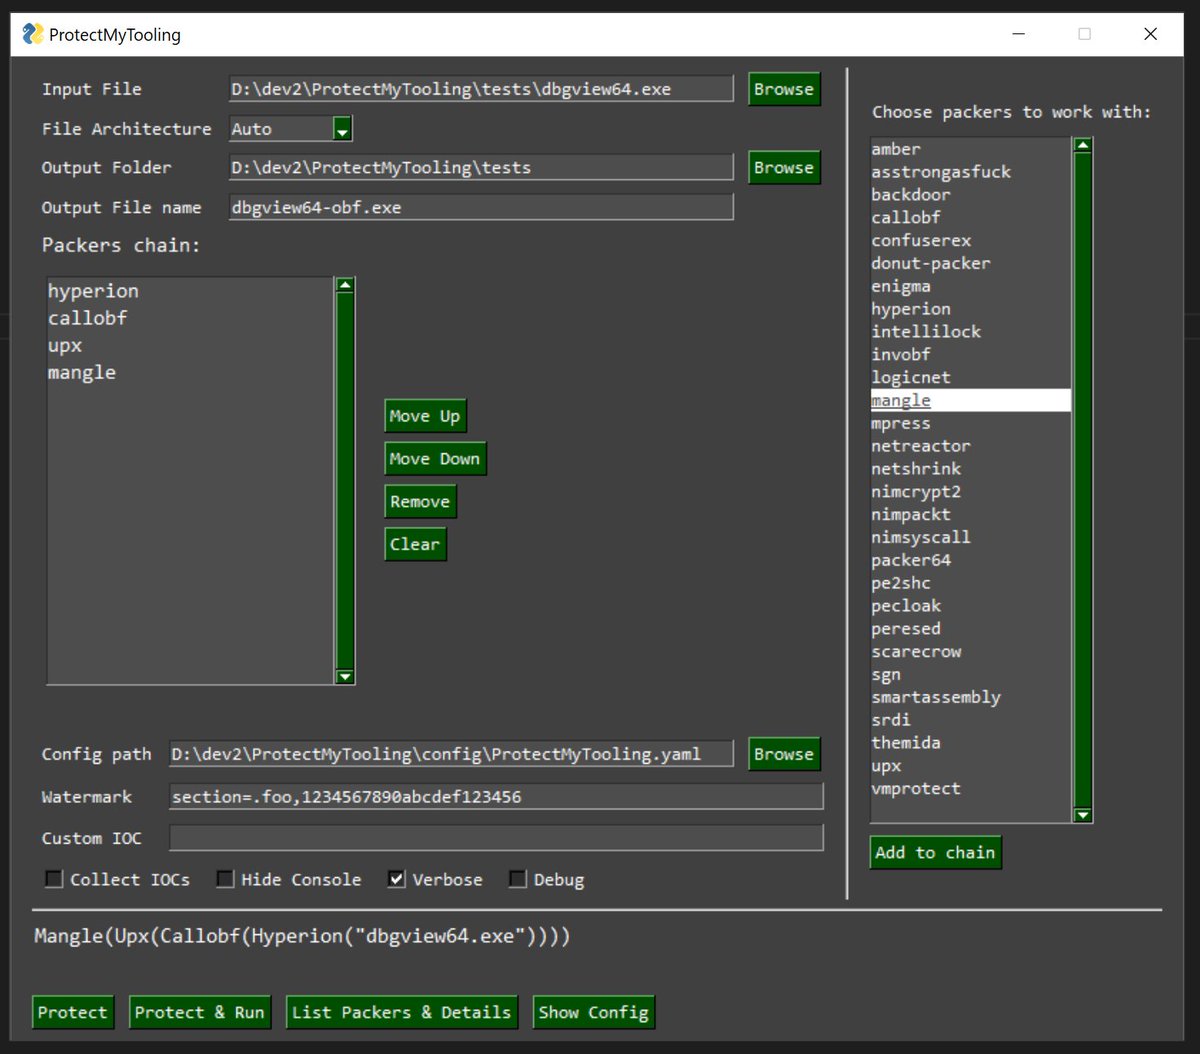
I hope that exposure of Multi-Packer wrapper will help lesser mature Red Teams step up their game and educate their Customers how their Blue Teams should not Detect.
If you want to play with Sliver C2, it is actually in the @kalilinux repository! All you need to do is run the following commands:
sudo apt install sliver
Once it has installed you can run the sliver-server to run it!
Credit to @ssh4un for the image!