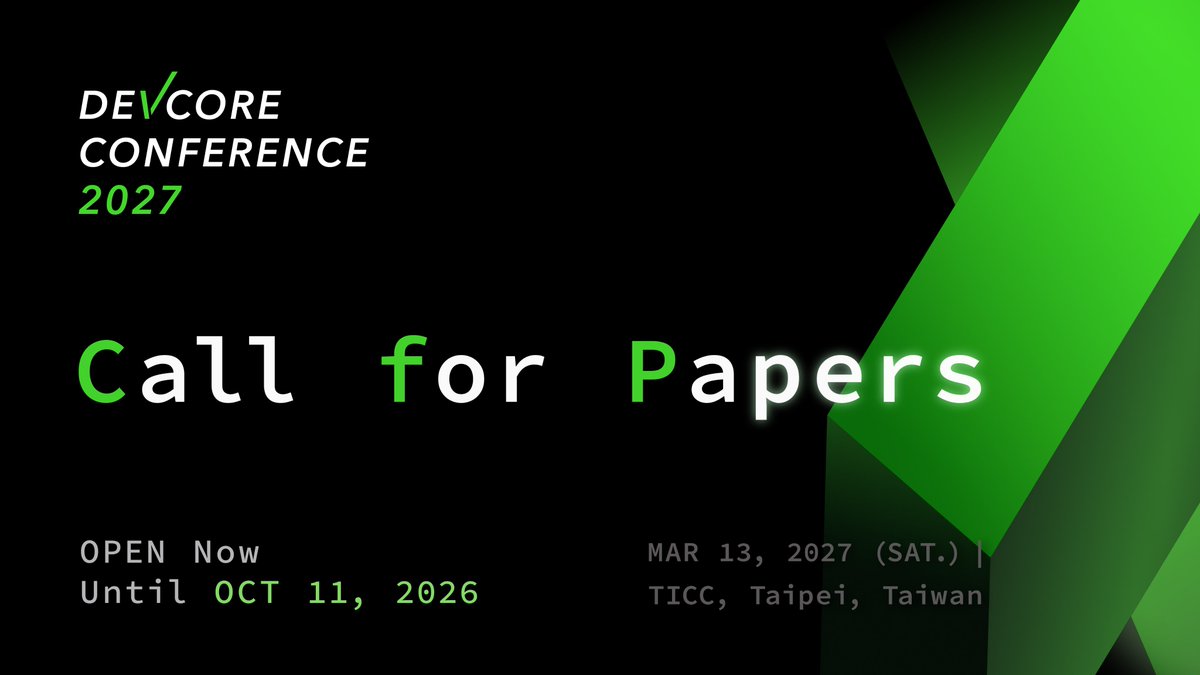
DEVCORE CONFERENCE 2027 | CFP is open
#Redteam, #VulnerabilityDiscovery, #Physicalsecurity, firmware and hardware RE, #AI attack surfaces. Bring the research that starts from a hacker's view.
Deadline: Oct 11, 2026, 23:59 GMT+8
https://t.co/hdvlNsAobJ
Tomorrow at @SEC_T_org, I’ll be breaking down the journey of how I found paths to compromise software supply chainS.
We’re going down the Linux side this time ;)
bug bounty still works, sure
problem is how much critical infra sits nowhere near it
most of it hasn't even had someone lazily throw a "hey chatgpt, find a 0-day for me make no mistakes" prompt at it yet
My #BHUSA 2026 slides are online!
It was an honor to share our AFD research and how a different perspective led to 30+ Windows kernel vulnerabilities.
Blog post coming soon — check out the slides here:
https://t.co/l8xIaRtL7V
so i actually got more than one RCE chain (~2.5?) for SharePoint at Pwn2Own this year, even though i ended up using the freakishly simple one (for strategic reasons :p)
here's another one of them:
https://t.co/OfefQK73KH
Two of our researchers hit the #BHUSA stage for the first time.
Angelboy(@scwuaptx ) shares how a different angle on AFD led to 30+ new #Windows kernel vulnerabilities. Splitline(@_splitline_ ) exposes backdoor risks in Go, Python & Flutter pipelines.
#VulnerabilityResearch
an incredibly simple but also incredibly critical bug i found on Python[.]org!
big thanks to PSRT and the maintainers for the quick fix and thorough follow-up
for the tl;dr: i can do this:
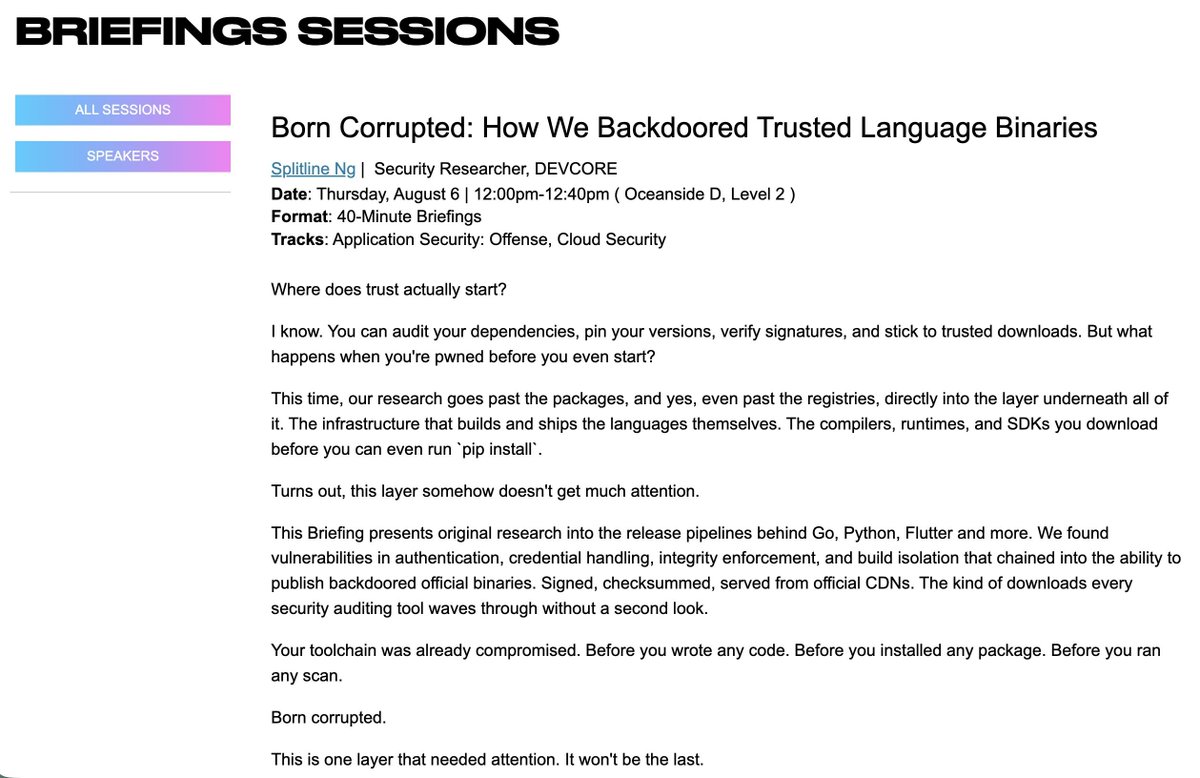
Next week at @BlackHatEvents#BHUSA, I'll present “Born Corrupted: How We Backdoored Trusted Language Binaries”
We found ways to compromise Python, Go, Flutter & Julia at the supply-chain layer, turning trusted bins into whatever hackers want them to be!
Check out the abstract: