I have compiled the list of resources from which I have learned Android hacking and put it in this repository in the hope that it will help you guys.
https://t.co/ubATvu5GpB
#BugBounty#bugbountytips#bughunting#Hacking#Pentesting
Some secrets are meant to stay secret. Hackers just keep finding better ways to make them talk. 👀🔥
At Upwind presents BSides Ahmedabad 0x7, Devang Solanki, Security Researcher at RedHunt Labs, is taking the stage for a Hack Talk on Bug Bounty Beyond Web & Mobile: Automated Secret Hunting in Developer Ecosystems. 🎤
If finding what others miss is your kind of thing, this one should be on your list.
📍 Hyatt Regency, Ahmedabad
📅 26–27 September 2026
🎟️ Got your eyes on this one? Don’t just save the post. Save your spot. Book your ticket: https://t.co/ppHZdsuaUv 😎
#BSidesAhmedabad #BSidesAhmedabad0x7 #HackTalk #BugBounty #SecurityResearch #CyberSecurity #InfoSec #CyberSecurityConference
Sat with @devangsolankii this weekend & configured a cron job (with @zcode_ai and @hackwithclaude) to fetch h1 publicly disclosed critical, high & medium reports every Monday, classify to the closest vuln type, generalize & make/update a skill out of it.
Ran it on some of my old targets where previous iterations couldn't give much fruitful results. So far it gave me 2 XSS (-> ATO with manual escalation), 1 IDOR, 1 Unauth API endpoint to 40K+ PII & Financial Data leak.
Guys, you're wasting your time with Burp.
Hacking shouldn't require anything but typing.
Use this tool on a target and if you don't like it, DM me, I will personally apologize!
https://t.co/3d5Ko481JD
@PinkDraconian Totally!
I found a Gemini token inside a browser extension for one of the biggest CRM companies.
Btw, can I use your tweet for my upcoming talk at BSides Ahmedabad?
We’re offering 1.5× bounty on High & Critical SQL Injection vulnerabilities.
Pawn your AI agents 👽
On top of that:
• First Blood — Critical: +$500
• First Blood — High: +$250
The First Blood bonus is in addition to the 1.5× campaign bounty.
https://t.co/IBx1Eyfvbl
@PinkDraconian What if they never make an account? And usually, it's already marked as out of scope.
I get what you're saying, but most of the time my reports get marked as N/A.
I've mapped most of the recon workflow I personally used over last few years - which helped me to earn $20K+ bounty and multiple critical vulnerabilities on even some of the well-tested targets.
Sharing the full workflow below 👇
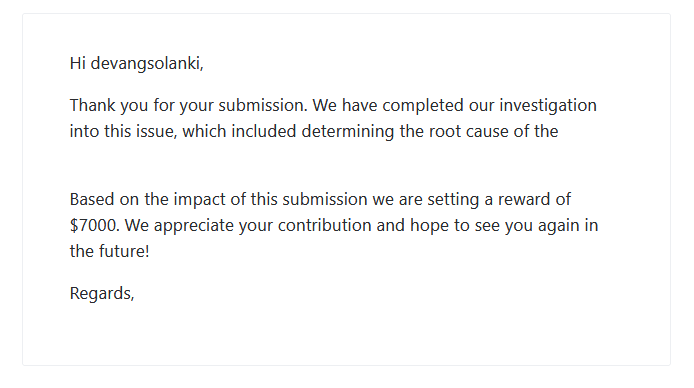
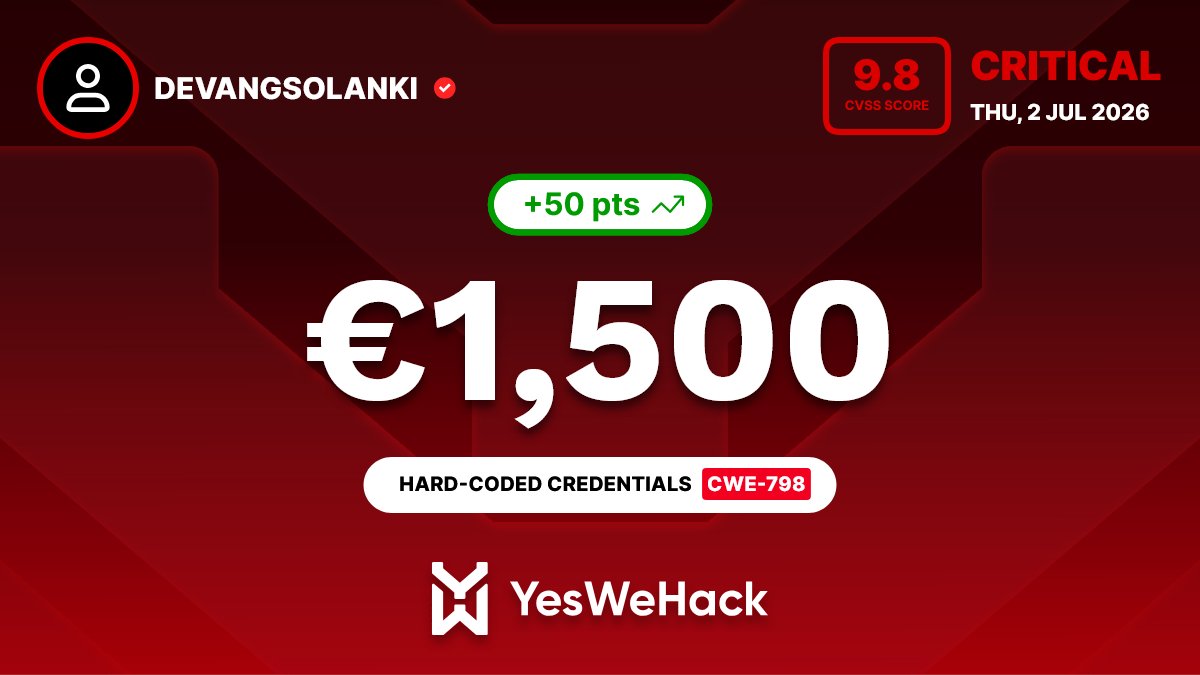
Just got a reward for a critical vulnerability submitted on @yeswehack -- Use of Hard-coded Credentials (CWE-798). https://t.co/V1iwgQGP5K
#YesWeRHackers#BugBounty