Innovative senior software engineer with 7+ years of experience in developing cutting-edge web and mobile applications.
Ask me about JavaScript, PHP & Dart.
Can I automate browsers with AI???
Can I automate email replies with AI???
Can I sleep at night peacefully, knowing fully well that there is something constantly monitoring the platforms under my care are running through scheduled checks?
Can I monitor that particular online store for discounts on products I would love to buy???
I answered YES to these questions and many more with my first personal project!
I'm calling it Flowshub for now, but that is still open for changes.
Watch this space for the final launch!
The full editor in all its glory.
Anything inside {{ }} is a valid JavaScript expression.
I can't believe I'm starting 2026 by writing a template engine with its editor.
😅😅😅😅
@nicksdot@sander_scode I work with all these in one window on Intellij IDEA.
Core - Laravel/PHP, TypeScript, CSS, HTML
Mail - Go
Mobile - Flutter/Dart
So all the other IDEs are basically Intellij IDEA Base + Language Plugin.
Thanks to a suggestion from @dr4goonis, we've added a new stats section to the Elephc homepage.
You can now see at a glance how far we've come in terms of PHP compatibility, with clear percentages tracking our progress.
Check it out: https://t.co/RkJoFkxdXY
None of my PHP projects are accepting file uploads directly anyways, I use direct to object storage approach for all uploads, so I have disabled multipart requests and this session upload progress thingy till further notice.
I have also updated the FrankenPHP PHP GitHub Gist I created with these new defaults so I can always copy it over to new projects:
https://t.co/c3XjK3mp7E
Set session.upload_progress.enabled=0 till next PHP release to block an unlikely RCE vector (CVE-2026-115560). Already recommended for CVE-2026-109619 Wed, keep disabled. Only apps with non-default serialize_handler switching it to "php" at runtime can be affected. #php#phpc
We protect over 5 million PHP sites and when we find a major exploitable vulnerability, we always see site cleanings. We have seen exactly zero hacked sites from php2shell. Zero. Across a population of 5 million PHP sites that our product protects. Draw your own conclusions. #php2shell
They are called SAPI (Server API) and they are abstractions of how PHP is executed.
You can check PHP_SAPI constant to get the current SAPI that a script is executing on.
Common values: apache2handler, cgi (until PHP 5.3), cgi-fcgi, cli, cli-server (php -S), embed, fpm-fcgi, litespeed, phpdbg.
@ferron_web@eevblog Yeah, the original post missed "embed" which is another form of PHP and that is the one you embed in other programming languages like what FrankenPHP is doing with Go.
@ferron_web@eevblog Yeah, the original post missed "embed" which is another form of PHP and that is the one you embed in other programming languages like what FrankenPHP is doing with Go.
Hetzner sent out a reminder to dedicated and cloud server users, to remind them that security is on them. Mail sounds like they talk to someone who runs root servers by accident. First I laughed, then I remembered vibe coders.
If all the govs shutting down servers for a PHP update, all the hosters & enterprises terrified by the vuln, gave $100k, or just $50k a year to the PHP Foundation, things could look very differently. Go, make your employer sponsor *today* https://t.co/z1mUcXMqy9 #php #phpc @Th@ThePHPF
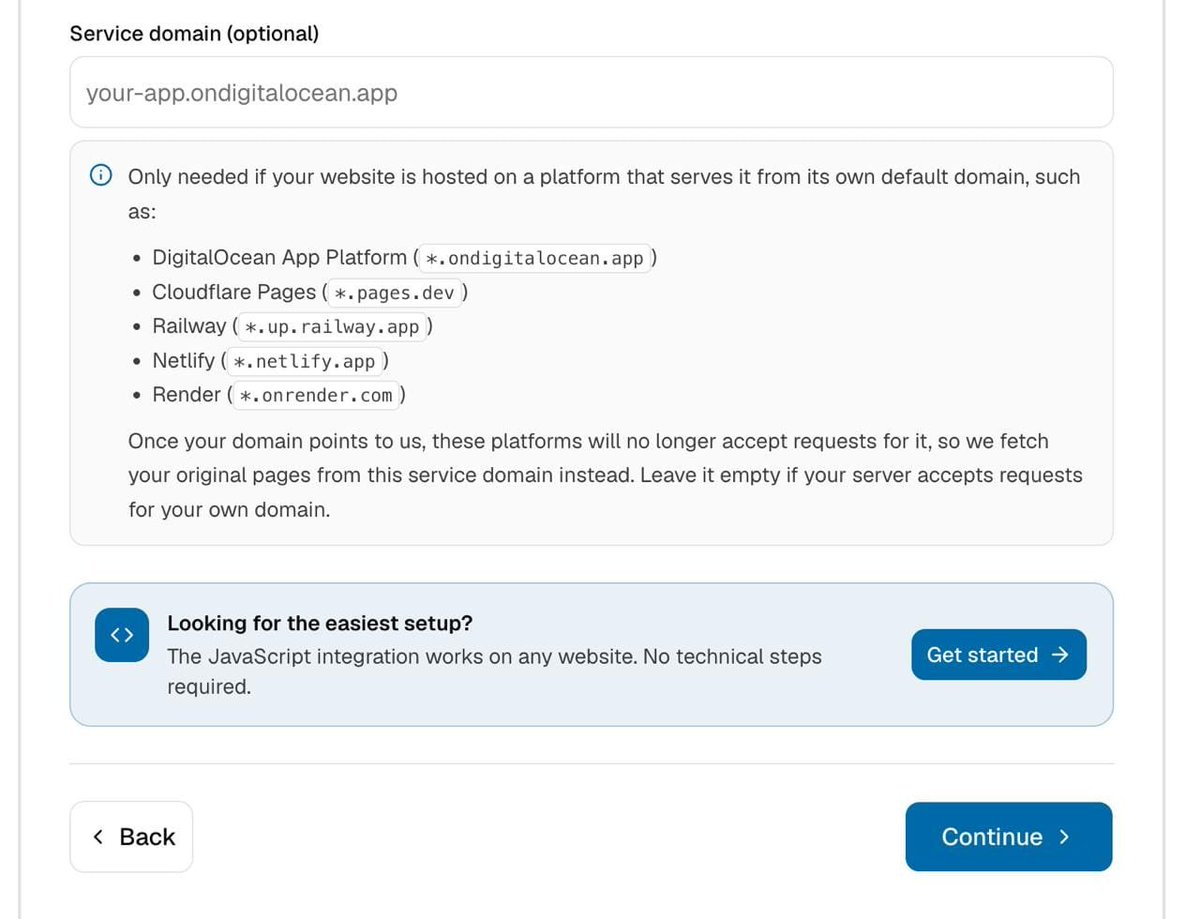
I did something similar to Caddy reverse_proxy directive yesterday to solve the particular issue that happens when we need customers to point their custom domain to us but they are already hosted on a platform that needs the same thing or they are using Cloudflare with CNAME at apex level.
Boss is happy.
😇😇😇