Stripe is not selling software. It’s selling compliance.
You can accept payments without having a legal department or even knowing what FATF is.
Many such cases. If your moat is software, you should be a little bit scared.
In September 1992, Unicode had a problem on Unix. Storing characters as 16-bit values could introduce zero bytes that C programs mistook for string terminators. Earlier encodings had compatibility problems of their own.
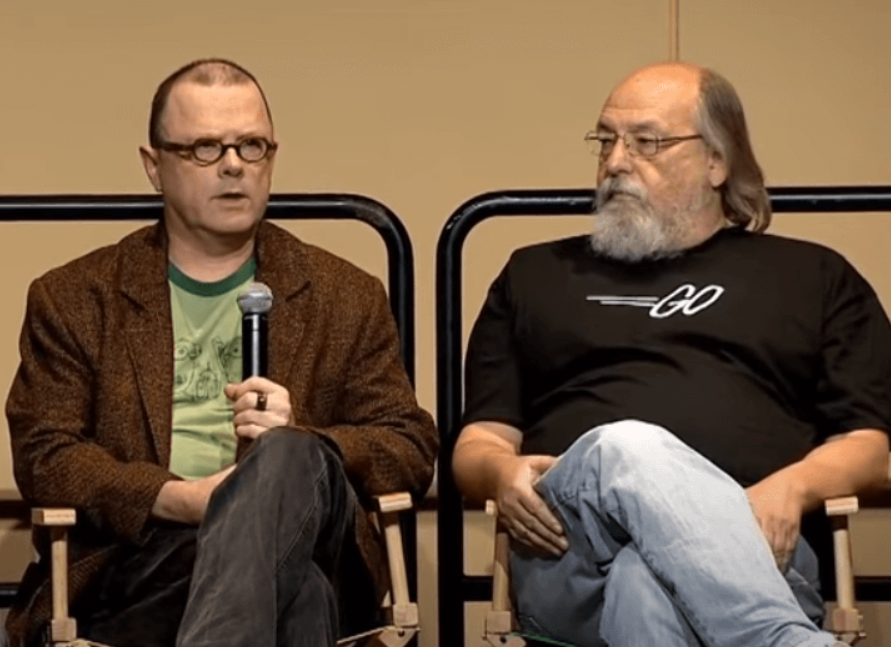
One evening, Ken Thompson and Rob Pike went to a diner in New Jersey. Thompson sketched a new encoding on a paper placemat.
ASCII stayed exactly as it was. Other characters used multiple bytes, without accidentally introducing null bytes or Unix path separators.
They went back to Bell Labs and started coding. By Friday, their Plan 9 operating system was running entirely on the new encoding.
They called it UTF-8.
Today, it powers over 99% of websites with known character encodings.
Developers, this is for you. please take your payment callbacks seriously. 🔐
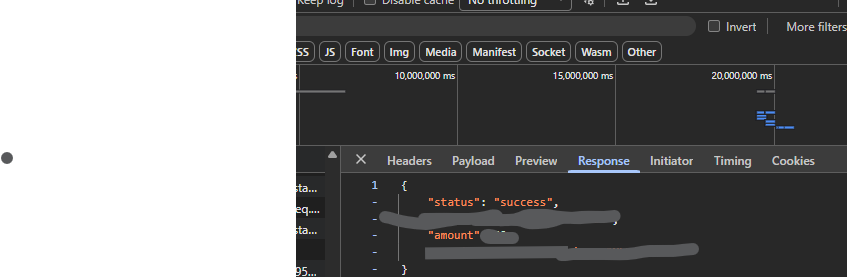
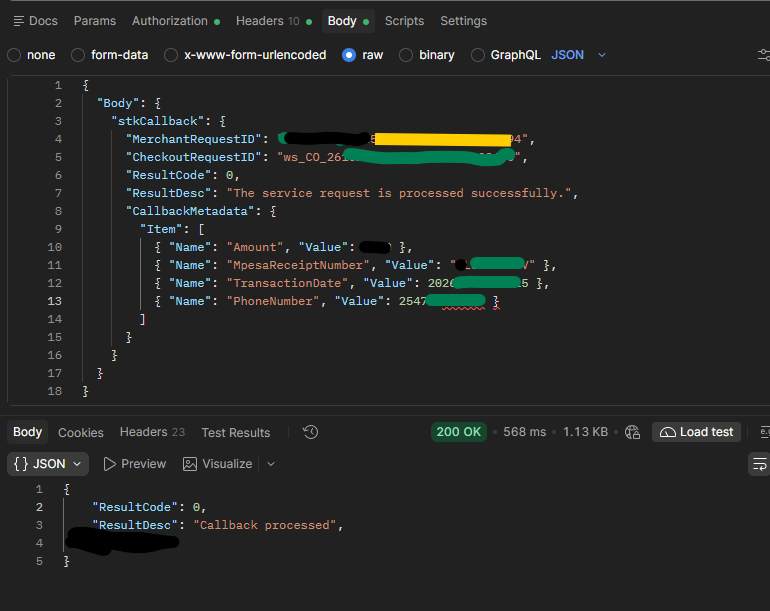
Yesterday, out of curiosity, I tested an M-Pesa integration on a critical live system. To my shock, I was able to submit a crafted payload that resulted in a payment being marked as successful.
Never trust a payment callback blindly.
Best practices:
- Verify callbacks against the payment provider.
- Validate the Merchant Request ID and transaction details.
- Verify payment status independently where possible.
- Restrict callback access by IP where supported.
- Make callbacks idempotent to prevent duplicate processing.
- Never mark a payment as successful based on an unverified payload.
One weak payment integration can undermine the integrity of an entire system.
Security is not just about protecting your APIs. It's about protecting the business logic behind them. 🔒
I wish more Kenyan founders were like akina @DanThaKaya,@PeterOkwara and @shadrac_matata.
Great dudes who've are pushing Kenya's founder scene forward.
I've learnt a lot from those guys. Wishing them all the success out there.
Anyone else I should know or connect with?
PHP isn’t the most sexy language, I give you that. Where I live in Belgium, government, school, hospital, help line, media, news, and what not websites are down.
It’s not because we don’t often hear about it that it isn’t big. Usually, PHP simply does the job. Nothing sexy, nothing worth shouting about. Only on these rare occasions do you get a feeling of the true impact of the language.
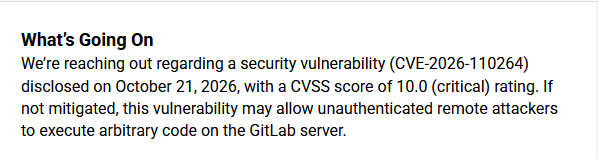
Two critical security vulnerabilities affecting PHP have been identified that result in unauthenticated remote code execution (RCE) for any PHP application. Ubuntu has released fixes for the affected packages for all supported releases.
Read more: https://t.co/uDs3s8zwju
#Ubuntu #Security #CVE