🇺🇸 I'd like to give something back to those who served.
I'm offering 4 months of FREE, 1-on-1 online cybersecurity mentorship to a retired U.S. Marine looking to break into the cybersecurity field.
No strings attached. Just my time, knowledge, and experience.
Please repost to help me reach the right person!
I can only commit to one person.
DMs are open. #Marines
🔎 What if you could run CodeQL on binaries as smoothly as on C/C++ code? We dug into CodeQL's internals to make it possible. Join our experts Raphaël and Maxime as they present BinQL, a CodeQL extension for querying binary formats at #GreHack26! https://t.co/FfuBC2B4uX
Okay fellas, we need to talk about something. If you report bugs to Apple and you are getting pissed because they are not paying you: you need to make damn sure that what you are submitting is actually REAL, EXPLOITABLE and you have submitted a WORKING exploit!
The program is VERY clear about the need to demonstrate impact with an exploit and this should not be news to any participants.
I can't believe I have to defend Apple here - as I personally have issues with them from time to time - but if they tell you to do something in order to get paid, it is NOT a suggestion. If you don't like it, fine: go work on something else or drop it publicly or however you want. These are the program's rules.
So:
LLM-generated (likely hallucinated) bugs are not enough. LLM-generated reports are not enough. PoCs are not enough. "It's totally exploitable bro" is not enough.
Get this through your head. Apple is not a vending machine that you can arbitrage with a claude subscription. If you think that, you are a fucking idiot.
Every lazy bounty grifter does this kind of "research", they all find the same low-quality crap, and proceed to collide with 10 others. That's why there's such a surge of unexploitable off-by-ones, panics, crashes and crap that literally doesn't matter 99% of the time.
Using LLMs is fine, but put some though into it, validate findings and submit a working exploit. Simple as that.
No amount of bitching on twitter will accomplish what working exploits can.
Thanks for coming to my therapy session
‼️ Apple will check every photo and file shared through a public iCloud link for harmful content, and can disable the accounts behind it.
From iOS 27.3, Apple may delete flagged items and, "if necessary", bring in law enforcement.
It does not say what counts as harmful.
anthropic just stole my best friends research
he spent the last 10 months developing zero knowledge proofs for AI accountability, only for @AnthropicAI to announce remarkably similar research days after he applied for compute support.
Can someone at Anthropic at least let him collaborate instead of jacking his research and calling it their own?
proof attached below
@thejailbreakhub At the moment, I have all the information on how SPTM works and what to do bypass SPTM, I think that in a couple of days everything will be ready on my device. Along the way, I will publish news and more proofs
@GalloDaSballo From the public opinion I heard that running a good open model requires $50k and running it on laptop is slow given how much resources it consumes. How should someone start in such cases as closed models will make the research public?
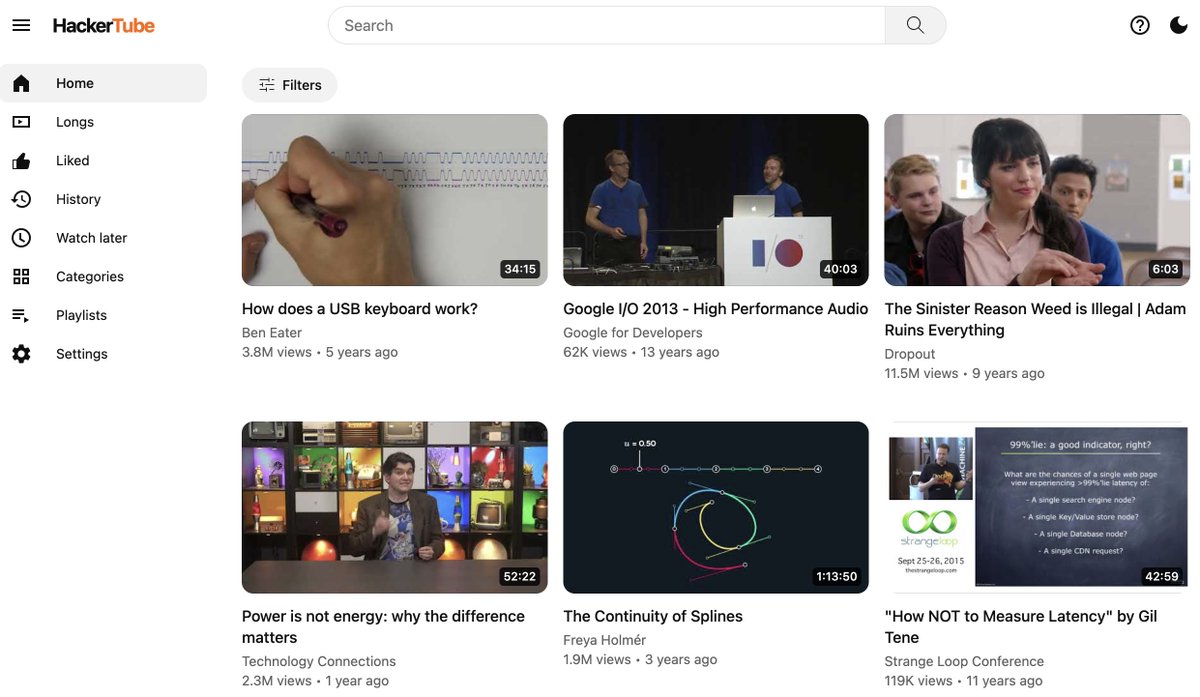
Weekend hack: HackerTube. I was annoyed with YouTube's recommendations so I had Claude filter down 43M comments over 20 years of HN to 6,454 videos that keep being recommended. *Significantly* better viewing experience, ~2 hours with Opus 5.5:
https://t.co/JIhXN7OSh1
- Excellent recs without any logins (state is kept in local browser session)
- Thumbnail is a representative frame from middle of the video instead of the super duper A/B test hyper-optimized user uploads
- Underlying data from the comment analysis as one zip file, point your Claude at it and ask for your own version
- HackerTube Longs ✊
A bit more on the process:
I use Claude Code (desktop app for Mac), Opus 5.5 on Medium effort as my default. I only talk to Claude and have it do everything, the only "manual work" I helped with in tandem was in the browser (reminiscent of MenuGen): 1) I had to create some kind of API key from Google Cloud UI to query YouTube for video metadata, 2) I booted up a VPS box for serving and 3) I bought the domain name. Once the box was up I gave Claude the IP and told it update, secure, harden, deploy and optimize the code, and it did the whole thing.
Many awesome projects that would have normally taken weeks/months even can now be few-shotted for breakfast. What else are we not thinking of.
IMO the hallmark of a "senior" vuln researcher is not only their ability to discover/exploit vulnerabilities in difficult targets, but, critically, their ability to effectively *invest and allocate resources*. Knowing when to sink more time/effort into an attack surface or difficult bug, and when you need to stop and *move on* is one of the hardest questions as a researcher, and you only develop that instinct through experience and hard-learned lessons.