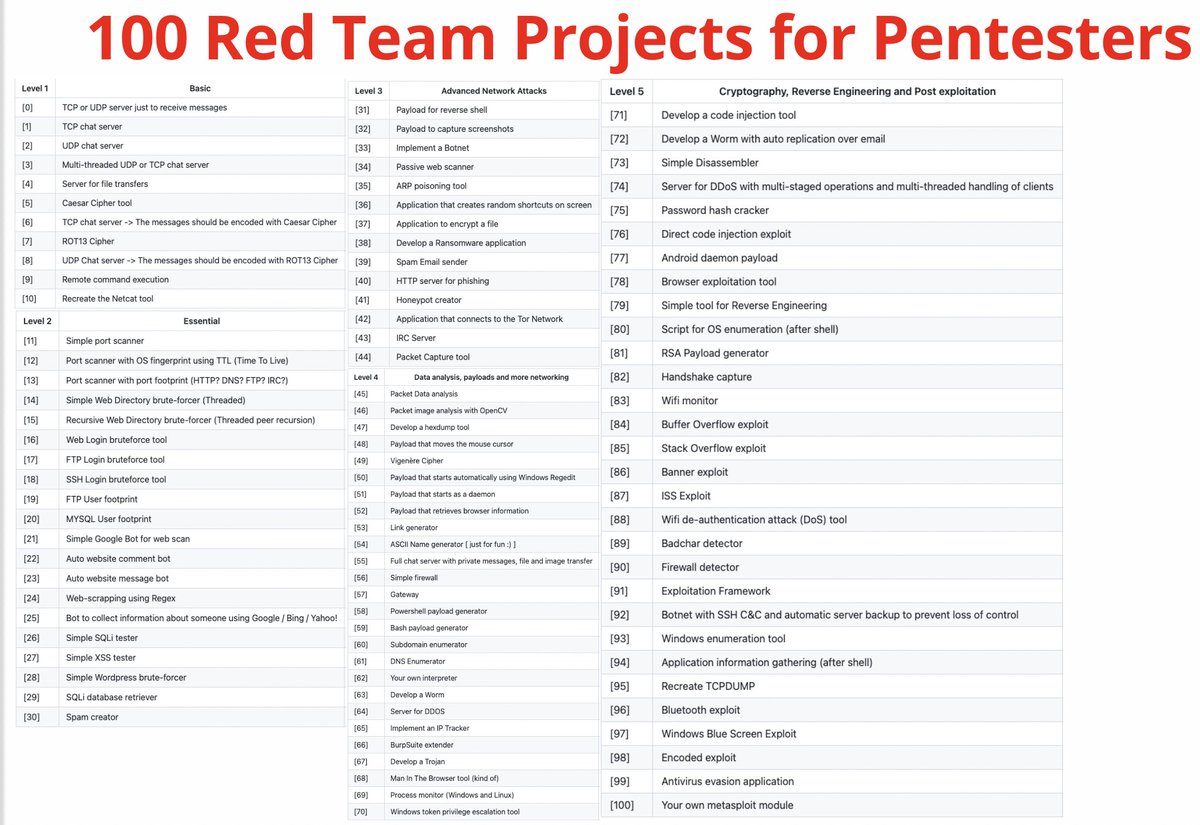
100 #redteam projects
A list of 100 projects that are worth a close look at the source code for someone who wants to become a high-level professional:
Advanced Network Attacks
Data analysis
Payloads
Cryptography
Reverse Engineering
Post exploitation
https://t.co/YOMzAwIzTu
Email #OSINT Technique
Using the ask[.]fm friend search engine, you can successfully reverse search an email address and get back a first and last name, image, username, and other data found on the user's profile.
☕️ Good morning. Wayback is an essential tool for OSINT.
Using The Time Machine, you can go back in time to find endpoints such as /api/ or JSON for #OSINT or #BugBounty.
Has offensive discovery capabilities too!
#bugbountytips
https://t.co/CTiXiCagx2
☕️ Good morning. People often ask me what resources are best for getting into #OSINT.
This guide I found on GitHub is an excellent primer for beginners and also a pathway to intermediate level.
There’s a heavy emphasis on the OSINT mindset.
https://t.co/ksgwu2vMIo
I didn't want to mention it, but after my last SANS preso on hunting drivers, I've decided to build a site similar to LOLBAS project presenting all known vulnerable Windows drivers. More to come.
Until then, give it a follow.
https://t.co/IfUnrKsmxm
If you're looking to get started in #malware#analysis or #reverse#engineering, consider checking out my @YouTube channel, I videos covering a wide range of topics!
🤔 https://t.co/jRe0upcWK8