New episode of Behind the Binary is live!
🎙️Joined by @L0Psec to break down macOS security, ClickFix social engineering, InfoStealers (AMOS/MacSync), DPRK developer targeting, and the evolution of obfuscation.
Plus, we talk about how AI is shifting reverse engineering and the inevitable future state...
🎧 https://t.co/8SlDtgWs55
🆕 Meet the Malware Analysis add-on for IDA Pro.
Detects packed samples on load and offers to unpack them, emulates Windows code safely with no VM, and maps sandbox events onto your disassembly.
Grab it for 50% off with promo code MALADD50
*See comments for rules and restrictions.
👉🏽 Check out the feature set and case studies here: https://t.co/zBeqzYnznz
Have you ever heard about São Tomé and Príncipe 🇸����? If not and if you care about cyber security, you should read on ⤵️
🔎 What is São Tomé and Príncipe?
São Tomé and Príncipe 🇸🇹 is an island nation located in the Gulf of Guinea off the western coast of Africa 🌍. Its country-code Top-Level Domain (ccTLD) is .st, which has recently attracted a surge of threat actors registering malicious domains to conduct cybercrime 🕵️.
📏 How big is the threat posed by ccTLD .st?
Public statistics from @spamhaus show roughly 11,600 active .st domains. Nearly 5,000 of them are flagged for malicious activities 🛑. That’s an astonishing abuse rate of over 40% of all active domain names within this ccTLD! 📈
➡️ https://t.co/0lKGJcZey5
While threat actors often register domains across various ccTLDs, the big issue with .st is how its registry is dealing with, or better said, not dealing with, abuse reports 📩.
Over the past few months we’ve sent nic .st several abuse reports about domains registered purely to run botnet command-and-control (C2) infrastructure.
Here's two recent examples of malicious domains within ccTLD .st:
1️⃣ thisisafalsepositive .st - An active botnet C2 domain for SilentNet, a Java-based Remote Access Trojan (RAT) and infostealer sold under a Malware-as-a-Service model. Over the past two months, more than 400 malicious GitHub repositories spreading SilentNet have been reported to URLhaus 🏠🔥.
2️⃣ imarapi .st - An active botnet C2 server for the infamous JackSkid DDoS botnet that was disrupted earlier this year by the US DOJ 🇺🇸. It infects IoT devices and Android TV 📺 boxes worldwide 🌍.
🗣️ How did nic .st respond?
The registry routinely pushes back, stating that:
"To be able to investigate we need official document that confirm illegal activity hosted under mentioned domain, this can be decision of courtroom or any other official authorities which will be authorization for us to perform investigation."
🛡️ What should you do?
If you don't do businesses in São Tomé and Príncipe, we strongly recommend you to entirely block .st at your network security perimeter 🛑
We're excited to have Tim Blazytko joining us at RE//verse 2027! His training covers software deobfuscation, including automated and agentic approaches to reversing protected binaries. If you've been fighting with obfuscated code lately, you won't want to miss his class! https://t.co/fz4lamvg1u
I'm thrilled to announce that I'll be at Objective By the Sea in Maui, Hawaii! 🌺
#OBTS brings incredible speakers every year, and it has become the conference I plan my year around attending.
If you enjoy Apple Security, I highly recommend going :)
It's time to put my Adventures of Wallet Hacking series to bed, but not before one final chapter! Free livestream for all courtesy of @unicampoficial LICS Cybersecurity League. Announcement here: https://t.co/U28EZfChta
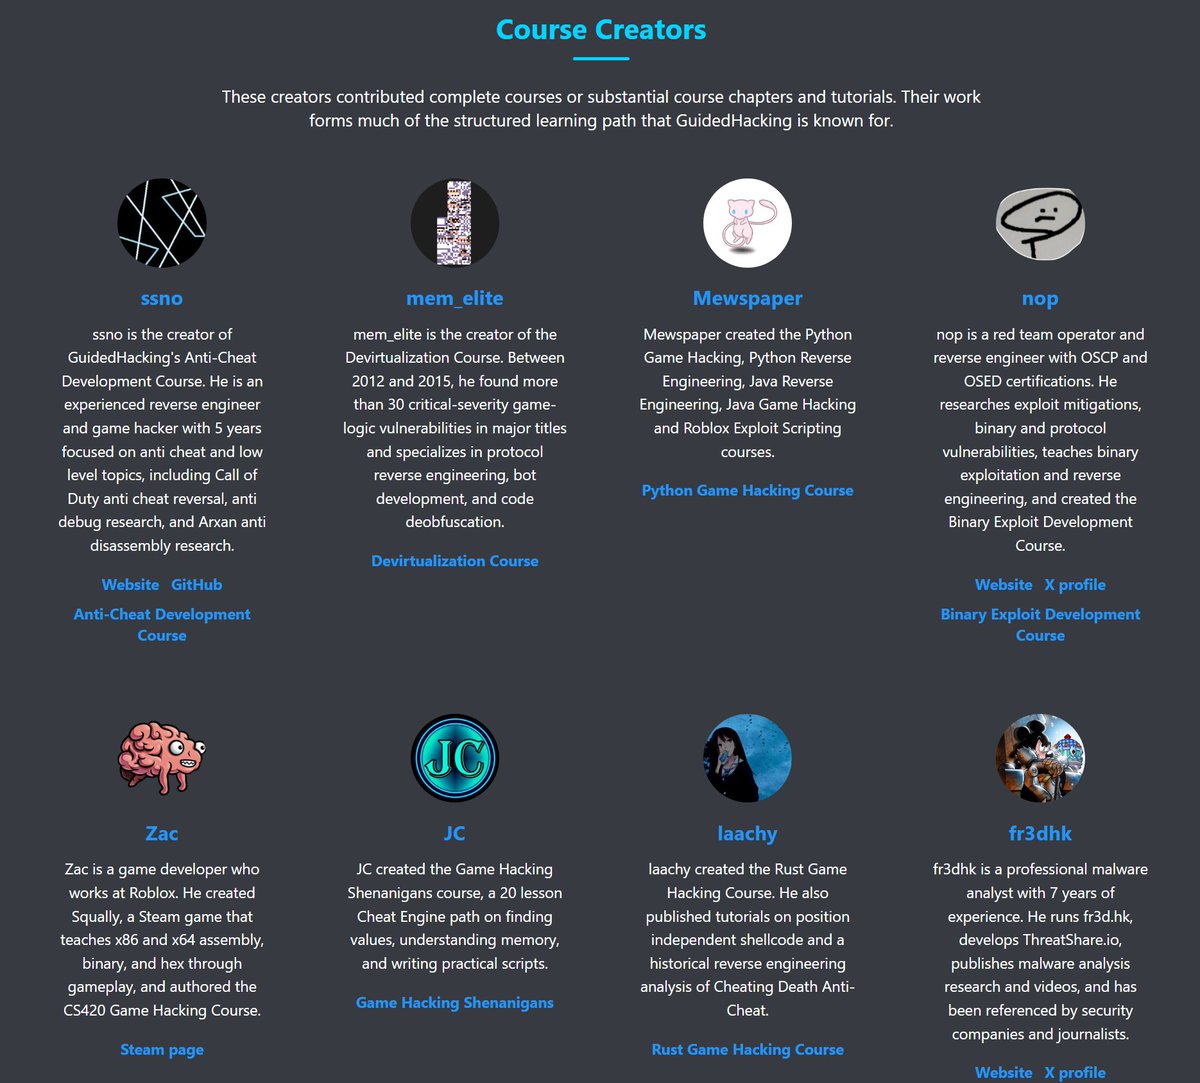
👥 Meet The Creators Behind Guided Hacking
We finally published our official "staff" page. While hundreds have contributed, this page recognizes the core researchers and educators who built our flagship courses, tools and tutorials.
👉https://t.co/61E2y2oEHm
First fine tuned model for #sage#lantern is done -https://t.co/Kp6qSlkdpT (and wtf is SAGE Lantern? A computer that fits in your hand [https://t.co/Q0uJWQSalO]) #sage#ai#governance#meshticulum#lora
New episode of Behind the Binary is live!
🎙️Joined by @L0Psec to break down macOS security, ClickFix social engineering, InfoStealers (AMOS/MacSync), DPRK developer targeting, and the evolution of obfuscation.
Plus, we talk about how AI is shifting reverse engineering and the inevitable future state...
🎧 https://t.co/8SlDtgWs55
Appreciate @jstrosch for the invite on the podcast! macOS malware is at an interesting place. Also, getting to talk about how reverse engineering workflows are changing with AI was fun/therapeutic. I wasn’t crying I promise. 😂
Wanted to share with any military folks (being retired ANG myself) - @Google is hosting Google Cloud Launchpad for Vets 2026—a free, 2-day virtual program covering GenAI foundations, enterprise workflows, and exam preparation. It includes a voucher to take the Google Cloud Generative AI Leader certification exam. Program info and RSVP 👇
https://t.co/A0zsGSnxdv
This is a new area to me but looks really interesting - decentralized, off-grid transport for local AI. @l33tdawg has been building Meshticulum to handle agent sync and data passing over small radios. 👇
If you are doing #FlareOn this year and want to rank yourself against other 𝗵𝘂𝗺𝗮𝗻𝘀 we made an unofficial leaderboard. Honour system only, but it's something.