As the IoT expands CCPA already has specific regs covering data on household devices says Chris Paterson @OneTrust comparing GDPR to CCPA #dpconf20@IrishCompSoc
As the IoT expands CCPA already has specific regs covering data on household devices says Chris Paterson @OneTrust comparing GDPR to CCPA #dpconf20@IrishCompSoc
Businesses must change to a more active model on consent for cookies as the cookie rule is really coming under the radar of regulators. Tracking pixels and 'nudging' all come under this rule says James Fenelon giving updates on 'marketing post GDPR' at #dpconf20@IrishCompSoc
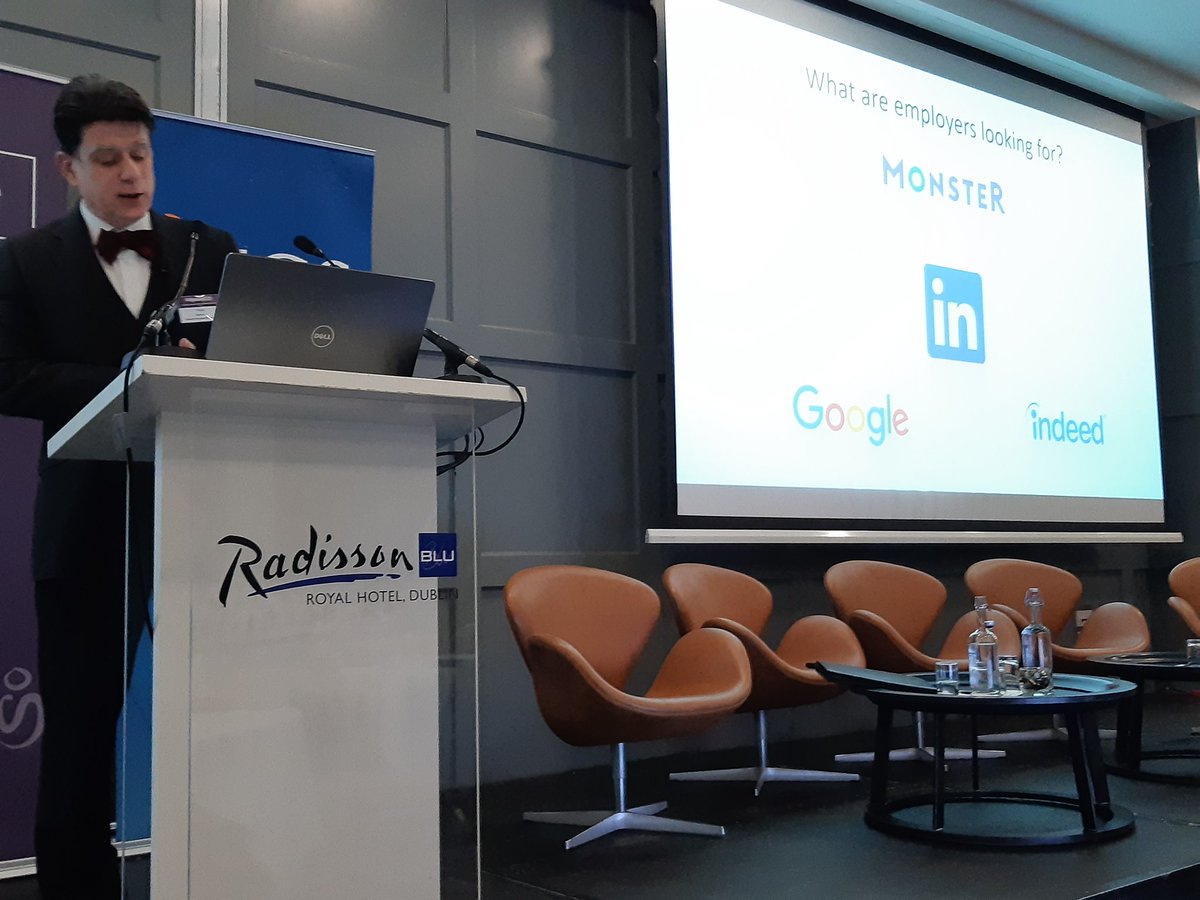
Does a DPO need to have legal qualifications? Actually no, according to Fintan Swanton as he explores the role of the DPO. Based on an analysis of current job ads, employers are inconsistent in specifying the requirements of their DPO teams and hires. #dpconf20@IrishCompSoc
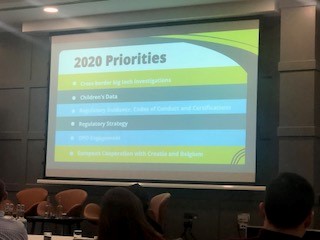
Data Protection Commission launches Statutory Inquiry into Google’s processing of location data and transparency surrounding that processing - https://t.co/3n5KnvTFyU
Chris Paterson will be running a live demonstration on how their program management tool helps companies to operationalise Data Protection Impact Assessment (DPIA) and Privacy by Design.
#dpia#privacybydesign#gdpr#gdprcompliance # #dataprotection
Few places left for the DPIA workshop on the 6 of February and only 24h to book! https://t.co/DWBu4HZSeX
Paul Walsh will guide you through:
Difference between a risk and crisis
Data Protection Impact as a GDPR requirement
Why DPIAs are required
Privacy by design
Waiting for @sheilafitzp at the #dpconf20 listen to her talking about the organisations that will thrive in a #privacy focused world and whether companies are truly embracing #DataPrivacy privacy.