We're excited to share that after achieving #SOC2Type1, Feedly has completed its SOC 2 Type 2 examination, verified by @Aligncompliance.
For #CTI teams operating under compliance mandates, this gives your InfoSec team a documented answer on how #Feedly protects your data.
https://t.co/G2D6w57SxV
@AICPA
Triaging an #IoC list means deciding which indicators are malicious enough to act on, and that usually means looking each one up in #VirusTotal separately and reconciling it by hand.
Feedly now pulls @virustotal#detectiondata directly into IoC Insights Cards: confirm if malicious in seconds, judge zero-detection domains from WHOIS, certs, and hosting, and trace your investigation into VirusTotal in one click.
Learn more: https://t.co/PX9EJGVl2a
12 new #AIprompts for #CTI work, free to use in any #LLM and grounded in what actually works for #threatintel.
Earlier this year our CTI Prompt Library covered the fundamentals. Volume 2 builds on it with prompt chaining, so a report can move through to a finished output in one pass.
https://t.co/Mlm0YK05Qk
We recently wrote a guide for operationalizing ASN data for threat detection with @feedly TI Essentials.
Check out how, when, and why to track ASNs alongside IOCs here: https://t.co/Vgxxd8pbwt
What's inside
- How to score ASNs with free tools
- Alerting vs. blocking
- Clustering to connect infrastructure
- Dive into Tycoon2FA
CTI teams need to process dozens of threat intel reports every week.
That’s why our #CTI Advisor Josh Darby MacLellan mapped out how to automate 5 workflows that cover #IOC enrichment all the way to stakeholder briefing.
Estimated time saved per report: 145–290 min
Full guide with actual prompts 👇
https://t.co/0Y74yp6a2H
AI won't make human capital less valuable it makes it more valuable. You can offload a task. You can never offload your learning.
The firms that win won't be the ones picking the best model, but the ones building a loop where people and AI compound on top of it.
Build a frontier ecosystem, not just a frontier model.
That's the whole game.
#MITRE ATT&CK is one of the most widely used frameworks in #cybersecurity, and its real power goes beyond technique mapping.
In our next #CTI Session, Amy and Lex from The @MITREattack Corporation walk through how to turn #TTPmapping into behavior-first detections that run in production.
https://t.co/59gsnWTcgN
#CTI practitioners are great at tracking adversaries but the best ones are also great at telling the story of why it matters.
Join us June 17 at 9AM PT!
We’ll break down the metrics that matter most at each stage of program maturity, and how to build a #businesscase that earns confidence from your #CISO and leadership team.
https://t.co/UhZUEFcj4F
Feedly #Threat Intelligence + #OpenCTI = a #CTI knowledge graph that's always ready!
We're excited to share our new integration with OpenCTI by @FiligranHQ and a sneak peek of how Feedly Threat Intelligence automatically delivers structured, contextual #OSINT directly into your OpenCTI knowledge graph so your analysts can jump straight to pivoting and investigating.
https://t.co/rs2NkjXoR7
Most #CTI teams want to be more proactive. Here's what that looks like in practice.
When #ScatteredSpider hit UK retail, Ian Parsons and his small team at @Quilter already had the full Dragon Force profile and an executive-ready report done the same afternoon.
Here's the challenge they faced and the workflow that changed everything 👇
https://t.co/YZRkOdMxu0
#ThreatIntelligence #CyberThreatIntelligence
If big companies can't make a net return on their LLM token costs, that doesn't mean it's impossible to. In fact this is exactly what you'd expect to happen with a new technology. Incumbents can't use it well, and are replaced by upstarts who can.
BFSI CTI teams juggle triage, incident response support, fraud coordination, and exec briefing, often at the same time.
That’s why we put together 10 prompt templates to help with #BFSI#CTI workflows: https://t.co/UrbJMN4tCG
#cybersecurity#threatintelligence
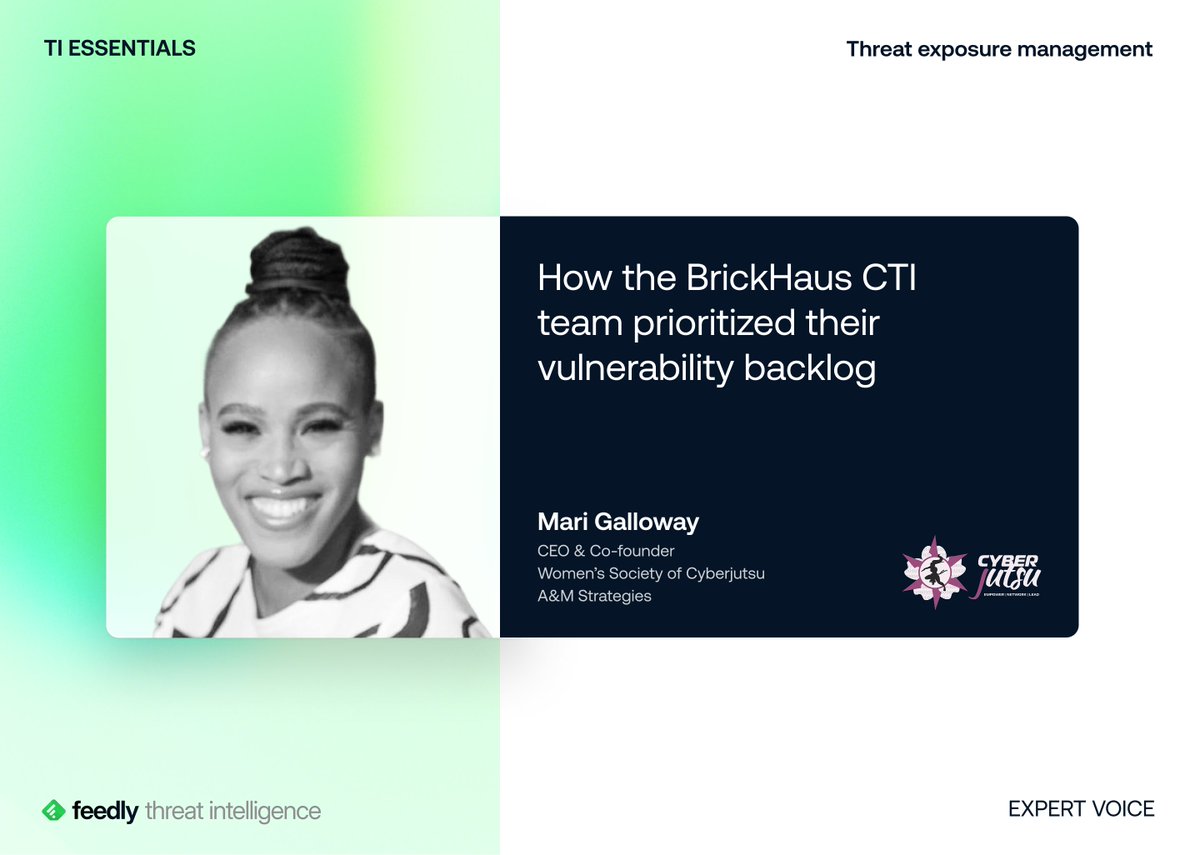
A #vulnerability rated MEDIUM sat unpatched for 3 months. Then #CISA added it to #KEV as actively exploited, CVSS 9.8.
That 3-month gap can be deadly. #CTI can help close it.
Mari Galloway, CEO A&M Strategies + CEO & Co-Founder of @WomenCyberjutsu walks through the exact playbook BrickHaus's #CTI team used to prioritize their vulnerability backlog.
https://t.co/GhDhM2JFsT
One Pharma security team is currently:
→ Pulling hundreds of #IOCs from 7,500+ sources without the manual work
→ Starting their day with a #TTP briefing waiting in MS Teams every morning at 7:30am
→ Monitoring #ScatteredSpider live and turning new TTPs into #detectionrules
Read the case study for the full breakdown 👇
https://t.co/67oUfXwgfS
In case you missed it…
We have a #TI Essentials article covering what good #cybercrime investigation actually looks like.
We sat down with Will Thomas (@teamcymru) and Garrett Carstens (@Intel471Inc) and did a deep dive from verifying #threatactor claims before you react, to #crypto tracing, to why you shouldn't try to engage criminals on the fly.
https://t.co/H7EOJiXqyF