@Hostinger No patching was needed. What was needed is to know that our site still works on the patch. Our end-to-end tests against production told us that.
@MsftSecIntel From 11 September the EU Cyber Resilience Act gives vendors 24 hours to file an early warning on an actively exploited vulnerability.
24 hours is not enough time for most vendors to find out what they shipped. It is only enough time to look it up.
Some of these releases went out through legitimate GitHub Actions workflows. Real signature, pipeline, but poisoned package.
Provenance tells you where it came from. Not what is inside it.
This will get worse before it gets better.
Microsoft Threat Intelligence is tracking active Mini Shai-Hulud npm supply chain attacks in which a threat actor compromised trusted maintainer accounts to distribute credential-stealing malware.
Compromised packages (confirmed malicious) include:
- [email protected]
- [email protected]
- [email protected]
- [email protected]
- qlik/[email protected]
- cacheable/memory, /utils, /net
- 17+ servicetitan/* packages (eslint-config, anvil-themes, table, form, log-service, etc.)
In this attack, a malicious preinstall hook launches an obfuscated dropper (setup.mjs) that downloads a Bun binary from GitHub and executes a credential-stealing payload, either Math_Symbol.js or Math_Init.js.
The payload is a Mini Shai-Hulud variant, a self-propagating npm supply-chain malware family. It harvests npm, GitHub, cloud and continuous integration (CI) credentials, exfiltrates collected secrets, and uses stolen publishing access to inject itself into package tarballs, increment their versions and republish the compromised releases.
Microsoft observed the same pattern across all affected packages, suggesting a single actor using multiple stolen tokens.
Microsoft Defender for Endpoint customers should act on these alerts: “Trojan:npm/MalBun.A”
Никола Цолов замени болида с колело и видя София по нов начин. И това не е случайно - столицата вече се синхронизира с ритъма на Giro d’Italia. 🚴♂️🇮🇹
На 10 май София ще бъде финал на третия етап от състезание с над век история - събитие, което приковава погледите на над 700 милиона души по света.
През всеки град, през който преминава, то е празник. Сега този празник идва тук, по улиците на София.
Ще има скорост, енергия и онези незабравими моменти, в които всичко се решава за секунди и които оставят следа в историята на столицата.
Нека излезем на улиците и направим София част от този празник, така че милиони по света да усетят атмосферата ѝ.
София не само мечтае за големи събития. Тя ги създава. 🚴♂️
Г-н Радев днес ни "изненада" с появата си Панорама. Беше обещал да стане това, което не "очакваме", а той просто е питал ChatGPT:
- какви са актуалните опорни точки в модерната политика? Тези точки, трябва да говорят на никой конкретно, но и на всички!
Какъв prompt според вас?
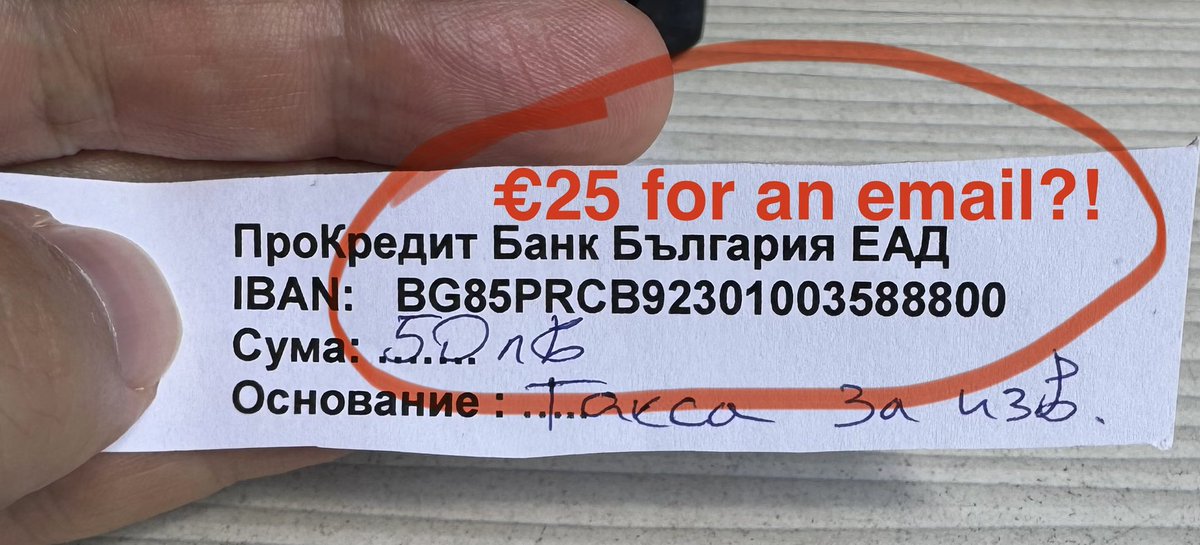
Ex-@procreditbank here:
Want your balance? Trek to their one building in all of Bulgaria, queue for the single guy at desk, then choose:
- pay 50 BGN/25 EUR for a 7-day email wait (proof below)
- beg for a printout like it’s 1999.
Banking or medieval quest? 😤
This is excellent break down of @karpathy insightful presentation.
I would argue about AI not replacing jobs, but it is what it is whether we like or not.
I'M BLOWN AWAY.
Andrej Karpathy just explained Software 3.0 at YC.
BIG IDEAS: English is coding. AI is electricity. And, build for LLMs, not just people.
Key takeaways:
@itsalexvacca AI “productivity” boost should not be measured in content volume. This is wrong and won’t last long.
Few decades ago programming was measured in line of code produced. That’s is not how it is now for a good reason - less is more.
Днес България е с една крачка по-близо до еврото.
Това ще означава повече инвестиции и обмен с партньорите от еврозоната и повече стабилност и просперитет за българския народ.
България също така ще заеме заслуженото си място при вземане на решенията в еврозоната.
Поздравления!