@h4x0r_dz@0xd0m7 Yea got the same experience hardcoded API key on a banking site, hitting the API with the hardcoded key and it was closed as OOS since https://t.co/0o2vJRd9wt was only in scope but the https://t.co/lhejshuIlQ is oos lmao...
@fr4vian When you think about it, it shouldn't be that hard to be able to sort out the slop from the real impactful bugs. So yea programs just be using this as an excuse.
@zack0x01_@sudosu01 I proved RCE like that and got scammed with only 100$ while the RCE bounty was set flat 10000$. Makes me really wonder if I should have went full blast even if I know its not allowed.
Altered Security Diwali Giveaway!
Win FREE access to:
• 1 CRTP seat
• 1 CARTP seat
How to participate:
• Like
• Comment & tag your Red Team buddies!
• Repost
Winners will be randomly announced on October 25, 2025
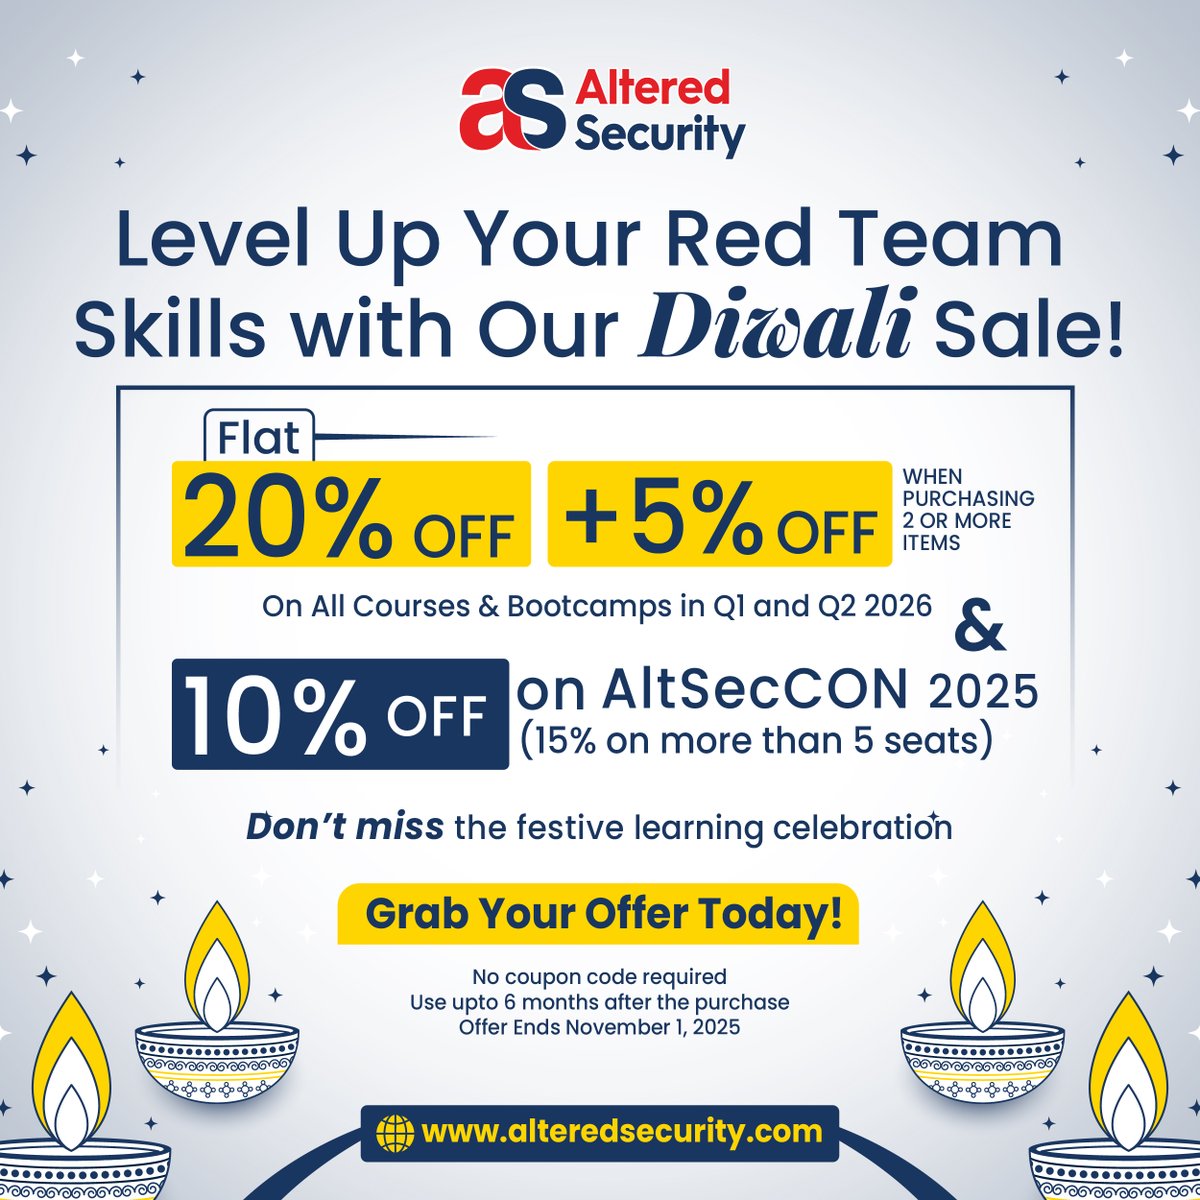
Our Diwali offers are already live - up to 25% OFF on Red Team labs & bootcamps and up to 15% OFF on AltSecCON 2025 tickets.
Bonus: Even if you’ve already availed our Diwali offer, you’re still eligible!
https://t.co/hp0GLwrqy7
Just published my first blog post "Hunting for postMessage Vulnerabilities"
https://t.co/oWxKEA6iHg
It covers 11 postMessage vulnerabilities I discovered on bug bounty targets. enjoy ☕️
#BugBounty#bugbountytips#websecurity