We gave Hackian better models. His score barely moved.
EthiBench F1: 66.1% → 66.6%.
Then we rebuilt the harness around the same models: 79.1%.
The models set the ceiling. The harness decides how close you get.
When you log in to the Ethiack portal, it starts with a choice: continuous exposure validation or run a pentest.
Let's talk about exposure validation. It's designed to set up continuous coverage across your entire attack surface.
Three steps, no overhead:
1. Enter your target domains
2. Define the scope and what assets are out of scope
3. Review and launch
You can assert test authorization in seconds and import multiple domains via CSV.
Try Ethiack now 👇
Continuous penetration testing doesn't just close gaps in your attack surface, it also provides much-needed peace of mind to your organization.
Here's Pedro Cunha, Security Officer and Data Privacy Officer at @Broadvoice talking about how Ethiack has helped the organization:
Ethiack has been featured in the Portugal Fintech Report 2026 by Portugal Fintech.
The report provides a look at the Portuguese fintech ecosystem, highlighting industry growth, innovation, collaboration, and the expanding influence of AI.
🚨 CVE-2026-123158 (sshole): OpenSSH sshd before 10.6p2 lets attackers log in over SSH without the password to certain accounts on musl-based Linux built without PAM, like Alpine.
Upgrade and restart sshd, or turn off password authentication.
https://t.co/a8Fpa2jhCE
Most ASM tools stop at discovery. They find assets. They don't tell you which ones an attacker can actually break into right now.
Hackian, Ethiack's agentic AI pentester, runs continuously against your discovered attack surface, chaining vulnerabilities, pivoting on failed attempts, building payloads on the fly. Every finding ships with reproducible proof of exploit: payload, evidence, and fix guidance your devs can act on.
This is validated exploitability, not just a longer inventory.
Learn more about how continuous discovery integrates with the validation layer
Testing an AI pentesting agent only once means you're only seeing half the picture of how it actually performs. 👀
Because LLMs are probabilistic, outputs change from run to run. In agentic pentesting, small shifts in early exploration multiply, leading to entirely different results by the end of an engagement.
A single run tells you almost nothing. But running dozens of end-to-end tests is expensive, so most teams test only 2 or 3 times. In this low-replication zone, standard p-value testing stops being reliable: with so few runs, a non-significant result often just means your sample size is too small to detect a real difference, not that the upgrade failed.
We built Ethibench to test AI pentesting agents properly, with the replication these systems actually need.
Find out more in the repo👇
CTFs are more active than ever.
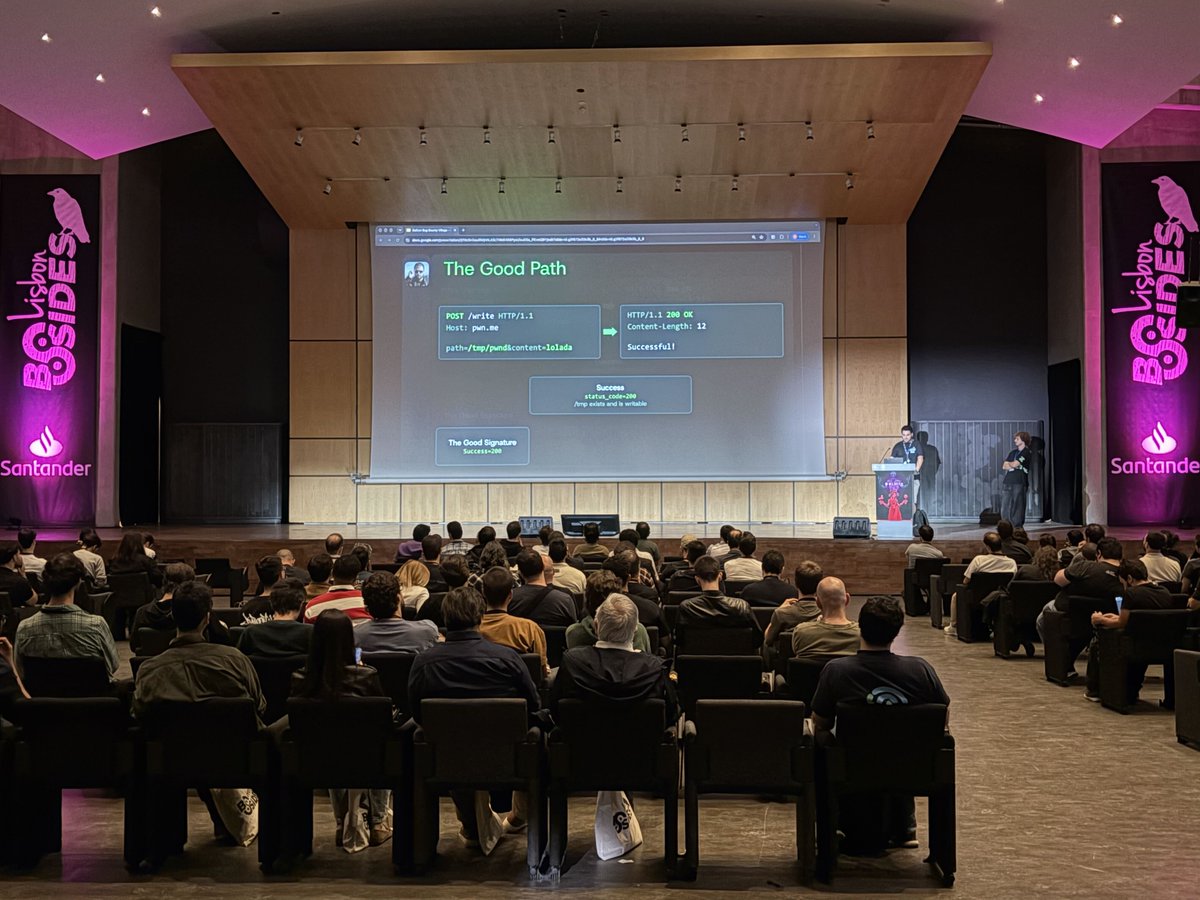
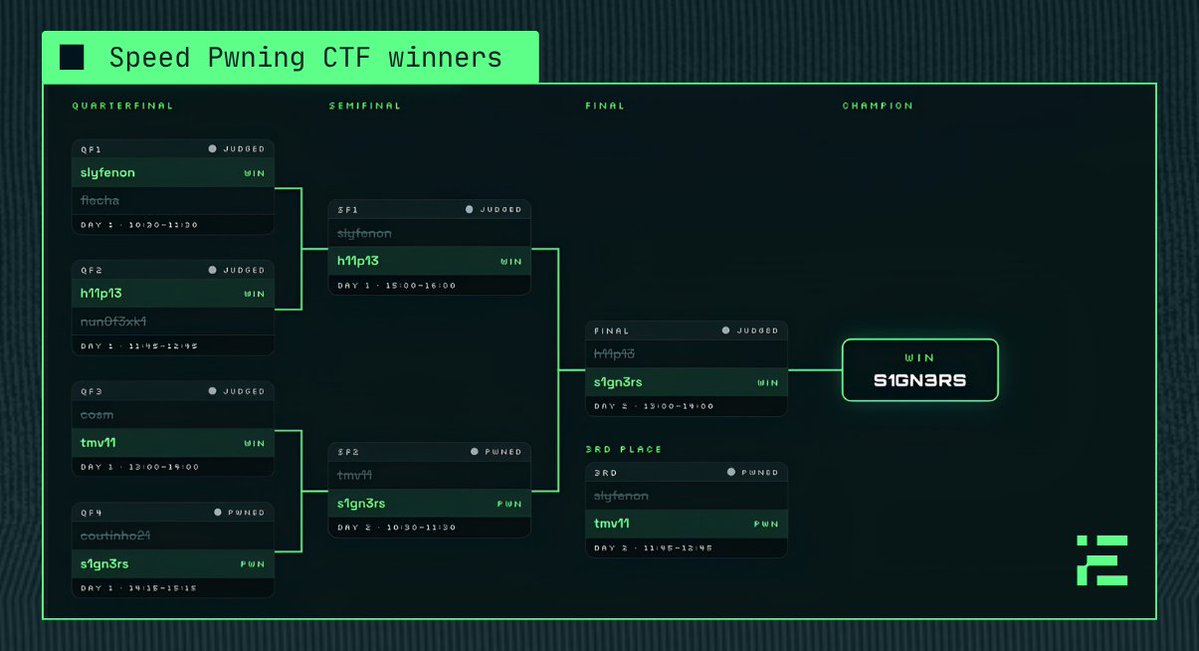
Last week at @BsidesLisbon, we ran a Speed Pwning CTF: No AI, human-only with players livestreaming their screens. Over 50 people stayed locked in to watch the competition.
Huge congrats to the winners:
🥇- s1gn3rs
🥈- h11p13
🥉- tmv11
SOHO Smashup winner: João Marono
Exploitation windows have collapsed from years to days to hours, with approximately 67% of exploited vulnerabilities now zero-days (zerodayclock).
What used to be an annual pentest cadence now leaves months of exposure between engagements, while a weekly vulnerability queue leaves days between "known" and "exploited."
To close this gap, we built Ethiack Zero, it tracks emerging vulnerabilities from the very first public signal (news, a vendor advisory, a KEV, a GHSA or the CVE record itself ) and validates actual exploitability before a CVE is even minted.
Learn more about Zero↓
For the second year in a row, Ethiack ran the CTF at @BSidesLisbon. The final match lasted over an hour and 15 minutes, and more than 50 people stayed to watch it live.
We also took the stage: Our Research team brought their DEFCON talk, “Write Once, Shell Everywhere: Turning Arbitrary File Writes into RCE,” to Lisbon.
Huge thanks to our team and to everyone who came to play, watch, and cheer. And to BSides Lisbon for having us back.
Stay tuned. we'll share more details in the coming days!