Cool research that outlines a jailbreak against many mazda head units. It requires physical access but can get root access via command injection and then can rewrite MCU firmware to send CAN messages since it doesn’t do secure update (really people??)
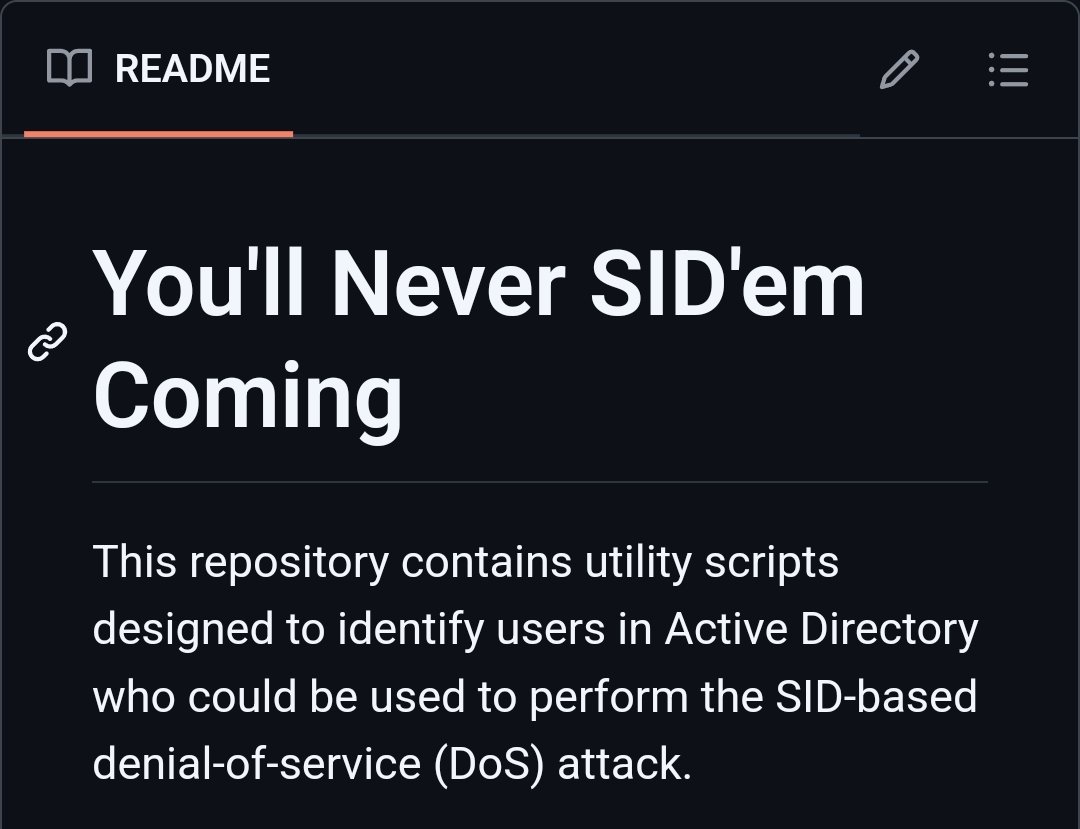
Did you know you can lock out ALL domain users (including Domain Admins!) by exceeding the Kerberos MaxTokenSize limit?
There are a few ways to do that.
I'll add links to the blogpost and #github repo in the comments .
@penterasec#redteam#activedirectory
New from 404 Media: we've confirmed that Apple quietly introduced code that automatically reboots an iPhone if it hasn't been unlocked after a period of time. This is why cops are being mysteriously locked out of iPhones they're trying to search. https://t.co/2YmUCmYoFD
New from 404 Media: police freaking out at iPhones stored for forensic examination mysteriously rebooting themselves. This makes brute forcing much harder. Cops hypothesize Apple pushed an update that tells nearby iPhones to reboot if not on phone network https://t.co/oJffld9GNx
"The Trump campaign’s research found that up-for-grabs voters were about six times as likely as other battleground-state voters to be motivated by their views of Israel’s war in Gaza." This is why Trump/Vance ramped up anti-war rhetoric in last few weeks of campaign https://t.co/doI1FOZVkW
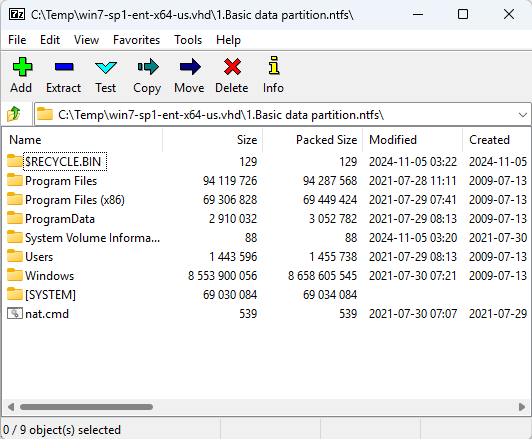
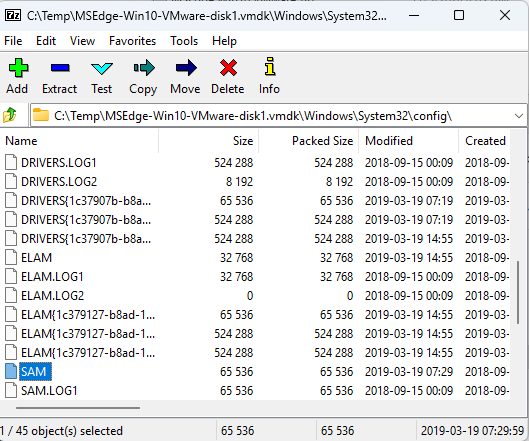
Did you know that 7z can browse .VHD and .VMDK files? You can open them right up, and even directly browse ntfs filesystems.
On a pentest and find a bunch of disk images? Copy the SAM/SECURITY/SYSTEM hives directly from the images, no mounting, copying, or fussing around.
I'm pretty sure the Chinese govt released this explicitly to slow down AI development in the West. They have excellent homegrown models, better than the older Llamas, it's the only actual explanation.
reminder that the bcrypt hash function ignores input above a certain length! so if you do bcrypt(username || password) for some reason, a sufficiently long username will make it accept any password. to fix this you can sha256 the input first.
INSANE writeup from @SophosXOps. I read it and re-read it a few times when it came out, just to wrap my mind around all of the incredible tradecraft from both attacker and defender.
Hats off to the team at @Sophos for documenting this so thoroughly.
https://t.co/vHJKUBKb48
Today, @CISAgov, @ODNIgov, and @FBI released a statement attributing yesterday's fake video destroying ballots in PA elections to Russia. Local election officials already debunked this video. Election officials are the trusted source for election info. https://t.co/Fz14mRSXQG
Lots of RC forum posts lately like:
“I am a hobbyist trying to <operate GPS jammed drone / lift unspecified heavy payload / vaguely mimic terminal guidance but for package delivery, obviously>. Can you help me?”
I miss the days of:
“Yo how do I make my Wii nunchuck fly???”
A 0-day exploited in the wild impacting FortiManager that (allegedly) enables a remote unauthenticated attacker to execute arbitrary API commands on devices... Waiting the public disclosure ⏳
https://t.co/fwWuF0gkxv
Da da da da da brrrrrr CVE-2024-47575 vvvzzzzzz prrrrrr.
Is what My nine months old wanted to express about Fortinet, if I’d have given her my phone. But I’m sure you can figure out what she means.
CONFIRMED!! Ken Gannon (@yogehi) of NCC Group (@NCCGroupInfosec) used 5 different bugs, including a path traversal, to get a shell & install an app on the #Samsung Galaxy S24. He earns $50,000 and 5 Master of Pwn points. #Pwn2Own#P2OIreland
Foreign intelligence services routinely target people online by posing as head-hunters, consultants, government officials, academics, and researchers. Here's what an actual Direct Message approach looks like, courtesy of the Australian Security Intelligence Organization.
For the second time in as many months, VMware attempts to patch a remote code execution vulnerability first documented — and exploited — at a Chinese hacking contest earlier this year.
https://t.co/kONRPv6bEJ