Comment2Shell: Zero Click Pre-Auth XSS to RCE in WordPress Core
One of our first contributors, @yeraisci_ (Security Researcher at Awesome Motive, Inc. and and current Top 1 of the WordPress bug bounty program), reported a pre-auth XSS vulnerability in WordPress comments that can be escalated to RCE when an administrator visits the injected page.
Read the technical details of CVE-2026-93485, an HTML parser issue in the wpautop() function that was recently fixed in the WordPress 7.1.1 security update
https://t.co/LZlHroivDK
Check out my latest writeup on mitigating RCE impact with defense in depth, using the recent responsibly disclosed OpenAI hack by @HacktronAI as a case study.
Exploring sandboxing, runtime restrictions, and reducing what an RCE can do.
https://t.co/GEVygonlc8
Introducing IDNSEC.
IDNSEC is a cybersecurity research and engineering society initiated by members of the Indonesian security community.
Our mission is to advance Indonesia's cyber defense and security research capabilities, while contributing useful research and engineering work to the global cybersecurity community.
Indonesia has a large and growing security community, with many capable researchers and engineers. We want to create a place where more of that capability can develop into deeper research, engineering, collaboration, and public technical work.
IDNSEC will publish writings in both English and Indonesian, covering security research, vulnerability research, defensive engineering, and analysis of cybersecurity issues relevant to Indonesia and the broader security community
Several research and engineering writings are already in the pipeline.
More about IDNSEC: https://t.co/zUYKuaeKun
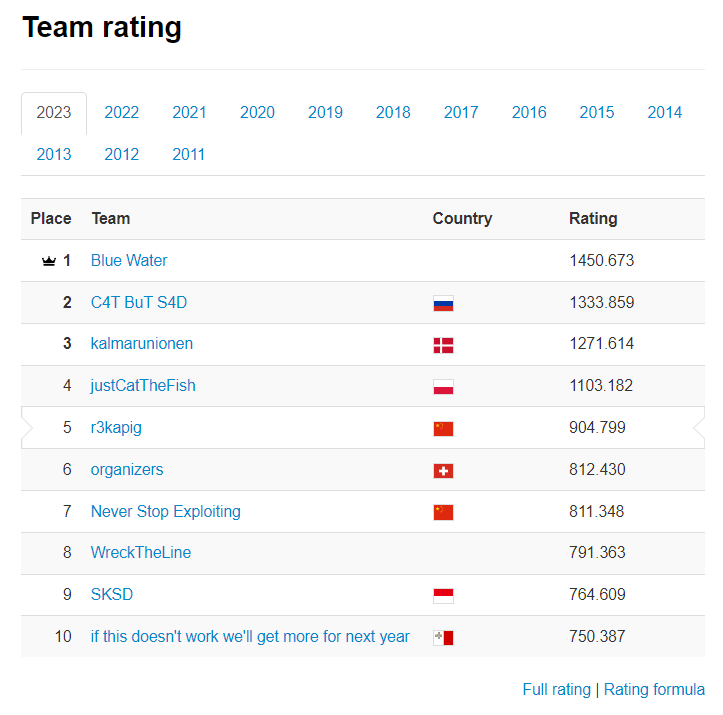
In 2023, we managed to unite some Indonesian CTF enthusiasts to establish the alliance team, SKSD. There's still a lot to learn, but thanks to the efforts of all team members, we're grateful to be among the Top 10 teams in the 2023 global CTF rankings. 🇲🇨
@Mohamed87Khayat yep, sometime I also found response manipulation that could lead to sensitive CRUD ops. By understanding that the real root cause is the broken auth design (not the response manipulation itself), usually we can find more bugs by analyzing the JS.
@Mohamed87Khayat if you could find a real issue with real impact after response manipulation, the client-side JS should be analyzed further to see if it's not a false positive. If it's really true positive then there is something really wrong with the web and you should find more bugs. [6]
@Mohamed87Khayat the later case (the program owner misunderstand their own web, probably because it's a legacy) happened quite a lot. The problem is, they don't understand that even after the patch for "response manipulation", the rendering for admin FE can still happen through another way. [5]
bi0sCTF 2022 is officially over!
Congrats to the winners:
🥇@thehackerscrew1
🥈@idekCTF
🥉SKSD
We hope you enjoyed the challenges, and hope to see everyone again later this year for bi0sCTF 2023!
Please do leave your feedback at https://t.co/Np5JdIDEUY.
#ctf#bi0sctf
This is my writeup for one of the web challenges from @RealWorldCTF 5th (2023), Dark Portal. A challenge with "normal" difficulty but only a few teams could solve it due to obfuscation. We used dynamic analysis and uncommon trick to solve it. https://t.co/6nbjTc3DYt