Head of Cyber Threat Intelligence @ Würth IT, GCTI/CPENT/CEH/CND/CSA/ECSA/ECIH/CTIA, owner of SATAYO CTI platform & deepdarkCTI - member of @Curatedintel
On 2 November 2026, two Administrator sessions on an internet-exposed Copeland XWEB Pro 1.9.0 refrigeration controller read settings across 31 devices. We examine the event log and its limits, and set out how operators can reduce exposure.
https://t.co/KJfzLze8FD
📢Finalmente ci siamo!
📍Domani, mercoledì 4 novembre, si terrà l'evento #SATAYO#Community#Connect!
🕑 L'appuntamento è per le ore 14:00 ad Egna (BZ), presso Würth Italia.
👉🏼 Se non siete ancora arrivati ad iscrivervi, fatelo subito da qui https://t.co/1d6lIiTWJg
☢️☢️☢️New #xpl0itrs ransomware gang. 4 victim organizations have been declared so far.
📌📌📌The DLS (Data Leak Site) link has already been tracked on the #deepdarkCTI project (https://t.co/1DYRpICrtY).
A new ransomware gang, #SevyWare, has advertised its RaaS services on #T1erOne. The moniker behind the post claims the gang includes former members of #Conti and #SLSH
No victim organizations have been identified so far. The data leak site has already been indexed on #deepdarkCTI
📢A new interview is available on #deepdarkCTI. This time, we wanted to delve deeper into the #NoName057 threat actor
☢️The pro-Russia hacktivist collective emerged in March 2022 following the Russian invasion of Ukraine
👉 You can read the interview at https://t.co/q95UQcmWIc
📢 A new interview is available on #deepdarkCTI. This time, we wanted to delve deeper into the #BreachForums, interviewing the forum owner, diencracked
🕵️♂️ The interview, which we publish in full, was conducted in May 2026.
👉 You can read the interview at https://t.co/iki5nALWEc
📢 A new interview is available on #deepdarkCTI. This time, we wanted to delve deeper into the #MedusaLocker ransomware gang.
🕵️♂️ The interview, which we publish in full, was conducted in May 2026 by Erez.
👉 You can read the interview at https://t.co/xDjTijSbZR
⚔️ The #SATAYO TIP becomes a key element in the continuous #threat#hunting process thanks to seamless integration with long-standing benchmark tools like Elastic Security and #MISP.
👉🏼 Read the full article at the link https://t.co/oNXNpRUj8r
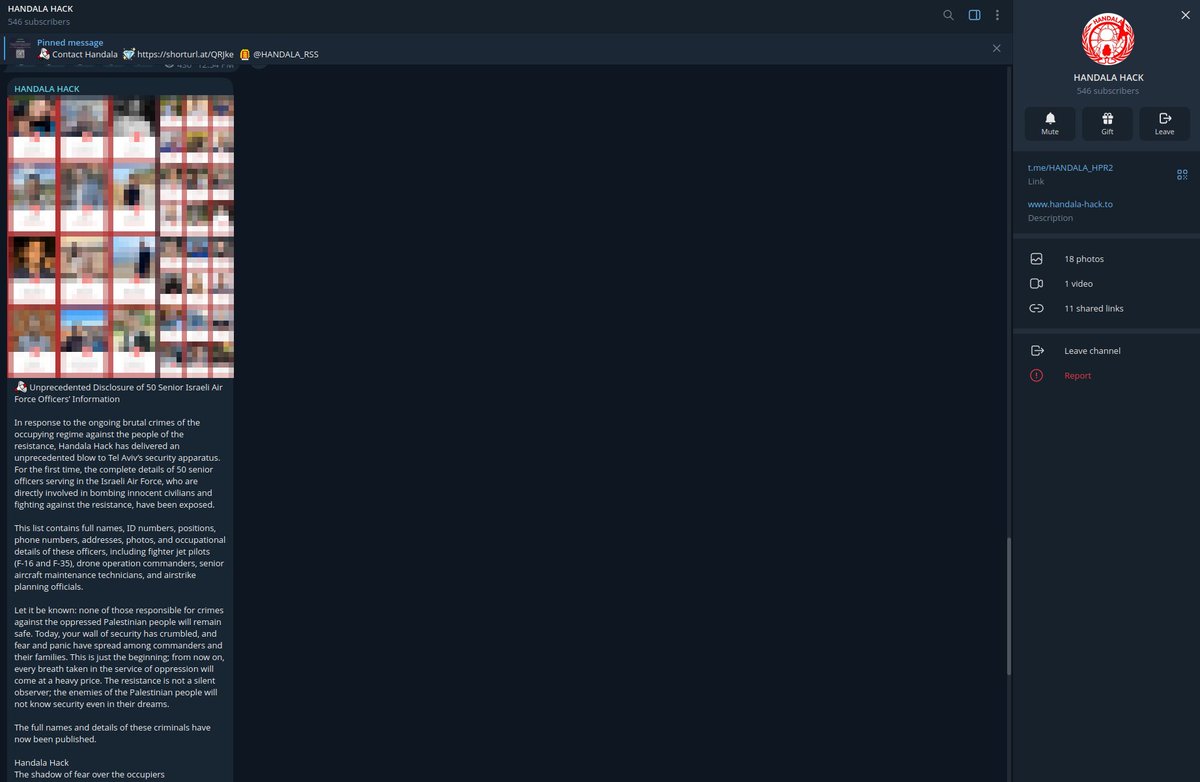
☢️ In recent days, the pro-Iran group #Handala has publicly released information regarding more than 180 profiles associated to the #Israeli#Air#Force and other strategic organizations/sectors.
👉🏼 Full article at https://t.co/6u2r6vKkxK
📢 New #Insomnia ransomware gang.
☢️ Active since October 2025, 17 victims published on their data leak site.
👉🏼 Onion link and TOX ID already available on #deepdarkCTI https://t.co/1DYRpICZjw
📌 How is the ransomware gang landscape evolving after the #RAMP forum seizure?
🔴 Another well-known forum seems to be becoming a point of reference in this field.
👉🏼 We discuss it in the article you can read at this link https://t.co/QULwlNQgXF
@0x6rss Yes, that chat contained a goldmine of information!
=== BAPHCHAT TELEGRAM CHAT ANALYSIS ===
Total records: 575,151
Unique users who wrote at least one message: 11,699
Top 3 most active users:
MissRose_bot: 11,362 posts
brucerivers: 7,534 posts
astounding: 7,442 posts
With 2025 now behind us, we can make some observations regarding the landscape of double-extortion #ransomware#attacks.
❓ Which ransomware gangs were the most active?
❓ Which sectors and countries were most affected?
👉🏻 Read the full article here https://t.co/RJ51GPcx1Z
📢 Recap of what happened in #deepdarkCTI in 2025:
✅ 586 commits
✅ 35 contributors
✅ 6,400 stars on GitHub
✅ 8 articles on https://t.co/MzpgQLnYdt
✅ 129 active users within the Telegram channel
✅ a total of 2,465 sources
🙏 Many thanks to the #deepdarkCTI community!
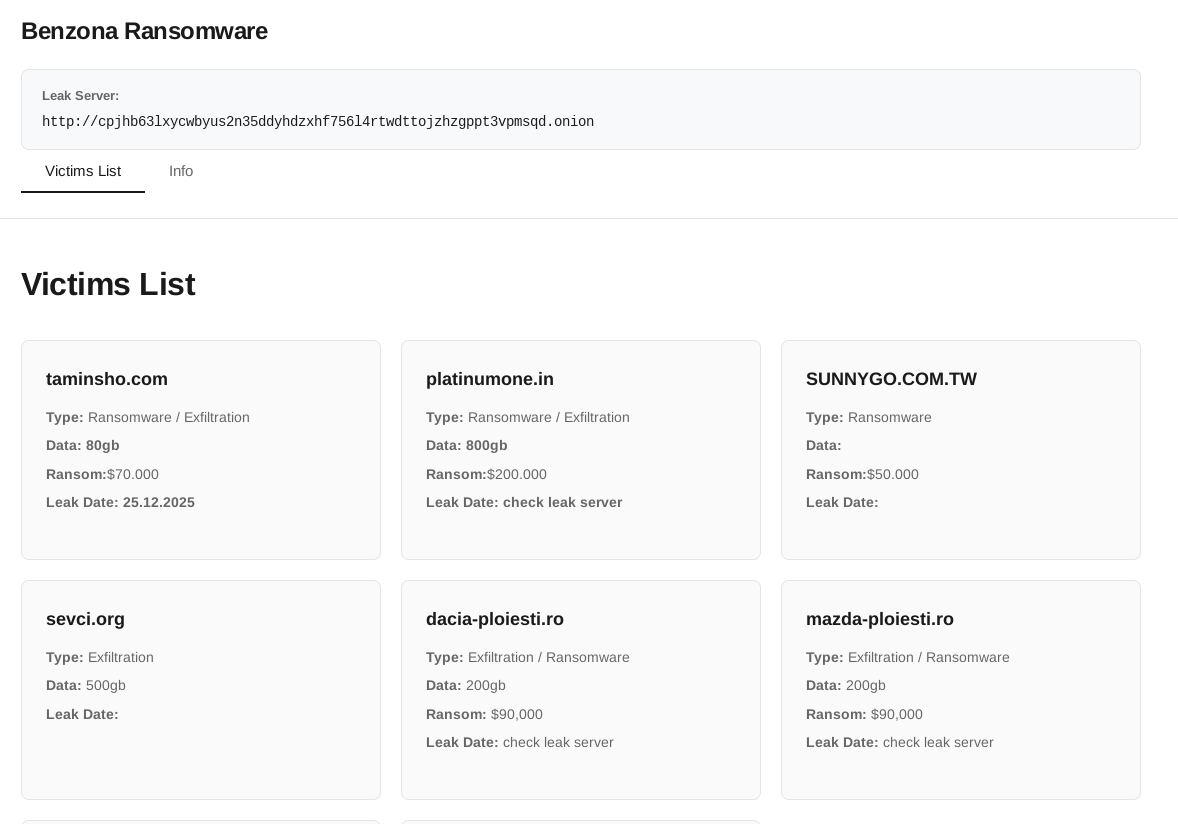
A new interview is available on the #deepdarkCTI project blog. This time, the interview concerns the #Benzona ransomware gang.
👉 You can read the full interview here https://t.co/UAnbGI8GLN
@MOHAMMADNI24249 Hi, the Telegram group of the project is reserved for contributors to the project itself. If you make a pull request to the project in Github by adding a source or if you want to write me in pvt, then I can send you the invitation link. Thank you!
🔴The problem of properly integrating #Threat#Intelligence into #Security#Operations processes is a recurring one.
📌 I wrote an article in which I described the integration process we have implemented.
👉🏻 Read the article here https://t.co/bcsxAQHRi9