Habakkuk 2:3 NKJV
[3] For the vision is yet for an appointed time; But at the end it will speak, and it will not lie. Though it tarries, wait for it; Because it will surely come, It will not tarry.
https://t.co/OYomIZq6YF
WhatsApp End-to-End Encryption vs. Forensic Extraction
Although WhatsApp uses end-to-end encryption to protect messages, calls, and shared media during transmission, this protection only applies while the data is moving between devices. Once the content reaches the device, it is stored unencrypted within WhatsApp’s local databases and media folders.
Out of the volumes of content, such as 733,543 WhatsApp messages, along with videos, audios, images, and documents.
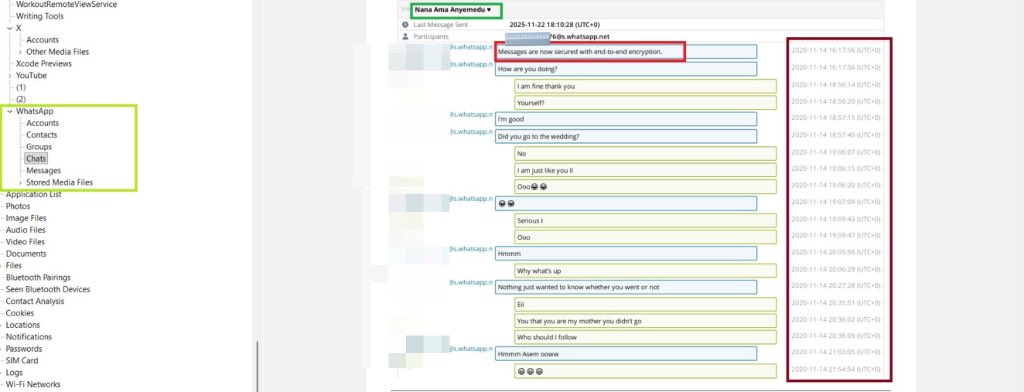
I was able to get a conversation between my kid sister @ama_Anyemedu in November 11, 2020.
The chat preview shows a typical WhatsApp conversation recovered from a mobile forensic extraction. At the top of the chat, WhatsApp displays the standard banner “Messages are now secured with end-to-end encryption.”
This banner simply means that when messages are being transmitted between two devices, WhatsApp’s servers cannot read them because they are protected by encryption keys stored only on the users’ devices.
However, end-to-end encryption does NOT protect data stored on the device itself.
Mobile forensics work by accessing the phone’s internal storage, not by intercepting messages from WhatsApp servers. Once a device is unlocked or decrypted by the lawful extraction process, the tool can read the local WhatsApp databases stored on the device (usually the `msgstore.db` and related SQLite databases).
This is why, despite the presence of the "end-to-end encryption" banner, the forensic tool is still able to extract:
* Full chat history
* Timestamps
* Participants
* Message contents
* Attachments
* Deleted messages (if still recoverable in the database)
End-to-end encryption protects data in transit, not data *at rest* on the device.
Forensic tools exploit lawful access to the device’s decrypted file system, enabling them to parse and display the stored WhatsApp database, which is why you can see the complete message timeline, content, and timestamps on the right side.
‼️ Chrome users, update now! ‼️
Google has released an update for its Chrome browser to patch six security vulnerabilities, including one zero-day.
https://t.co/xfr7EkPGDZ
A system was completely locked up by malware. Antivirus failed. We had no access to the hard drive…
But we had one thing: a full packet capture.
Here’s how I used Wireshark to trace the infection, extract the malware, and analyze its behavior.👇
The Setup:
The infected host: 12.183.1.55
I had the full .pcap from the time of infection.
My goals:
Identify where the malware came from
Extract the file from the packet data
Analyze what the malware did
Look for signs of worm-like propagation