Modern offline first Application Security Intelligence Platform for Android, iOS, Flutter and React Native with attack-chain analysis, explainable findings, source exploration, AI-assisted investigation and professional reporting.
Resource/Credit: https://t.co/GpiUjONqfx
Built a mobile application security platform from the ground up.
Static analysis for Android & iOS, designed to help security engineers find what matters faster.
Meet Beetle. 🪲
🔗 https://t.co/Q87R5dvg3H
#AppSec#CyberSecurity#Android#iOS#MAST#InfoSec
Flutter apps quietly break most SSL pinning bypasses.
On a recent pentest, reFlutter, Objection, and the usual Frida scripts all failed — zero traffic in Burp.
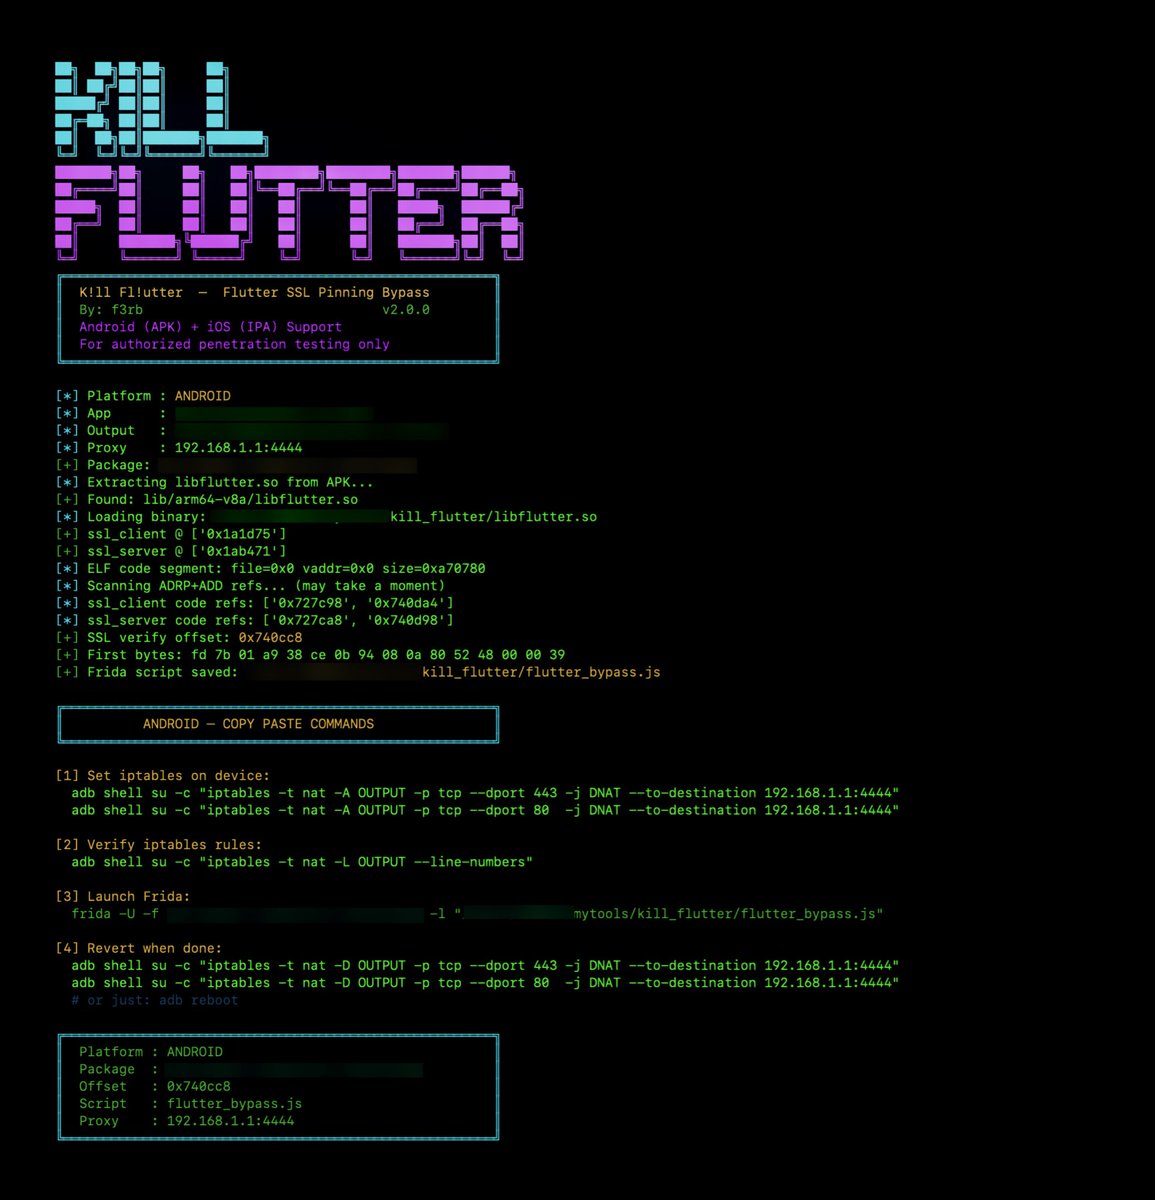
So I built K!ll Fl!utter 🔪
Automated Flutter SSL bypass, Android + iOS.
🔗 https://t.co/Dd2c8Oo1aa
Point it at an APK or IPA → get a ready-to-use Frida script + copy-paste commands.
Works across Flutter versions. Android & iOS.
Open sourced for authorized mobile testing 👇
🔗 https://t.co/Dd2c8Oo1aa
#Flutter#MobileSecurity#Frida#PenTesting
K!ll Fl!utter finds the cert-check function fresh in each binary — using fixed BoringSSL string markers + ARM64 addressing, not a hardcoded offset or version table.
It recalculates the offset every time, so the Frida hook lands on any build.
No Ghidra. No manual RE.
Why the usual tools fail:
• Objection/SSL Kill Switch hook OS trust APIs — Flutter never calls them
• Frida scripts hook a hardcoded offset — but that offset changes in every Flutter build
• reFlutter needs the version in its table — new builds aren't recognized
@0xRAYAN7 I tried it, its actually pretty good to confirm vulnerabilities identified in active scans but the only issue that Im facing is once the session got expired we have to scan again, idk is there a option to scan requests from repeater or history directly
Don't forget to capture a moment at our photo stations! Share your photo and tag us on Twitter/X or LinkedIn for a chance to win an exclusive BlueHat Yeti cup and shopping tote. #BlueHatIndia