Built & verified an end-to-end JML Identity Pipeline today! 🔐
🛠️ Windows Server 2022 AD + Okta Workforce
🔄 Profile Sourcing & OEL Mapping
🔑 Delegated Auth (DelAuth via HTTPS)
⚡ Dynamic Group Rules (Automated RBAC)
Lesson learned: You can't force enterprise hybrid sync onto a developer tenant!
Upgrading to the Okta Workforce 30-Day Free Trial now to get full access to the AD Agent, Universal Directory, & Lifecycle Management. 🚀 #IAM#Cybersecurity#Okta#ActiveDirectory
The Integrator plan is designed for app developers testing OIDC/SAML—it completely excludes on-prem AD agent endpoints. The 404 was simply Okta saying: "That feature endpoint doesn't exist on this plan tier."
- Explored DNS/SRV records, FSMO roles, SYSVOL
- Figured out how much PowerShell I actually need (not much, tbh)
Tomorrow: Okta integration.
#IAM#ActiveDirectory#Okta
IAM lab build 🧵
- Actually understood A-G-DL-P (not just memorized it)
- Built a full permission chain: group → group → shared folder, tested live across 2 VMs
- Restructured my OU hierarchy (Tier-0 isolation, centralized groups)
Broke my AD lab today. Repeatedly. Building toward IAM engineering, one troubleshooting session at a time.
Today: Group Policy + password hardening, AD tiering & Kerberoasting audits, domain-joining a client VM (RIP my evening, courtesy of DNS + a Windows Home edition plot
Now that the AD foundation is solid, the next step is finally installing the Okta AD Agent, configuring Delegated Auth, and running our first inbound sync into Universal Directory.
Brick by brick. 🚀 #IAM#Cybersecurity#Okta#ActiveDirectory
It’s been about a week since my last lab update, but work behind the scenes hasn't stopped.
My original plan was to build a Windows Server AD DC and immediately link it to Okta via the AD Agent. But once I got inside Windows Server 2022, I got completely carried away. 🧵👇
I also set up Fine-Grained Password Policies (FGPP) using Password Settings Objects (PSOs) in ADAC to enforce strict security rules on privileged accounts, rather than relying on standard global GPOs.
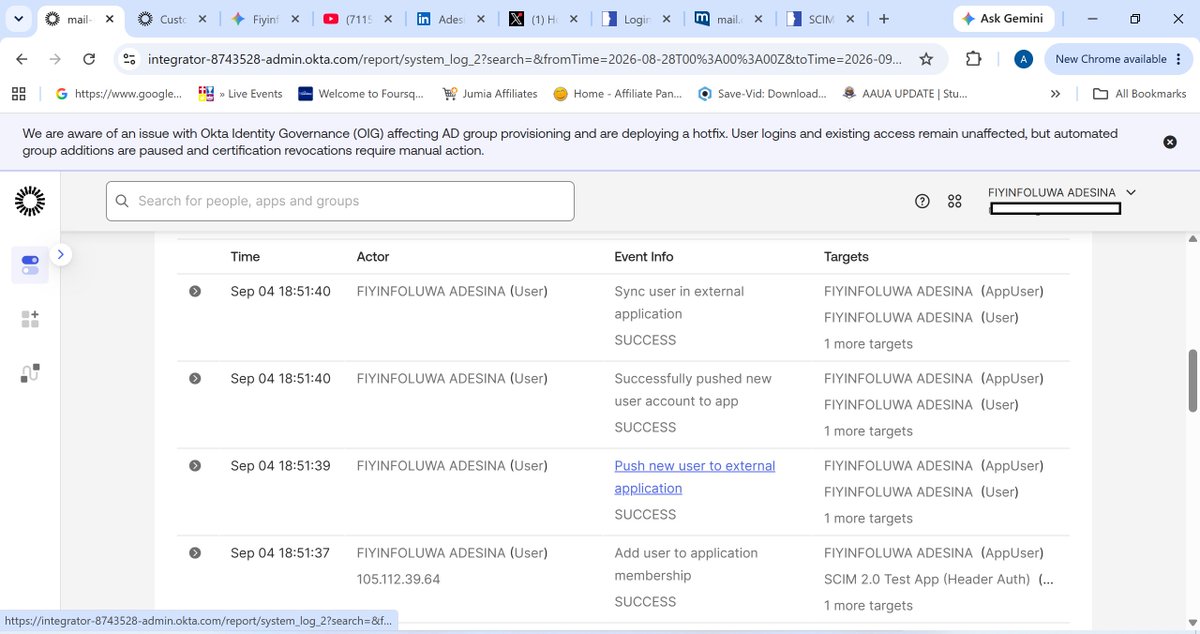
3️⃣ Automated Lifecycle (JML): Verified outbound POST calls for user creation and PATCH calls (active: false) for deprovisioning upon unassignment.4️⃣ Checked System Logs (app.provision.user.deactivate) to trace API responses.
Took a 4-day break due to personal challenges, but I’m back on my IAM grind! 💥 Today I proved live SCIM 2.0 provisioning & Dynamic Group automation inside my @Okta developer tenant (integrator-8743528). 🧵👇 #BuildInPublic#IAM#Cybersecurity
1️⃣ Dynamic Group Rules: Automated user assignments based on attribute conditions. No manual group additions needed.2️⃣ SCIM 2.0 Integration: Linked Okta to https://t.co/fc4GKe1ren using Bearer token authentication.