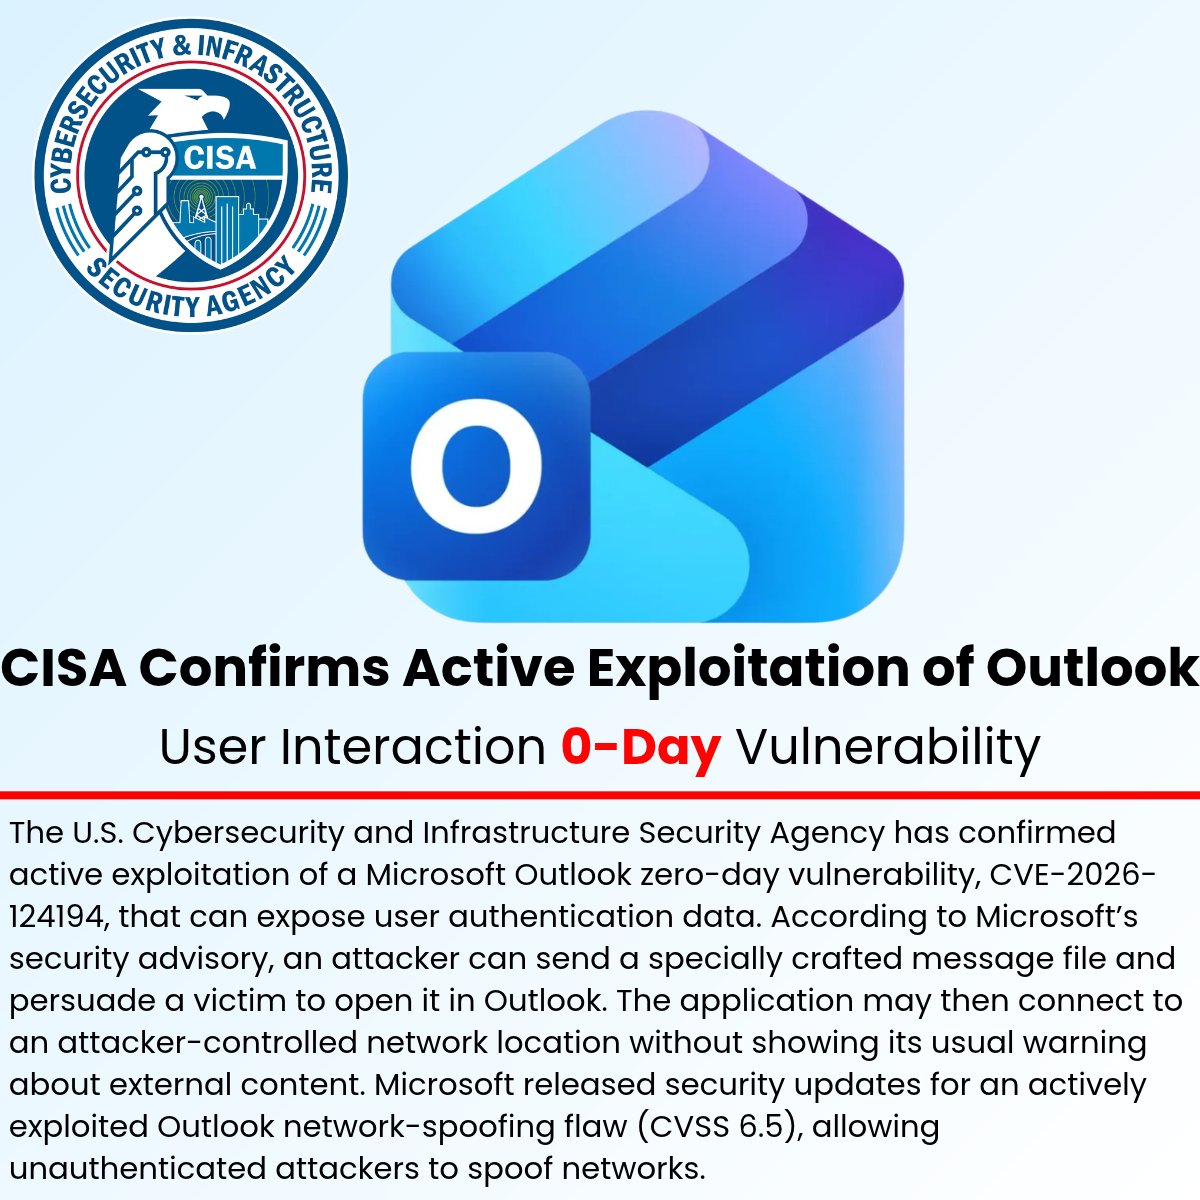
‼️ CISA Confirms Active Exploitation of Outlook User Interaction 0-Day Vulnerability
Details: https://t.co/9hqn7XHeqI
The U.S. Cybersecurity and Infrastructure Security Agency has confirmed active exploitation of a Microsoft Outlook zero-day vulnerability, CVE-2026-124194, that can expose user authentication data.
According to Microsoft’s security advisory, an attacker can send a specially crafted message file and persuade a victim to open it in Outlook.
The application may then connect to an attacker-controlled network location without showing its usual warning about external content. Microsoft released security updates for an actively exploited Outlook network-spoofing flaw (CVSS 6.5) that allows unauthenticated attackers to spoof networks.
#CybersecurityNews
Infectan iPhones con spyware mediante anuncios de Instagram sin clics
Anuncios maliciosos en Instagram para infectar iPhones vulnerables con el spyware DarkSword (variante P7)
El ataque, que utilizó un anuncio relacionado con la Copa del Mundo, permite exponer información sensible de los usuarios sin necesidad de que hagan clic en el anuncio, descarguen archivos o instalen aplicaciones
https://t.co/qnyY1rAWqG
La Policía Nacional del #Ecuador 🇪🇨 (@PoliciaEcuador) estaría sufriendo un tercer #ciberataque en lo que va del 2026. El grupo The Gentlemen lo ha señalado en su blog como una posible víctima de un ataque de #ransomware.
@MinInteriorEc
Monitorea este y los demás incidentes de la #PoliciaEcuador en VenariX https://t.co/FAJHiLDQYW
Un usuario de un foro de #hackers habría publicado #dataleak potencialmente vinculado al Consejo Nacional Electoral del #Ecuador 🇪🇨 (@cnegobec), un organismo gubernamental que organiza, administra y supervisa todos los procesos electorales en #Ecuador.
Monitorea este incidente en #VenariX ➡️ https://t.co/OW9Te2XdwS
#InfoSec #Quito #CiberSeguridad #CiberAtaque
CYBER INTELLIGENCE ALERT: WAVE OF DDoS ATTACKS AGAINST ECUADORIAN STATE INFRASTRUCTURE 🇪🇨 ⚡
[STATUS: DENIAL OF SERVICE (DDoS) ATTACK]
A series of coordinated distributed denial-of-service (DDoS) attacks have been detected against multiple Ecuadorian government websites.
Threat Actor: Attributed to "Hider_Nex".
Scope: Multiple critical government entities have been impacted simultaneously.
Affected Entities and Availability Reports
The attack has caused disruptions to the web services of the following institutions:
Superintendency of Popular and Solidarity Economy (SEPS): https://t.co/mkrY05ooNA [Report: https://t.co/lGhGJzUuNR]
National Institute of Meteorology and Hydrology (INAMHI): https://t.co/02ZJtSlGoQ [Report: https://t.co/eWwb4tFBjk]
Superintendency of Companies, Securities and Insurance: https://t.co/qFroeLdzEp [Report: https://t.co/kAiGdyiCI0]
Council for Citizen Participation and Social Control (CPCCS): https://t.co/kpiStn72Od [Report: https://t.co/5BzyVWKqez
Ecuadorian Electricity Corporation (CELEC EP): https://t.co/qRA8v8XOsz [Report: https://t.co/nvTjzeaUR8]
National Electricity Corporation (CNEL EP): https://t.co/KR4wbz94ao [Report: https://t.co/v9KatBhzod]
Guayaquil Port Authority (APG): https://t.co/UBy5gM4dzY [Report: https://t.co/TyH65BCnlp]
Ecuadorian Transit Commission (CTE): https://t.co/y1pC5dB1cI [Report: https://t.co/AgTe7DFG6p
Security Considerations ⚠️
Operational Impact: These attacks primarily aim to disable citizen access to information portals and procedures, causing significant disruption to the continuity of digital public services.
Recommendations 🛡️
Mitigation of Malicious Traffic: Affected institutions are required to urgently activate DDoS protection protocols, including the use of Web Application Filtering (WAF) solutions to mitigate illegitimate traffic.
Monitoring and Resilience: Government IT teams are urged to strengthen the resilience of their internet-facing services and collaborate closely to identify the attack vector and prevent future intrusions.
#CyberSecurity #Ecuador #DDoS #GovernmentSecurity #ThreatIntelligence #CyberAlert #VECERT #UnderInvestigation
🚨 🇪🇨 CYBER INTELLIGENCE ALERT: ALLEGED DATA COMPROMISE AND EXFILTRATION (GUALAQUIZA COOPERATIVE)
⚠️ STATUS: VISIBLE EVIDENCE; UNCONFIRMED
Malicious activity has been detected on cybercrime forums where the threat actor "VandalsGroupCh" claims to have compromised the systems of the Gualaquiza Cooperative in Ecuador.
🏢 Affected Entity: Gualaquiza Cooperative
👤 Threat Actor: VandalsGroupCh
📊 Volume: 30,000 member records
📅 Publication Date: May 30, 2026
🛠️ Access Vector: Exploitation of vulnerabilities in the Vimasistem platform (use of webshell + adminTool for root access to the database).
🔍 Scope of Exposed Data
The actor has published a JSON sample containing highly sensitive information about its associates, including:
Identification Data: Full names, national identification numbers, fingerprint codes, and nationality.
Personal Information: Profession, date of birth, age, marital status, and education level.
Geographic Data: Province, canton, and parish of residence and birth, along with the exact physical address.
Family Relationships: Parents' names.
Banking Information: Structure for banking access data (although specific user information, mobile phone number, email, and account number appear hidden in the sample, the breach confirms the exposure of this data structure).
🛡️ Recommendations and Mitigation
Containment: It is critical that the IT department of the Gualaquiza Cooperative and the provider Vimasistem immediately audit the servers to close the backdoors (webshells) used and revoke unauthorized root access.
User Notification: The entity must inform the 30,000 affected members about the exposure of their personal and financial data to prevent fraud.
Identity Protection: Cooperative users are advised to be extremely vigilant against possible phishing, social engineering, or identity theft attempts, and to request a change of their online banking passwords.
⚡Strategic Monitoring Tools
Intelligence Platform: https://t.co/wk9bZJ2Nli
Security Verification: https://t.co/5LuqwzYuS6
#CyberSecurity #Ecuador #DataLeak #Vimasistem #Gualaquiza #BreachAlert #CiberAlerta #VECERT #FinancialInfrastructure
🚨 🇪🇨 CYBER INTELLIGENCE ALERT: POSSIBLE DATA BREACH AND ILLEGAL ACCESS — ECUADOR
⚠️ DETECTION OF ACTIVITY BY THE ‘VANDALSGROUP’ AGAINST ECUADOR'S PUBLIC INFRASTRUCTURE
[STATUS: UNCONFIRMED / UNDER INVESTIGATION / SAMPLES PRESENT]
Malicious activity attributed to the cybercriminal group VandalsGroup has been detected. They have published records that allegedly affect the population of Ambato, Ecuador.
According to the information displayed, the actor claims to possess a database with 490,000 citizen records.
It is crucial to note that these claims have not been independently confirmed by Ecuadorian authorities and are currently under investigation.
🎯 Affected Entities:
Municipality of Ambato
Provincial Government of Tungurahua
👤 Threat Actor: VandalsGroup
🌍 Location: Ambato, Tungurahua, Ecuador
📊 Data Visualized in the Samples (Proof of Concept)
Data structures consistent with sensitive information of Ecuadorian citizens were identified in samples from the actor. The visualized samples (Proof of Concept) contain the following fields:
National Identification Numbers (ID cards).
Registration Codes.
Full Names.
Dates of Birth.
🛡️ Security Recommendations
⚠️ Immediate Forensic Audit: The IT teams of the Municipality of Ambato and the Provincial Government of Tungurahua are advised to conduct an urgent audit of their web servers to identify and remove the reported webshells.
🛡️ Containment Action: Close all unauthorized access to the intranet and conduct a thorough review of access logs to determine the extent of the exfiltration.
⚡ Strategic Monitoring
🌐 Intelligence System: https://t.co/wk9bZJ2Nli
🛡️ Quickly assess your website's security with: https://t.co/YnDw1QjN9c
#CyberSecurity #DataLeak #Ecuador #Ambato #Tungurahua #VandalsGroup #ThreatIntelligence #CyberAlert #VECERT #UnderInvestigation #NoConfirmation
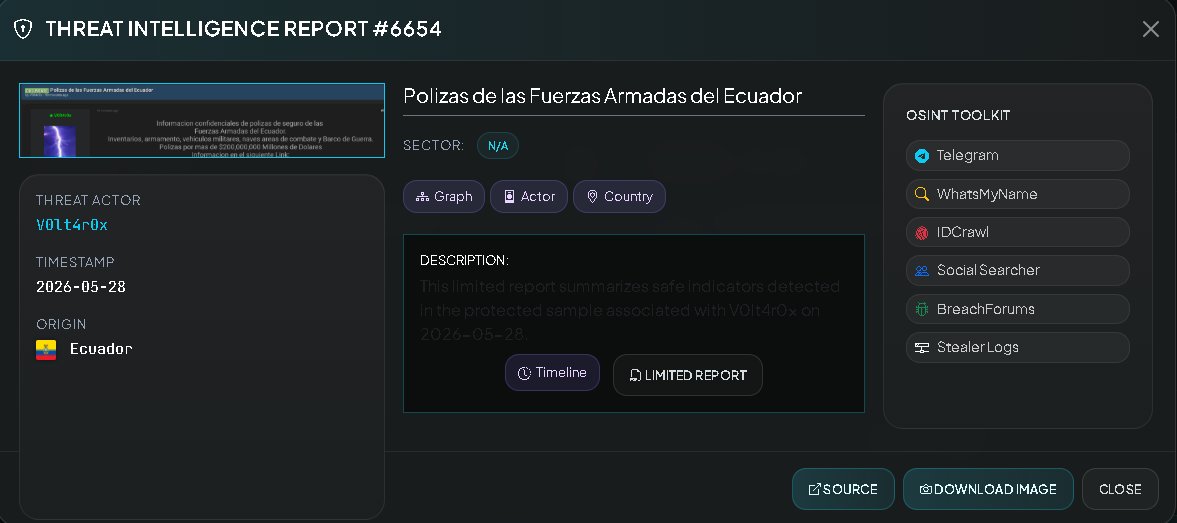
🚨 🇪🇨 STRATEGIC CYBER INTELLIGENCE ALERT: ALLEGED LEAK OF MILITARY DOCUMENTS — ECUADORIAN ARMED FORCES
[STATUS: UNVERIFIED / UNDER INVESTIGATION / SAMPLES PRESENT]
A post has been detected by the threat actor identified as V0lt4r0x, who claims to have obtained detailed confidential information regarding the insurance policies of the Ecuadorian Armed Forces. According to the post, the material includes inventories, weaponry, military vehicles, combat aircraft, and warships, with policies valued at over $200,000,000.
The attacker has provided an external link to download the content and has attached previews of the documents.
🎯 Affected Entity: Ecuadorian Armed Forces.
📂 Volume and Scope: Alleged insurance policy documentation, valued at over $200 million, including inventories of strategic assets (land, air, sea).
👤 Threat Actor: V0lt4r0x.
⚠️ Verification Status: UNVERIFIED / UNDER INVESTIGATION. Although visual samples of documents that appear to be official have been provided, the veracity, integrity, and full scope of the leak still need to be confirmed by the appropriate authorities.
📊 Data Exposed (as shown)
The screenshots specifically suggest the exposure of sensitive technical and financial information, including:
Strategic Assets: Inventories of buildings (hangars, dormitories, workshops, administrative offices, warehouses) and values associated with air bases.
Financial Information: Breakdown of costs by facility and asset categorization.
Operational Terminology: Documents referenced under names such as "INSURANCE SUMMARY.pdf" and "TERMS OF REFERENCE.pdf".
🛡️ Mitigation Recommendations
🔍 Security Audit: Conduct a review of the systems hosting public procurement and insurance documents related to the Armed Forces.
🛡️ Intelligence Monitoring: Continue monitoring the source forum and the provided link, assessing the impact of the exposure of this inventory of strategic assets.
⚡ Strategic Monitoring
🌐 Intelligence System: https://t.co/wk9bZJ2Nli
🛡️ Quickly assess your website's security with: https://t.co/YnDw1QjN9c
#CyberSecurity #DataLeak #Ecuador #ArmedForces #V0lt4r0x #ThreatIntelligence #CyberAlert #VECERT #UnderInvestigation #StrategicAssets
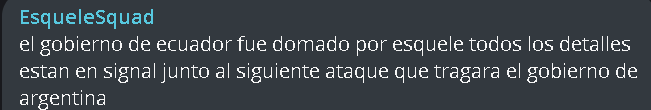
🚨 CYBER INTELLIGENCE ALERT: CLAIM OF RESPONSIBILITY AND ATTACK THREAT — GOVERNMENTS OF ECUADOR AND ARGENTINA 🇪🇨🇦🇷
⚠️ "ESQUELESQUAD" GROUP CLAIMS TO HAVE COMPROMISED ECUADOR AND ANNOUNCES OFFENSIVE AGAINST ARGENTINA
[STATUS: CLAIM OF RESPONSIBILITY PUBLISHED / IMMINENT THREAT / MIGRATION TO ENCRYPTED CHANNELS]
Through monitoring of clandestine communication channels, a message published by the cybercriminal group calling itself EsqueleSquad has been identified. In its statement, the threat actor claims to have successfully compromised the government of Ecuador. Additionally, the group issues a direct warning, announcing that its "next attack" will be directed against the government of Argentina.
🎯 Affected Entities:
Claimed Victim: Government of Ecuador.
Imminent Threatened Target: Government of Argentina.
👤 Threat Actor: EsqueleSquad.
📂 Incident Type: Claim of Intrusion and Threat of Cyber Sabotage/Attack.
⚙️ Operations Channel (OPSEC): The group indicates that technical details of its operations are being shared through the encrypted messaging application Signal.
🛡️ MITIGATIONS AND PREVENTIVE RECOMMENDATIONS
🛑 Early Warning (Argentina): The National CSIRT of Argentina (ArCERT) is advised to elevate its alert level regarding the perimeter monitoring of .gob.ar domains, paying particular attention to anomalous traffic spikes (DDoS) or attempts at SQL injection and authentication bypass on ministerial portals.
🔍 Compromise Verification (Ecuador): Government entities in Ecuador must audit their identity management systems and citizen databases to confirm or rule out recent data exfiltrations that would validate the claims made by "EsqueleSquad."
#CyberSecurity #CyberThreat #EsqueleSquad #Ecuador #Argentina #Hacktivism #ThreatIntelligence #CyberAlert #VECERT #Infosec #LATAM
🚨 CYBER INTELLIGENCE ALERT: ALLEGED DATABASE LEAK OF THE MINISTRY OF ENVIRONMENT AND ENERGY — ECUADOR 🇪🇨
[STATUS: UNDER INVESTIGATION, SAMPLES NOT EVALUATED / UNCONFIRMED]
The threat actor identified as Skull1172, operating in coordination with or under the influence of the EsqueleSquad group, has published and released an alleged internal database of the Ministry of Environment and Energy of Ecuador (MAE). The illegally distributed data contains administrative access credentials and compromised records of ministry employees. The information has been openly exposed in structured JSON format, compromising the authentication vectors of one of the country's most strategic government agencies.
🏢 Affected Entity: Ministry of Environment and Energy of Ecuador (MAE - Government of Ecuador).
👤 Threat Actor: Skull1172
⚔️ Attack Vector: Extraction of production database / Compromise of internal user identity control repositories.
🛡️ TECHNICAL RECOMMENDATIONS AND PREVENTIVE MITIGATION
🚫 Mass and Forced Revocation of Credentials (Immediate Action): The IT team and the Ecuador CERT are urged to immediately invalidate all passwords, access tokens, and institutional email accounts of employees belonging to the ministry.
🔄 Active Directory Audit: Monitor and audit Active Directory authentication logs for anomalous access or the creation of fake persistent accounts by the attacker before the leak was published.
📊 MONITORING AND EVALUATION
Intelligence System: https://t.co/wk9bZJ2Nli
Quickly assess your website's security with: https://t.co/QZhWp0kFrO
#CyberSecurity #Ecuador #MAE #Skull1172 #EsqueleSquad #GovBreach #DataLeak #JSONDatabase #EnergySector #ThreatIntelligence #CyberAlert #VECERT #Infosec #ConfirmedBreach
@StarkPrivacy Cellebrite da una lista de los tipos de extracción que puede ejecutar inclusive que modelos no puede acceder sin el password o patrón. “Ninguna herramienta hace todo”




![VECERTRadar's tweet photo. CYBER INTELLIGENCE ALERT: WAVE OF DDoS ATTACKS AGAINST ECUADORIAN STATE INFRASTRUCTURE 🇪🇨 ⚡
[STATUS: DENIAL OF SERVICE (DDoS) ATTACK]
A series of coordinated distributed denial-of-service (DDoS) attacks have been detected against multiple Ecuadorian government websites.
Threat Actor: Attributed to "Hider_Nex".
Scope: Multiple critical government entities have been impacted simultaneously.
Affected Entities and Availability Reports
The attack has caused disruptions to the web services of the following institutions:
Superintendency of Popular and Solidarity Economy (SEPS): https://t.co/mkrY05ooNA [Report: https://t.co/lGhGJzUuNR]
National Institute of Meteorology and Hydrology (INAMHI): https://t.co/02ZJtSlGoQ [Report: https://t.co/eWwb4tFBjk]
Superintendency of Companies, Securities and Insurance: https://t.co/qFroeLdzEp [Report: https://t.co/kAiGdyiCI0]
Council for Citizen Participation and Social Control (CPCCS): https://t.co/kpiStn72Od [Report: https://t.co/5BzyVWKqez
Ecuadorian Electricity Corporation (CELEC EP): https://t.co/qRA8v8XOsz [Report: https://t.co/nvTjzeaUR8]
National Electricity Corporation (CNEL EP): https://t.co/KR4wbz94ao [Report: https://t.co/v9KatBhzod]
Guayaquil Port Authority (APG): https://t.co/UBy5gM4dzY [Report: https://t.co/TyH65BCnlp]
Ecuadorian Transit Commission (CTE): https://t.co/y1pC5dB1cI [Report: https://t.co/AgTe7DFG6p
Security Considerations ⚠️
Operational Impact: These attacks primarily aim to disable citizen access to information portals and procedures, causing significant disruption to the continuity of digital public services.
Recommendations 🛡️
Mitigation of Malicious Traffic: Affected institutions are required to urgently activate DDoS protection protocols, including the use of Web Application Filtering (WAF) solutions to mitigate illegitimate traffic.
Monitoring and Resilience: Government IT teams are urged to strengthen the resilience of their internet-facing services and collaborate closely to identify the attack vector and prevent future intrusions.
#CyberSecurity #Ecuador #DDoS #GovernmentSecurity #ThreatIntelligence #CyberAlert #VECERT #UnderInvestigation](https://pbs.twimg.com/media/HKFVlckWUAAeSH3.jpg)