The Academy is hosting its first X Space next Saturday.
Topic: Getting Into Offensive Security: what it is, what it takes, and how to get started.
Straight from people who actually do the work.
📅 Saturday, 26th September 2026
🕙 7PM WAT | 6PM GMT | 1PM EST
Follow @ExFacademy and set a reminder. This is the conversation worth showing up for. 🔥💯
Most security tools answer one question:
“What vulnerabilities exist?”
ThreatMind answers a better one:
“Which security issues actually matter in my product?”
From threat modelling to secure code review, web, API, mobile, and cloud security testing…
Every great journey starts with a single step.
ExploitForge Academy is here🚀.
@ExFacademy
Built for aspiring cybersecurity professionals, career switchers, and curious minds ready to develop practical skills, think like attackers, and defend like professionals.
The journey starts now.
Join the waitlist: https://t.co/nomLXWuJQ6
LinkedIn: https://t.co/oUbBCXDIHf
#techskills #cybersecurity #exploitforgeacademy #cybersectraining
Happy to announce that the latest version of VulnBank is now live!
Last month, VulnBank turned one year old and crossed 600+ stars on GitHub. I had several ideas in mind for a major update, but my schedule didn’t permit me to work on them at the time.
Fast forward to this month, I was discussing the plan with @_aligorithm (a.k.a. “My Liege”) and mentioned how I hadn’t had the time to execute those ideas. He told me not to worry and said he would revamp the whole frontend while I focused on implementing the new functionalities.
We got to work on it, and now it’s finally ready.
New features in this release:
- Modern UI with Dark/Light Mode
- Admin Dashboard with stats and analytics (including some GraphQL API bugs 👀)
- Account Suspension and User Management
- User Bio Update functionality
- Virtual Card Funding supporting multiple currencies and crypto
(USD, NGN, GBP, JPY, QAR, BTC, ETH)
PS: If your country’s currency isn’t listed yet, drop a comment and I’ll add it in the next update.
I’m really curious to see who will be the first to uncover the new bugs in these features.
(https://t.co/AspazxJI26) Happy hacking!!!
Most organizations don’t realize they’re vulnerable, until the impact makes it obvious.
Test before you are tested. Attackers rarely “break in.” They authenticate, pivot, and escalate through weaknesses that were assumed to be controlled.
Most breaches aren’t zero-days. They’re preventable configuration gaps. In most of the reviews and assessments we conduct, the issues aren’t exotic or Hollywood-level exploits. They’re the basics; controls that were assumed to be in place, partially implemented, or enforced only on the frontend.
Things like JWTs accepted without strict validation, default or shared service credentials still in use, roles and tokens with more privilege than necessary aren’t “advanced attacker” problems, they’re discipline and configuration problems.
Be honest, which one has shown up in your environment before? Was it caught internally, or did your VAPT partner flag it?
You thought we forgot about this? We didn’t.
Is your team ready?
Are you ready to prove to the world that you’re the best among millions of professionals?
Brace up, just like we advised earlier and keep your eyes on all our social media platforms.
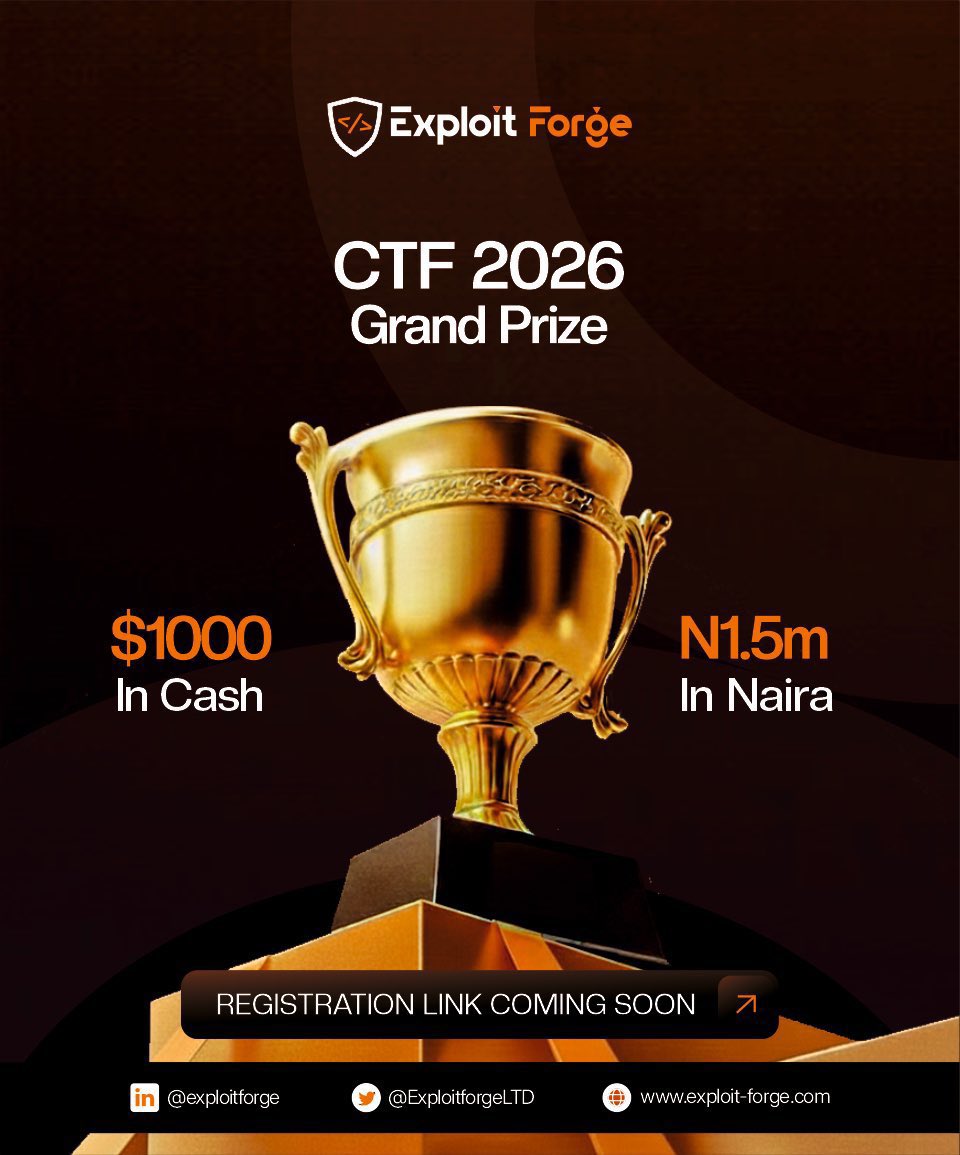
Exploit Forge CTF 2026 is coming.
We’re expanding our security service offering.
Exploit-Forge now provides compliance services alongside our core offensive security services, supporting local and international frameworks such as NDPA/NDPR, ISO 27001, NIST Cybersecurity Framework, CIS Controls, GDPR, PCI DSS, and others.
This isn’t checkbox compliance. Our compliance work is led by technical security professionals who understand systems, threats, and real-world risk not just policies.
The result is compliance grounded in strong security, practical implementation, and audit readiness for local and globally operating businesses, without slowing teams down. We’re committed to a vision where every business that trusts us stays secure not just in their software, but across their operations and processes, without compromise
Security first. Compliance follows.
Are you ready? Exploit Forge CTF 2026 isn’t built for individuals. Red and Blue teamers work side by side to hack, exploit, review logs and outthink the challenge as it evolves.
If your team can break systems, hold the line under pressure, and think smarter than the challenge itself, this is where you prove it. And yes, there’s a prize on the line for teams that rise to the top.
Check out the infographics for the details. Registration opens soon, don’t miss it.
@commando_skiipz shared this tweet earlier on and I’ll reiterate it
https://t.co/hA9BdgCeKc
Security is in every single thing you do, fine you added authentication and authorisation on certain endpoints
What about Business Logic Flow, is there a way to mess with the business logic to yield something
If I fuzz or inspect legit requests, can I see other users data, there’s a reason why Security Firms, Engineers and Penetration Testers are paid to do the job that they do, they see things that you’d likely not see
Yeah this endpoint receives username and password
What if it can receive much more than that
What if I can inflate my balance
What ifs are so plenty that we can never exhaust them, this is why these people are paid and the cost effect of having a Pentest as compared to an actual breach can’t even be emphasised enough, there’s a reason why there’s “Security Best Practices”, no matter who you are
QA, Frontend, PM, Backend,
You need security
Imagine Twitter wasn’t secure enough and for some weird reason I could see other peoples DMs
That would be disastrous
Two years ago, while I was still at MTN, a senior developer refused to approach my team for a security architecture review and requirements for what seemed to be an important project. The go-live date was already very close, and the team was still fixing bugs. I think the CIO got involved, and it became a big issue for the engineering team to deliver.
As it turned out, they fixed all those bugs the night before the go-live date. According to our change management policy, only the security team can grant approval for engineering teams to deploy a solution to production. And for the security team to give that approval, a penetration test must be carried out and come out clean.
Around 7 p.m., I got an email requesting security approval for an “urgent” project I wasn’t even aware of. I asked my teammates, and none of them knew about it either. Because of the urgency, I began testing, and I found several critical business logic flaws. I couldn’t help but laugh with joy because I always like to teach developers a lesson to never bypass security for anything.
By around 11:45 p.m or so., I sent a well-composed email listing all the issues I found. I highlighted them in red so that everyone copied in the mail could clearly see there would be no deployment that night.
About ten minutes later, my phone started ringing. It was the lead developer, speaking angrily:
“Hello Badmus! I just saw your email now, what do you mean? We did some validations from the backend, bla bla bla…”
I smiled and let him finish his rant before replying,
“Have you opened the 15-page report I attached to the email? Please go through it, all the screenshots and reproduction steps are there.”
A few minutes later, he called back with a much calmer tone:
“Please, can we jump on a call to go through these issues together? The CIO will kill me if he hears there’s something like this.”
Then I said, “You see why it’s very important to involve us early in your projects?”
In the race to build, launch, and scale, security often gets pushed aside for “more urgent” priorities but one breach is all it takes to undo years of innovation, customer trust, and investor confidence.
The cost of a breach goes beyond dollars, it disrupts operations, damages reputation, and slows growth.
Penetration testing isn’t just about uncovering vulnerabilities, it’s about protecting growth, preserving trust, and ensuring resilience.
If penetration testing feels expensive, consider this:
The average data breach costs over $4.4 million, while a comprehensive pentest averages $15K–$50K, less than 1% of that.
At Exploit Forge, we help organizations identify weaknesses before attackers do, enabling secure, confident growth.
Dear Founders, CTOs, Managers, and Developers,
I want you to read the quoted tweet and genuinely imagine this happening to your own product, the one you’re building or have already built.
The truth is, the founders of Bunni probably never took security seriously. And just like them, many of you still don’t, because “security doesn’t make money,” right? “We’re a small business,” “hackers won’t bother with us,” “we’ll deal with it later.”
That mindset is exactly how companies end up in situations like this.
Every time I get the opportunity to speak with people in your position, I emphasize one thing: invest in security early. Hire at least one competent security engineer. Budget for external penetration testing, not for compliance, but to protect your brand, your customers, & your reputation.
Security might not directly generate revenue,
but it prevents you from losing everything you’ve built.
Yes, security is expensive.
Yes, security is a choice.
But the cost of a breach is a hundred times greater, and when that day comes, you’ll realize it’s no longer a choice, it’s a debt you’ll have no option but to pay.
Please, take this as a wake-up call.
Reflect, & start taking security seriously, before someone else forces you to.
Help tag any founder, engineering manager, or developer to read this.
Ever received an email shouting “Act now or lose access!”? That’s not urgency, that’s manipulation.
Phishing thrives on panic because when you rush, you skip the checks. This Cybersecurity Awareness Month, slow down. Pause, verify, think before you click.
At Exploit Forge, we believe awareness turns every employee into a defender.
#Cybersecurity #Awareness
Exploit Forge Limited will be attending @moonshotbytc by @TechCabal 2025, a gathering that celebrates bold ideas shaping the future of technology and innovation across Africa.
As enterprise, new and existing startups continue to emerge and scale, we understand that innovation without security is a ticking time bomb. The same creativity that drives product growth often introduces unseen vulnerabilities that attackers can exploit. At Exploit Forge, we see it as our responsibility to help these startups stay ahead of the curve, not by fear, but by foresight.
Our offensive security team partners with founders, engineering teams, and investors to identify and remediate weaknesses before they evolve into breaches. We provide vulnerability assessments and penetration testing, red teaming, threat modeling, SSLC, vulnerability management services tailored to the unique realities of growing African startups.
The startup ecosystem is built on speed, innovation, and trust. Our goal is to ensure that trust remains intact as startups scale, by enabling them to build securely from day one. At @moonshotbytc by @TechCabal, we look forward to connecting with visionary founders, accelerators, and investors who believe that security is not a cost; it’s a growth enabler.
Exploit Forge exists to make resilience a competitive advantage because when startups secure their systems, they secure their future.