I found a silly bug in @WhatsApp that let attackers spoof a normal-looking link preview while controlling the URI opened - allowing arbitrary app deeplinks, with attacker-controlled parameters, launched without confirmation.
Fixed by @Meta.
Write-up : https://t.co/LboVeUmuy3
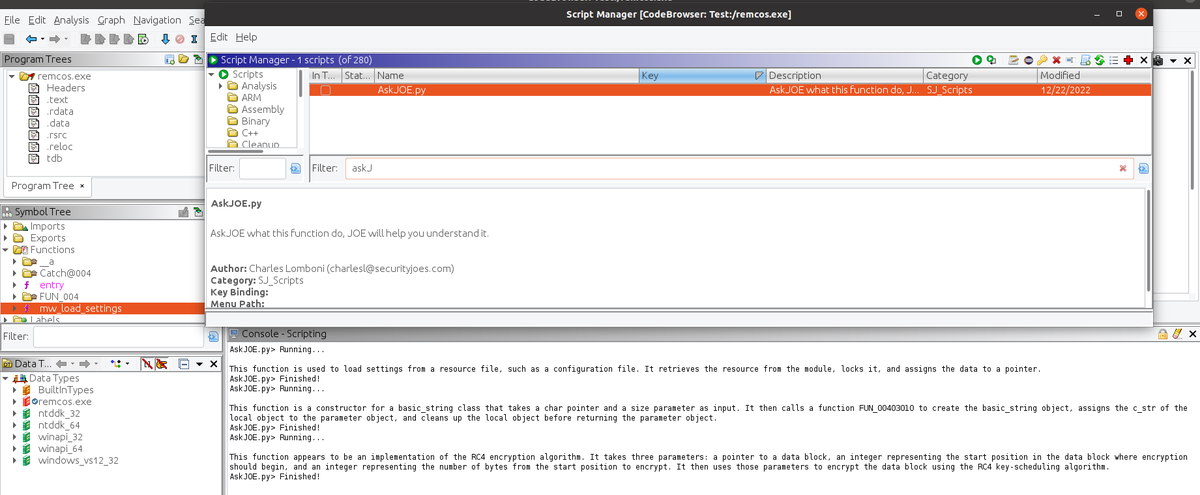
During our latest incident response, @charleslomboni implemented #ChatGPT into #Ghidra.
We've released the code so you could use it too:
https://t.co/p8x48JFhjW
Charles called it AskJoe 🤠
Enjoy & share
How We Fuzzed Microsoft Defender for IoT and Found Multiple Vulnerabilities : https://t.co/70vIdaDNT1 credits @kasifdekel@SentinelOne
Pwning Microsoft Azure Defender for IoT - Multiple Flaws Allow RCE for All : https://t.co/lbUM1fDY6F
🔥New on #SentinelLabs! We’ve just disclosed 10.0 CVSS vulnerabilities on Microsoft’s Azure Defender for IoT allowing unfettered access to your Microsoft-protected organization. By @kasifdekel & @ronenshh.
https://t.co/e8TvQEhM5z
#azure#iot#xdr#vulnerabilities
In what seems like nearly perfect conjunction with the latest @binarly_io disclosure, today we publish the 6th installment of our UEFI blog post series where we dissect 6 new vulnerabilities in HP's firmware that allow privilege escalation to SMM.
https://t.co/q2SlBFdaqX
@liba2k
Sorry about that @FlowerCode_ & @tiraniddo, I reported a LPE vulnerability and they decided to remove it. Hoped they'd release a fixed version. I find DeviceTree useful too and you can find a signed version in the repo alongside with the vuln details: https://t.co/9w6SciFonw
Fuzzing is an effective offensive security tool that defense has widely adopted. Unfortunately, it’s altogether insufficient for defense.
“I wrote fuzzers and found the vulns!” No. You didn’t. You found some vulns. If you’re in offense, your job is done. In defense it’s not.
1/
🔥New on SentinelLabs! 25 CVEs and counting: Vulnerabilities in #AWS & other major #cloud services. @kasifdekel's latest research reveals millions of cloud users are exposed to privilege escalations from bugs in shared driver software.
https://t.co/eeMGFeadSw
#cybersecurity