I found a vulnerability in #Azure allowing me to access Azure accounts of companies worth billions
We all know vulnerabilities exist. This isn't an injection, XSS, or RCE.
But the crazy thing about it?
It took 2 hours to discover. 🤯
Here's the story of #AutoWarp👇 (1/10)
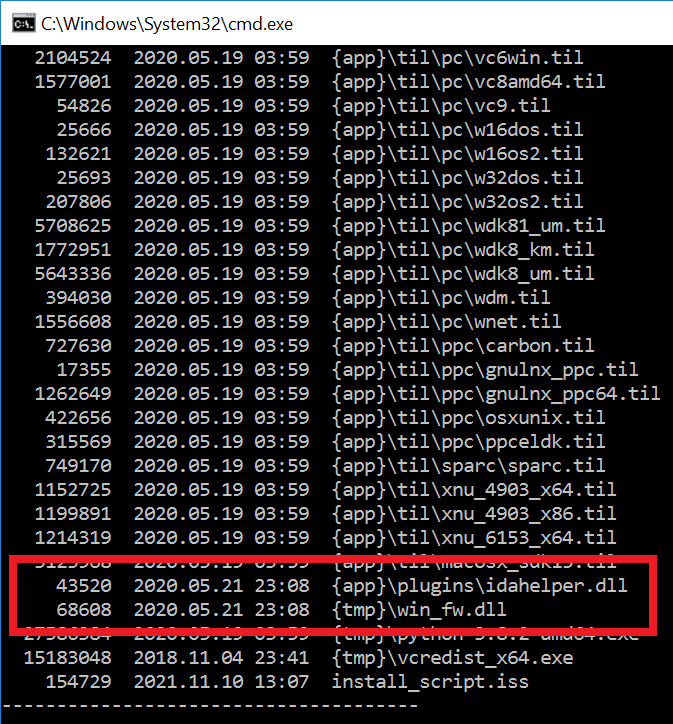
#ESETresearch discovered a trojanized IDA Pro installer, distributed by the #Lazarus APT group. Attackers bundled the original IDA Pro 7.5 software developed by @HexRaysSA with two malicious components. @cherepanov74 1/5
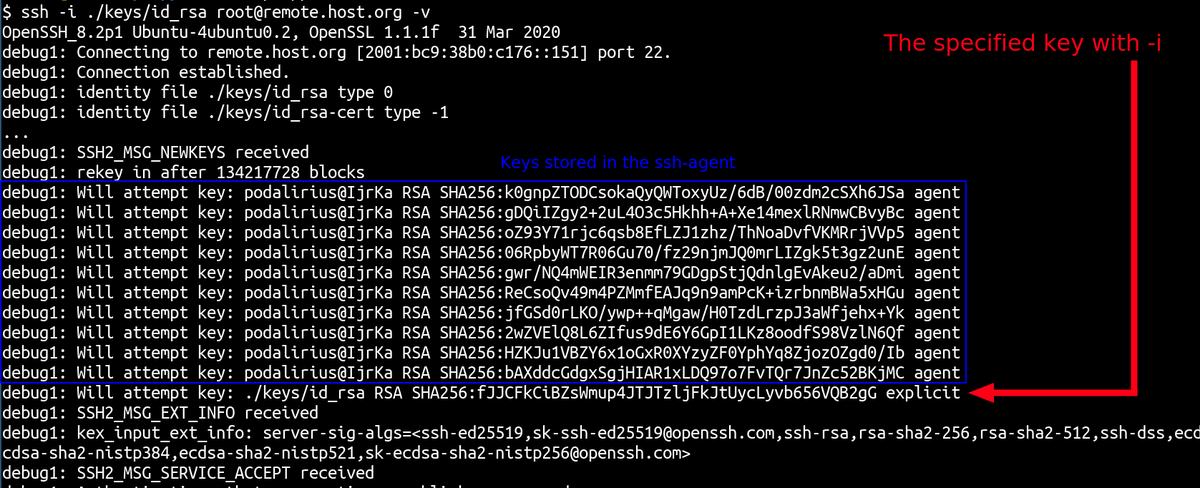
[thread] Did you know that ssh tries to authenticate with stored keys BEFORE the key specified with -i in the command line ? I just noticed this, the hard way 😐.
Let's imagine you have more than 5 keys loaded in your ssh agent. When authenticating to a remote server, you get:
[thread] Tired of using complex payloads to get access to the os module in Server Side Template Injections on jinja2 ? I have new awesome payloads for you 😎
{{ self._TemplateReference__context.cycler.__init__.__globals__.os }}
More information ➡️ https://t.co/U9uTPdo98U
@squintar Si je comprends bien, soit on accepte, soit on souhaite refuser (et la décision revient quand même à Twitter). Enfin c'est tellement pas clair que j'ai du mal à avoir confiance.
Le groupe Babuk s’est fait remarquer ce début d'année, par le succès rapide de cyberattaques ciblées via son rançongiciel contre de grandes entreprises. L'analyse de nos experts dans les #CyberSeChronicles : https://t.co/gjf73Ozkor
Here's a threat on some overpowered technologies to slow down attackers that you can implement _now_.
First, re-implement LAPS (https://t.co/GvdXwpy52L) at your peril.
1/14
CVE-2020-16898 (Windows TCP/IP RCE) is beaten by CVE-2020-16952 (SharePoint post auth file inclusion leading to RCE). CVE-2020-16952 has an exploit out and when combined with password spraying/phishing for creds s a threat right now - https://t.co/IZbbn8aB4o