@dieworkwear Idk if you ever been to Tucson, but that place is a ghetto shit dump lmao
Worse than downtown Phoenix by far.
No way I'm paying 850k to live there.
@iykyk719@TipOfTheBanana When I was in college I used to stop at a hotel every morning for my 7am databases class and load up a giant plate of sausage, eggs, and bacon and feast during class.
Shitty food, the sausage patties are my favorite, but can't beat free 😆
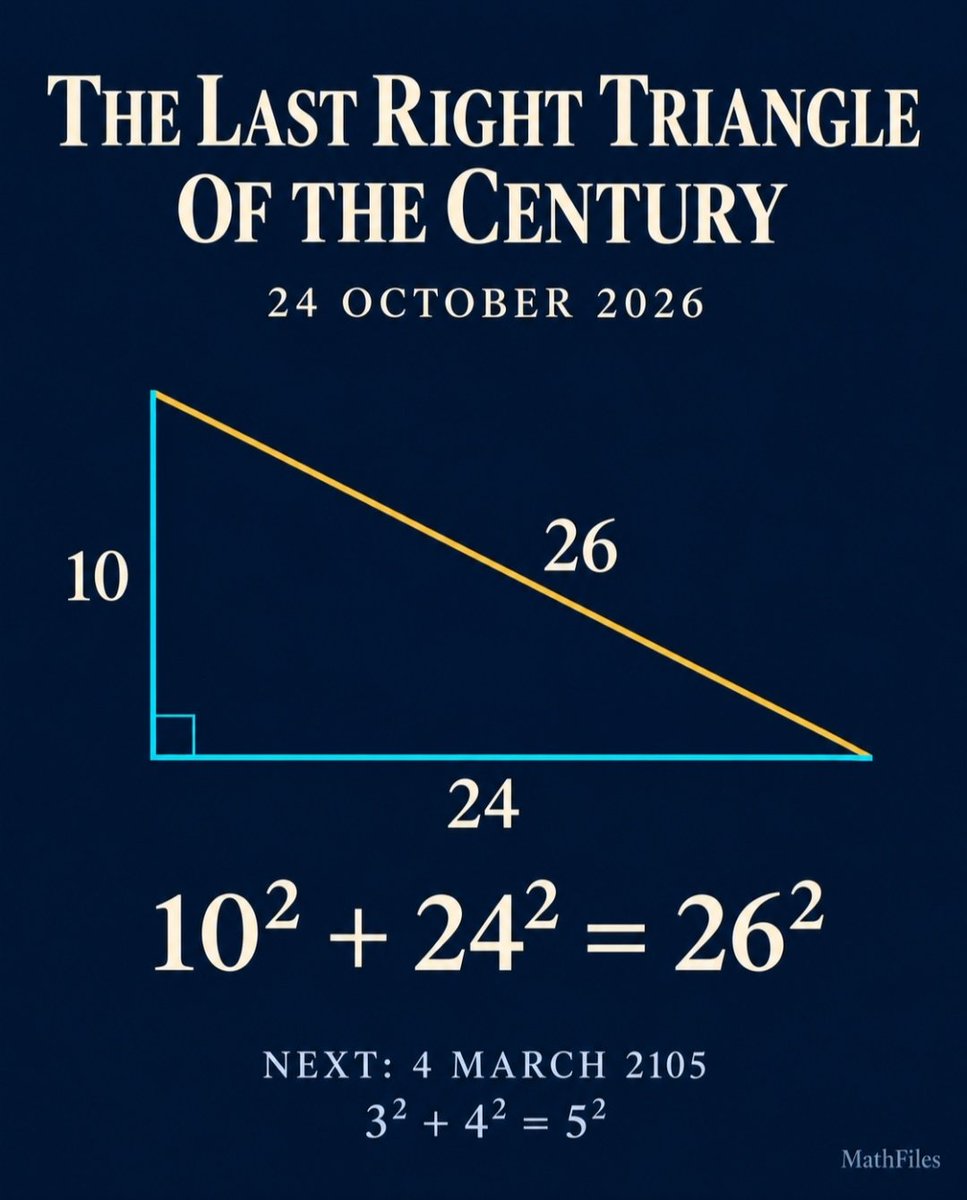
Today, the calendar makes a right triangle, for the last time this century.
This Saturday is October 24, 2026.
Write it as 10/24/26 or 24/10/26, and the same beautiful relationship appears:
10² + 24² = 26²
100 + 576 = 676
But here’s what makes today special.
There are infinitely many Pythagorean triples. Only a handful fit our calendar.
Using the rule
month² + day² = (last two digits of the year)²,
the month cannot exceed 12, and the day cannot exceed 31. Those small limits leave exactly 12 qualifying dates in this century.
Today is the last.
The next will be March 4, 2105:
3² + 4² = 5²
That is a wait of more than 78 years.
An infinite family of triangles. Just twelve appearances on a century’s calendar.
Happy Pythagorean Triple Day.
@pnadolny@drjoshcsimmons This is not harsh. All of big tech does this at minimum yearly. They take the bottom 5-10% of performers and fire them. The banking industry moves at the pace of a snail. They should all be fired.
@roguebogey Absolutely, c-level should be held to a higher standard. They have the most access to critical company information.
If you're not rolling u2f then.. you should be fired too.
What kind of circus are you running? Zero accountability whatever it is.
@roguebogey They shouldn't be shamed. They should just be fired. If employees "don't care" about security, then they don't really care about their job.
They can go somewhere else that they care about more.
Effective Immediately, all organizations using PHP for their systems are advised to be prepared for an update addressing two critical vulnerabilities. PHP is widely used for web applications. These vulnerabilities often provide a direct path to the server's file system or database. If an immediate update is not feasible, it is recommend that organizations take the system offline until it can be fully mitigated. NSA will follow up shortly with more specific guidance.
@NomN0m@StabilityTheory@sagitz_@uwu_underground That's kinda irrelevant. The exploit was leaked by a third party outside of php. There's nothing they could have done other than warn people.
Would you rather them just not say anything at all? Lmao