@__Hesser__@Dr_Biohacker Cholesterol on its own isn't a problem (as long as it stays within non-pathological limits), the issue is its combination with an inflammatory state, which creates sclerotic plaques
ELON: IF WE DON’T MAINTAIN THE CULTURAL IDENTITIES OF THE VARIOUS COUNTRIES, THEY WILL DISAPPEAR
“I think there is value to a culture, we don't want Japan to disappear, we don't want Italy as a culture to disappear, we don't want France as a culture to disappear.
I think we have to maintain the reasonable cultural identity of the various countries, or they simply will not be those countries.
Italy is the people of Italy.
The buildings are there, but really, what is Italy?
Italy is the people of Italy.”
Rome, December 16, 2023
🚨🚨🚨 @RDNTCapital has been hacked 🚨🚨🚨
All Binance Web3 wallet users, please make sure to revoke any token approvals tied to the following contract addresses ASAP:
Ethereum: 0xA950974f64aA33f27F6C5e017eEE93BF7588ED07 Arbitrum: 0xF4B1486DD74D07706052A33d31d7c0AAFD0659E1 BNB Smart Chain: 0xd50Cf00b6e600Dd036Ba8eF475677d816d6c4281 Base: 0x30798cFe2CCa822321ceed7e6085e633aAbC492F
👉👉👉 https://t.co/u8dHEygTLX
Stay safe🙏
#PeckShieldAlert@decentraland's X has been compromised. The phishing site is launch-decentraland[.]org.
Do *NOT* click the link until further official announcements
Move to El Salvador 🇸🇻
Europe has obnoxiously criticized El Salvador in the past few years and yet today it really feels that the once cradle of freedom and democracy is slowly falling into dark ages again.
Identification Of Malicious Extension
Over the last week, we received reports that a small number of users using Solana DeFi got drained.
After extensive investigation, we have identified a malicious Chrome extension called “Bull Checker” that had targeted users on several Solana-related subreddits.
Users with this extension would interact with the dApps as per normal, have the simulation show up as normal, but have the possibility of their tokens being maliciously transferred to another wallet upon transaction completion.
If you have this extension (or similar extensions with extensive permissions you cannot trust), please remove it immediately.
Note that there is no vulnerability found in any of the dapps or wallets.
A report with all the key technical details, including why the simulation looked normal, is available at:
https://t.co/u5mfmRbJMz
For the report, we collaborated with @0xslipper from @Offside_Labs who was extremely helpful for much of the technical analysis.
Much thanks to @blowfishxyz, @RaydiumProtocol and @phantom who also reviewed this post too.
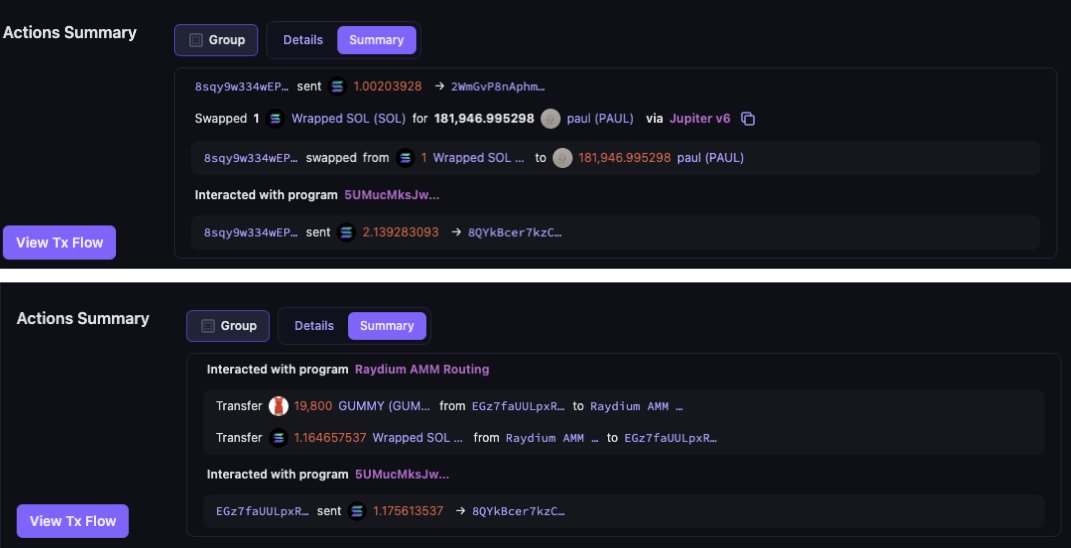
Example Transactions
Here are 2 examples of transactions that have interacted with the malicious program
5UMucMksJweA1AtgyxrK8DJeBXr3DQGEGRs5Kkq2pZjr
https://t.co/gGodMZNuvK
https://t.co/hvziyniTuQ
In both cases, malicious instructions were added to regular Jupiter and Raydium instructions, and the resulting transaction was signed by the user as per normal, but had their tokens and authority transferred to the malicious address.
The Suspected Extension: Bull Checker
Upon further investigation of several affected users who have been drained by the same program, we have identified an extension called “Bull Checker”, which has the permissions to read and change all the data on the website, as a potential cause.
Raydium has confirmed that their affected user has the same extension installed.
Bull Checker is supposed to be a read-only extension that allows you to view the holders of memecoins. There should be no need for an extension like this to read or write data on all websites.
This should have been a major red flag for users, but apparently several users continued to install and use the extension.
After installing Bull Checker, it will wait till a user interacts with a regular dApp on the official domain, before modifying the transaction sent to the wallet to sign. After modification, the simulation result will still be “normal” and not appear to be a drainer.
Technical Analysis
For a full technical analysis, including why the simulation check looked normal, how the drainer tx worked, and what the extension code did, please refer to the jupresearch post here:
https://t.co/u5mfmRbJMz
Targeting Memecoin Traders
In addition to the above information, while researching “Bull Checker” we discovered that it was publicised by an anonymous Reddit account, “Solana_OG”. This person appeared to target users looking to trade memecoins, and lured them to download the extension.
Links:
https://t.co/WuhFWj5gdH
https://t.co/j5Du0YRi4L
Key Safety Habits
While we have identified one malicious extension, there might still be other malicious extensions out there.
1. If you suspect an extension contains malware, particularly if they have both “read” and “change” permissions, uninstall it immediately.
2. Do not trust something just because someone mentioned it on Reddit or other media and it has many upvotes. Astroturfing and social engineering for the purpose of scamming are very real.
3. Extensions that request for extensive permissions are highly suspicious. An extension like Bull Checker should not need to read and modify all your website data. You should have an extremely high degree of confidence in an extension before you start using it.
4. In addition, Blowfish has released a new guard instruction feature called SafeGuard that prevents all simulation spoofing attacks. It’s currently being adopted by multiple Solana wallets and will likely be useful in prevent such future attacks.
Conclusion
Stay safe out there, and don’t install extensions that can read/write data unless you are really sure.
Many thanks to Siji from Offside Labs, Blowfish, Raydium and Phantom for assisting in this investigation.
The decision to close the 𝕏 office in Brazil was difficult, but, if we had agreed to @alexandre’s (illegal) secret censorship and private information handover demands, there was no way we could explain our actions without being ashamed.
The European Commission offered 𝕏 an illegal secret deal: if we quietly censored speech without telling anyone, they would not fine us.
The other platforms accepted that deal.
𝕏 did not.
Hey frens,
Some iOS users received a scam notification. We're investigating it.
Sorry for the inconvenience. We'll update you ASAP.
Thanks for your understanding.
🍏🍏🍏 Update your iOS devices as soon as possible!
A recent iOS update addresses at least two vulnerabilities exploited as 0-day.
CVE-2024-23225 and -23296 are kernel and RTKit vulnerabilities that enabled attackers to bypass kernel memory protections, which appears to be a direct path to privilege escalation.
Apple has neither disclosed the attackers who used these vulnerabilities nor credited third-party researchers for the discovery, which may suggest an ongoing investigation. In the meantime, we strongly recommend all iOS users to update ASAP.
Furthermore, another vulnerability, CVE-2024-23243, allowed a malicious app to access sensitive location data.
To safeguard yourself, update to the latest iOS/iPadOS version, 17.4 https://t.co/J39SwptZpo
Scammers everywhere: 4 new wallet drainers and Twitter access scams you should be aware of ↓
#1: Download and test our app
I first came across this scam a few months ago.
Scam flow:
• Someone on Twitter contacts you, promising a guaranteed four-digit airdrop, a high-paying job, or an invitation to become an advisor/ambassador.
• You express your interest, and the conversation moves to Telegram.
• You are assigned an onboarding manager whose mission is to explain the product, or you're invited to test the app immediately. Each action you take will lead to a reward.
• They share a link with you, and you proceed to download and install the app.
• Whoosh! Your device is compromised, and your wallet is drained.
#2: Schedule a call with us
Flow:
• You receive a direct message on Twitter from someone expressing interest in interviewing you (pretending to be a member of a reputable media i.e. Forbes) or sharing a lucrative job offer.
• They provide a link for scheduling a call, which appears similar to Calendly or Google Meet.
• Upon clicking the link, you are prompted to authorize access with your Twitter account to book the call.
• Voila! Scammers gain access to your Twitter account.
#3: Extended threads
Flow:
• You closely follow one of the protocols and come across a thread.
• As you go through the thread, you notice a CTA posted by an account that mimics the continuation of the original thread.
• The CTA might say something like "Check your airdrop eligibility" or "Learn more".
• Curious, you click the link and are redirected to a phishing site.
• Unbeknownst to you, you connect your wallet, only to find out later that it has been drained.
#4: Verification badges
Flow:
• You follow certain protocols on Twitter.
• As you scroll through your timeline, you encounter a sponsored tweet from one of these brands (imposter), distinguished by a golden or grey verification badge.
• Curiosity gets the best of you and you click on the link, only to find your wallet drained once again.
Tips for staying safe:
1. Use a browser without wallet extensions (e.g., Safari) when browsing your timeline or visiting new sites.
2. Before accessing any official website, verify the link by visiting the account's official Twitter page.
3. Connect to new sites with an empty or low balance wallet.
4. When running a project, number your tweets in threads (e.g., 1/15).
5. Avoid clicking on links received in DMs, especially if they are accompanied by business or job offers.
6. Be paranoid, it helps.
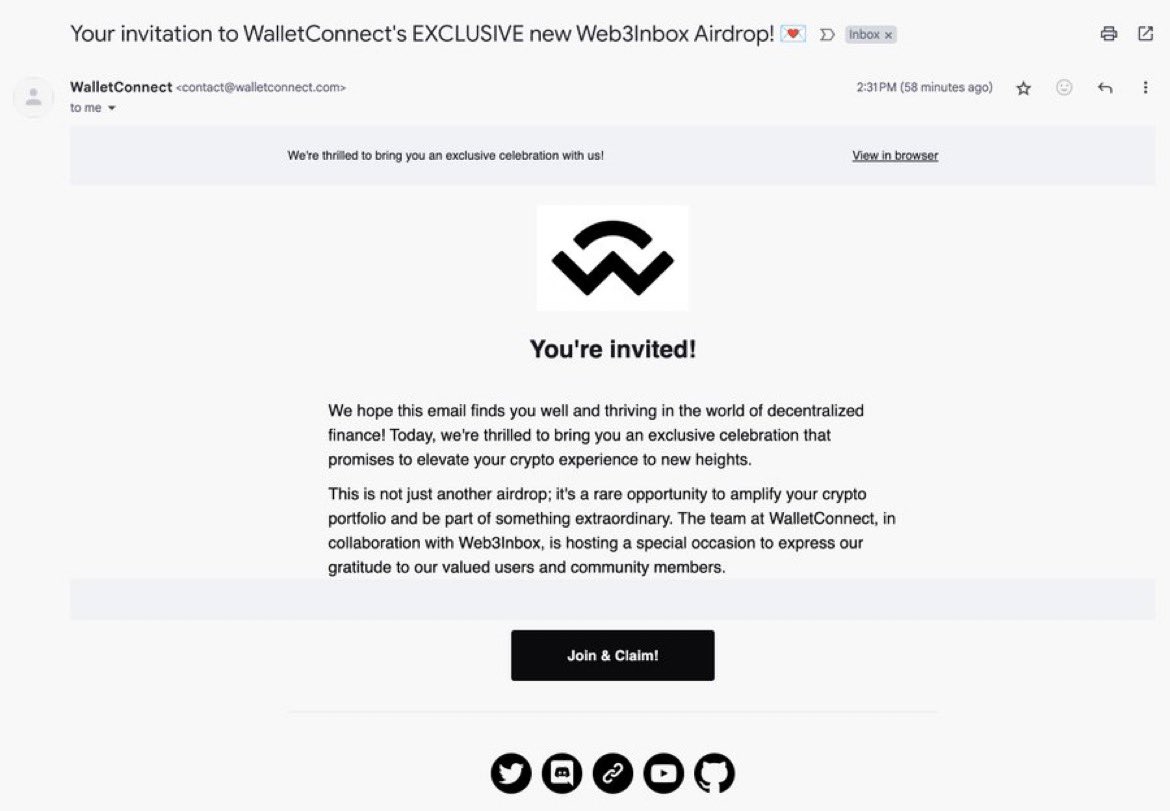
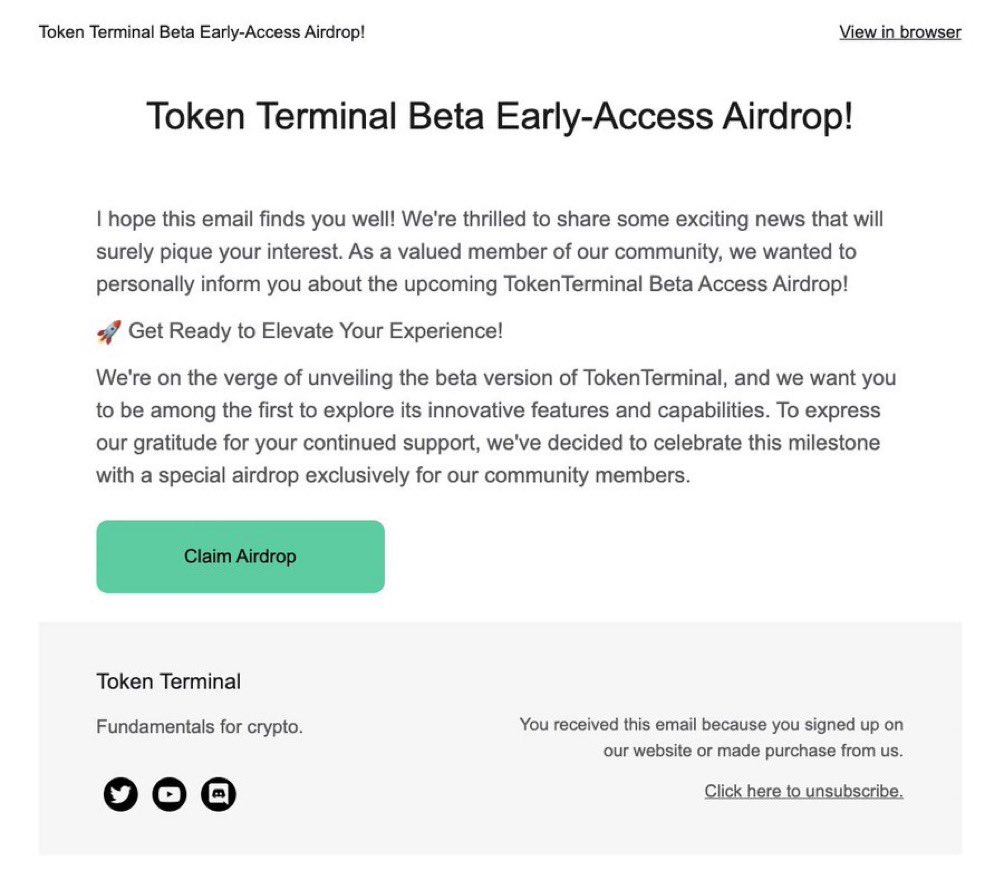
Community Alert: Phishing emails are currently being sent out that appear to be from CoinTelegraph, Wallet Connect, Token Terminal and DeFi team emails.
~$580K has been stolen so far
0xe7D13137923142A0424771E1778865b88752B3c7
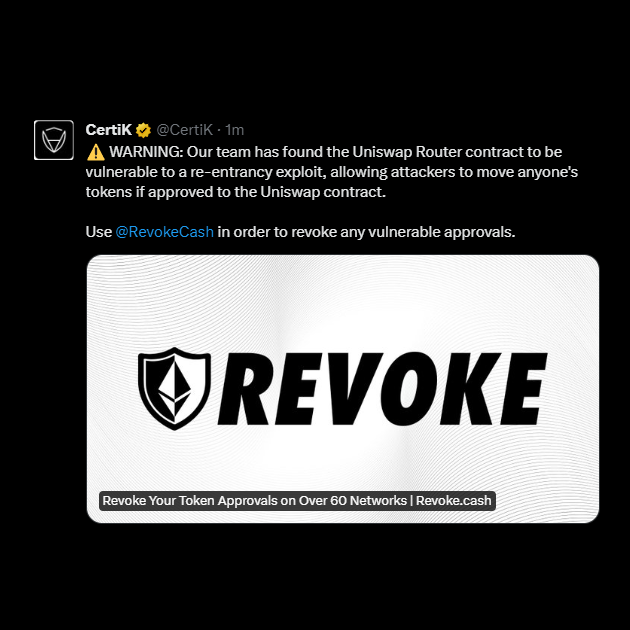
🚨 CERTIK X PAGE COMPROMISED
The official page for CertiK has been compromised & is posting fake masked Revoke Cash links to a wallet drainer.
DO NOT INTERACT - SHARE & STAY SAFE!
Quick PSA for newcomers to ze cryptoverse on here... I've noticed the scams using Twitter ads are getting way more aggressive/sophisticated lately...
Twitter's current ad format is very 'native' ie the ads or boosted tweets look 99% similar to actual organic normal tweets...
A lot of the scammers are now using paid/boosted tweets replicating airdrop threads and similar stuff, and also using purchased/recycled accounts that might have notable followers and therefore look legitimate...
So yeah be insanely hypervigilant when it comes to links/airdrop-related stuff/etc on here...
🚨 CHROME ZERO-DAY: CVE-2023-7024
Update your Chrome browsers (Brave, Opera, Edge, etc.) now! Google has released emergency updates to address this zero-day vulnerability.
Share & stay safe! 🫡
🚨 @THIRDWEB DISCLOSURE
Due to the lack of information we advise you revoke all unneeded approvals ASAP.
Visit https://t.co/lkFyXAJZW5 to revoke your approvals now.
To see if your contract is at risk use the tool provided here https://t.co/8432KpA8fF.
Share & stay safe. 🫡