Want to learn firmware reverse engineering on an IoT device? I'll be giving a free, women-only workshop with BlackHoodie at Hexacon in Paris on October 15. #reverseengineering
https://t.co/fgp2qRX5hH
Reverse engineering Google's undocumented DSP pays off! Our co-workers @st424204 & @Peterpan980927 found the first public vuln in Pixel 8's DSP → kernel takeover
MTE? What MTE? 😎
Their talk got accepted at @HacksInTaiwan
https://t.co/kAOAug43ya
4,000 hours of reverse engineering the Microsoft Xbox: literally every trick, from soldering to acid etching to X-raying chips. 👨🏻🏭🎮🪚♨️
More details on:
LinkedIn: https://t.co/PztIWJXj6V
Substack: https://t.co/oRyqc6aNGY
The master branch of MaskRomTool now delivers a mask of bit damage to the disassembler, so that in decoding a damaged file you can see which instructions make use of damaged bits and should not be trusted.
It should also help figure out when the undamaged words are meaningless.
🚀 Open source is awesome! Just one day after open-sourcing the LiteX WR NIC for SPEC-A7, we’ve got a PR from Mimil25 adding the missing piece for the LiteX Acorn Baseboard Mini: White Rabbit support without the specific VCXOs! 🎉 This will also unlock WR support on the LiteX M2SDR! 😍
PR: https://t.co/hNclwR1RHD
Can't wait to test it!
😍
In my field of fun hacking reversing unknown protocols I always find some checksum or CRC or hash that needs to be identified.
The CRC catalogue is priceless for those moments.
https://t.co/QyBA93vYMr
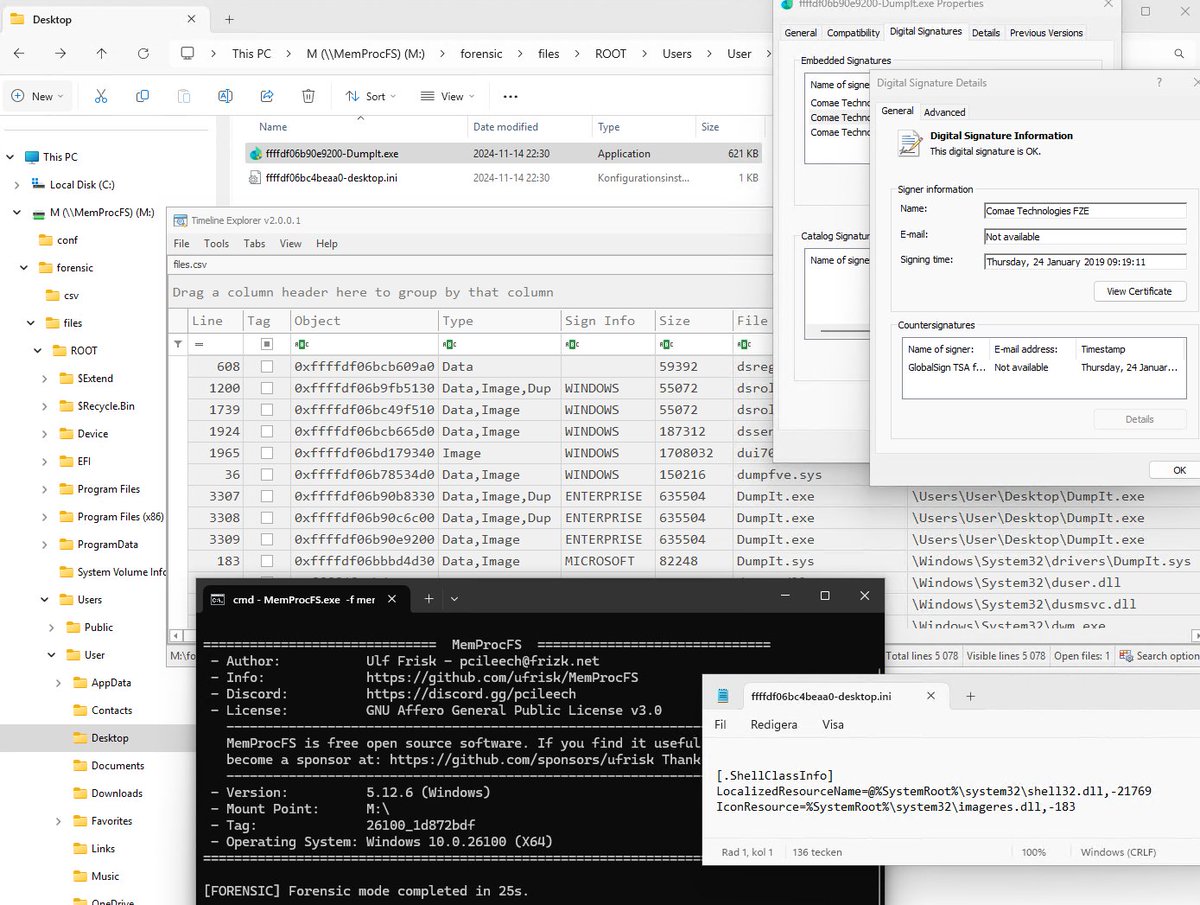
MemProcFS now supports console text recovery!
Recover text from Cmd and Powershell to Find Evil with MemProcFS super fast memory forensics!
https://t.co/inOM3l1GIF