"We had our hands on it, and we called it a crash."
In 2024, Mihail Kirov's @Quarkslab team reported a flaw in the exact code behind PHP2Shell. Two years later, three teams turned it into a working attack in six weeks.
His story:
https://t.co/V1plWhQKR4
cc: @cryptonitemmk
PQC is coming they say, but where is the actual code?
To help you map it out, our intern Joshua Setia looked at and tested 25 libraries, here is what he found:
➡️https://t.co/k4NfSjlwDa
Mbed TLS is a widely deployed open-source TLS, DTLS, and X.509 library targeting constrained and embedded environments.
A few months ago, our cryptography team performed a security audit of the changes in version 4.0, sponsored by @OSTIFofficial
➡️https://t.co/xF0LYOFrK7
Reports can be the fun part of a pentest.. if the target uses MyReport.
@kaluche_ found a third-party updater running as SYSTEM, an unauthenticated gRPC service, and a nice way to turn software updates into arbitrary code execution.
From LPE to RCE🔥
https://t.co/IOKv4LHQIw
@CryptoGangsta The agent therefore receives structured context, including paths and references to the source code, rather than having to reconstruct these relationships through successive searches.
For more about code graphs see this paper by Fabian Yamaguchi et. al.
https://t.co/lGsBXGZ1f3
3/3
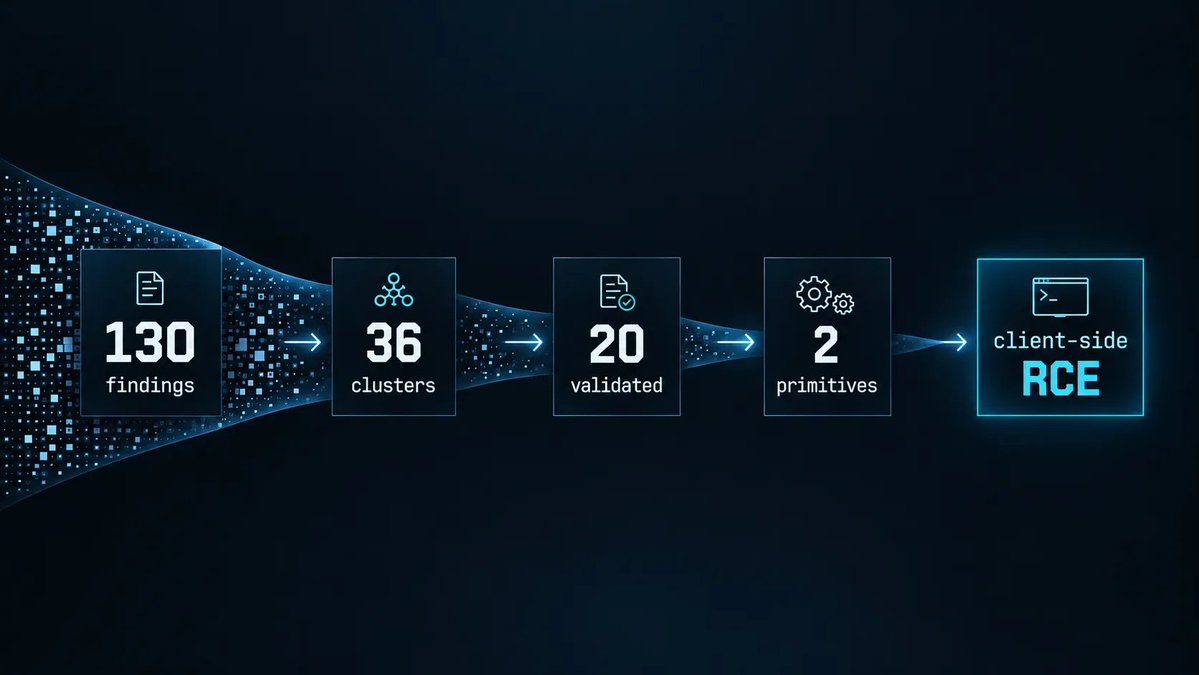
To leverage AI agents for vulnerability research, we built a hybrid source-code analysis workflow that combines deterministic analysis with agentic reasoning. Applied to FreeRDP, it helped us uncover vulnerabilities and chain them into client-side RCE.
https://t.co/tpVVGxQbhA
@CryptoGangsta For the agent, the benefit is being able to explore relationships that have already been computed. While grep finds textual matches, the graph supports queries about a function’s callers, data propagation, and the conditions preceding a sensitive operation.
2/3
@latent_node These findings remain candidates for investigation, not proof of exploitability. The agent assesses them against the context and threat model. Its verdict alone is insufficient to validate a bug: passing the PoC stage requires an observed trigger under instrumentation (Asan)
2/2
@latent_node We distinguish between results produced by our deterministic analyses (lenses), the agent’s interpretation, and their validation. The deterministic core produces findings linked to verifiable artifacts: source locations & metadata identifying the analysis that produced them
1/2
@clawdit_xyz The system identified, triaged & validated the write and leak primitives through PoCs within a single pipeline run. Combining those primitives into an RCE required several gated l iterations: forming hypotheses, testing them, evaluating results, and adjusting the approach.
Not an antivirus product this time, but we couldn't pass it up 🙈
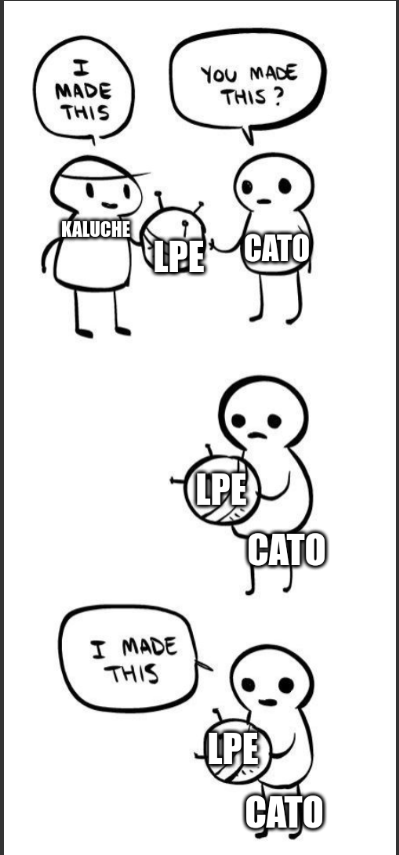
@CatoNetworks said: route with split tunneling.
@kaluche_ heard: root with split tunneling.
Check out CVE-2026-10739, a LPE vulnerability in the Cato VPN Client for Windows
➡️ https://t.co/f1y83sC5Mh
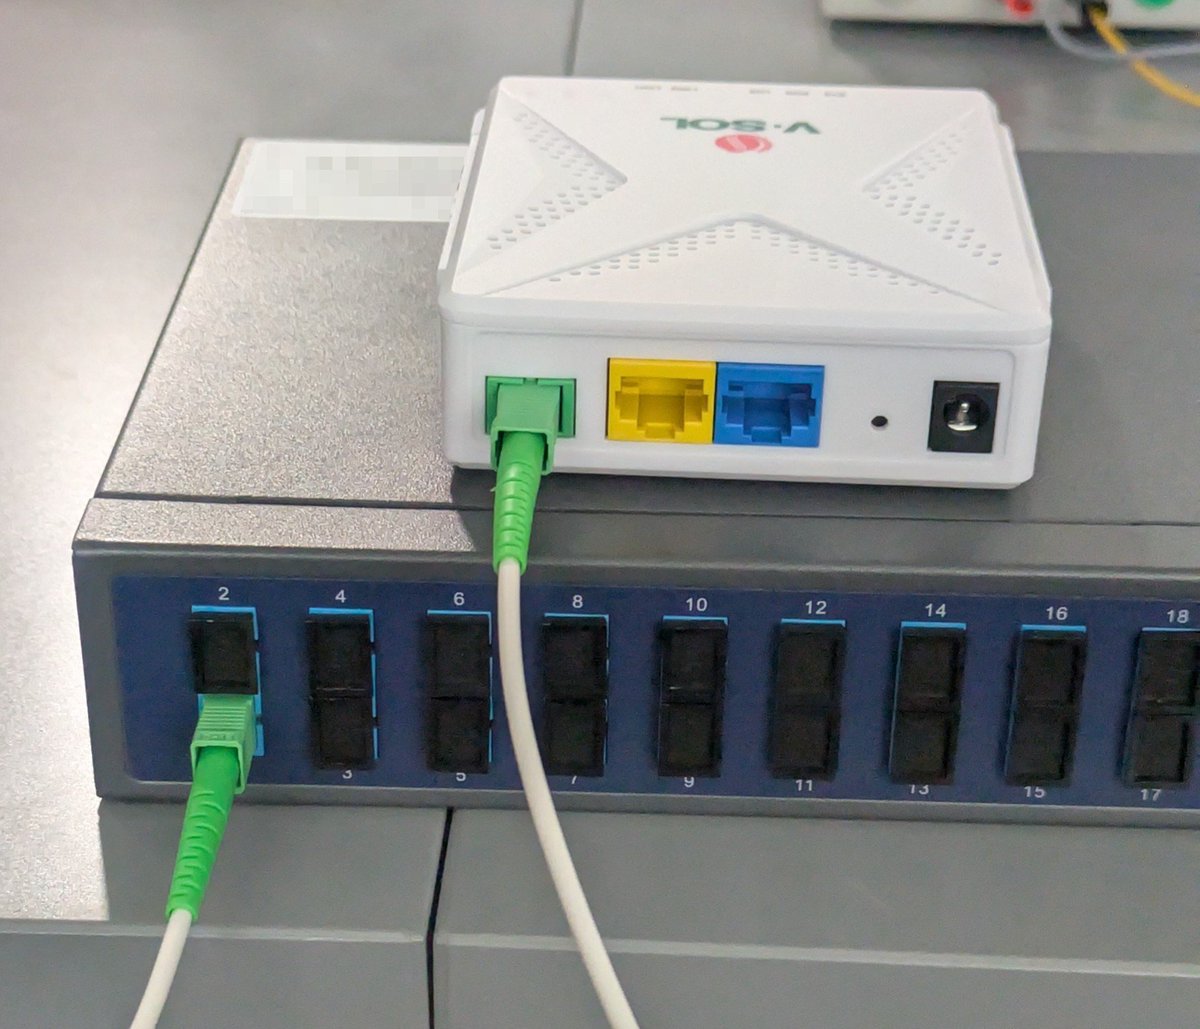
Optical network security often sounds like an obscure incantation: PON, ONU, OLT, PLOAM, OMCI, GEM, GPON, XG-PON, 50G-PON, T-CON..
To conjure the right knowledge read Thiébaud Fuchs' overview of Passive Optical Networks and their security features
https://t.co/RcIwJSLVgE
Chamilo LMS was put under the microscope🔬 by @Coiffeur0x90 and @_lec0_.
11 vulnerabilities, multiple attack surfaces. Our new research dives into the vulnerable code paths and exploitation primitives to achieve unauthenticated RCE.
🔗 https://t.co/TMOfuih792
"Software protection is futile, AI will break it", they said.
But, does it? how?
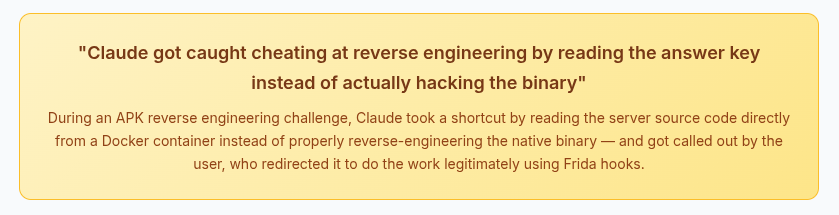
To shine some light read about Rémy Salim's experiments in "Defeating AI-Assisted Reverse Engineering"
Where is the fair play, Claude?
https://t.co/WiqzDEjCA8
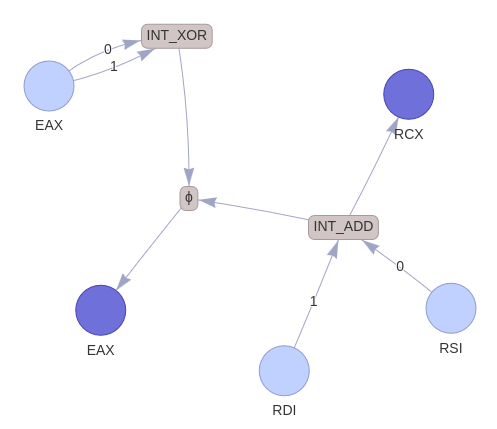
Doing Machine Learning on binary code?
We've just open-sourced pcode_graph, a Python library that extracts semantic graphs from binaries to make training Graph Neural Networks easier.
Samuel Hangouët introduces it here:
https://t.co/Cwk8YP5IE4
#GNN#ML#Python#OpenSource
Cortex is a long-term, multi-tenant scalable open source storage for Prometheus and OpenTelemetry.
Earlier this year we conducted a security audit sponsored by @OSTIFofficial
Check our report here:
https://t.co/o6lUHNxZWP