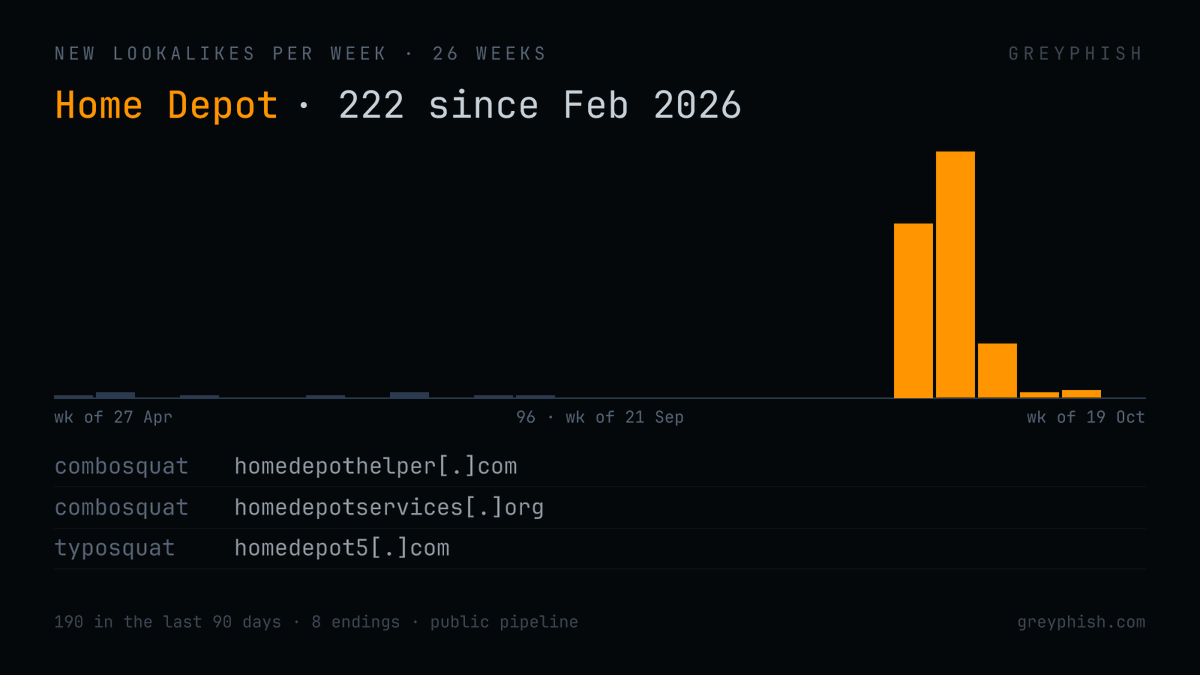
We have recorded 222 domains resembling Home Depot since February 2026, and 190 in the last 90 days alone. Most (84%) are typosquats: a keystroke or two from the real name.
Among the latest: homedepothelper[.]com
@HomeDepot#brandprotection
One compromised login credential sat undetected for four months on a vendor SFTP site -- long enough to copy student records (names, DOBs, addresses, school IDs) on potentially millions of California students. Per CDE, SecurityWeek.
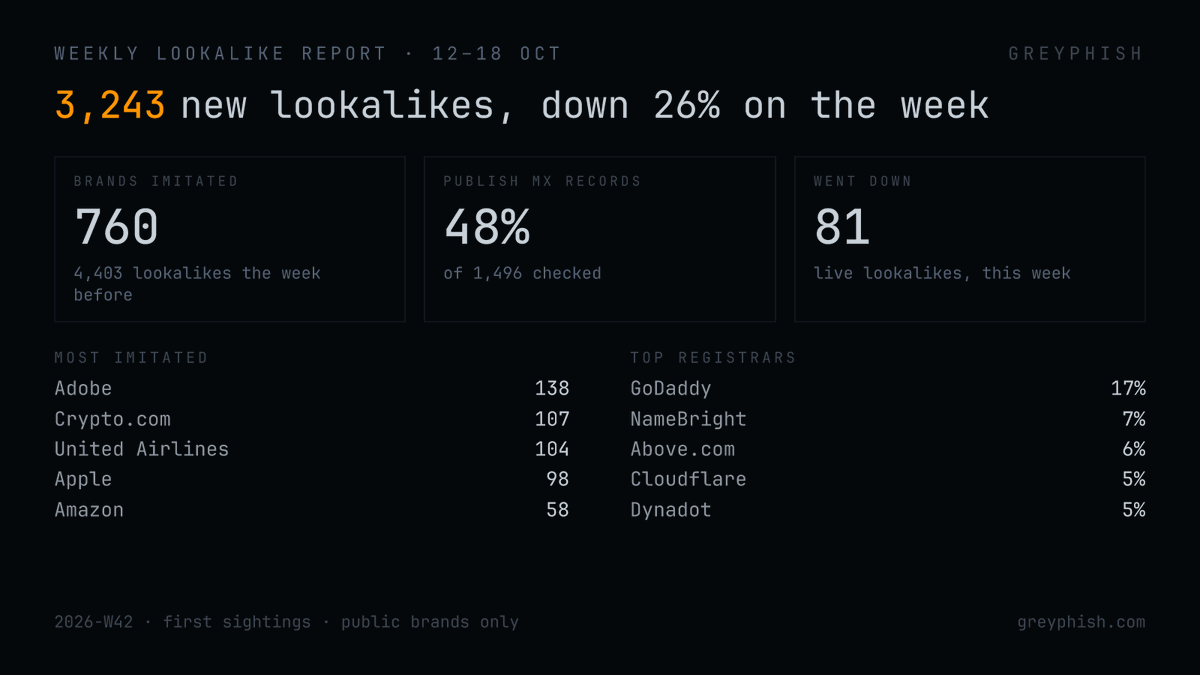
Last week (12–18 Oct): 3,243 new lookalike domains, down 26% on the week before.
Most imitated of 760 brands: Adobe 138, Crypto[.]com 107, United Airlines 104
48% of the 1,496 we checked publish MX records
81 live lookalikes went down
The full report is on our site.
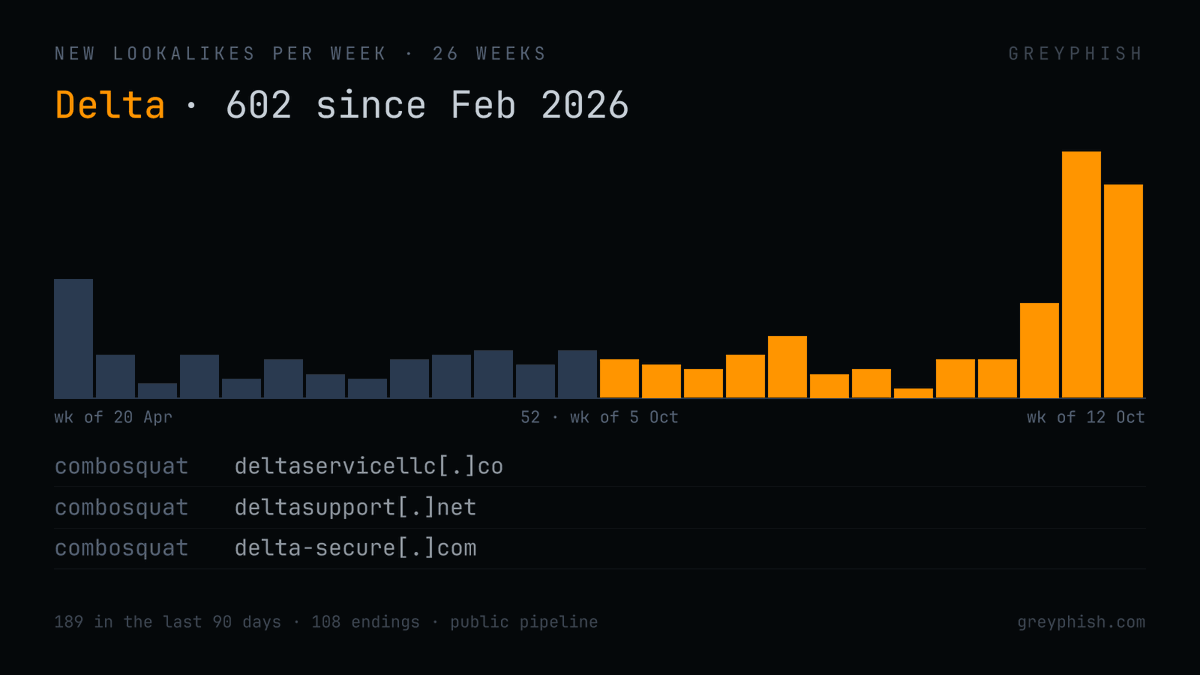
Delta lookalikes, by the numbers:
602 since February 2026
189 in the last 90 days
108 different endings
Most (82%) are combosquats: the name spelled right with a word added, most often "web" or "service".
A recent one: deltaservicellc[.]co
@Delta#threatintel
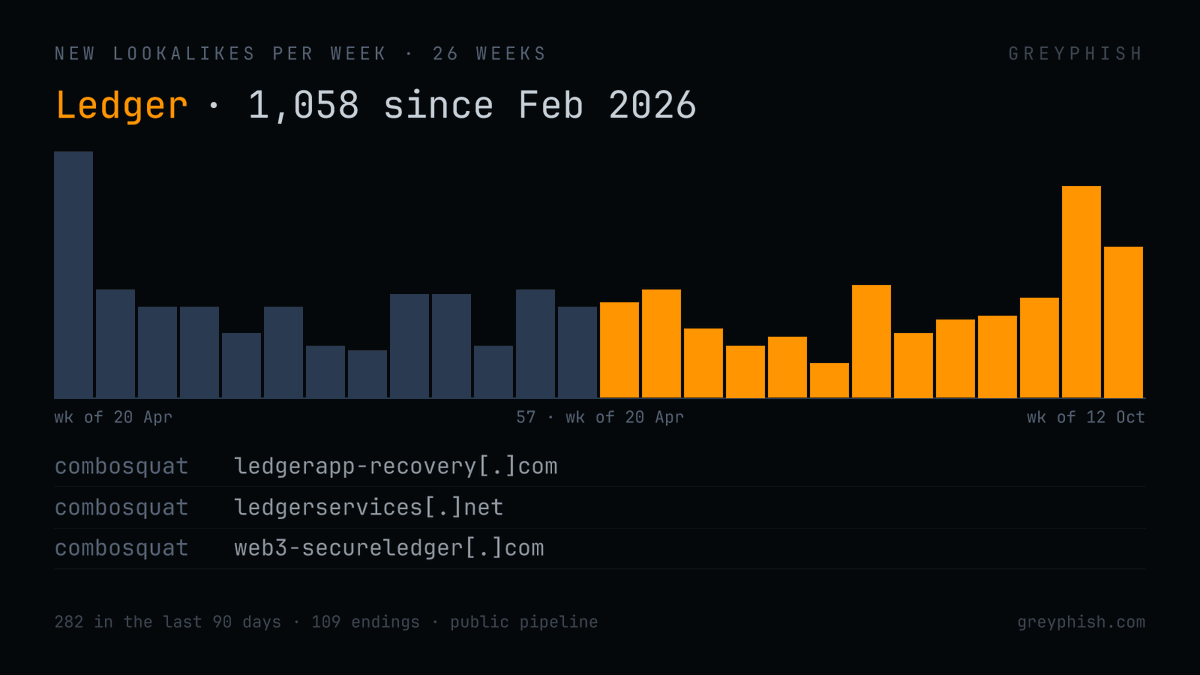
1,058 domains that resemble Ledger since February 2026, 282 of them in the last 90 days, on 109 different endings.
Most (86%) are combosquats: the name spelled right with a word added, most often "wallet" or "app".
One of the latest:
ledgerapp-recovery[.]com
@Ledger
support-clients-microsoft[.]com
A name you'd recognise, plus "support" and "client". First seen on 12 Oct 2026.
It serves a live site and publishes MX records.
@Microsoft#combosquatting
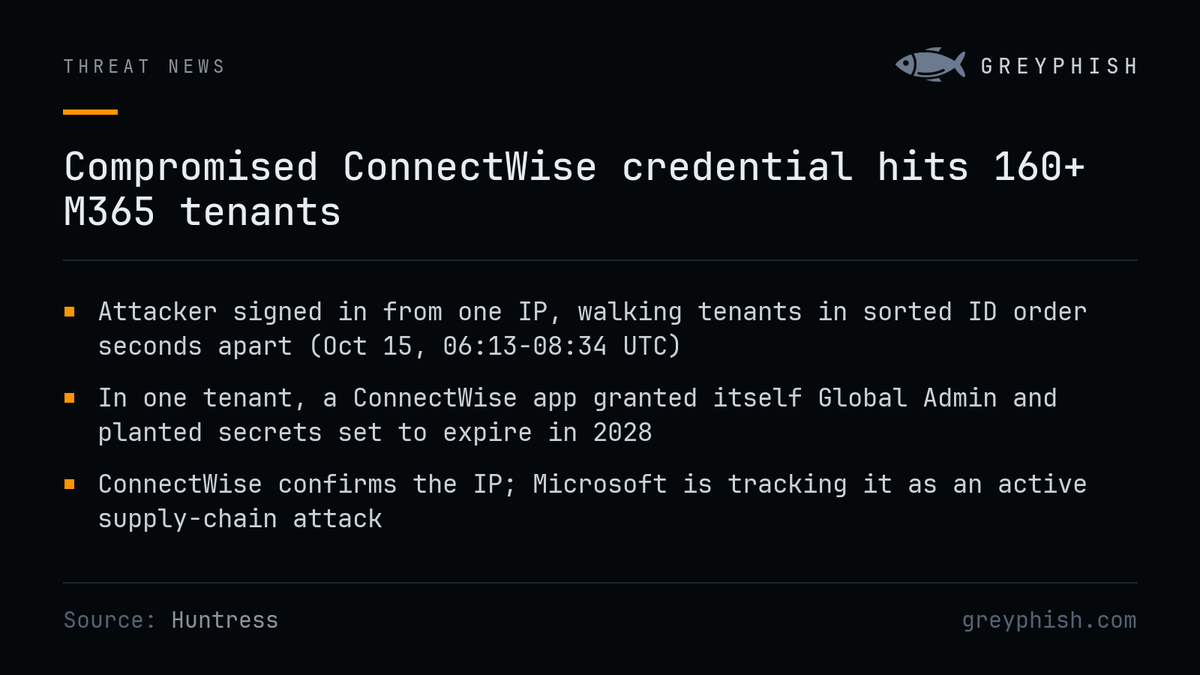
One stolen API credential for ConnectWise's MSP backup tool gave an attacker scripted sign-ins across 160+ Microsoft 365 tenants, seconds apart, in sorted ID order. In one tenant, a related app granted itself Global Admin and planted secrets set to expire in 2028. Per Huntress.
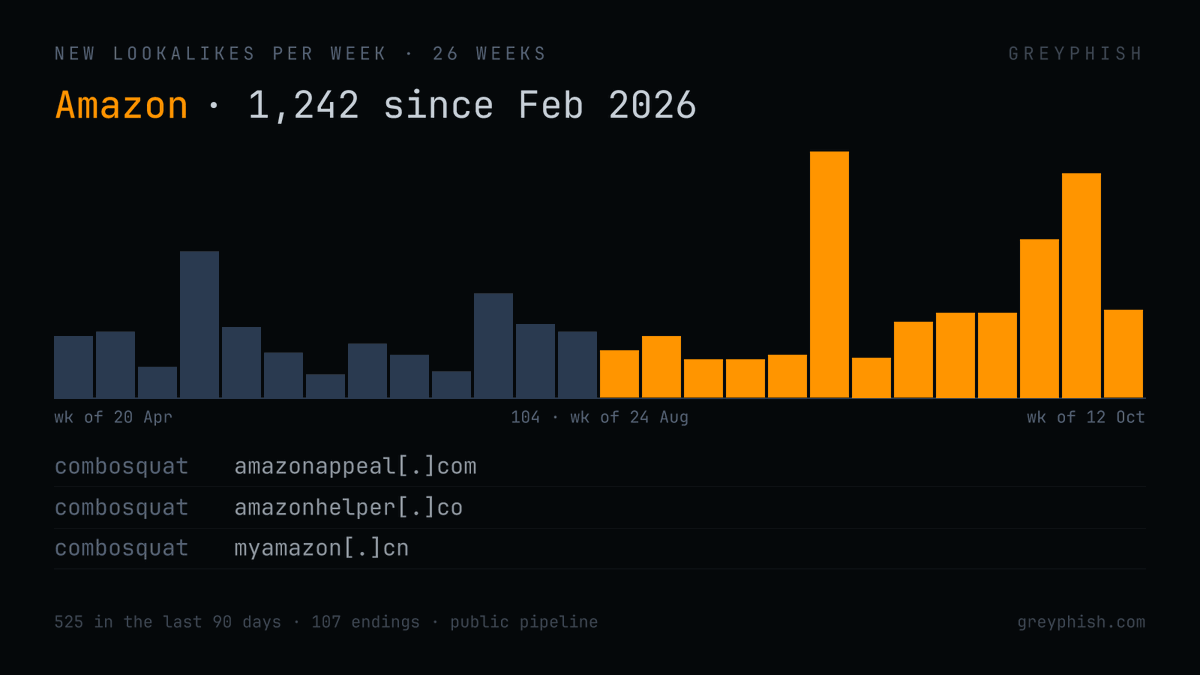
A recent Amazon lookalike: amazonappeal[.]com
It is one of 1,242 we have recorded since February 2026, 525 of them in the last 90 days.
Most (73%) are combosquats: the name spelled right with a word added, most often "service" or "web".
@amazon#threatintel#brandprotection
A pre-auth zero-day in BeyondTrust's remote-support tool let a China-linked group harvest every credential it stored and wipe the logs -- undetected for a month. The tool meant to secure privileged access became the single point attackers wanted. Per BleepingComputer.
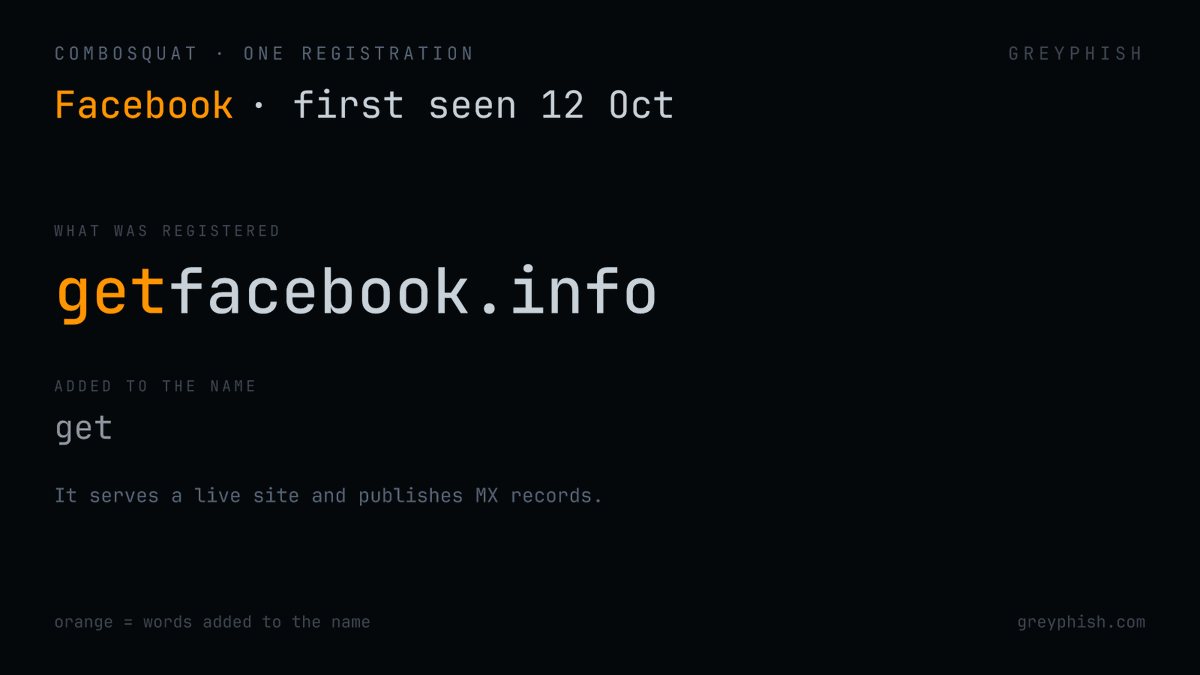
Combosquatting, first seen on 12 Oct 2026:
getfacebook[.]info
A recognisable name plus "get", in one domain.
It serves a live site and publishes MX records.
#combosquatting#infosec