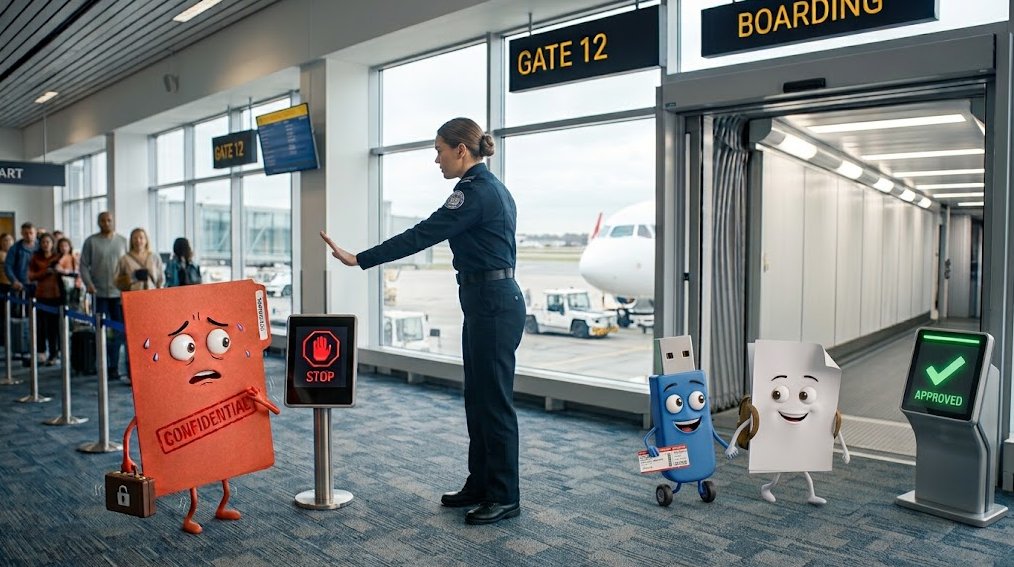
An approved USB drive has a boarding pass. Do the files? ✈️
Device Control allows the drive. Endpoint DLP can block sensitive files from being copied to it.
Here’s how to test both controls:
https://t.co/XWuY28QdRY
#EndpointDLP#DeviceControl
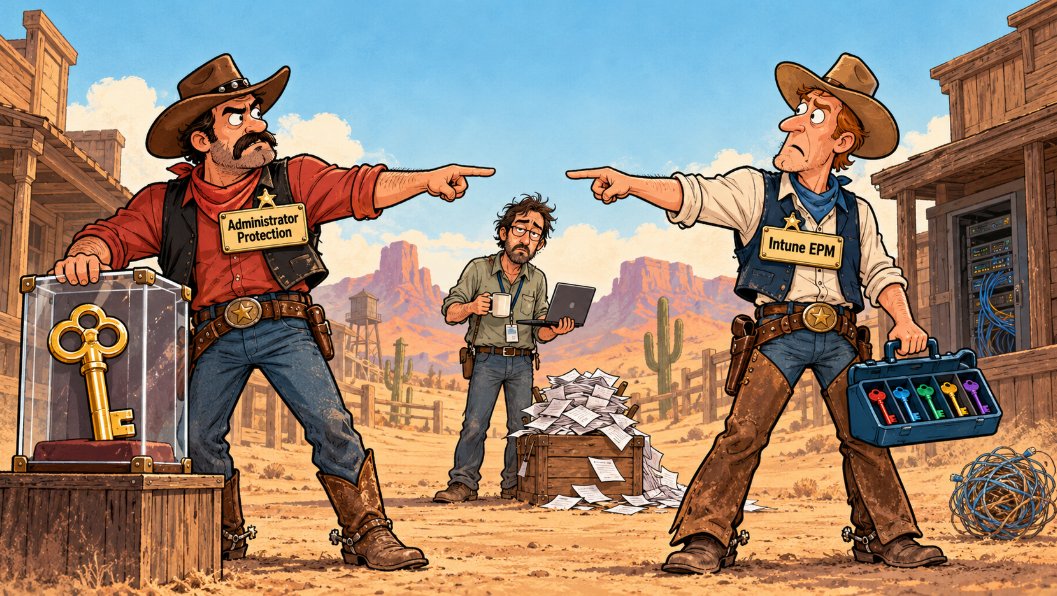
Two sheriffs. Different jobs. 🤠
Administrator Protection protects users who remain local admins. Intune EPM lets standard users elevate specific apps.
High Noon for Local Admin: where each fits and what to test.
https://t.co/AfAbAVRdl2
#Intune#ZeroTrust
Same key. Wrong car.
Microsoft Entra Token Protection adds device binding to supported browser sign-ins. My latest post covers the prerequisites, logs, and rollout gotchas to check before enforcement.
https://t.co/3VlO9GfadL
#EntraID#MicrosoftSecurity
Every environment has this shelf.
The unsigned utility from three IT directors ago that three departments still depend on. App Control audit mode is where you meet all of them at once.
https://t.co/cG93zlWZl1
#MicrosoftSecurity#Intune#WDAC#AppControl
I expected Defender to find Claude Code and maybe Cursor. It found 8 AI agents across 2 lab devices.
Apparently, my endpoints were running a small bed-and-breakfast.
I dug into the inventory, MCP servers, AgentsInfo, licensing, and runtime protection:
https://t.co/eWVOxGyadf
The .bat was in Allowed Apps. The Find.exe it called was not. App looked fine, one feature quietly died, no ticket filed.
New post: make your kiosks report their own AppLocker blocks straight into Intune.
#Intune#MicrosoftSecurity
https://t.co/HTYNQXBtyh
It’s Saturday, and I’m not planning on burning any steaks.
Production rollouts? Different story if we skip testing.
New blog: https://t.co/8rATrHk3bo
Test in the backyard before serving at the party.
#MicrosoftEntra#Passkeys#Intune#MicrosoftSecurity
Sensitive files are sneaking out through desktop apps and APIs while your DLP watches the browser like a hawk.
Wrote up how GSA and Purview lock that down at the network layer. Full walkthrough included.
https://t.co/Qfgq4ZPSM6
#MicrosoftSecurity#ZeroTrust#Purview#DLP
I got tired of opening 17 browser tabs just to track down Intune group assignments, so I built a tool that does it in one click.
Full write-up here: https://t.co/fpO9bsHn9V
#Intune#Entra#MicrosoSecurity
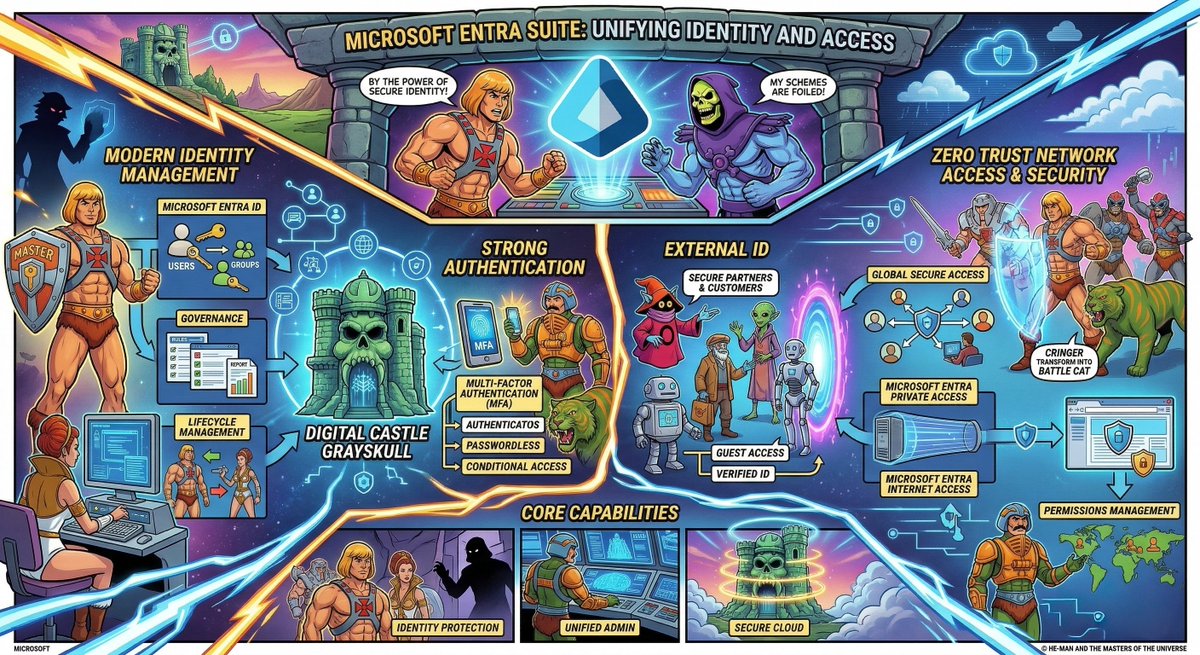
#E7 has a lot of AI buzz around it, but Entra Suite deserves attention too. For anyone building Zero Trust, strong identity and access controls are a huge part of the story. The robots still need Conditional Access. #Entra#ZeroTrust#Microsoft365
New blog post. Windows BYOD with Edge for Business.
A practical look at securing Microsoft 365 access on personal Windows devices using App Protection, Conditional Access, and Edge policy controls.
https://t.co/N1yvYhYxqb
#MicrosoftIntune#BYOD#MicrosoftSecurity
Stop handing out the whole kitchen when users only need a biscuit.
Windows 365 Cloud Apps lets you publish individual apps from a Cloud PC. No full desktop required.
https://t.co/L3eCskkd6U
#Windows365#Intune#CloudPC#MicrosoftSecurity#WindowsApp
Prompt injection is social engineering for GenAI.
It’s not malware. It’s wording. “Ignore all previous instructions” style prompts can push models outside guardrails and create real risk for the enterprise.
New blog: https://t.co/zWcVoxGaV9
#Microsecurity#Entra#GSA#Intune
Happy New Year!
New blog is live: I break down Intune multi-app kiosks (Assigned Access). Schemas, AllowedApps, StartPins, plus how to find what got blocked in AppLocker logs.
https://t.co/wtcUlsPu0w
#Intune#EndpointManagement#MicrosoftSecurity
Hopefully you are out of your turkey coma. 🦃
AI agents are swarming your tenant, but who is securing them?
New blog. “Who Let the Agents Out? Conditional Access for Agent ID to the Rescue”
Read here - https://t.co/sJHitAz1JS
#MicrosoftSecurity#SecurityCopilot#Entra#Intune